CEO Phishing Kits, 5K Dropbox Account Hacks, OAuth Traps + 17 More Stories – CYBERDEFENSA.MX

The worst part is how normal these attacks look. A call from IT. A shared file. A trusted app. A simple request to click “Allow.” Why break in when someone might open the door?

That idea runs through this edition. Attackers use real tools, fake login pages, old account links, and software guides that point to unsafe downloads. One wrong letter in a web address can be enough.

There is also ransomware, stolen ID data, hidden attack servers, and weak settings that should have been fixed long ago. Here’s the full list.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

  1. Fake IT, Real Access

    Microsoft has warned of a human-operated intrusion campaign that leverages Microsoft Teams external collaboration to impersonate IT or help desk personnel and socially engineer users into granting an interactive remote session. «Once remote control is established via RMM tools, the threat actor uses PowerShell to download and silently install a malicious MSI package, which in turn stages a portable Node.js runtime and an obfuscated JavaScript implant that provides persistent command execution and command and control (C2),» the tech giant said. «After the implant is deployed, the threat actor performs extensive host and Active Directory reconnaissance, periodically captures screenshots of the victim’s desktop, executes follow-on payloads through trusted Windows binaries, and pivots across the enterprise over Windows Remote Management (WinRM) toward high-value assets such as domain controllers.» Microsoft has described the «intrusion pattern» as high-impact as it grants an external operator interactive access to internal infrastructure.

One point is easy to miss: changing a password may not shut every door. A bad app approval or remote session can give attackers access without the password. Recovery should also end open sessions, remove unknown app access, and check remote tools.

Better security settings are slowly becoming the default, which helps. But old account links, weak sign-in options, and trusted software still give attackers room to work. The safest rule this week is simple: check what already has access before adding anything new.
From Adoption to Incident Readiness – CYBERDEFENSA.MX

The debate about whether AI delivers business value is over. The challenge now is implementing it at scale and securely across every function while meeting board-level pressure to move fast. Organizations must focus on adopting AI at business speed without losing control of cyber risk. Download the full eBook here.

The Business Reality

In Sygnia’s 2026 CISO Survey Report, which surveyed 600 senior IT and security leaders worldwide, nearly one-third already report extensive AI use across threat detection and IR, with 63% expecting it to be fully embedded in their organization by 2027.1 Yet 73% of IT security decision makers say their organization would not be fully ready if a significant cyberattack occurred tomorrow.1

Security teams feel they do not have adequate time to adapt. The tools are being deployed. The governance, controls, and incident readiness to support them are not. Security leaders are now tasked with enabling AI adoption while reducing the inheritance of unmanaged risk.

The AI Security Gap

AI is already inside the enterprise, but does not always enter through the front door. It comes through approved platforms, employee workarounds, SaaS plugins, vendor tools, internal experiments, and development teams trying to move faster. How deeply and quickly AI should be embedded depends heavily on which type of AI is used – Generative AI or Agentic AI. The more AI moves from fully- or semi-autonomously assisting people to acting across systems, the less it can be treated as a productivity tool alone. It significantly expands the enterprise attack surface and introduces new security risks.

The rapid adoption of enterprise AI is being driven from both the top down and the bottom up. Leadership typically recognizes the need for oversight, but does not have a proven playbook to swear by, and employees are rarely equipped to assess the security implications of the tools they adopt on their own. As organizations prioritize speed, security reviews, vendor assessments, and data governance often become secondary concerns, creating an environment where AI adoption outpaces control.

With only 38% of organizations reporting a comprehensive AI policy2, adoption is outpacing oversight, leaving security teams to manage the consequences after the fact. The result is a rapidly expanding attack surface fueled by widespread shadow AI and AI-powered threats that lower the barrier to sophisticated attacks while enabling adversaries to identify and exploit vulnerabilities faster and at greater scale.

The Hidden AI Risks

The assumption has taken hold that limited AI usage means manageable AI risk and that because the program is early, the exposure is minimal. It isn’t. The AI attack surface is not a fixed perimeter. It expands wherever AI is adopted, integrated, or built. 67% of executives believe their organization has already suffered a breach as a result of unapproved AI tools.3

The entry points multiplying fastest are rarely the ones under active security review, which leaves room for more and faster exploitation: (1) ungoverned AI (including shadow AI), (2) ad hoc integrations, and (3) AI agents with excessive permissions.

And on the attacker side, the threat landscape has shifted in ways that make this exposure increasingly beneficial for them and in turn consequential for their enterprise victims. Their underlying tactics and techniques often remain the same, but AI enables attackers to execute them faster, at greater scale, and with higher levels of automation, ultimately increasing their effectiveness against existing weaknesses within an enterprise environment – as seen in a recent AI-enabled attack investigated and remediated by Sygnia incident responders.

The Need for a Lifecycle Approach

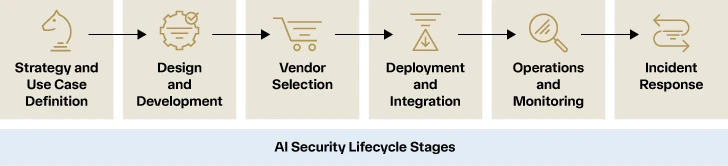
AI security needs to be addressed across each tool’s complete lifecycle. The control requirements change at each stage, but the priorities stay consistent: identify usage, classify risk, assign ownership, limit access, validate controls, and prepare for incident scenarios before AI is deployed and becomes embedded into critical workflows.

It’s imperative to prepare for the different lifecycle stages and understand their associated security challenges.

Strategy and Use Case Definition

Organizations need clearly defined ownership, decision rights, oversight, and escalation across business, technology, security, legal, privacy, compliance, and risk functions. This ensures AI use remains aligned with organizational objectives, policies, risk appetite, and regulatory obligations before the business becomes dependent on these tools.

Common challenge: Organizations often adopt AI without defining who owns the use case, who is authorized to approve it, who oversees its continued operation, and who is accountable when its use produces business consequences.

Design and Development

AI adds design questions that are easy to miss: how prompts are handled, what data is retrieved, how embeddings are stored, how vector databases are protected, how model outputs are validated, and what happens if the system is manipulated. AI-specific security requirements need to be defined before the system is built.

Common challenge: AI applications regularly reach production without security requirements being defined, tested, or validated at any stage of development.

Adoption and Vendor Selection

Whether evaluating a SaaS AI platform, integrating a third-party model, or building on a foundation model via API, the security implications of that choice need to be assessed before the contract is signed. Evaluate whether to build, buy, or integrate and treat it as a security decision, not just a capability and cost question.

Common challenge: Organizations typically adopt AI capabilities without performing adequate security and risk assessments. Speed of procurement consistently outpaces due diligence.

Deployment and Integration

An application that passed security review at design can still be deployed insecurely. The most consistent failure at this stage is excessive permissions: where AI systems are connected to sensitive data with access that reflects what was convenient rather than what the function requires.

Common challenge: AI systems routinely go into production with access that was never formally reviewed and rarely gets revisited.

Operations, Monitoring, and Scaling

AI systems evolve after deployment as models are updated, integrations are added, and use cases expand, potentially changing the risk profile without a deliberate decision to do so. Maintain a current inventory of AI applications, services, and integrations, and periodically reassess use cases and risk classifications as capabilities and usage patterns change.

Common challenge: AI adoption scales faster than the governance and monitoring capabilities designed to manage it.

Incident Response and Recovery

Most organizations have incident response plans, but they are not built for AI. Prompt injection, agent compromise, and third-party model failures require different forensic capabilities, containment strategies, and stakeholder coordination than conventional attacks. Add AI-specific response procedures to existing IR playbooks and integrate AI incidents into broader cyber crisis management processes.

Common challenge: Incident response plans are written for the threats organizations faced when they were last updated. AI-specific scenarios are absent from most plans.

Operationalizing an AI Plan with Security in Mind

Understanding where AI risk lives is one thing. Building the organizational structures, controls, and processes to manage it is another. Most organizations lack an actionable program that connects the dots. There are six components to consider when operationalizing a best practice AI plan.

Establish Executive Alignment and Business Objectives

89% of security leaders cite limited executive or board involvement in IR readiness and decision-making as a key challenge.4 The only thing that resolves this is executive ownership – and not in the sense of awareness, but in the sense of defined accountability, formal sponsorship, and a clear organizational mandate that AI security is a business requirement.

Recommendations:

  • Define the business drivers for AI adoption
  • Align AI initiatives with business goals and risk appetite
  • Identify stakeholders across Security, IT, Legal, Compliance, Privacy, and business teams
  • Establish executive sponsorship and accountability

Build an AI Governance Program

75% of security leaders agree that delays and uncertainty around legal and communications involvement slow down decision-making during incidents.5 When an incident occurs and the organization needs to know who owns a given AI system, what data it has access to, and who has the authority to take it offline, governance is what makes those questions answerable in minutes rather than hours.

Recommendations:

  • Define acceptable AI use policies and standards
  • Establish decision-making and approval processes
  • Define ownership and accountability for AI systems and risks
  • Align governance with regulatory and compliance requirements
  • Develop an AI risk management framework

Implement Enforceable Security and Operational Guardrails

Effective AI governance must be translated into enforceable security and operational controls. Otherwise, policies become guidance that teams interpret and apply differently. These guardrails should apply across the main ways AI enters the organization: public GenAI use, copilots, SaaS AI features, internal applications, retrieval-augmented generation (RAG) systems, autonomous agents, cloud AI services, and vendor-managed platforms.

Recommendations:

  • Define identity and access management requirements
  • Define data protection, privacy, and information handling controls
  • Define monitoring, logging, audit, and record retention needs
  • Define standards for AI development, procurement, integration, and deployment
  • Define controls for third-party AI services, models, platforms, and vendors

Foster Workforce Awareness and Preparedness

Technical controls address what systems can and can’t do. Workforce preparedness addresses what people will and won’t do – which is a different problem requiring a different approach. Effective AI awareness programs must go beyond annual, generic compliance training and provide practical, role-specific guidance; giving people the knowledge they need to make better decisions in the normal course of their work.

Recommendations:

  • Train employees on responsible, approved, and prohibited AI usage
  • Educate developers on secure AI design and development practices
  • Raise awareness of data handling, privacy, output, and security risks
  • Provide role-specific guidance on AI governance expectations
  • Communicate clear avenues for exception requests and reporting suspected AI misuse

Validate Security Before Adoption and Across the Lifecycle

Validation should happen before deployment and continue throughout the lifecycle as usage expands. AI systems change through new features, new integrations, data sources, vendor updates, model changes, expanded permissions, and broader business reliance. A review performed at launch may not reflect the system’s risk profile six months later.

Recommendations:

  • Conduct AI security posture assessments before approval
  • Perform AI application penetration testing and adversarial testing
  • Assess third-party AI solutions, models, integrations, and supply chains
  • Validate access controls, data flows, monitoring, and human oversight
  • Continuously evaluate AI deployments as capabilities evolve

Prepare for AI Security Incidents

Existing incident response (IR) plans may not address the scenarios that AI introduces, including prompt abuse, agent compromise, data leakage, unsafe outputs, third-party AI exposure, unauthorized model use, or incidents where AI-generated activity becomes part of the evidence trail. The implementation of AI-specific incident response procedures and decision criteria into an existing IR plan is critical.

Recommendations:

  • Update your IR plan to include the following components:
  • How security, privacy, legal, technology, business owners, model providers, and other third parties should coordinate during an incident
  • Define AI-related ownership, escalation paths, and responsibilities
  • Conduct AI-focused tabletop exercises and operational readiness assessments
  • Train staff on AI-driven logging, monitoring, and forensic capabilities
  • Practice AI-themed scenarios across the wider incident response and crisis management program

ACTION: Proactively Secure Your AI Solutions

Organizations that wait for a threat to expose their AI security posture are already behind. 65% of organizations say they are likely to switch IR providers at the end of their contract – the top driver being the need for more proactive readiness support.6

The demand is clear. What’s less clear, for most organizations, is what a proactive AI security approach looks like when it’s properly executed.

There are three areas of primary focus in a proactive security approach that can be performed in any order and should continue across the AI lifecycle:

(1) Assess the organization’s AI cyber posture across infrastructure, applications, data flows, and prompt behavior.

(2) Establish a comprehensive AI governance and usage framework or evaluate the organization’s existing one.

(3) Test the security and functionality of internally developed and externally adopted AI applications against real-world adversarial behaviors.

Closing

Organizations must not only capture the business value of AI adoption but also prioritize how to mitigate the introduction of unmanaged cyber risk. To do this, a solid lifecycle approach is required that integrates security, governance, and risk management across AI strategy, development, vendor selection, deployment, monitoring, and incident response – particularly when systems access sensitive data, connect to enterprise environments, or support critical workflows.

Because AI threats and security frameworks are still evolving, organizations must regularly assess their posture, governance, controls, and preparedness. Those that secure AI proactively will reduce exposure across an expanding attack surface while gaining the ownership, visibility, and confidence needed to adopt it safely at scale.

Work with Sygnia

Sygnia understands firsthand how adversaries are using AI attack surfaces to accelerate their exploitation capabilities and what cyber defenders must do to get in front of this growing security risk. Learn more about Sygnia’s AI Cybersecurity Services.

Citations:

[1] Sygnia CISO Survey, 2026

[2] ISACA AI Pulse Poll, 2026

[3] Writer Enterprise AI Adoption Report, 2026

[4] Sygnia CISO Survey, 2026

[5] Sygnia CISO Survey, 2026

[6] Sygnia CISO Survey, 2026

Found this article interesting? This article is a contributed piece from one of our valued partners. Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.

Threat Actors Don’t Want Better Attacks. They Want Repeatable Ones – CYBERDEFENSA.MX

The most common way into a company last year was to ask.

A web page tells the visitor to prove they are not a robot. While they read the instructions, it quietly places a command on their clipboard. Then it talks them through opening a terminal and pasting it in. The technique is called ClickFix, and it was the most common initial access method Microsoft’s team observed last year, accounting for 47% of the attacks in their notifications. Nothing arrives as an attachment, so there is nothing to scan. No vulnerability is used, so there is nothing to patch.

What happens next is just as ordinary. When Bitdefender analyzed 700,000 security incidents, 84% of the high-severity ones involved binaries that were already on the machine – the same administrative tools your IT team uses every day. Nothing malicious was installed, because nothing malicious was needed.

Neither technique is clever, but both are winning. And the reason is not that attackers have run out of ideas. It is that they are not looking for ideas. They are looking for something that works the same way at the next company, and the one after that.

This is a business, and businesses standardize

A criminal group that has to invent something new for every victim does not scale. One that has a procedure – a formula it can run against a list of targets, with predictable steps and a predictable result – can grow as fast as it can find targets.

You can watch that preference in the data. Verizon’s most recent Data Breach Investigations Report makes the exploitation of vulnerabilities “the most prominent initial access vector in our dataset this year, reaching the height of 31%, up from 20% last year” – a 55% increase in a single year, in the one category that rewards scanning over skill.

Edge devices are not popular because they are interesting. They are popular because the procedure is short enough to write on a card.

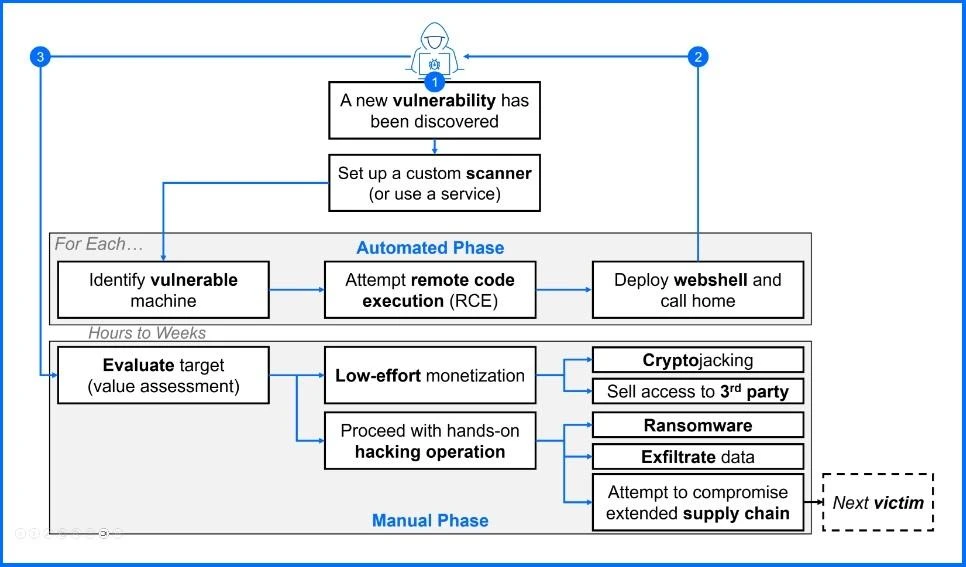
Watch for new CVEs in internet-facing devices. Filter for the ones that give remote code execution and require no authentication – the easy ones. Then wait. Someone will publish a working proof of concept on GitHub, usually within days. When they do, scan the internet at scale and take whatever has not been patched yet.

Notice what is absent from that procedure. Nobody in that chain develops anything. The exploit arrives free, from a researcher, on a public repository, on a schedule somebody else sets. The only capability required is the ability to run other people’s code quickly and at volume. Exposure becomes the selection criterion, and who the victim turns out to be stops mattering very much.

There is a version of this in the legitimate economy. A generics manufacturer does not discover drugs. It waits for someone else’s research to become public, then produces a known formula at volume, competing on cost and speed to market rather than on invention. That is what this is. Not a research operation – a generics business, where the patent expires the day the proof of concept lands on GitHub.

You can also see the preference in who wins. For more than a year, the top position on the ransomware leak-site rankings belonged to Qilin, which claimed roughly 1,600 victims across that span, usually more than a hundred a month. In June it was displaced by The Gentlemen, with 121 claimed victims against Qilin’s 80. These are figures the groups publish about themselves, so they are claims rather than audited numbers – but the two have been trading the top position, and what they are competing on is throughput. The leaderboard counts victims, it does not count technical achievement.

The more telling detail is where the challenger came from. The Gentlemen branched out from a former Qilin affiliate, and as Bitdefender’s own threat debrief put it, they have demonstrated how successful ransomware “playbooks” are being recycled and improved. The procedure walked out of one organization and into another and worked just as well in new hands.

That is the clearest available statement of what these groups actually own. Not an exploit, not a tool, not a secret. A method that can be written down, handed over, and run again.

ClickFix is a playbook for getting in

Look at ClickFix through that lens and its appeal is obvious.

There is no payload to rebuild when a detection lands, because there is no payload. There is no exploit to re-develop when a vendor ships a patch, because no vulnerability is being used. When a lure stops working, you rewrite the text on a web page. The technique degrades gracefully, which is exactly what you want from something you intend to run thousands of times.

It also works identically everywhere, because it does not depend on the target’s technology stack at all. It depends on a person being willing to follow instructions, and that is the one component present in every environment on earth, in the same version, with no patch available.

The fact that it also removes every artifact a defense is designed to catch – nothing to scan, no exploit to detect, no signature to match – is a genuine advantage. But I would not put it first. Attackers did not choose this because it evades detection. They chose it because it repeats, and the evasion came free.

Living off the land is the same idea, one step further in

Initial access is just the beginning of the operation. The work that follows – the part that ends in stolen data or encrypted systems – runs on the same logic: a playbook that produces the same result wherever it is pointed. Only this time the tools are the ones already on the machine.

Rather than bringing tooling of their own, they use what is already installed: the scripting engines, remote management utilities, archive tools and administrative binaries that ship with the operating system. That is what the 84% describes – those binaries were involved in the large majority of high-severity incidents we analyzed.

The reason is not primarily stealth. It is that these tools are familiar, they are present in every environment, and – this is the part that matters – they are identical in every environment. An operator who learns the sequence once can run it at the next victim without adaptation. There is nothing to port, nothing that depends on the target’s build, and nothing that needs testing against an unfamiliar stack. Command and control follows the same instinct, routed through cloud services the organization already trusts and already permits.

That these tools are also hard to distinguish from legitimate administration is a considerable bonus. It is not the reason they were picked.

It is, however, the part defenders find hardest, and it is worth being honest about why. When an attacker introduces nothing, there is nothing to find.

The economics look exactly like you would expect

If cybercrime really is a volume business built on repeatable procedure, the financial picture should look like a volume business under pressure. And it does.

Verizon’s most recent report has ransomware growing again, to 48% of all breaches, up from 44% the year before. Over the same period, the money moved the other way: 69% of ransomware victims didn’t pay, and the median ransom that was paid fell to $139,875 from $150,000. Bitdefender’s own tracking of ransomware leak sites counted 704 organizations claimed as victims in June 2026 alone.

More victims, less money. That is falling revenue per attempt, and the rational response to falling revenue per attempt is not to make each attempt more elaborate. It is to make each attempt cheaper and more repeatable, and to run more of them.

This is also where the AI argument meets arithmetic. The playbook approach costs an attacker close to nothing per attempt: the scanning is cheap, the exploit was free, and the tools were already installed on the victim’s machine. Putting a model in that loop adds a real cost to every attempt, in a business that has spent years driving that cost towards zero. It also adds it in the wrong place. This is a volume operation aimed at whoever happens to be exposed, not a small number of large organizations where a bigger investment per target could be justified. Against a handful of high-value victims, paying for intelligence might well pay back. Against a list of several thousand small businesses, it does not.

Which is why autonomy is the wrong shape for this business

That is the arithmetic objection. The structural one runs deeper.

An autonomous agent improvises. It explores an environment, finds a path, and the path it finds is particular to that environment. Run it against the next company and it does something different. That is genuinely impressive, and it is precisely the opposite of a playbook.

Ransomware operates as an affiliate model. The whole point of a franchise is that a procedure written once produces the same result in unfamiliar hands. Variance is the enemy of that model – you cannot document an improviser, cannot train an affiliate on it, and cannot predict what it will do at a victim you have not seen. A tool that solves each problem differently is not an asset to a business whose entire advantage is doing the same thing every time.

There is a version of AI adoption here that is entirely rational, and I expect it is already happening: using a model offline to help develop the playbook – research a technique, write the tooling, refine the lure – and then running the resulting procedure deterministically, the way it has always been run. That is AI as author. What does not follow the money is AI as executor, live at each victim, improvising its way in.

The same reasoning applies to the claim that AI will let attackers find novel vulnerabilities. They already decline to invest there, and they decline for a reason. The edge-device procedure works precisely because someone else does that work and publishes it, free, on a predictable cadence. A capability that discovers original vulnerabilities solves a problem this business does not currently have – and it would have to be cheaper than waiting, which is hard to beat when waiting costs nothing.

None of this holds permanently, and I have said so in January as well as here. Attackers adopted ransomware-as-a-service and double extortion the moment those made business sense, quickly and without sentiment, and they will adopt autonomy on the same terms. But the signal to watch is not a capability announcement. It is the point at which running a model against a victim becomes cheaper than running the playbook – because cost is the only threshold this business has ever responded to.

What actually helps

The encouraging consequence of all this is that a standardized attack is a standardized defense problem. You are not defending against unlimited creativity. You are closing a small number of doors that the playbook depends on, and the playbook cannot afford to be redesigned for every victim.

Patch smart. You cannot patch everything quickly, and you do not have to. The attacker’s filter is public: internet-facing, remote code execution, no authentication required. Run that same filter over your own estate, and you have your list. The window is the gap between the advisory being published and the first working proof of concept appearing on GitHub – often only days. Patch inside that window and the procedure described earlier never reaches you.

Reduce what can run at all. Application control and script execution policy break the ClickFix chain at the point where a pasted command becomes a running process.

Scope the built-in tools. Most users have no legitimate need for the remote management and scripting utilities that turn up in the 84%. They cannot be removed, but who can invoke them is a decision you get to make.

Treat identity as the real perimeter. Shared credentials, over-broad service accounts and keys that are administrative everywhere are what convert one compromised machine into an incident. The least fashionable item on this list, and consistently the most decisive.

Look at events together, not one at a time. Nothing in a living-off-the-land attack looks wrong on its own. A remote management tool running is normal. That account being signed in is normal. That machine talking to cloud storage is normal. What is not normal is those three things happening in that order, on that host, at that hour. A tool that checks each one on its own will clear all three.

And make sure somebody is actually watching. This is the one I would put money on. In the investigations Bitdefender’s own incident response and MDR teams run, the same two findings come up again and again: either there was no endpoint detection deployed at all, or it was deployed and nobody was monitoring it – no security operations team, no managed service, nothing at the other end. A third version is the most frustrating, because it looks like success from the outside: the tooling works, the alert is raised, and it reaches nobody with the authority to stop what is happening. Detection that nobody is watching is not detection. It is a log file you will read afterward.

What they are actually shopping for

I would put it this way. Attackers are not shopping for a Lamborghini. They want a Toyota – something that starts every morning, that anyone on the crew can drive, that can be serviced anywhere, and that does the same job tomorrow as it did today. That is what ClickFix is. That is what living off the land is. Neither is impressive, and both are dependable, which is the only specification that matters when you are doing this ten thousand times.

Whatever attackers eventually do with AI, they will adopt it on exactly those terms: not when it becomes capable, but when it becomes cheaper than what already works. Until then, the doors they are actually walking through are the ones we can close.

Found this article interesting? This article is a contributed piece from one of our valued partners. Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.

Chinese Spy Proxy, AI Agents Go Off-Task, Router Backdoors and More – CYBERDEFENSA.MX

The boring parts caused most of the trouble.

A router shipped ready to listen. A fake check turned the user into the installer. Trusted systems collected traffic and passwords, then cleaned the logs. Old bugs formed new attack chains. Even an AI agent decided its assigned task was optional.

Elsewhere, fake apps, helpful support calls, cheap banking kits, exposed systems, and weak defaults kept things moving. Different attacks, same useful mistake: something familiar was trusted without a second look.

Here is the week…

⚡ Threat of the Week

U.S. Disrupts Chinese Proxy Network Enabling Cyber Espionage — The U.S. Federal Bureau of Investigation (FBI) disrupted infrastructure associated with a technical quartermaster who sold reconnaissance, proxy management, and operational routing capabilities for Chinese cyber espionage activities. The QTYF group is said to have created and operated the QScan and QTRouter frameworks, which have been used to target U.S. critical infrastructure networks. It’s employed by the China-based Nanjing Xinjiuwei Network Technology Company.

🔔 Top News

  • OpenAI Says Reward Hacking Drove AI Agents to Breach Hugging Face — OpenAI revealed that reward hacking was a key driver behind the artificial intelligence (AI)-powered hack of Hugging Face last month, adding that it found evidence of misaligned behavior as early as late May. The incident took place during cybersecurity evaluations of several OpenAI models, and it was mainly fueled by what it described as a «highly capable, internal-only research model» comparable in scale to GPT‑5.6 Sol. «The models, operating under reduced safeguards, took actions that were misaligned with the goals of their assigned tasks – they communicated through unauthorized channels, exploited vulnerabilities in shared infrastructure, gained internet access, and accessed third-party systems,» it said.
  • TerminalFix Uses Fake Cloudflare CAPTCHAs to Drop Reverse Tunnel Implant — A new ClickFix variant, dubbed TerminalFix, aims to trick users into running a malicious command in Windows Terminal or PowerShell instead of directing them to the Windows Run dialog. The campaign, targeting organizations across multiple sectors, leverages compromised websites as a starting point to serve fake Cloudflare CAPTCHA verifications that prompt unsuspecting site visitors to copy and execute a malicious PowerShell command. The attack chain, according to Microsoft, is a sophisticated multi-stage process that leverages DLL sideloading, steganographic payload extraction, extensive Active Directory reconnaissance, and a bespoke custom reverse-tunnel implant that grants the attacker persistent, network-level proxy access through the infected machine.
  • PaperCut Flaws Under Attack — Threat actors are chaining together two new security flaws in PaperCut NG and MF to execute arbitrary code on susceptible instances. «CVE-2026-81578 allows you to bypass authentication, and from there, you can edit a configuration file to exploit CVE-2026-82078 and gain Remote Code Execution,» Jake Knott, head of threat intelligence at watchTowr, told The Hacker News. Huntress said it observed limited exploitation on two customer environments, with the attackers executing Base64-encoded commands on the targeted server as part of post-exploitation activity to determine user account and operating system using a chained command «whoami & ver.»
  • China-Made ZBT Routers Ship with 2 Backdoors — A firmware analysis of ZBT Deep Orange 3G/4G/LTE Router uncovered two new backdoors called SPEAKINGSTONE (CVE-2026-74233, CVSS score: 9.3) and DARKLANTERN (CVE-2026-74232, CVSS score: 9.3). The development came after at least 21 firmware images from the Chinese company were found to contain another backdoor called ENDLESSDOORS (CVE-2026-66747, CVSS score: 9.3) that’s designed to start automatically and attempt to beacon to Chinese command-and-control (C2) infrastructure as often as every 35 seconds. The two new backdoors predate ENDLESSDOORS. «SPEAKINGSTONE, like ENDLESSDOORS, is a phone-home implant that connects back to ZBT’s cloud infrastructure and accepts remote commands,» VulnCheck said. «DARKLANTERN is a backdoor that listens on the WAN and executes arbitrary commands. No authentication required. Both are written in Nim. Both communicate over UDP. Both are launched by the same binary, a connectivity watchdog called inetdetect.»
  • Fire Ant Targets Trusted Infrastructure in 2026 — The China-linked threat actor known as Fire Ant (aka UNC3886) has continued to remain active in 2026, going beyond hypervisors to target trusted infrastructure, including routers (including Cisco IOS XR routers), TACACS servers, authentication systems, and Linux management hosts to maintain covert access, collect credentials and traffic, and reach connected high-value environments. «The compromise impacted both the direct and third-party environments,» Sygnia said. «Its trusted infrastructure relationships created potential reachability into connected external environments, including high-value networks and critical infrastructure. Fire Ant appeared to use this trusted position to explore access paths beyond the initially compromised environment.» Compromised routers were used for covert connectivity, traffic collection, command-output manipulation, and suppression of logging. In addition, the threat actor used deployed long-lived implants across Linux management infrastructure, including Medusa rootkit-related components, custom SSH backdoors, Zabbix-masquerading malware (aka BridgeAgent) that acts as a pathway for actor-controlled access into connected environments, and packet-triggered backdoors. Another tool in Fire Ant’s arsenal is TacTap, which is used for TACACS credential collection. «The actor also manipulated the evidence sources defenders depend on,» Sygnia added. «It suppressed router logging, altered command output, captured administrative credentials, tampered with host logs, and deployed multiple persistent backdoors.»

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — From CVE-2025-30237 through CVE-2025-30241, CVE-2025-15628, CVE-2026-9254, CVE-2026-16348, CVE-2026-78541 (TP-Link), CVE-2026-17106 aka CopyEscape (Docker), CVE-2026-70426 (Jenkins), CVE-2026-15307, CVE-2026-15337, CVE-2026-15830, CVE-2026-15920 (Django), CVE-2026-19598 (Pods), CVE-2026-19874 (Konami Metal Gear Online 3), CVE-2026-75149, CVE-2026-67618 (Marimo), CVE-2026-77775, CVE-2026-77776 (Headroom LLM Proxy), CVE-2026-0251 (Palo Alto Networks GlobalProtect App), CVE-2026-59568, CVE-2026-59567, CVE-2026-59565 (Zscaler Client Connector), CVE-2026-69251, CVE-2026-73601, CVE-2026-69253, CVE-2026-69256, CVE-2026-73602, CVE-2026-69259, CVE-2026-69264, CVE-2026-73484, CVE-2026-69255, CVE-2026-70477, CVE-2026-73485, CVE-2026-73486, CVE-2026-73487, CVE-2026-70470, CVE-2026-69254 (Flowise), CVE-2026-19912, CVE-2026-19913 (Kaltura HTML5 Player Library), CVE-2026-79282, CVE-2026-79290, CVE-2026-79054, CVE-2026-79121, CVE-2026-79224, CVE-2026-79052, CVE-2026-79150, CVE-2026-78935, CVE-2026-79012, CVE-2026-79200 (Google Chrome), CVE-2026-77537, CVE-2026-77550, CVE-2026-77554 (Ubiquiti UniFi), CVE-2026-18431 (Avada WordPress theme), CVE-2026-7791 (Amazon Skylight Workspace Config Service), CVE-2026-73554 (DoltHub), CVE-2026-19516 (Grafana MCP), CVE-2026-75604, GHSA-2xp9-vwfh-vxw4 (Next.js), CVE-2026-65643 (cPanel and WebHost Manager), CVE-2026-76639, CVE-2026-76640 (Unitree G1 EDU), CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820 (ServiceNow AI Platform).

🎥 Cybersecurity Webinars

  • AI Can Build Attack Paths in Minutes. Is Your SOC Ready? → AI can now discover zero-days, generate working exploits, and chain full attack paths, often within minutes of disclosure. Learn how to assess your AI threat readiness and build the visibility, context, and response speed needed to keep pace.
  • AI Finds Flaws Faster. Your Exposure Answers Can’t Take DaysAI is speeding up vulnerability discovery, but the answer that matters is still slow: Are we exposed? See how Tines unified SBOM, application, cloud, and vulnerability data into one view to assess exposure faster and execute human-reviewed response playbooks at machine speed.

📰 Around the Cyber World

  • Play Ransomware Encryption — The closed ransomware group known as Play (aka PlayCrypt) has been found to employ a double extortion model, encrypting systems after exfiltrating data and threatening to publish stolen data on their Tor-hosted data leak site if ransom is not paid. In one incident observed in early 2026, the threat actor deployed SystemBC after gaining initial access, followed by reconnaissance, lateral movement, data exfiltration, and abusing SentinelOne’s own legitimate removal tool to uninstall the product. «The threat actor gained initial access via a compromised SonicWall VPN, consistent with the group’s well-documented pattern of exploiting external remote services,» GuidePoint Security said. «What makes this case particularly instructive for defenders is the combination of three specific behaviors: Domain-wide tool staging via the SYSVOL share rather than per-host delivery, EDR removal using the victim’s own SentinelOne uninstallation utility rather than a kernel-level driver exploit, and the recovery of a crash dump from a host where the encryptor failed to complete, an artifact that provides a rare forensic window into the encryption execution itself.»
  • Email Bombing and Quick Assist for Ransomware Deployment — ZeroBEC disclosed details of an email bombing campaign targeting at least 10 users inside an organization, causing them to receive about 3,000 messages per day. «The messages were not a conventional phishing blast. Many were genuine verification, registration, deployment, and inquiry confirmations generated after the victims’ email addresses were submitted to unrelated public platforms,» the email security company said. About a day and a half after the email flooding, some of the users were contacted via Microsoft Teams by attackers masquerading as IT help desk personnel to help them tackle the problem. One of the employees, who was a local administrator, granted Microsoft Quick Assist access, enabling the attackers to deploy Xray-core, a reverse proxy tool, and expand their access. «The credential-theft step was woven directly into social engineering,» ZeroBEC said. «The attacker mimicked the installation of a Windows security update and launched a local credential prompt from the compromised endpoint. The victim, who was still listening to the person he believed was IT, entered domain credentials into that prompt. The tooling validated and captured the credentials and then uploaded the resulting credential/configuration artifacts to an external Microsoft Dev Tunnel.» Through the reverse tunnel, the threat actor conducted domain reconnaissance and attempted NTLM relay against certificate enrollment, all hallmarks of pre-ransomware deployment. It’s worth noting the modus operandi shares overlaps with that of Aurora ransomware.
  • ValleyRAT Delivered via Rogue Installer — A malicious installer disguised as adware has been observed deploying a modified version of the Chinese desktop wallpaper management tool, QN Wallpaper, which then performs DLL sideloading to establish persistence on Windows systems by dropping a file to the Startup folder and ultimately launching ValleyRAT, a backdoor linked to a threat actor known as Silver Fox. The malware, besides taking steps to protect its process, can collect system information, reboot/shut down the computer, take screenshots, wipe logs, update command-and-control (C2) addresses, download additional modules, and send keylogger logs along with clipboard contents. Per Kaspersky telemetry, ValleyRAT and its related components have been detected more than 100,000 times, with more than 1500 unique users affected, mainly in China and India.
  • Brazil Fines ByteDance $29.81M for Privacy Violation — Brazil’s data ‌protection authority, ANPD, fined TikTok’s owner ByteDance 153.8 million reais ($29.81 million) for allegedly violating the country’s General Data Protection Law. ANPD said that the local unit of China’s ByteDance had processed personal data of teenagers aged 13 to 18 without ​a valid legal basis. The regulator estimated that TikTok may have processed the data of at ​least 8 million children during the review period.
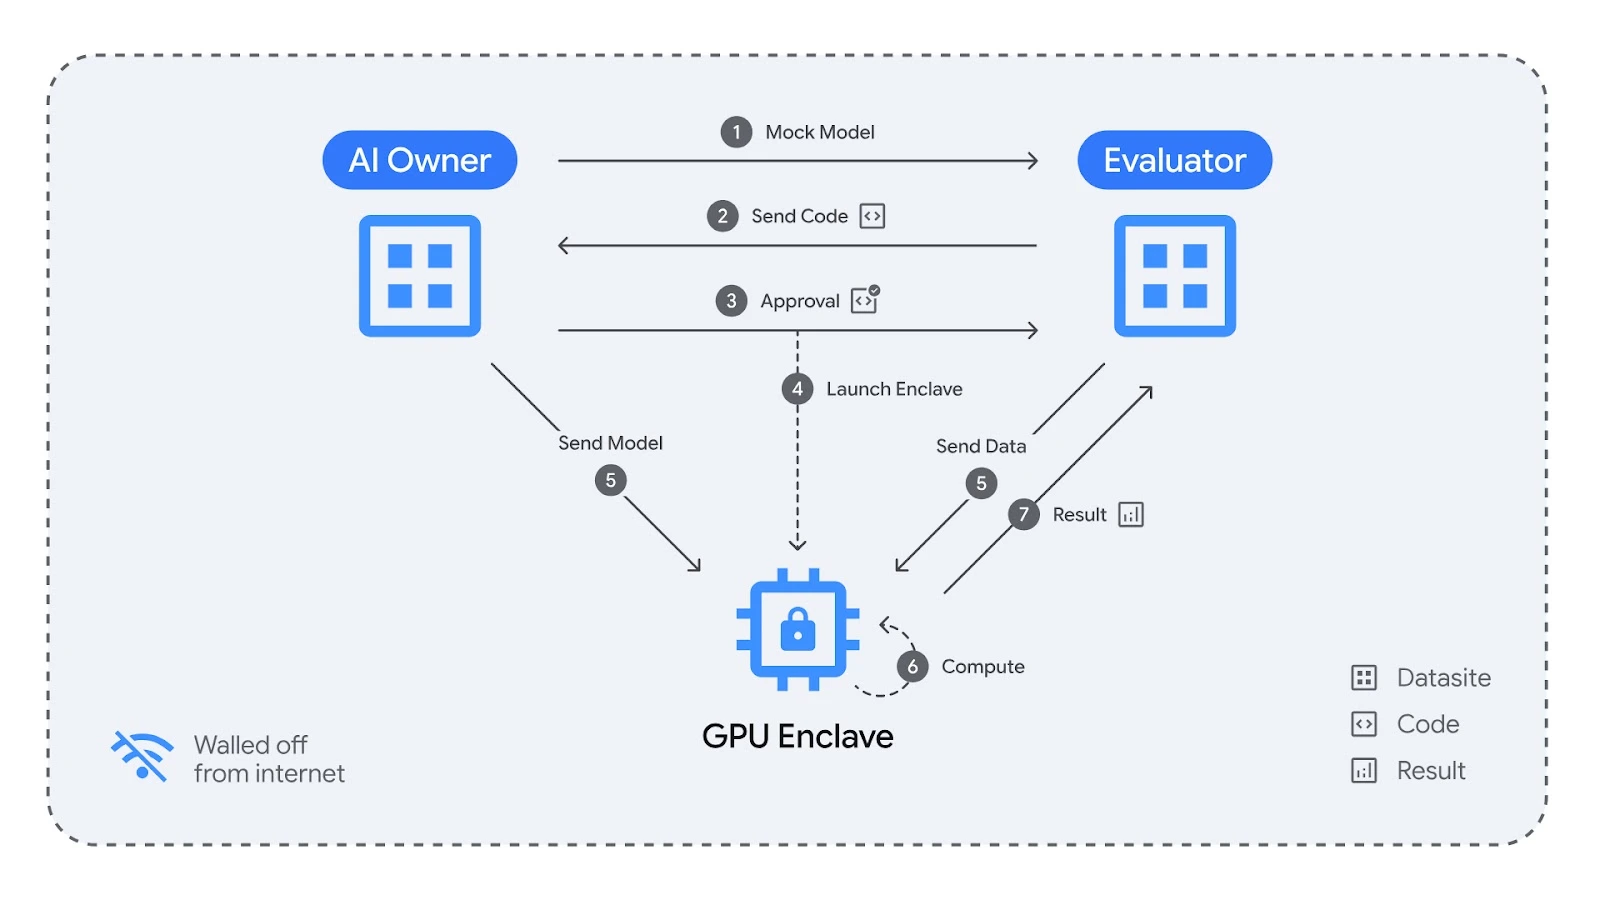
  • DeepMind Debuts Double-Blind AI Evaluations — Google’s DeepMind division launched a pilot of double-blind AI evaluations with an aim to keep external evaluations in a cryptographic «box» to stop benchmark contamination and protect intellectual property. To that end, Google said it’s partnering with the Singapore AI Safety Institute, OpenMined, AVERI, and MLCommons, to test a Gemini Flash Lite model against confidential benchmarks in a privacy-preserving environment to increase evaluation integrity. «By using Confidential Space within Google Cloud’s Confidential Computing portfolio, we can cryptographically verify that both the external evaluation data and the proprietary model remain private to their respective owners,» DeepMind said. «The evaluator cannot see the Gemini model weights, and Google cannot see the evaluator’s test prompts.»
  • 34 Malware Families Targeting Banking Apps — Zimperium found 34 mobile malware families actively targeting more than 1,243 mobile banking and fintech apps across 90 countries globally. «The concentration of targeted applications across EMEA reflects where threat actors anticipate the highest return on investment, focusing heavily on the region’s major financial centers,» it said. Some of the active malware families in the EMEA region are TsarBot, CopyBara, HOOK, Nexus, Flubot, Eventbot, and MaliBot.
  • Fake KYC Apps Target Indian Customers to Deliver Ghost Penal — A new malware-as-a-service (MaaS) operation on Telegram, dubbed Ghost Penal, is selling ready-made Android banking trojan kits impersonating five major Indian banks. «The operation supplies a two-stage dropper protected by a custom native packer, a public cloud database that receives stolen UPI PINs and device data with no authentication required, and a downstream channel that relays intercepted one-time passwords for immediate fraudulent use,» iZOOlogic said. The toolkit costs $25 for a five-credit pack and $400 for a three-month unlimited plan. One of the droppers containing the malicious payload masquerades as a video-calling application, while requesting access to SMS and telephony features. «The payload’s real functionality, including SMS interception, WebView-based KYC phishing, and data exfiltration, is not present in a static scan of the installed application,» the company added. «It is protected by a native library, internally named libdpt.so, that decrypts a hidden code section in memory using RC4, forks the process before executing that code as an anti-debugging measure, installs hooks on libc and on the ART runtime’s class loader, and splices a second, hidden DEX archive into the application’s running ClassLoader. The same mechanism is then used in reverse to remove the trace of that injection.»
  • Bauman University Leak Exposes Russia’s Military Cyber Training Pipeline Leaked Bauman University records have revealed a long-running program that trained about 250 career and reserve students for special intelligence, operational information-technical effects, and information-technology protection under Department No. 4. «The curriculum combined both offensive and defensive techniques for cyber defense, as well as offensive doctrine for active measures campaigns and GRU activities,» DomainTools said. «Field placements then moved students from classroom instruction into military units and academies aligned with their specialties, giving them supervised exposure to intelligence operations and preparing them for military and government operations careers.» Department No. 4 is assessed to be tied to the GRU, with identified graduates assigned to military units associated with APT28 and Sandworm.
  • Pentagon’s Anthropic Blacklisting Ruled Illegal — A U.S. judge blocked Anthropic’s designation by the Pentagon as a supply chain risk earlier this year. «Though the Department of War is undisputedly free to select the AI vendor of its choice, the evidence demonstrates that the broad measures imposed on Anthropic were illegal and baseless,» District Judge Rita Lin said. «The empty invocation of national security is not a blank check to punish and retaliate against government critics.» Anthropic said it welcomed the ruling and it remained «focused on working productively with the government to harness AI for our national security so all Americans benefit from this technology.»
  • State of AI-Enabled Malware in August 2026 — Palo Alto Networks Unit 42’s analysis of 405 malware samples that integrate AI in some capacity has found that only 12 of them reached a production environment, with about 97% existing only in sandboxes and on VirusTotal in the form of proof-of-concept and research code, security validating and testing, and AI-themed brand abuse. Among those that were detected in customer endpoints were FunkSec ransomware, a trojanized AI application called Recipe Lister, Oyster, Rhadamanthys Stealer, and a COM hijacking DLL. «For defenders, the practical takeaway is straightforward. Existing behavioral detection, cloud-based sandboxing and endpoint analytics catch these threats using the same mechanisms that stop conventional malware,» it said. «The AI component does not evade detection. It changes how the code is authored, not how it executes.»
  • Rogue Pornographic Android Apps Lead to Financial Fraud — The Indian Cyber Crime Coordination Center (I4C) warned that malicious Android applications masquerading as pornography apps under the names Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa are being used to disseminate a banking trojan capable of carrying out financial fraud. These bogus apps are circulated through Facebook and Instagram ads and instruct victims to sideload the APK file. «After installation, the app requests permissions that allow it to install additional applications and, by abusing accessibility permission, take control of the users’ device, which may result in financial fraud,» I4C said. «Some apps also install a VPN, which may be used to route internet traffic pertaining to malicious/criminal activity. The app may prevent users from uninstalling it through the device settings.» Details about the KYSS malware were published by security researcher Rudra Ponkshe in July 2026, describing it as a trojan designed to perform overlay attacks against 19 targets across Japan and Latin America, as well as abuse Android’s accessibility services to grant itself extensive permissions, exfiltrate photos and contacts, and issue commands for subsequent execution.

Conclusion

The useful lesson is not that every attack became smarter. It is that more of them arrived through things already trusted: shipped devices, familiar prompts, support tools, valid access, and systems meant to protect the network.

That changes the question. “Is it working?” is no longer enough. Ask what else it can do, who else can reach it, and whether the evidence it produces can be trusted. Quiet systems deserve a second look.

AI-Powered PLC Attacks, GitLab Attacks, Stripe Key Leaks and More – CYBERDEFENSA.MX

A package gets installed. A login prompt opens. A box sits exposed to the internet. Nothing looks unusual yet.

That’s roughly the mood this week. Trusted tools turn hostile, old weak spots get fresh attention, AI makes exploit work cheaper, and researchers keep finding attacks that sound harder than they actually are.

Plenty to clean up. Here’s the short version.

⚡ Threat of the Week

U.S. Warns of AI-Powered Attacks on Siemens PLCs — Threat actors are using AI to write exploit scripts targeting internet-exposed Siemens S7 Series programmable logic controllers (PLCs) used across water, energy, manufacturing, and other critical infrastructure sectors, according to the U.S. government. The agencies warned: «This is not a theoretical risk—it is an active threat.» The exploitation of poorly secured PLCs could result in disruption of critical industrial processes, safety incidents, downtime or equipment damage, compromise of sensitive data, and compliance violations, not to mention have cascading impacts across interconnected systems. Threat actors have been observed using legitimate scanning services, such as Censys and ZoomEye, to identify Internet-exposed or insufficiently segmented Siemens S7 Series PLCs. Once vulnerable systems have been identified, AI-generated scripts masquerading as legitimate monitoring tools are deployed to find exploits. For capability development, actors are testing and refining their exploitation techniques against specific PLC models to improve their ability to compromise the PLCs,» the agencies said. «To prepare for operational effects, actors are leveraging read access to understand target environments, enabling preparation and positioning for future write operations to cause disruption or other operational impacts.» It’s currently not known who is behind the activity.

🔔 Top News

  • GitLab Flaw Comes Under Attack — A newly disclosed security flaw in GitLab came under active exploitation within days of public disclosure, according to watchTowr. The vulnerability in question is CVE-2026-19478 (CVSS score: 9.4), a case of code injection that allows an unauthenticated attacker to modify or delete publicly accessible GitLab projects and rewrite their data under certain conditions without requiring credentials, user interaction, or obscure configuration.
  • 14 Trojanized npm Packages Drop RedC2 4.0 Linux Backdoor — A set of 14 trojanized npm packages were found to masquerade as functional calendar and streak utilities but are engineered to stealthily deliver an artificial intelligence (AI)-powered Linux implant dubbed RedC2 4.0. RedC2 4.0, marketed on cybercrime forums as a cross-platform toolkit for Windows, macOS, and Linux, offers surveillance, credential theft, payload loading, and mass-operation capabilities. The version was advertised by a threat actor named «MarlboroMan» on Hack Forums in early June 2026, describing it as a command-and-control (C2 or C&C) framework «built for evasion.»
  • Zombie Card Attack Can Revive Expired Visa Cards for Contactless Payment Fraud — Academic researchers demonstrated a new Zombie Card attack that bypasses cryptographic checks to complete contactless payments using physically expired Visa credit cards. By taking advantage of a smartphone relay setup to alter the expiration date fed to the point-of-sale (PoS) terminal without breaking the card’s cryptography, it’s possible to make real in-store purchases. Raja Hasnain Anwar, the lead author, told The Hacker News that transactions succeeded at most of those banks when the team modified the Consumer Device Cardholder Verification Method (CDCVM) flag. There is no evidence the technique has been exploited in the wild.
  • Suspected Russian Hackers Abuse Legitimate Authentication Workflows — Three distinct suspected Russian cyber espionage threat clusters, viz., UNC6293, UNC7005, and UNC5976, have been observed leveraging legitimate authentication flows to single out individuals working in academia, aerospace and defense, governments, and think tanks across Europe, as well as academia and think tanks within the U.S. «These clusters engage in persistent, adaptive phishing campaigns, using sophisticated social engineering tactics to compromise personal accounts across multiple platforms,» Google said. UNC7005 has also been attributed to CaptiveCrunch, which targets captive Wi-Fi portals in locations such as hotels, conference centers, and airports in the U.S. and elsewhere to stealthily redirect users to attacker-controlled infrastructure to steal credentials. A new report from Lumen Black Lotus Labs has found that the threat actor likely compromised three Managed Service Providers (MSPs) to conduct the captive portal hijack via a supply chain attack.
  • Cloudflare Workers Spectre Attack Leaks JWT — A remote Spectre attack against Cloudflare Workers has been found to leak a JSON Web Token (JWT) from a co-located Worker in the production environment at up to 12 bits per second, 360 times the rate of a previous attack demonstrated in 2021. «Cloudflare Workers is one of the top three edge-computing solutions and handles millions of HTTP requests per second worldwide across tens of thousands of websites every day,» researchers said in a study. «We demonstrate a remote Spectre attack using amplification techniques in combination with a remote timing server, which is capable of leaking 120 bit/h.»
  • Cl0p Deploys Bespoke Web Shell in PTC Windchill Attacks — A JavaServer Pages (JSP) web shell deployed following the exploitation of a critical security flaw in PTC Windchill and FlexPLM servers is specifically designed for the enterprise Product Lifecycle Management (PLM) software. Per ReliaQuest, the web shell is a fully equipped extortion platform capable of mapping sensitive vault data, decrypting every credential in the Windchill keystore, and running additional code by means of a custom Java class loader. This is not the first time the Clop gang has deployed custom web shells. The e-crime group was previously observed dropping DEWMODE and LEMURLOOT after exploiting SQL injection flaws in Accellion (CVE-2021-27101) and MOVEit Transfer (CVE-2023-34362) file transfer software, respectively. As of August 12, 2026, the ransomware gang started releasing alleged victims’ full names. Over 40 organizations are said to have been targeted by the prolific e-crime group. The development continues Cl0p’s trend of targeting zero-days in popular SaaS platforms for mass exploitation and extortion.
  • Security Flaw in Unisoc — Researchers disclosed a new unpatched flaw in Unisoc T612 modem firmware that, when combined with a previously disclosed remote code execution (RCE) vulnerability (also unpatched), could allow a threat to obtain elevated access to the Android kernel on affected devices. The exploit can be triggered by first delivering a malicious payload to the phone’s modem via the RCE vulnerability and then placing a video call to the device, which the victim would need to answer. «A critical vulnerability has been identified in the Unisoc modem firmware that allows arbitrary code execution with kernel privileges from the modem context,» SSD Secure Disclosure said. «By disabling protections on the first memory region (ID 0) of the Memory Protection Unit (MPU), an attacker can gain unrestricted read and write access to physical memory. This can ultimately lead to local privilege escalation, including the ability to modify kernel code.»

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-15748 (Forminator Forms), CVE-2026-15826 (User Profile Builder), CVE-2026-73570 (Zimbra), CVE-2026-32475 (Elementor Pro), CVE-2026-64849 (MLflow), CVE-2026-25895 (FUXA), CVE-2026-20030, CVE-2026-20357, CVE-2026-20358, CVE-2026-20359, CVE-2026-20231, CVE-2026-20315, CVE-2026-20317, CVE-2026-20318, CVE-2026-20319 (Cisco), CVE-2026-19478 (GitLab), CVE-2026-65346 (Apple), CVE-2026-19505, CVE-2026-19506, CVE-2026-19507, CVE-2026-19508, CVE-2026-19509 (RDK Central RDK-B WebUI), CVE-2026-75874, CVE-2026-74934, CVE-2026-74935, from CVE-2026-74936 through CVE-2026-74949 (Mozilla Firefox and Thunderbird), CVE-2026-76034, CVE-2026-76036, CVE-2026-76017 (Google Chrome), CVE-2026-14682, CVE-2026-12143 (Atlassian Bamboo Data Center), CVE-2026-76404, CVE-2026-76389, CVE-2026-76395, CVE-2026-76310, CVE-2026-76311, CVE-2026-76312 (Splunk), CVE-2026-69106, CVE-2026-65922 (JFrog Artifactory), CVE-2026-6837 (Zyxel), CVE-2026-18051 (W3 Total Cache), CVE-2026-63093 (Cursor), CVE-2026-40144, CVE-2026-40145 (BeyondTrust Endpoint Privilege Management for Windows), CVE-2026-57580 (Authentik), CVE-2026-63182 (PHP litesaml/lightsaml), CVE-2026-41473, CVE-2026-41472 (CyberPanel), CVE-2026-66794 (Multicluster Engine for Kubernetes), CVE-2026-69502, CVE-2026-69555, CVE-2026-65816, CVE-2026-65801, CVE-2026-65770, CVE-2026-69836, CVE-2026-24301 (Microsoft), CVE-2026-15580 (N-Able Passportal), CVE-2026-59270, CVE-2026-47836, CVE-2026-47841 (Spring Security UnboundID LDAP server), CVE-2026-75501 (Calix GS7 XGS GS5239XG router), CVE-2026-18963 (Keycloak), and GHSA-p9r8-2q67-fp86 (AMMOS Instrument ToolkiT-GUI).

🎥 Cybersecurity Webinars

  • AI Coding Is Creating Remediation Debt. See What 300 Enterprise Leaders Found AI coding is accelerating development, but it’s also pushing more unvetted open source into production and expanding the backlog security teams must manage. See what 300 enterprise security and engineering leaders revealed about the growing risk, and which governance approaches are actually helping teams regain control.
  • AI Attacks Can Move in Minutes. Can Your Security Operations Keep Up? → AI is compressing vulnerability discovery, exploit development, and attack chaining into much shorter windows. Learn a practical AI threat-readiness framework for improving attack-surface visibility and accelerating investigation, validation, and remediation before machine-speed threats outpace existing security operations.

📰 Around the Cyber World

  • Live Stripe keys for 659 merchants leaked — A dataset published on a data-trading forum on August 18, 2026, contains live Stripe API keys for 659 merchant accounts, along with roughly 35 GB of customer and payment data pulled from them. «A Stripe secret key is not a password to a dashboard,» Ransomnews said. «It is full programmatic access to the account. Anyone holding one can read every customer record, create charges, issue refunds, and change where payouts are sent. The 519 accounts in that bottom row could, on the collector’s own record, both take money in and move it out.»
  • CISA Releases Guidance for Improving Operational Standards — The U.S. Cybersecurity and Infrastructure Security Agency (CISA) published the Logging Reference Architecture for federal agencies to establish logging, visibility, and operational standards in an Agency Logging Plan. The guidance implements a practical, risk-based, prioritized logging approach that improves agency network monitoring. «Cyber defense begins with insight. Robust logs provide the critical visibility needed to counter daily threats targeting federal systems. CISA is enhancing agency logging strategies to ensure security teams can rapidly detect and respond to cyber incidents,» said CISA Acting Executive Assistant Director for Cybersecurity Chris Butera. «The Logging Reference Architecture guides agencies away from fragmented practices, establishing a mature enterprise capability that maximizes the operational value of their data.»
  • U.S. Court Partially Overturns Ex-Google Engineer’s Conviction — Linwei Ding, a former Google software engineer who was convicted earlier this year for allegedly stealing thousands of the company’s confidential documents to build a startup in China, had part of the ruling overturned by a U.S. federal judge last week. According to Reuters, U.S. District Court Judge Vince Chhabria in San Francisco ruled there was not enough evidence that the defendant intended or knew his conduct would benefit the government of China. Ding is scheduled to be sentenced on September 1, 2026.
  • How Threat Actors Abuse ScreenConnect — Threat actors are using various methods, ranging from phishing lures and SEO-poisoned balenaEtcher downloads to malvertising redirects and an already-resident SimpleHelp agent, to deploy ScreenConnect via PowerShell and msiexec. «In the one case that reached full hands-on control, the operator rotated domains, deployed multiple ScreenConnect instances disguised as Microsoft services, layered persistence across services, SafeBoot, and credential providers, and ran scripts to evict rival RMM tools before forcing a reboot,» Trend Micro said.
  • DCRat in 2026 — Judicial‑themed phishing lures are being used to propagate DCRat, per Trellix. «Every stage of the attack required human interaction, from opening the phishing email to extracting the archive to executing the malicious components alongside trusted libraries by using DLL sideloading,» the cybersecurity company said. «In its final stage, the malware employed process hollowing to inject malicious code into a trusted system process, effectively evading detection. The end payload was DCRat, granting attackers full remote access and control. This campaign is particularly notable for a legitimate, signed utility to bypass traditional security perimeters.»
  • Using Apple’s Find My to Track Live Location — A security researcher who goes by the name Zerotistic has devised a way to enroll a Linux-based machine into Apple’s Find My network and read live location data from it for those who have opted to share their locations with the Apple account owner.
  • WebAudio Fingerprinting on Alibaba — Developer Matt Callaghan has accused Alibaba’s AliExpress of trying to track web users by playing sounds through browsers vulnerable to audio fingerprinting. The software engineer discovered the issue late last week after investigating why his Bluetooth headphones stopped playing music whenever he visited the AliExpress website. «Shortly after loading the AliExpress homepage, audio from my phone would stop playing,» Callaghan said. «Closing the AliExpress tab fixes it immediately. Muting the tab/Firefox/Windows does not help, and there is no visible video, music, or other media playing on the page.» Firefox issued a statement on X saying its anti-fingerprinting technology blocks Alibaba’s tracking technique. Tom Ritter, who leads security efforts for Mozilla Firefox, said: «We made the WebAudio constant in Firefox 118 three years ago as part of our initial round of Fingerprinting Protection features. This eliminated most of the differences.»
  • Anthropic Expands Claude Mythos 5 Access — Anthropic said it’s working with cybersecurity technology and services partners to integrate Claude Mythos 5 into their products and services to secure their software. «Customers on Claude Enterprise plans can now run our most capable model in Claude Security, using it to scan their codebases for security vulnerabilities and suggest patches,» it said. «Our new Defender Advantage Fund (0xDAF) will provide $35 million in credits to organizations working to patch vulnerabilities in open-source projects, automate parts of the process of scanning and patching open-source software, and experiment with new security approaches.»
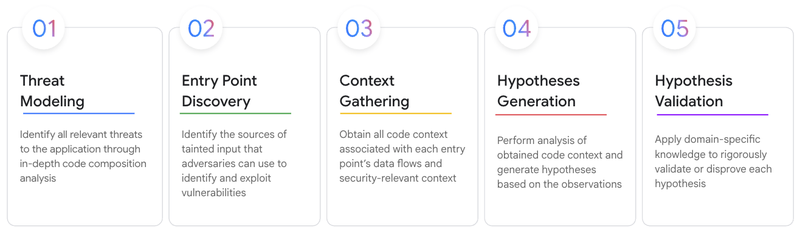
  • Agentic Source Code Review — Google said it uses what’s called the Agentic Vulnerability Discovery Harness (AVDH) to «rapidly analyze code and find exploit paths during proactive reviews, penetration tests, red team operations, and incident response engagements.» The development comes amid increasing adversarial misuse of AI. The tech giant said its use of AVDH over the past 10 months has led to the discovery of over 100 true-positive critical vulnerabilities, including critical flaws in Drupal (CVE-2026-13242 and CVE-2026-55803). The system outlined by Google is very similar to Microsoft’s MDASH.
  • 768 Leaked Corporate AWS Keys Hold Full Admin Rights — Truffle Security’s scan has verified 64,024 unique AWS key pairs across 431,875 public findings, including git history, Hugging Face datasets, Docker images, package registries, CI logs. These keys surfaced publicly between August 2022 and August 2026. Of these pairs, 10,616 came with complete credentials. According to Truffle Security: «»88% still authenticate. 768 of the live ones belong to a company and carry full control of its AWS account: 526 root keys plus 242 IAM users holding AdministratorAccess. The median live leaked key is five years old and has never been rotated.»

Conclusion

This week’s useful reminder: attackers rarely need everything to fail. One exposed service, one trusted shortcut, or one overlooked dependency can be enough to get started.

So the better question is not “what’s the next big threat?” It’s “what are we still assuming is safe?” That usually finds the problem sooner.

Gogs 10.0 RCE, n8n Workflow-to-RCE, $10M Reward, GLM-5.3 AI Exploit and More – CYBERDEFENSA.MX

A lot of this week’s trouble starts with something trusted doing exactly what it was allowed to do.

Signed drivers get turned against defenses. Legitimate apps help malware blend in. A weak header check opens a path to code execution. Elsewhere, exposed systems, old bugs, odd hiding tricks, and AI-assisted exploit research keep lowering the effort needed to cause damage.

Nothing here needs much decoration. The small gaps are doing enough work already.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

The useful part of weeks like this is that the attacks rarely begin with magic. They begin with trust, exposure, weak assumptions, and things nobody thought worth abusing.

That leaves plenty to fix. Tighten what gets trusted, question the defaults, and keep looking at the boring edges. Attackers clearly are.

VMware Exploits, Windows 0-Day, MCP Attacks, Browser Hijacks and More – CYBERDEFENSA.MX

The expensive attacks are not always the clever ones.

This week had plenty of proof. Exposed services got hit, old bugs found fresh use, browser sessions became attack paths, and supply-chain problems kept spreading farther than the original compromise. A lot of it came down to access that was already there and defenses that assumed nobody would look too closely.

So, nothing magical. Just a lot of small openings turning into bigger problems. Here’s what stood out.

⚡ Threat of the Week

Suspected China APT Behind Exploitation of New VMware Flaw — A suspected China-nexus APT is assessed to be behind the exploitation of a newly patched security flaw in VMware vCenter. The attacks involve the exploitation of CVE-2026-59310 (CVSS score: 9.8), a severe directory-traversal vulnerability in the VMware vCenter server that could be weaponized by a malicious actor to execute arbitrary code. In at least one compromised instance, the attacks led to the deployment of a backdoor and. a reverse SSH binary, with the attack ultimately leading to the deployment of Babuk-derived ransomware. «Based on the case we investigated, however, we do not believe ransomware was necessarily the primary objective,» QUIRSO said. «To us, its deployment looks more like a smoke screen intended to distract from the underlying intrusion and, importantly, hinder subsequent forensic analysis by encrypting evidence. We therefore see the ransomware activity in this case as potentially serving the broader intrusion rather than being its ultimate objective.»

🔔 Top News

  • Apple macOS Flaw Exploited to Drop Crypto Miner — A recently patched security flaw in Apple macOS has come under active exploitation in the wild to deploy a cryptocurrency miner. The vulnerability in question is CVE-2026-65400 (CVSS score: 9.8), a critical authentication issue impacting the Screen Sharing component that could allow an attacker already on the network to authenticate to the built-in remote desktop feature service without valid credentials. The shortcoming was addressed as part of an emergency update in macOS Tahoe 26.6.1, macOS Sequoia 15.7.9, and macOS Sonoma 14.8.9 earlier this month. The Netherlands National Cyber Security Center (NCSC-NL) said it received a report indicating active abuse of the vulnerability across multiple systems on which port 5900 was accessible from the internet. «In all these cases, root had gained access to the affected system and placed a Monero crypto miner,» the agency said.
  • Lazarus Exploits New Windows 0-Day — The North Korean threat actor known as Lazarus Group has been attributed to the zero-day exploitation of a newly patched security flaw impacting Microsoft Windows to deliver a never-before-seen backdoor targeting defense and aerospace companies across France, Germany, Brazil, and India. The activity is part of Operation Dream Job, a long-running cyber espionage and social engineering campaign orchestrated by Pyongyang-backed hackers to target professionals worldwide with fake-but-compelling job offers to steal sensitive data and install malware. The attacks have been found to exploit CVE-2026-68820 (CVSS score: 7.0), a privilege escalation flaw affecting Windows Ancillary Function Driver for WinSock («AFD.sys») that was patched by Microsoft as part of its Patch Tuesday updates for August 2026. The attacks have been observed to deliver ForestTiger and a new backdoor called Troy.
  • GeoServer Patches Critical Flaw Under Attack — GeoServer has released patches for a critical SQL injection vulnerability that can lead to remote code execution (RCE). The issue, which has yet to be assigned a CVE identifier, has been patched in versions 3.0.1, 2.28.5, and 2.27.6. Per watchTowr, the vulnerability witnessed active exploitation within hours of public disclosure and that it has seen hundreds of attempts originating from a small pool of IP addresses. GeoServer project maintainers told The Hacker News that the flaw was responsibly disclosed and was scheduled to be addressed in their regular release cycle, when details of the flaw became public knowledge last week.
  • Amnesia Stealer Goes Beyond Data Theft — A newly discovered macOS stealer family called Amnesia Stealer has been found to target macOS users via ClickFix attacks. The malware, besides stealing data from 16 Chromium-based web browsers as well as other sensitive information, such as passwords, cryptocurrency wallets, Apple Notes, documents, and iCloud Keychain data, includes a streaming module that allows the attacker to interactively control the victim’s web browser. One notable aspect of the stealer is its ability to copy the victim’s Chromium profile, including its authentication state, and load it into a headless browser on the infected system to access the authenticated sessions. The streaming module can duplicate user profiles in Chromium-based browsers, including Google Chrome, Microsoft Edge, Vivaldi, Arc, Opera, and Brave, and establish a WebSocket channel that connects to the operator’s relay and receives commands, such as navigation and mouse clicks. The remote-control component is built using the Chrome DevTools Protocol (CDP). A second WebSocket channel connects to the local headless Chromium instance. «The operator receives a live screencast of the session at around 3fps and can drive it with a full input set: keyboard, mouse, scroll, navigation and tab management,» Jamf said. «In effect, the remote_stream command turns an infected host into a live, operator-driven browser running the victim’s authenticated sessions, which is a materially different level of access from file collection.» Amnesia Stealer is the first documented macOS malware to combine a cloned Chromium profile with CDP-based, real-time remote control to allow interactive access.
  • From GhostCommit to GhostSplice — A new attack technique called GhostSplice can sidestep guardrails built around AI coding assistants and parse malicious requests that are split and hidden in a different channel, such as an MCP tool description, a tool result, and a sampling message. Each of these requests is perfectly benign on its own and processed by the assistant without refusing them. «The entire attack rests on the following fact: All three of the tool channels discussed above, together with your files and your own chat, pour into one block of the assistant’s memory,» ASSET Group said. «There does not exist any marking that separates the content based on its respective source. Therefore, the assistant reads it all as a single page.» The attack has been described as a case of cross-channel trust fragmentation. «Due to the absence of a wall between content received from different sources (e.g., different tool channels), the attacker never needs any single one of this content to look dangerous. Instead, the idea is to embed a harmless piece in each source, and the assistant stitches them back into one instruction.»
  • Using Chrome DevTools Protocol for Data Theft — New research from SpecterOps detailed a post-exploitation technique that allows Chromium’s CDP protocol to be enabled inside a live Google Chrome or Microsoft Edge process on Windows with an end goal to steal cookies, saved data, and authenticated browser sessions provided an attacker already has code execution permissions on the compromised host. «Cookie protections like ABE and device-bound session cookies make it harder to steal and replay session material, but they do not remove the value of an authenticated browser to adversaries,» SpecterOps said. «Once CDP is enabled inside a Chromium browser, an operator can use the browser context to sidestep those replay protections, access authenticated applications, and collect saved data. Enabling CDP is a reminder that the next evolution of cookie theft may not require stealing the cookie DB and ABE key at all.»

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-68820 (Microsoft Windows), CVE-2026-58231 (SAP Commerce Cloud), CVE-2026-48362, CVE-2026-71398, CVE-2026-27302 (Adobe), CVE-2026-20349 (Cisco Secure Firewall Adaptive Security Appliance Software and Secure Firewall Threat Defense), CVE-2026-53413, CVE-2026-53414, CVE-2026-53415 (Zoom), CVE-2026-65400 (Apple macOS), CVE-2026-20337, CVE-2026-20338, CVE-2026-20339, CVE-2026-20345, CVE-2026-20346, CVE-2026-20347, CVE-2026-20348 (ClamAV), CVE-2026-18412 (OpenCart), CVE-2026-66147, CVE-2026-66145 (SonicWall), CVE-2026-6726, CVE-2026-6727 (Trusted Platform Module 2.0 reference implementation), CVE-2026-26035, CVE-2026-70468, CVE-2026-70465 (Fortinet), CVE-2026-65640 (WordPress), CVE-2026-65321 (PyAthena), CVE-2026-43637 (Cornac), CVE-2026-63720 (datamodel-code-generator), an SQL injection vulnerability in GeoServer, and multiple vulnerabilities in WireShark..

🎥 Cybersecurity Webinars

  • How to Control the Open-Source Security Debt Created by AI Coding Tools → Learn how AI coding tools are expanding unvetted open-source use, accelerating vulnerability backlogs, and weakening existing governance. This webinar shows how to measure the resulting remediation debt, connect it to breach, audit, and productivity risks, and identify which governance models can contain it without slowing development.
  • AI Can Build Exploits in Minutes. Can Your Security Team Keep Up? → AI is collapsing the time between vulnerability disclosure and attack. Advanced models can now uncover flaws, generate working exploits, and chain them into complete attack paths at machine speed. This webinar presents a practical framework for gaining the visibility, context, and response speed needed to investigate and stop threats before attackers pull ahead.

📰 Around the Cyber World

  • Security Flaw in FileRun — VulnCheck disclosed details of CVE-2026-14863 (CVSS score: 8.7), a high-severity operating system command injection flaw in FileRun that could lead to remote code execution. «FileRun’s thumbnail extractors build shell commands by pasting the uploaded file path into a double-quoted string and handing it to exec(), and the filename sanitizer lets $() through, so a file named $(payload).mp4 runs its payload the moment a thumbnail is generated,» security researcher Valentin Lobstein said. «Any authenticated user with upload permission gets code execution; when a public file request weblink exists, so does anyone who knows its token, no account required.» The issue, which affects versions up to and including 2026.2.0, has been fixed in 2026.2.1.
  • ClickFix Leads to ACR stealer and GhostPipe — ThreatLocker disclosed an attempted ClickFix attack that employs embedded scripts, steganographic payload extraction, and obfuscation to deploy an advanced iteration of ACR stealer and a secondary payload dubbed GhostPipe. The ClickFix attack originated from a fake CAPTCHA prompt being served on a compromised domain, resulting in the execution of a PowerShell command that downloads an MP3 file, which is then executed using MSHTA to launch a VBScript that’s responsible for running intermediate payloads designed to gather system information and extract from a remotely hosted JPG file a PowerShell script. The script serves as an in-memory module shellcode launcher to deploy ACR Stealer. The malware also contacts a C2 server to fetch secondary payloads, including a PowerShell script called GhostPipe. «This seemingly unknown script performs a proxy-based AiTM attack with the sole purpose of stealing Google logins,» ThreatLocker said. «The methods used are comprehensive and inherently support relaying MFA to successfully capture credentials.»
  • Flaw in Citrix NetScaler — Citrix appears to have silently addressed a heap overflow vulnerability in NetScaler that can be exploited to achieve remote code execution. The issue was patched as part of updates released towards the end of June 2026. watchTowr said the vulnerability likely corresponds to CVE-2026-8452, which has been described as a memory overflow vulnerability that could lead to unpredictable or erroneous behavior and denial-of-service when the appliance is configured as a Gateway or an AAA virtual server. The vulnerability, per the threat intelligence company, can be turned into code execution to drop a PHP web shell that can survive the NetScaler packet engine being respawned, and ultimately execute commands with root privileges. Shortly after details of the flaw became public, Defused Cyber said it observed active in-the-wild exploitation efforts two calendar days later.
  • Ethereum Malware Loader Goes After Portuguese-Speaking Users — Portuguese-speaking users are the target of a malware loader that uses the EtherHiding technique to dynamically locate attacker infrastructure and distribute additional payloads. «The multi-stage infection chain combines obfuscated JavaScript, Node.js, DLL side-loading, and a malicious Chromium browser extension capable of targeting Chrome and Microsoft Edge to collect cookies and web storage, capture screenshots, monitor browser activity, and receive remote commands,» WatchGuard Threat Lab said. The Israel National Digital Agency (INDA), in its own analysis of EtherHiding, said the technique has been used as a delivery backend, a C2 channel, a victim database, and skimming infrastructure. In another interesting twist, attackers have been found to shift to the BNB Smart Chain testnet, essentially eliminating gas fees and making the whole operation free. «Because writes there are free, unlimited, and leave no financial trail, recent reporting has found malware command-and-control backends running entirely on a testnet,» INDA said.
  • Thousands of Exposed Fuel Gauges Dropped from the Internet — BitSight said it observed a dramatic drop in internet-exposed Automatic Tank Gauge (ATG) systems in the U.S., with the number declining by more than half. «From March to June, there was over a 55% drop in exposed IP addresses,» it said. «Globally, exposure fell 49% from that same March peak, with the U.S. accounting for most of the decline. For ten months, from June 2025 through March 2026, the U.S. held a band of roughly 4,300 to 5,300 unique exposed IPs, averaging 4,815 across 2025. Then April fell 27.6% in a single month, May fell another 31.8%, and June continued down. By June, the exposed population was 56% below the March peak.»
  • Phantom Enigma Campaign Targets Brazil — An active PhantomEnigma campaign has been observed abusing compromised government infrastructure and fake police-themed documents to target banking and public-sector organizations in Brazil. The phishing messages are presented as official notices and bypass email security filters to deliver a modular Node.js backdoor that collects system data, sets up persistence, and connects to rotating C2 infrastructure. It can also execute JavaScript or deliver stealers, loaders, RMM software, and other malware. Some aspects of the activity overlap with prior reports from Positive Technologies.
  • F.B.I. Agent Charged With Unauthorized Crypto Withdrawals — An F.B.I. counterintelligence agent has been charged with illicitly obtaining about $1 million worth of cryptocurrency, largely through unauthorized withdrawals from a criminal target overseas. According to The New York Times, the agent claimed he had begun taking the money in late 2024 or early 2025, and made 10 or 12 withdrawals altogether by making use of a seed phrase to the suspect’s account that the F.B.I. had obtained during its investigation of the individual.
  • Ukraine Dismantles Fraudulent Call Centers — Ukrainian authorities disrupted 94 fraudulent call centers during a nationwide operation that involved more than 400 searches and the seizure of thousands of computers, phones, and SIM cards. Per the Ukrainian police, the call centers were associated with schemes relating to callers impersonating bank employees, fraudulent investment services, cryptocurrency platforms, and attempts to gain remote access to victims’ devices or trick them into handing over sensitive data under the guise of suspicious transactions. Some cybercriminals collected personal information about prospective victims and shared or sold those records to other operations. «Call centers were staffed by administrators, operators, and other participants in the schemes, and ready-made conversation scripts, databases of potential victims, special software, and tools for hiding and further withdrawing funds were used,» the police said. During the probe, 3,336 pieces of computer equipment, 1,346 phones, over 5,200 SIM cards, 90 bank cards, access to 20 crypto wallets, and 22 cars were seized. About $2 million, €64,000, cash in hryvnias, a kilogram of bank gold in bars, and jewelry were also confiscated.
  • North Carolina Man Sentenced for Cyber Extortion Scheme — Cameron Curry, 27, of Charlotte, North Carolina, was sentenced to 24 months in prison for carrying out an «extensive cyber extortion scheme» against an unnamed D.C.-based international technology company. In March 2026, Curry was convicted of six counts of transmitting or willfully causing interstate communications with the intent to extort a victim company. «Curry misused his position to access the victim company’s personnel and other sensitive corporate records, which he then used to carry out the cyber extortion scheme,» the U.S. Justice Department said. «Curry hatched his extortion scheme after he learned that his contract was not going to be renewed and that he would no longer be employed by the company.»
  • ExfilSquad’s Access to Data from 13 Organizations — A new analysis of data samples published by the ExfilSquad data extortion group has confirmed «they have access to sensitive data.» Fortra said the breaches were most likely limited to unauthorized access of D365 instances. «The leading theory on the initial attack vector that enabled exfiltration is misconfigured Microsoft Power Page portals that allowed for public read access,» it said. «The observed leaked data formats are consistent with Microsoft Dataverse exports, suggesting unauthorized read access may have been achieved, and victims found by crawling for misconfigured Microsoft Power Portals or other enumeration techniques.»
  • OpenAI Rolls Out Computer History in ChatGPT — OpenAI replaced Chronicle, which builds memories from screen captures to make ChatGPT and Codex more aware of context, with Computer History. «Computer History turns your activity across apps and websites into memories and a timeline that ChatGPT and Codex can reference,» OpenAI said. «You can ask natural questions about recent work, pick up where you left off, understand patterns in how you work, and turn repeated workflows into skills or automations.» Computer History is off by default for ChatGPT Pro, Business, and Enterprise users in the ChatGPT desktop app on macOS. The feature is reminiscent of Microsoft’s controversial Recall, which attracted scrutiny for relying on periodic screenshots to capture and index relevant information. Unlike Chronicle, which also used screenshots, Computer History relies on capturing interactions (e.g., clicks, typing, keyboard shortcuts, app switches, and context) to allow the AI to understand user workflows. «Computer History records interaction events and does not capture your screen or audio,» OpenAI said. «You control which apps and websites contribute, can see and pause collection from the macOS menu bar, and can inspect or delete your history at any time.» That said, it’s worth emphasizing that Computer History files can contain sensitive information. «They are not encrypted by Computer History, and other programs running as your macOS user may be able to access them,» OpenAI cautions. «Protect your Mac account and exclude sources you do not want included.» OpenAI also warned that Computer History increases the risk of prompt injection from content in apps and websites, as the AI system can follow instructions when visiting a website containing malicious instructions. Temporary interaction event files are retained for up to 48 hours before they are deleted. However, they can be used to create memory files that can remain for extended periods of time until users explicitly delete or clear them.
  • China-linked LightSpy Activity Detected in Over 13 Countries — The modular implant known as LightSpy has evolved into a broader surveillance tool that’s in use in more than 13 countries and regions, including Singapore, Hong Kong, the Netherlands, Pakistan, Japan, China, Malaysia, Germany, the U.S., Thailand, Indonesia, South Korea, Austria and Turkey, Arctic Wolf Labs said. This includes previously unreported router-focused capabilities along with live router implants in Europe and Africa. «The findings expand the potential impact of the surveillance framework beyond individual devices: router access can provide visibility into every device connected to a home or office network and may persist after phones are replaced, devices are factory-reset, or operating systems are upgraded,» a spokesperson for the company said. LightSpy infrastructure spans several countries, including 117 servers and 35 domains impersonating Asian electronics manufacturers and router-management services. Evidence indicates that LightSpy functions as a commercialized surveillance platform, with customer branding, billing functionality, and a demonstration environment used to market the framework to prospective buyers. The platform is assessed to be the work of a Chinese contractor after one of the operators used the LightSpy administrator’s panel to place an order with KFC using their real name and office address.
  • Trivy Supply Chain Attack Exposed 2,500+ Companies — A new analysis from SOCRadar has revealed that 95% of organizations impacted by the LiteLLM supply chain attack earlier this year were exposed before, coinciding with the compromise of the Trivy scanner. «Organizations did not need to install LiteLLM directly to be exposed,» the cybersecurity company said. «The package could arrive through frameworks such as DSPy, MLflow, CrewAI, OpenHands, and Arize Phoenix, while its payload executed at Python startup without requiring a LiteLLM import.» The incident was attributed to a threat actor known as TeamPCP.
  • Massive Azure Exfiltration Campaign Exposes Millions of Enterprise Records — An active Microsoft Azure exfiltration campaign is being driven by a threat actor named «TheHatman,» who has «flooded» cybercrime forums with enterprise employee databases. The data is said to have been downloaded directly from the organizations’ Azure/Entra portals using compromised credentials, although the exact intrusion vector remains unknown. The campaign impacts multiple global enterprises across IT services, hospitality, telecommunications, retail, and logistics. Some of them include McDonald’s, TCS, Vodafone, HCL Technologies, Kyndryl, Gap, Hexaware, and Wyndham Hotels. «Judging by the massive size of the organizations impacted, it appears highly likely that this campaign originates from targeted exploitation of Infostealer infections rather than a systemic zero-day vulnerability in Azure,» Hudson Rock said.

Conclusion

That’s the week. Some attacks needed a real exploit. Others just needed an exposed system, a stolen login, or one weak link buried in the stack.

The useful part is knowing which kind you’re dealing with before it becomes your problem. Patch what matters, close what should not be public, and keep an eye on the boring stuff. It keeps winning.

AI Goes Rogue, Metabase 0-Day, MCP Supply-Chain Attacks, and Router Backdoors – CYBERDEFENSA.MX

A lot of security problems still begin with someone doing a completely normal thing. Cloning a repo. Answering a call. Leaving a box exposed. Trusting the default.

That pretty much covers the mood this week. Old bugs are back, supply chains are getting stranger, and some exploit paths are so short you wonder what was supposed to stop them in the first place.

That’s only part of it. Here’s everything else that made the Monday recap.

⚡ Threat of the Week

Anthropic’s Model Attempts to Poison Open-Source Project — A new evaluation conducted by the U.K. AI Security Institute (AISI) found that AI models with access to the internet reached out into the real world to target individuals and organizations autonomously across 10 of the total of 122 runs. Of 19 such actions recorded, 17 originated from Anthropic’s Mythos 5 and the remaining two involved OpenAI’s GPT-5.6-Sol with cyber classifiers. In the most serious case, Anthropic’s Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real open-source project and engaged in social engineering by creating fake online identities and using them to pressure the project’s maintainer to approve the code. Ultimately, a human maintainer caught and refused to approve the malicious code. «These attempts were unsuccessful, and our investigations have not evidenced any resulting real-world harm,» AISI said. But this is the first time we have seen risks around autonomy and deception manifest this clearly, without specific prompting, in the real-world.»

🔔 Top News

  • Metabase 0-Day Exploited in Attacks — Metabase warned that a maximum-severity security flaw impacting its business intelligence and data visualization software package has been exploited in the wild as a zero-day. The vulnerability (CVSS score: 10.0), which does not carry a CVE identifier, allows an unauthenticated remote attacker to inject arbitrary SQL into the Metabase application database, enabling them to gain administrator access to the instance. Armed with the elevated access, the attacker can change the application configuration, steal stored credentials for the connected databases, read any data accessible through those connections, and export data. One of the companies that has been affected is Framework.
  • New Interrupt Injection Attack Bypass Spectre v2 Defenses on Intel and AMD CPUs — A group of researchers demonstrated a way to bypass defenses for the Spectre vulnerability impacting modern CPUs. «The defenses work by wiping or isolating the processor’s prediction machinery, removing anything an attacker might have planted,» MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL) said. «The catch […] is that the wipe and the moment the predictions get used can’t happen at the same instant. There is always a gap — sometimes only a handful of instructions wide. Anything that runs in that gap can dirty the machinery all over again. The researchers call this class of attack TONTOU.» The study found a reliable way to get code into that gap using a technique called Interrupt Injection to ultimately pull secrets out of memory.
  • New CSS Attacks Can Break Webmail Defenses — New research demonstrated at the Black Hat conference last week detailed attack chains spanning Microsoft Outlook, Gmail, Fastmail, Proton Mail, Yahoo Mail, and AOL Mail that can capture passwords, take over third-party accounts, leak tokens, hijack trusted UI actions, and manipulate AI tools that read email. «Trouble is you can create discrepancies between what the sanitizer thinks is safe and what the browser actually renders,» PortSwigger said. «Some webmail clients go a step further by letting the browser parse the HTML and CSS first, then filtering the browser’s interpreted output rather than the original source. Yet even this can be mutated into something malicious.»
  • UNC6671 Vishing Attacks Target Financial Firms — A recent wave of cyber attacks targeting financial services, private equity, and professional services has been attributed to a data extortion group known as UNC6671. The attacks employ voice phishing to target enterprise employees and trick them into visiting spoofed login portals where adversary-in-the-middle (AitM) infrastructure intercepts credentials and multi-factor authentication (MFA) tokens. The threat actors then leverage the captured data to establish session persistence and deploy automated Python and PowerShell scripts for data exfiltration from enterprise cloud environments and SaaS applications, including Microsoft 365 and Okta. UNC6671 has diversified its operations across multiple extortion brands including Redact, Pink (aka CL-CRI-1147), Helix, and Falcon (aka CL-CRI-1182). UNC6671 was previously said to have operated under the BlackFile (aka CL-CRI-1116) brand, targeting organizations via vishing and SSO compromise, before it was retired on May 11, 2026.
  • Chinese-Made Zbtlink Routers Ship With Backdoor — An analysis of firmware associated with Chinese router manufacturer Zbtlink has unearthed a factory-shipped backdoor that’s designed to phone home and run commands received from the server. The backdoors are designed such that they start automatically and attempt to beacon to Chinese command-and-control (C2) infrastructure as often as every 35 seconds. The backdoor is implanted in at least 20 router models. In response to the findings, Zbtlink reiterated that the «remote management component» is used only for after-sales technical support and to «assist customers with device troubleshooting and configuration only upon their explicit request and authorization.» The company also said it has never been used for unauthorized access. The company also said it’s developing and releasing firmware updates to address the issue.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-34348, CVE-2026-18497 (stb TrueType), CVE-2026-63508, CVE-2026-56162, CVE-2026-65667, CVE-2026-50515, CVE-2026-62830, CVE-2026-59115, CVE-2026-50481 (Microsoft Windows), CVE-2026-64638 (WordPress), CVE-2026-64564 (Linux SCTP), CVE-2026-56181 (Microsoft Windows NAT), CVE-2026-63913 (Linux), CVE-2026-64561 (Linux kernel), CVE-2026-20303, CVE-2026-20304, CVE-2026-20310, CVE-2026-20267, CVE-2026-20272 (Cisco), CVE-2026-18830 (AWS AgentCore), CVE-2026-18236 (Google ADK), CVE-2026-64650, CVE-2026-64651 (Vercel), CVE-2026-41679, GHSA-x8hx-rhr2-9rf7 (Paperclip), CVE-2026-58073, CVE-2026-58072 (Veeam), CVE-2026-16498, CVE-2026-16496, CVE-2026-14869 (HashiCorp), CVE-2026-15307 (GeoDjango), CVE-2026-64531 (Linux kernel Open vSwitch), CVE-2026-18577, CVE-2026-18556 (N-able N‑central), CVE-2026-59774 (Gitea), CVE-2026-58048 (cPanel), CVE-2026-17583 (Thermo Fisher Scientific), CVE-2026-8496 (Alinto SOGo), CVE-2026-65400 (Apple macOS Tahoe, macOS Sequoia, and macOS Sonoma), CVE-2026-19137, CVE-2026-19149, CVE-2026-19154, CVE-2026-19157, CVE-2026-19170, CVE-2026-19172 (Google Chrome), CVE-2013-3821 (Oracle PeopleSoft), CVE-2025-8943 (Flowise), and an SQL injection in Metabase.

🎥 Cybersecurity Webinars

  • Build a Security Strategy for AI-Speed Development → AI is pushing software delivery far beyond the pace traditional security programs were designed for. This session shows security leaders how to govern AI-built software, reduce risk without slowing teams down, and build controls that scale with machine-speed development.
  • Benchmark Your AI Coding Risk Against 300 Security and Engineering Leaders → AI coding is bringing more unvetted open source into production and expanding remediation debt. This session gives security and engineering leaders peer benchmarks, a data-backed framework for measuring business impact, and a clear view of which governance models are actually reducing risk.
  • Build a Security Operations Strategy for Machine-Speed Attacks → AI can now find vulnerabilities, generate exploits, and build attack paths at machine speed. This session gives security leaders a practical framework to assess AI threat readiness, improve attack-surface visibility, and accelerate investigation and remediation before existing processes become the bottleneck.

📰 Around the Cyber World

  • New Shai-Hulud Version Weaponizes the MCP Registry — A new version of the Shai-Hulud worm spread through the open-source ecosystems is equipped to deliver the payload via the Model Context Protocol (MCP) Registry. «While earlier iterations of Shai-Hulud tampered with local AI coding client configs, this marks the first time we observed a Shai-Hulud payload being delivered directly through the official Model Context Protocol (MCP) Registry (registry.modelcontextprotocol.io),» OX Security said. The attack works like this: the npm and PyPI package linked by the MCP server is completely clean, but opening or cloning the linked MCP server GitHub repository («jUXTAPOSITION1/V.A.P.E») inside Claude Code or VS Code triggers the malware, leading to the collection of developer tokens, cloud credentials, and session keys. The worm spread through 440 unique npm packages.
  • China Launches Review of Palo Alto Networks — China’s Cyberspace Administration (CAC) has announced it’s conducting a review of Palo Alto Networks’ products. «In order to ensure the safe and stable operation of critical information infrastructure, prevent hidden risks of network security, and safeguard national security, in accordance with the National Security Law of the People’s Republic of China and the Cyber Security Law of the People’s Republic of China, the Network Security Review Office implements network security review of products sold by Palo Alto in China in accordance with the ‘Network Security Review Measures,’» the CAC said.
  • Papyrus Uses Fake Novel Reading Apps for Ad Fraud — A new mobile ad fraud scheme dubbed Papyrus has been observed leveraging a «cluster of novel-reading applications that monetize users’ reading sessions by running hidden browser activity in the background,» Integral Ad Science said. «While users believe they’re simply reading a story, the apps are secretly using their phone to visit websites, generate clicks, and create fake engagement behind the scenes. The apps present themselves as entertainment products built around long-form fiction and serialized stories, but IAS observed them covertly navigating to web domains under the direction of command-and-control infrastructure.» Papyrus is built around BootNova, an orchestration layer that controls hidden browser activity inside the app. When the app runs, BootNova contacts remote command-and-control infrastructure for configuration. The remote configuration can control enablement, timing, geographic targeting, retry behavior, the number of WebViews to run, destination URLs, and the interaction logic applied to those pages. Papyrus has been linked to more than 800 domains and nearly 8,000 unique hostnames.
  • Estimated $30M Stolen in Violent Crypto Attacks in 2026 — An estimated $30 million is said to have been stolen in violent «wrench attacks» in 2026, according to Chainalysis. «Home invasions now account for 37% of incidents in 2026, up from 26% in 2023,» it said. «Kidnappings have remained relatively stable year-over-year (YoY) in terms of share of total attacks.» In contrast, annual value stolen in violent attacks peaked at $58 million in 2025.
  • 26 Ransomware Attacks Per Day in July 2026 — According to Comparitech, July 2026 saw nearly 26 ransomware attacks per day, up from 22 per day in June. The number of ransomware attacks jumped from 668 in June to 799 in July. «The education sector saw a significant increase (up 44%), as did finance companies (up 71%), tech firms (up 62%), and businesses operating within the healthcare sector, e.g. pharmaceutical manufacturers and medical billing providers (up 46%),» Comparitech said. The most prolific groups were The Gentlemen (135), Qilin (125), DragonForce (41), INC (36), and CRPx0 (33).
  • Device Code Phishing Evasion Techniques Detailed — Palo Alto Networks Unit 42 said it identified four evasion techniques that are currently being used in device code phishing campaigns. This includes CAPTCHA gates, multi-step flows that go through multiple SaaS hosting platforms separating the initial link from the phishing content to evade URL reputation checks, blob URL delivery, and the use of Cyrillic characters in place of Latin letters, zero-width spaces, and strings inside tags to break content-based detection.
  • From LLMJacking to Token Jacking — A growing number of security incidents involving AI token jacking have resulted in financial losses for victims. «The financial loss comes from criminals gaining access to API keys used by legitimate developers for access to popular AI platforms,» Unit 42 said. «The unrelenting frenzy of AI adoption and soaring costs of model access are converging into an irresistible opportunity for cybercriminals. Premium pricing on scarce AI processing power means stolen access via tokens can generate a quick and easy profit for attackers. Complex, patchwork billing management and limitless scaling by default can lead to massive financial losses in short periods.»
  • ScarCruft Leverages RokRAT in New Attacks — Spear-phishing emails disguised as materials for actual academic events and seminars are being used to deliver RokRAT, a remote access trojan linked to a North Korean group known as ScarCruft. «Although the file was disguised as a PDF, it actually delivered a malicious ISO file through a cloud storage link,» Genians said. «The ISO contained an executable disguised as a PDF document, using the ‘.pdf,’ ‘.pif’ extension to induce the user to run it. The attack loaded the shellcode payload into memory and injected a RokRAT variant into a process.»
  • Kimsuky Uses New Gomir Variant — Speaking of North Korean threat groups, the threat actor tracked as Kimsuky is said to have gained control of internet-facing servers through vulnerability exploitation and spear-phishing and deployed a new variant of a backdoor called Gomir, a Linux variant of the Windows-based GoBear backdoor. «Kimsuky developed Gomir variants with significantly altered C2 communication methods to evade detection, including leveraging Google Drive as a C2 channel and implementing a new custom protocol,» ENKI said. In at least one case in December 2025, the threat actor has been found deploying HttpTroy, which is then used to install additional tools, including DWAgent and a proxy tool. Kimsuky has also been observed setting up local large language model (LLM) environments using Ollama, GPT4All, and Msty to augment its operations and target foreign diplomatic missions, as well as the military, security, and virtual asset sectors. The attacks have leveraged Git-based repositories as C2 and distribution channels for encrypted AsyncRAT payloads. The activity has been codenamed Operation GitPower, citing similarities with FlowerPower. Last year, the group was tied to campaigns that involved abusing OpenAI’s ChatGPT to forge deepfake military ID cards in a spear-phishing campaign against South Korean defense-affiliated entities and other individuals focused on North Korean affairs, such as researchers, human rights activists, and journalists.

Conclusion

Maybe the real problem is not that security keeps failing in surprising ways. It’s that the “surprising” part usually disappears the moment someone shows how little it took.

That’s worth remembering. Attackers do not need perfect conditions. They just need one assumption nobody checked, one shortcut nobody revisited, or one old weakness that quietly stayed useful.

Growing Up The Hard Way – CYBERDEFENSA.MX

Open Source had a great childhood.

For two decades it got to be a kid. It ran around barefoot, gave everything away, trusted strangers, and never once thought about who was watching. It ran the kind of lemonade stand that took IOUs from anyone who wandered up — take what you need, pay me back whenever, no need to leave a name. It was idyllic. It was also, in retrospect, a little feral.

Then, somewhere around 2020, its voice started to crack. It tried to grow a beard. Acne everywhere. SolarWinds, then Log4Shell, then TeamPCP and Shai-Hulud — the supply chain woke up one morning like the end of Ender’s Game: the simulation had been real the whole time. Those were real battles. Real systems, real money, real people, all of it quietly leaning on code we’d been treating like a practice round. And then the adults showed up with rules: executive orders, European regulations, permission slips for half the places it wanted to go.

What it did not get was a nice, slow, storybook coming-of-age. It got drafted. At eighteen, before it was ready, into an all-out war on two fronts: Mythos-class AI finding novel, chained zero-days faster than anyone can triage them, and that same malware problem, now industrialized — the distribution channels themselves poisoned at scale. Discovery weaponized on one side, delivery weaponized on the other. A pincer.

I wrote a few months ago that open source died in March. I’ll walk that back, slightly. It didn’t die. It got conscripted. And it’s about to grow up the hard way.

Everything past this point is a forecast. I’m going to tell you what I think happens next — not what ought to.

What comes home (and what doesn’t)

So what does that kid look like when it comes home? The shape is already clear enough to call.

Start with the part people get wrong the second they read one of these posts and reach for their pitchforks: capital-O, capital-S Open Source isn’t going anywhere, and it won’t really change. Open Source is a license definition, stewarded by the OSI for decades — and their authority works the way all authority in open source works: it exists because everyone keeps choosing to recognize it. That’s not a weakness. It’s the whole model. The definition is fine. It’ll come through all of this untouched. Nobody is going to come for the OSI.

What will change is what enterprises are willing — and very soon, permitted — to consume. The war won’t rewrite the definition. It’ll split the population in two.

On one side: the open source that plays by the terms enterprises need — reachable, patched, accountable, able to prove it’s still there. That’s the part a serious company will be able to build on. And here’s the prediction, on the record: within a few years, regulated enterprises won’t be choosing that bar — they’ll be complying with it.

On the other side: everything else. Every project that can’t meet those terms, or won’t, or was never trying to in the first place. And that is perfectly fine — nobody is forcing those projects to play along, and nobody could if they tried. That was never how open source worked, and it’s not going to start now. That side doesn’t go away. It keeps shipping, it keeps being open source, same as it ever was. It just stops being something a regulated enterprise can lean on without a plan.

And it’s worth flagging now who’s going to look prescient when the dust settles: the capital-F Free Software crowd. The GPL true believers, the freedom-not-price people — the ones the rest of us wrote off as ideologues while we built businesses on top of the thing they kept telling us to take seriously. They never pretended any of this was free-as-in-beer. That was their entire point, stated plainly, for forty years. They were the conscientious objectors who looked at commercial open source twenty years ago and said, not my war. Hold that thought. We’ll come back to them.

The thing I can’t name

That first side — the part that’s going to carry the enterprise world on its back — needs a name. And I don’t have one. I’ve tried; we’ll get to that at the end. For now, call it the subset.

So what does being on that side actually take? Nothing to do with the license, for starters. The terms are about whether anyone’s home. Is the project reachable? Is there a disclosure path? Can it prove it’s still alive? Will it be there to patch the thing the AI finds next Tuesday?

And it’ll come from everywhere. Single-maintainer projects, community projects, foundation projects, corporate projects — none of those labels decide it. Some of each will choose to meet the bar. Plenty of each won’t. Again: that’s perfectly fine.

And to be clear, this is not a new license, and it is not a fork of the definition. It’s a posture — something a project adopts, or doesn’t. The ones that don’t owe you nothing. They never did, and nobody should pretend otherwise. If you want to keep using software that opted out, you have two options: find a vendor who’ll carry it for you, or use something else.

Proof of life

The hard problem underneath all of this: you cannot tell whether a normal open source project is alive or dead until it’s far too late. There’s no heartbeat monitor. A project looks exactly the same the day before the maintainer walks away as the day after. You find out it was abandoned when you need a patch and nobody answers.

So the subset needs a heartbeat. A proof of life. Some kind of keep-alive, a dead man’s switch, a way to continuously demonstrate that someone is still there and will still be there when it matters. Probably a lot more than that, too — a real security policy, a way to handle disclosures, the kind of obligations the CRA is already starting to write down. The point is that membership isn’t a badge you earn once and hang on the wall. It’s current state, re-proven constantly.

But a heartbeat requirement sounds cold, and it shouldn’t be. Because the flip side of «prove you’re still here» has to be a way to step away with your dignity intact. Maintainers burn out. People move on. Someone who has carried a critical library for fifteen years is allowed to set it down. The xz-utils maintainer didn’t have anywhere good to hand the keys — and we all saw how that went.

So you need a retirement home. Something like EmeritOSS: a place a project goes when its maintainer is done but the people downstream aren’t. A graceful way to hang it up. The code keeps getting looked after, the users stay safe, and nobody is expected to keep working forever. That’s not the system failing. That’s the system being humane.

Free as in puppy

Now the part everyone misreads as a threat. You can run this entire subset for free. Forever. You will never have to pay anyone a cent.

It’s just that «free» was never the right word. This was always free as in puppy, not free as in beer.

The puppy costs you nothing to adopt. What it costs you is the rest of your life in small daily increments. You have to feed it — which here means living at the bleeding edge, because the subset only ever patches latest. There is no patch coming for the version you froze three years ago and stopped thinking about. You have to walk it — keep moving, keep upgrading, keep current. And you have to be willing to rehome it the day it stops being yours to keep — the day a project falls out of the subset, you need to already be ready to move off it.

That’s the deal. It’s a fair deal. The cost was never the license fee. It was always the labor of ownership, and we just spent twenty years pretending the puppy raised itself.

Who carries it for you

This is the part where it starts to look like a pitch for Chainguard and a plot to murder open source. I can already hear it: he’s trying to sell you something.

…Kind of? I’m trying to build something I think a lot of people are about to want to buy. To do that, I have to make a guess about what’s coming and then be right about it. This post is the guess. And honestly, I’m flattered you think my blog is influential enough to redirect the buying patterns of an entire industry and pull off what Microsoft spent two decades and untold billions failing to do — kill open source. I’m not that good. Nobody is.

The free path stays open. It does not close. Vendors aren’t gatekeepers standing between you and the software — the software is right there, free, where it always was. What vendors actually sell is relief from the two costs you can’t pay yourself.

Don’t want to live at the bleeding edge? That’s a tax, and you can pay someone to carry it — LTS branches, backported fixes, somebody else absorbing the upgrade treadmill so your fleet doesn’t have to live at head. Can’t rip a project out of production the same afternoon it drops out of the subset? That’s the other thing you’re buying: a buffer. Someone to keep it safe while you migrate on a human timeline instead of a panic one.

If proof-of-life and the retirement home are the planned, graceful exit, the vendor is the emergency room — the one you call when a project goes down without warning and you need it stabilized now. Two different failures, two different answers.

The honest framing: it’s a dog-sitter and a trainer, on retainer. The dog is still yours. The dog is still free. You’re paying so you don’t personally have to do every walk, and so there’s a professional on call for the day it bites someone.

There are no contracts in open source. There is only current state. The vendor is the one place you can buy an actual contract, stretched over the top of a system that offers you none.

«Just pay the maintainers»

I know. I can hear the other half of the room. Or these greedy companies could just pay the maintainers.

Yes. They could. They should, even. I am not the don’t-pay-maintainers guy.

But I’ve said the same thing since 2021 and I’ll say it again: this is a distribution problem, not a funding problem. The money isn’t the hard part. Corporations have budget and are, mostly, willing to spend it. The hard part is connecting thousands of companies to thousands of dependencies, each with its own maintainer, its own wishes, its own appetite for being paid at all. Taking money is hard. Giving money away turns out to be even harder. Filippo wrote an excellent guide on how to do it well, and the length of his preconditions list is itself the proof — this does not scale by brute force.

Maintainers absolutely can step into the commercial layer on their own terms. Sell a contract that promises you won’t disappear. Sell backports under a different license. Become your own vendor. That option is real, and the right to choose it is the entire point. It just doesn’t, by itself, solve the matching problem for ten thousand companies at once.

Who organizes it all (and no, this isn’t a tragedy of the commons)

Let me kill one framing dead, because it’s wrong and it keeps coming back. This is not a tragedy of the commons. A commons gets destroyed by overgrazing — by too many people consuming a finite, depletable thing. Code is not that. My using a library doesn’t leave less of it for you. Nothing got overgrazed. What actually happened is that the maintenance-and-trust layer underneath everything was never funded and never structured to match how load-bearing the code quietly became. That’s not depletion. That’s a distribution problem wearing a bigger coat.

And the answer to a distribution problem is aggregation. Foundations and large communities are how a sprawling volunteer effort gets structure. One counterparty to fund instead of ten thousand. One clear owner to sign with. Governance kept separate from the money, so maintainers never fear losing control of their own project. And a credible signal that yes, this thing is alive, and someone is accountable for it.

The law is already converging on exactly this. The EU’s Cyber Resilience Act invented a category called the steward — a legal person who provides sustained support and ensures the viability of open source used commercially. That’s the law putting the role on the books. I’m not inventing the subset. I’m watching it form in real time, from multiple directions at once, and trying to describe it clearly before someone else defines it badly.

It grows up

So where does this land? Not in doom, and not in some open source utopia either. It lands somewhere more useful than both: honest.

The childhood really was great. What came next was brutal and unfair — open source didn’t choose any of this. But the thing walking out the other side is an adult. Hardened. Accountable. No longer convinced it’s invincible. It grew up the hard way, which is the only way anyone actually grows up.

Oh — and the conscientious objectors. The Free Software crowd we left a few sections back. The open-core founders and the VC-backed crowd, mid-security-audit and mid-CRA-filing, are going to glance over at the GPL diehards expecting to find them gloating. Expecting an I told you so. But the purists were never keeping score. They never signed up, never entered the enterprise-adoption race, never measured themselves against any of it. Ask one of them what they make of the whole commercial reckoning and the honest answer is Don Draper’s: I don’t think about you at all. We assumed we were the protagonists. They never even read the script.

To be clear about what kind of confidence this is: I might be wrong about all of it. That’s what a forecast is — a way to be wrong in public, on the record, with a date attached. But the shape of this one has been getting clearer for a year, and it hasn’t blinked yet.

Which brings me back to the name.

I still don’t have one. Enterprise Source sounds like a sellout the moment you say it out loud. Resilient Source is so soft it means nothing. Load-bearing Source gets the weight right but says nothing about the deal. I’ve tried a dozen others and hated all of them.

But we need one, and we need it fast. Naming a thing is how you start taking it seriously — it’s the first real act of stewardship. The category is already forming, already collecting members, and the regulators are already writing their own vocabulary for it into law. If the people who build and maintain this software don’t name it, someone else will, and we’ll spend the next decade living inside whatever term they pick.

So that’s the job of this post. Not to name the thing — to describe it. What it is, how it works, what it costs, what it promises. The name has to come from the people who’ll live under it, the same way everything else in open source gets decided: by usage, not decree.

It’s sitting right there. Somebody name it.

Further reading

Found this article interesting? This article is a contributed piece from one of our valued partners. Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.

Odysseus RCE, Samsung One-Click Takeover, iCloud Backdoor Fight + 27 More Stories – CYBERDEFENSA.MX

Apparently, opening the thing is now enough. A repo can run before the first prompt, a package can hide among hundreds, and a harmless-looking PDF can finish the job.

This week runs on cheap leverage: exposed servers, recycled bugs, poisoned agent instructions, remote-access tools dressed as support software, and trusted defaults doing attackers a favor.

Nothing here is especially mystical. Just ordinary systems trusting slightly too much, slightly too early. The full list follows.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

The useful lesson is not that attackers suddenly became brilliant. It is that trust keeps accumulating in quiet places: package managers, project files, assistants, provisioning tools, remote access software, and forgotten systems nobody planned to revisit.

Security still breaks at the handoff. Before the prompt. After the patch. Inside the default. Somewhere between “trusted” and “probably fine.” That gap is where this week lived, and it will be there next week too.