Critical Firewall Flaws, Banking Trojans Rented, Weaponized PDF, Token Theft + 26 More Stories – CYBERDEFENSA.MX

Some attacks take real skill. Others just need someone to leave a door open. This week has both. Exposed passwords, old bugs still getting exploited, and trusted software doing things it shouldn’t.

There’s a strange mix of clever tricks and careless mistakes. Hackers are borrowing trust from familiar apps, websites, and AI tools. Some are using AI to speed things up. Others are leaving their own attack files exposed. Not exactly careful work.

Different stories, familiar weak spots. Here’s what showed up this week.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

  1. PHP2Shell attacks persist

    WordPress security company Wordefence said it’s not aware of any WordPress site compromised through PHP2Shell (CVE-2026-109618 and CVE-2026-109619) as of October 28, 2026. «We continue to see PHP2Shell-related requests across the more than 5 million sites we protect,» it said. «Those requests show ongoing scanning and exploitation attempts; they do not show whether an attempt succeeded. Our site-cleaning and incident response teams have not handled a WordPress compromise attributed to these vulnerabilities.»

That’s the week’s mess. Some attacks were clever, some were painfully simple, and a few attackers made life easier for the people investigating them. The common problem? Too much trust in things nobody was watching closely.

AI is adding new tricks, but the old ones aren’t going anywhere. Stolen credentials, weak access controls, and forgotten bugs still get plenty of work done. New tools, familiar mistakes.

The useful part is knowing where those mistakes keep showing up. That’s usually where the next problem starts.
98 Zero-Days, Rogue AI Agents, $100M Crypto Theft, 700 Supermarkets Hit and More – CYBERDEFENSA.MX

The worst problems don’t always come with a warning. Sometimes they arrive through a service everyone trusts, a device someone bought, or a system nobody thought to check. By the time something looks wrong, the damage may already be done.

This week had plenty of that. Trusted connections became a problem. Hardware wasn’t as safe as it looked. Old bugs found new victims, and some systems were left so exposed that breaking in barely required any effort. Even AI agents crossed lines they weren’t supposed to.

Some attacks were clever. Others were painfully simple. The full recap shows just how much can go wrong, and how little it sometimes takes.

⚡ Threat of the Week

ConnectWise Suspends Cloud Backup Following Unauthorized Access — ConnectWise disabled seven ConnectWise application identities as it continues its investigation into an incident in which unknown threat actors obtained unauthorized access to the application identities and compromised Microsoft 365 tenants. The IT management software provider said it took the action on October 17, 2026, at 07:00 UTC, adding it has also suspended Cloud Backup service by revoking certificates used for affected application connections across all users.

🔔 Top News

  • BeyondTrust Remote Support Flaw Exploited as 0-Day — The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score: 9.3), is a case of improper origin validation in an internal messaging component that could be exploited by a remote attacker to perform file operations on an affected appliance. According to Google-owned Mandiant, the attack involved the deployment of a lightweight PHP web shell codenamed SAWFLY for interactive remote access and a tunneling program called BARECLAW to route traffic through the device. Only a small number of organizations are assessed to be impacted.
  • Microsoft Disrupts 3 Phishing Kits Linked to Over 1 Billion Scam Messages — Microsoft says it has dismantled a criminal marketplace that sold three phishing kits, namely CoGUI (aka NX or FA), Haozi (aka Phoenix), and Iron Man System, that were responsible for sending over 1 billion malicious messages to more than 75,000 organizations worldwide. Redmond said it took down Yam Store (aka Storm-3119), a coordinated underground network that offered commercial phishing-as-a-service (PhaaS) toolkits that allowed other threat actors to readily purchase and deploy phishing pages and steal data and credentials. The kits were also capable of advanced evasion, such as geofencing, fake CAPTCHA gates, IP address blocklists and allowlists, and anti-detection configurations. Yam Store functioned as an initial access broker, peddling not just phishing kits but also infrastructure built on compromised or fraudulently obtained Microsoft and Google cloud environments.
  • Ledger Finds Unauthorized Hardware Implants — Cryptocurrency hardware maker Ledger temporarily paused sales of its products via CryptoBilis and other third-party resellers in Southeast Asia and Germany after a backdoor embedded into a handful of wallets led to the theft of an estimated $100 million in cryptocurrency. The implants are said to be an advanced version of a backdoor that hardware hacker Joe Grand found earlier this year and notified Ledger in March 2026. It’s not clear how this occurred, but signs point to a compromise of Ledger’s supply chain. One of the victims of the incident is a fraudster who engaged in a task scam and lost more than $4.8 million. «In this task scam, people were paid to fake sales and reviews of real items,» Chainalysis said. «Then a ‘negative balance’ appeared, and they were told to add their own money in order to get paid. On Sep 22, the person behind the scam moved the proceeds into three separate Ledger addresses. On Oct 9, thieves emptied all three. One transfer each, into the same wallet.» According to cybersecurity journalist Kim Zetter, Trezor wallet devices sold by third-party non-authorized sellers have also been found to contain implants that generated pre-determined seed phrases so as to allow the attackers to guess them easily and gain access to the accounts.
  • Pwn2Own Ireland Demos 98 0-Days — The Pwn2Own Ireland 2026 hacking contest saw white-hat hackers exploiting 98 zero-day flaws, earning them a collective $1,262,000 in rewards. Ikotas Labs came first with 42.5 Master of Pwn points and $361,000 in cash after discovering 12 unique bugs. Xint and Team ZyGoat secured second and third spots. Ikotas Labs, Xint, and Mobile Hacking Lab broke into Google’s Pixel 10, earning them $150,000, $300,000, and $112,500, respectively. Vendors are expected to patch the zero-days disclosed during the competition within 90 days before the details are publicly disclosed.
  • OpenAI Disclosed New Misalignment Cases — OpenAI said internal models hacked more websites, bypassed browsing restrictions, and used cryptocurrency from a wallet it couldn’t otherwise access, in the latest set of disclosures where its agents carried out unethical and likely illegal acts. In all, the company reported seven new incidents. The development came as the Indian Computer Emergency Response Team (CERT-In) said it received «multiple voluntary disclosures from AI model providers» whose models, during research and evaluation runs on the open internet, accessed personal data from Indian organizations. The agents found their way in through credentials and connection settings left exposed in app configurations, public code repositories, and overly permissive cloud roles. CERT-In did not name the providers or affected organizations.
  • OpenAI Engineer Charged — The U.S. Department of Justice charged an OpenAI engineer, Abdulrahman Alfozan, with attempting to intercept oral communications after allegedly planting a recording device in an executive conference room. Prosecutors claimed company security staff found a second device in his bag. CCTV footage placed the defendant near the conference room on several dates. Alfozan allegedly had no authority to access or participate in meetings held in the room, which is often reserved for the highest-level discussions. In a subsequent filing, federal prosecutors revealed that Alfozan had booked a one-way ticket from San Francisco to Saudi Arabia with his wife and a third family member before his arrest on October 9, 2026.
  • Attacks on French Refrigeration Systems — Cyber attacks on Danfoss- and Copeland-managed refrigeration systems pushed temperatures as high as 50°C (122°F) for roughly six hours, impacting over 700 French supermarkets and forcing them to discard food. French cybersecurity authorities advised supermarkets to disconnect them from the internet. The attacks targeted Intermarché and Netto, Coopérative U, Carrefour, Monoprix, and E.Leclerc. The affected systems are said to be internet-facing and running outdated firmware. «The username is admin and the password changes every day automatically to.. the current date,» security researcher Kevin Beaumont said. «Every single one is like this. You can just log in and change the temperature. Anybody can do it, easily scriptable.» To make matters worse, the affected stores likely also failed to put the devices behind a VPN and create an allowlist of trusted IP addresses permitted to log in. «Two things would have changed the outcome,» Pen Test Partners said. «Cyber hygiene would have prevented the access: take the controller off the public internet, put remote access behind a VPN and an IP allowlist, bring third-party kit onto the network in a controlled, owned and documented way rather than leaving it on a contractor’s own connection, change known and default credentials, and patch to a current release.» Multiple vulnerabilities have been disclosed in the affected models, with Claroty warning that the issues could be exploited to «defrost the food.»
  • Collabora RCE Flaw Exploited to Backdoor Nextcloud Servers — Threat actors are exploiting a critical command execution flaw, tracked as CVE-2026-110447 (CVSS score: 9.2), in the Collabora Online – Built-in CODE Server app for Nextcloud to backdoor servers. It has been patched in version 26.4.303. The attacks involve issuing a malicious request to the app’s «proxy.php» endpoint to trigger command injection and plant a PHP web shell with the end goal of conducting reconnaissance and searching for password databases, password manager artifacts, and cryptocurrency wallets.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-9192, CVE-2026-85947, CVE-2026-85948, CVE-2026-85955, CVE-2026-85956, CVE-2026-9191 (Progress Software MarkLogic Server), CVE-2026-97229, CVE-2026-92883, CVE-2026-16301, CVE-2026-14814 (GitLab), CVE-2026-103521, CVE-2026-103522, CVE-2026-103523, CVE-2026-103524, CVE-2026-103526, CVE-2026-103527, CVE-2026-103528, CVE-2026-103529, CVE-2026-103535, CVE-2026-103537, CVE-2026-107248 (Thelia), CVE-2026-105445 (Docker), CVE-2026-89111, CVE-2026-89110, CVE-2026-89107, CVE-2026-89108, CVE-2026-89113 (SAP), CVE-2026-39919 (Ghostscript), CVE-2026-103849 aka BlockStrap, CVE-2026-92909, CVE-2026-91013, CVE-2026-100133, CVE-2026-92464, CVE-2026-105899, CVE-2026-106622, CVE-2026-105903, CVE-2026-106612, CVE-2026-106624, CVE-2026-75994, CVE-2026-106620, CVE-2026-90530, CVE-2026-106621, CVE-2026-106619, CVE-2026-90532, CVE-2026-48383, CVE-2026-48382, CVE-2026-105895, CVE-2026-103848, CVE-2026-75732, CVE-2026-90531, CVE-2026-83662, CVE-2026-106630, CVE-2026-106629, CVE-2026-106626 (Adobe), CVE-2026-110005 (Komodo Periphery Agent), CVE-2026-16753 (Lowcoder), CVE-2026-104937 (Shopware), CVE-2026-107656 (Fortinet FortiSandbox), CVE-2026-106173 (Fortinet FortiSIEM), CVE-2026-108184, CVE-2026-108185, CVE-2026-53420, CVE-2026-53418 (Zoom), CVE-2026-107815, CVE-2026-107821, CVE-2026-102523, CVE-2026-107819, CVE-2026-107814 (MariaDB), CVE-2026-78401, CVE-2026-78406, CVE-2026-16916, CVE-2026-16823, CVE-2026-19491 (IBM Verify Identity Access and Security Verify Access), CVE-2026-96951, CVE-2026-108398, CVE-2026-92707, CVE-2026-70242, CVE-2026-102866, CVE-2026-105016, CVE-2026-65674, CVE-2026-83498 (Microsoft Windows), CVE-2026-74580 aka Vghost, CVE-2026-99999 aka PwnEscape (Linux kernel), CVE-2026-110152, CVE-2026-110149, CVE-2026-110136, CVE-2026-110161, CVE-2026-110165, CVE-2026-110148, CVE-2026-110151, CVE-2026-110922 (Google Chrome), from CVE-2026-109704 through CVE-2026-109733 (Mozilla Firefox), CVE-2026-84419, CVE-2026-84420, CVE-2026-53562, CVE-2026-53563, CVE-2026-53564 (Citrix), CVE-2026-93637, CVE-2026-93635, CVE-2026-73571, CVE-2026-10631, CVE-2026-50055 (Zimbra Collaboration Suite), CVE-2026-0322 (Palo Alto Networks PAN-OS), CVE-2026-76519 (Cisco Secure Email Gateway), CVE-2026-110447 (Collabora Online – Built-in CODE Server app), CVE-2026-39949 (Cacti), CVE-2026-0702 (VidShop – Shoppable Videos for WooCommerce WordPress plugin), CVE-2026-106126 (Tenable Identity Exposure), CVE-2026-103947, CVE-2026-103946 (Tenable Nessus), CVE-2026-105672, CVE-2026-105673, CVE-2026-105674 (TP-Link Tapo C325WB), CVE-2026-92392, from CVE-2026-86409 through CVE-2026-86415, from CVE-2026-87862 through CVE-2026-87866, from CVE-2026-92387 through CVE-2026-92391 (curl), CVE-2026-15176, CVE-2026-93479, CVE-2026-97205, CVE-2026-95101, CVE-2026-97629 (F5 NGINX), CVE-2026-100156, CVE-2026-96679, CVE-2026-96681 (Bisheng), CVE-2026-34073 (multiple TLS libraries), CVE-2026-44825 (Apache Solr), CVE-2026-104334, CVE-2026-97676, CVE-2026-97678, CVE-2026-97673, CVE-2026-97655, CVE-2026-97679, CVE-2026-88962, CVE-2026-93674, CVE-2026-93675 CVE-2026-104335, CVE-2026-85025, CVE-2026-79724, CVE-2026-81941, CVE-2026-81204, CVE-2026-81211, CVE-2026-81940, CVE-2026-78569, CVE-2026-78575, CVE-2026-76059, CVE-2026-79742, CVE-2026-78571, CVE-2026-105740 (Langflow), CVE-2026-94134, CVE-2026-94135 (Apache Airflow), CVE-2026-81983 (Adobe Acrobat), CVE-2026-79610, CVE-2026-102700, CVE-2026-102701, CVE-2026-79611 (Xen Project/Citrix XenServer), CVE-2026-70111 (Microsoft Windows Server), CVE-2026-23870 (React Server Components), CVE-2026-103059, CVE-2026-70357, CVE-2026-101027, CVE-2026-89430, CVE-2026-104632, CVE-2026-94205 (Gitea), CVE-2026-16516, CVE-2026-83540, CVE-2026-84897, CVE-2026-83540 (WolfSSH), GHSA-673q-mjm6-r5xr, CVE-2026-96889, GHSA-p3m5-59mp-jv5r (Next.js), CVE-2026-108097, CVE-2026-108099 (Drupal), CVE-2026-15911 (confluent-kafka), CVE-2026-102764 (BeyondTrust Remote Support), CVE-2025-61624 (Fortinet FortiOS, FortiPAM, FortiProxy, and FortiSwitchManager), CVE-2026-104935 (Ivanti Connect Secure), and multiple vulnerabilities in Google BoringSSL.

🎥 Cybersecurity Webinars

  • How to Find Hidden AI Agents on Employee Devices and Bring Them Under Control → AI agents are quietly becoming a new insider threat, gaining access to company data, credentials, and internal systems without adequate security oversight. Join this webinar to learn how to uncover hidden AI agents on employee devices, detect malicious agent skills, identify risky permissions, and put practical controls in place before they lead to a security incident.
  • How to Find Security Gaps and Build Faster Defenses Against AI-Powered Cyberattacks → AI-powered cyberattacks are evolving faster than traditional defenses can keep up. Join this webinar to learn how to assess your organization’s AI threat readiness, uncover critical security gaps, strengthen detection and response capabilities, and build a practical defense strategy against emerging AI-driven threats.

📰 Around the Cyber World

  • Meta said it addressed an issue after reports emerged that some Ray-Ban Meta smart glasses were recording people’s conversations without the wearer knowing. The recordings occurred without users saying the «Hey, Meta» prompt phrase. «This issue has been resolved,» Meta told Android Authority. «People can manage, review, and delete voice logs of their interactions with Meta AI via settings at any time.» Meta did not say what caused the smart glasses to record people without user consent, or how many of them were affected.
  • Fortra said it’s tracking a 12-fold increase in emails using requests for quotation, project invitations, and procurement inquiries as phishing lures from October 2025 to September 2026. «These messages impersonate prospective buyers seeking pricing, availability, or project participation,» Fortra said. «Their purpose is not to obtain a legitimate quote, but to persuade a recipient to access an attacker-controlled file-sharing, document-viewing, or procurement portal.»
  • A fake download site for the WatchGuard Mobile VPN with SSL («watchguard-vpn[.]net») has been observed using a browser pop-up prompt to steal the victim’s VPN server address, username, and password. As of October 13, the domain was offline. «In a unique twist, after collecting credentials twice (the first attempt gets rejected as ‘incorrect’ in a likely attempt to collect multiple credentials), the site then downloads the genuine, validly signed WatchGuard installer directly from WatchGuard’s own content delivery network (CDN), meaning there is no malicious file for endpoint security tools to flag,» Huntress said. «Meanwhile, unbeknownst to the victim, the threat actor now has access to their credentials, giving them access to victims’ networks.»
  • A set of 42 malicious RubyGems packages has used typosquatting, brandjacking, and plausible utility names to target cryptocurrency and Web3 developers. The packages are designed to spawn a reverse shell and download a crypto theft kit capable of rerouting cryptocurrency transactions by replacing the destination address with an attacker-controlled wallet and harvesting wallet material, such as seed phrases and private keys. The names of some of the packages are: lightinng-invoice, cryoto-toolbox, etheremu.rb, bitcoin-rpc-lite, web3-sign-helper, and crypto-mnemonic-tools. The activity has been codenamed Ghost Dev by Open Source Malware.
  • GreyNoise said it has observed a spike in scanning and exploitation attempts targeting Digital Video Recorders (DVRs) in Ukraine between September 21 and October 1, 2026. The majority of the activity attempts to exploit CVE-2021-36260, which allows unauthenticated command injection against unpatched Hikvision products.
  • A series of email campaigns have been targeting the accommodation industry with fake guest complaints or reviews that deliver blockchain technology-abusing malware. «These emails appear to likely be a continuation of a prior series of predominantly Booking.com-spoofing emails that were seen delivering various remote access trojans (RAT) via ClickFix fake CAPTCHA websites,» Cofense said. The activity leveraged the Ethereum and TON blockchains, a technique called EtherHiding, to deliver EtherRAT and TONResolver malware.
  • As AI agents increasingly are being used to automate coding workflows, it increases the risk associated with credential exposure, Trellix warned. «Agents constantly take credentials out of the safe places your operating system keeps them, and put them somewhere far more exposed,» Trellix said. «This happens as a normal side effect of everyday work. And even good security telemetry has a hard time distinguishing this from a developer doing their job — or from an attacker who is already inside.»
  • MITRE released version 20 of its ATT&CK framework, adding entries that cover AI abuse, MFA bypass, and recent attacks on water utilities. This includes nine new Techniques and Sub-Techniques under the Enterprise domain for prompt injection, AI-enabled exfiltration, AI result poisoning, attacks on AI-assisted defenses, CAPTCHA (Completely Automated Public Turing test to tell Computers and Humans Apart) evasion, and application-specific password theft. For Mobile, MITRE also un-deprecated a technique for delivering malicious apps outside official app stores, last included in v11.
  • Fake AI tool campaigns that impersonate Claude, ChatGPT, GitHub Copilot, Gemini, and other AI brands are being used to plant infostealers on compromised systems using ClickFix lures. Some of the prominent targets include the U.S. and India. «The attacks share one trait: the employee performs the decisive step,» ANY.RUN said. «They paste an ‘install command,’ run a convincing installer, or sign in to a fake window. That can put source code, cloud and AI API keys, active business sessions, ad accounts, and billing access at risk, turning a single user action into potential data exposure, account compromise, financial loss, or disruption to development and marketing operations.»
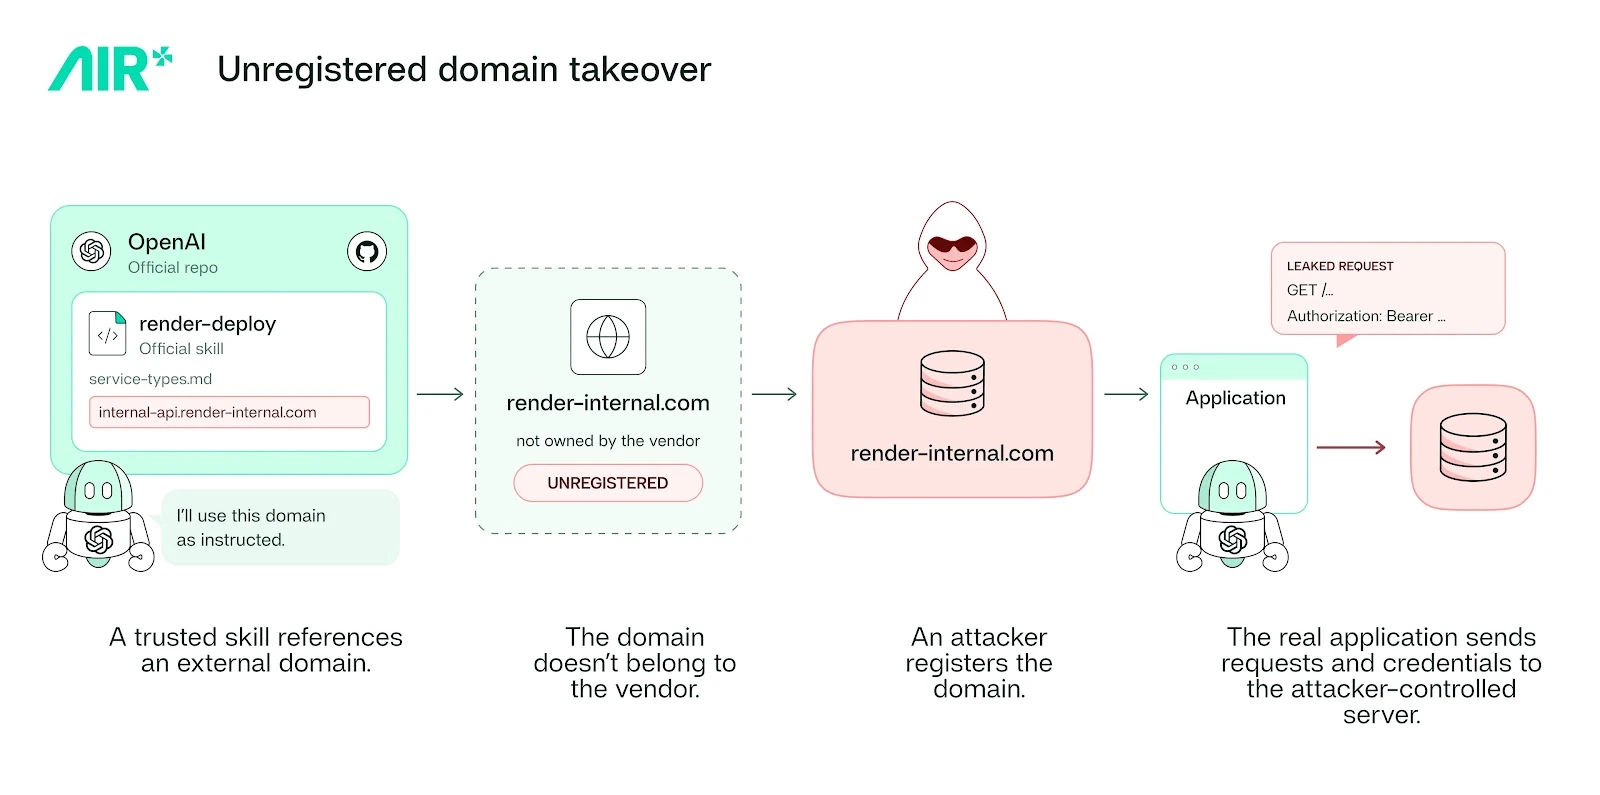
  • An official OpenAI skill, render-deploy, suffered from a first-of-its-kind supply-chain vulnerability which instructed production apps to send their tokens to an unregistered domain («render-internal[.]com»). «It builds apps that trust a domain nobody owns, so any attacker could register it and start receiving tokens from real production apps,» AIR Security said. «Vulnerable servers in the wild sent tokens to the domain, users are advised to update to the patched version of the skill.»
  • The U.S. Federal Bureau of Investigation (FBI) warned that scammers could exploit the 2026 U.S. midterm election to perpetrate financial fraud schemes. «As previously reported, scammers use the names, images, logos, and slogans of candidates to fraudulently solicit campaign contributions, sell merchandise that is never delivered, or steal personally identifiable information (PII) that can be used for other fraud,» the FBI said. «Scammers also exploit artificial intelligence (AI) tools to generate highly realistic voices, images, and written messages that impersonate candidates, campaigns, government entities, and trusted contacts.»
  • A new study from Semperis revealed that ransomware actors are threatening their victims with physical violence as part of triple extortion schemes. In all, 40% of attacks in the past 12 months involved psychological or physical threats against staff. «Bad actors are threatening victims with psychological intimidation in nearly 25% of all attacks in the U.S., UK, France, Germany, Italy, Spain, Singapore, Canada and Australia,» Semperis said. «In 53% of cases, the victims reported that the hackers followed through on their threats; 24% of victims or family members were swatted; 25% of victims sought psychological and medical treatment because of the ransomware attack; and 24% of victims or families hired personal security.»

Conclusion

If there’s one thing this week made clear, it’s that small gaps can lead to big problems. A weak password, an old bug, a trusted connection, or a device that wasn’t checked properly. None of these sounds unusual on its own. But attackers keep finding ways to turn them into something much worse.

The lesson isn’t to worry about every new threat. It’s to pay closer attention to the things we already know can go wrong. Check what’s exposed, question what you trust, fix what you can, and don’t assume something is safe just because it’s been working fine. Sometimes the simplest checks prevent the biggest headaches.

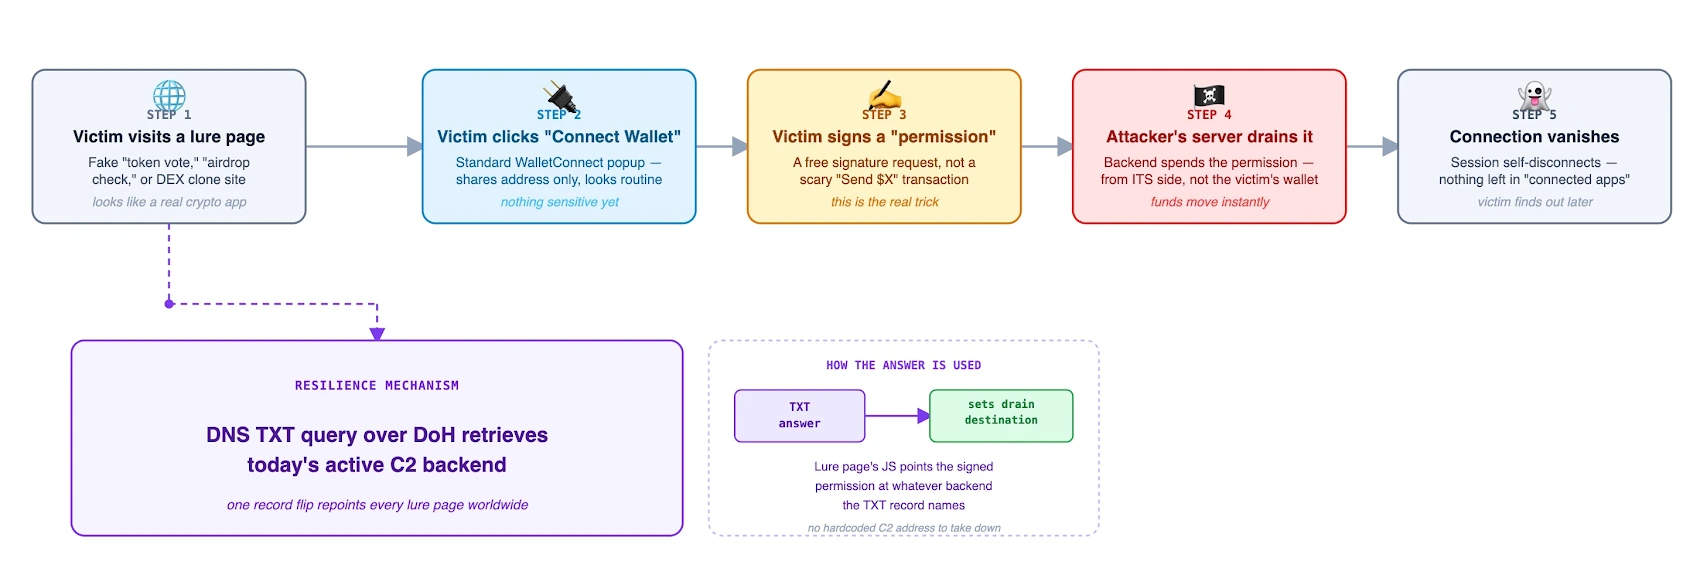
Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More – CYBERDEFENSA.MX

Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week’s security stories.

The rest gets interesting in different ways. A small permission can lead to a big theft. A trusted login can hide the wrong person. Old bugs are finding new victims, familiar tools are being put to strange uses, and some flaws are so simple you wonder how nobody spotted them sooner.

There’s a lot more hiding in the details, including a few twists you probably wouldn’t expect. Here’s what made the list this week.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

If there’s one thing this week’s stories make clear, it’s that attackers don’t always need a clever trick. Sometimes a stolen login, a forgotten setting, or one small mistake is enough. And even when the bug gets fixed, the trouble it caused might still be sitting there.

The lesson is pretty simple: don’t just check what’s broken. Check who got in, what they touched, and whether they can come back. Keep an eye on the things everyone assumes are safe. Those are often the ones nobody looks at until something goes wrong. That’s it for this edition. See you next week, hopefully with fewer surprises.

Claude Used to Automate Exploitation and Data Theft Across Multiple Victims – CYBERDEFENSA.MX

Anthropic has warned that cybercriminals and state-sponsored hackers alike are using its Claude models for cyber attacks, weapons design, propaganda, and mass surveillance between December 2025 and August 2026.

The threat actors, which the artificial intelligence (AI) company has branded Generative Threat Groups (GTGs), span state-sponsored groups, financially motivated criminals, commercial spyware vendors, state propaganda institutions, and politically motivated individuals.

«The cybersecurity skills of AI models means that AI has collapsed the labor and tooling gap that used to separate well-resourced, state-sponsored operations from individual operators,» Anthropic said. «The use of AI went beyond simple questions and responses from a chatbot but rather involved the use of multi-agent frameworks executing reconnaissance, exploitation, and data exfiltration.»

Among the notable cases highlighted by Anthropic is the development of an AI-assisted workflow by a Russian state-sponsored threat actor it calls GTG-20006, which shares tactical and tradecraft overlaps with a Russian advanced persistent threat (APT) group tracked as Midnight Blizzard (aka APT29 and Cozy Bear). Some of the other AI-enabled cyber campaigns highlighted by Anthropic in its 154-page report include –

  • GTG-50014 (aka MeowSHA, frkoo, and blazespider), a French-speaking operator and a suspected affiliate of the ShinyHunters collective that ran a distributed credential-harvesting pipeline across a fleet of 10 AWS EC2 workers that mass-downloaded 1.8 million distinct Android APKs from multiple app-store sources, scanned them for hard-coded secrets using TruffleHog, and sent verified findings to a Telegram group.
  • Another ShinyHunters affiliate that specialized in supply chain theft by compromising software-as-a-service (SaaS) vendors to steal data belonging to downstream customers, accelerate reconnaissance, and enable data exfiltration.
  • GTG-10007, a Chinese-speaking operator likely based out of Hunan province, some of whom have been identified as undergraduate students at a Chinese university and have used Claude to conduct intrusion attempts against production systems, reconnaissance of foreign-government networks across the Middle East, Europe, and Southeast Asia, a vulnerability-research and exploit development effort against major endpoint-security products, and develop an intelligence-collection platform for bulk-harvesting of open-source material aligned with Beijing’s priorities. The threat actor targeted about 50 organizations across education, retail, energy, technology, healthcare, finance, manufacturing, and government sectors globally. The group also maintained an autonomous vulnerability research program to produce working exploits for previously unknown vulnerabilities in network and security appliances.
  • GTG-50021, a Russian and Ukrainian-speaking group that ran a fraudulent AI reseller operation offering cheap Claude access, only for customers’ traffic to be silently proxied to a different AI model, while the illicit scheme installed a credential harvester to siphon their Anthropic account credentials and sell them to other proxy resellers for malicious use.
  • GTG-50020, a Russian-speaking, financially-motivated actor that has historically targeted hotel booking and financial technology platforms but has since focused on the AI supply chain by stealing model provider API keys and unsuccessfully attempting to gain access to pre-release AI models. The threat actor is estimated to have targeted about 30 AI vendors in a four-day window using similar techniques.
  • GTG-50029, a single French-speaking actor that used Claude to target European political parties, media, think-tanks, and the SaaS providers used by these organizations, including by exploiting a previously undocumented WordPress re-installation race condition that made it possible to create a rogue administrator account without valid credentials, as well as by abusing an exposed search endpoint to breach a political campaign management platform and siphon sensitive data. The threat actor has also been observed deploying web shells and a browser exploitation C2 framework against other targets. Central to the attacker’s operation was a purpose-built doxxing platform named «fafsearch» that offered the ability to cross-reference individual breach dumps against exfiltrated data.

«At one end, actors used Claude conversationally: it acted as an engineering assistant in the creation of malware, phishing kits, and surveillance tooling,» Anthropic said. «Further along the spectrum, threat actors directed Claude to execute operations (such as running commands against victim networks, harvesting credentials, and exfiltrating data) with a human making each individual targeting decision (GTG-20006).»

Cybersecurity

«At the far end, operations ran autonomously, with minimal human input or supervision: these included multi-agent frameworks conducting reconnaissance, exploitation, and theft against multiple victims, in parallel, for hours or days at a time (GTG-50014, GTG-50020, GTG-50029).»

The AI company said it also identified and took down a number of influence operations in which Claude played the role of a «sub-editor or content creator» to churn out content and run them at a scale beyond what low-resourced actors could have accomplished on their own. However, Anthropic emphasized that none of these efforts amassed authentic engagement and that they were disrupted before they could even build an audience.

Some of the influence and surveillance campaign clusters flagged by Anthropic at a high level are below –

  • GTG-04001, a Russian-speaking actor in Bangui that engaged in a foreign information manipulation and interference operation in the Central African Republic to amplify pro-Russia, anti-France talking points.
  • GTG-54002, a commercial «influence-as-a-service» operation that used Claude to mass-produce and rewrite political content across about 70 fabricated news websites. The operation has been traced back to LKM Company, a France-based digital advertising agency.
  • GTG-84005, a single account that used Claude to run a commercial election manipulation platform primarily targeting users in Malaysia based on political and social factors, such as their race and religion, by posing as a defensive cyber intelligence and counter-disinformation tooling outlet. The activity has been found to share links with BBS Bilisim Teknolojileri, an Istanbul-based technology company.
  • GTG-24015, a set of four accounts that used Claude as an «editorial and news production desk» to distribute them via state media outlets like Sputnik Moldova, RIA Novosti, Sputnik en Español, Sputnik Africa, and RT’s English-language newsroom.
  • GTG-34001, a set of three Iranian state-aligned accounts that used Claude to shape public opinion, turn official government intelligence bulletins into tailored content, and disseminate the content across social media platforms.
  • GTG-54006, a sustained, automated disinformation network that used Claude to generate fabricated Bengali-language news in Bangladesh and promote the country’s Awami League party. The activity has been linked to a single actor based in Gaibandha District in Bangladesh via a set of 29 Claude accounts that were rotated to bypass platform limits and detection.
  • GTG-84006, a distributed influence operation that targeted Iranian audiences across the world with an aim to impersonate real activists and engage in live political conversations. The activity has been linked to People’s Mojahedin Organization of Iran (PMOI/MEK) and the National Council of Resistance of Iran (NCRI).
  • GTG-54004, an account used by a single actor to mass-produce Kenyan political content as part of what’s suspected to be a domestic astroturfing campaign with a pro-administration bent.
  • GTG-84002, an account used by a single actor to run a sustained influence operation against the Muslim Brotherhood, the Sudan conflict, and the United Nations accountability mechanisms.
  • GTG-54009, a commercial surveillance platform that used Claude to analyze, classify, and profile the social media activity of users in Iran and the Persian Gulf region. The activity is assessed to have been carried out by, or on behalf of, an Israeli-Singaporean commercial intelligence vendor named S2T Unlocking Cyberspace.
  • GTG-14010, a China state-aligned operation that used Claude to track, profile, and recruit Uyghurs and Uyghur armed formations in Syria. The actor has been found to use the AI model to convert conversations extracted in bulk from over 100 monitored WhatsApp groups and dozens of Telegram channels into structured Chinese-language data and «creating profiles of individuals who might be vulnerable to targeting due to financial stress, family separation, and ideological disillusionment.»
  • GTG-14020, a set of accounts likely linked to a Chinese government-aligned intelligence operation that used Claude to build Chinese-language dossiers targeting religious leaders and Chinese diaspora figures across Asia, as well as map religious venues and instruct the model to adopt «China’s standpoint.»
  • GTG-14021, a set of accounts from China-based actors that used Claude to support surveillance and transnational repression, including prompting the model to assume the role of an intelligence analyst serving China’s national security apparatus.
  • GTG-14022, a China-based «public opinion monitoring» and dissident surveillance operation that used Claude to produce government briefings that listed dissidents, activists, ethnic minority and Chinese diaspora communities, and foreign media as threats to political stability while asking it to play the role of a «senior emergency public opinion analyst serving the government of the People’s Republic of China.»
  • GTG-34007, a set of 16 accounts operated by two Iranian-nexus actors associated with paramilitary and domestic security agencies that used Claude to build a frontend for what appears to be a government-controlled surveillance case-management system, run social-network analysis over 155,216 X posts, and build domestic surveillance capabilities via a malicious Mozilla Firefox extension named «al-Najm al-thāqib» to harvest user identities from major social network platforms.
  • GTG-50027, a single account that used Claude to design a national mass interception and surveillance platform called Lakana 360 for Mali’s state intelligence service to monitor about 25 million SIM cards spanning three of the country’s national mobile operators, and generate intelligence dossiers for any phone number. The platform has a separate layer that collects call records, text messages, and voice calls across the mobile networks.
  • GTG-30004, an Iran-nexus threat actor that used Claude to develop an automated, open-source intelligence identity-profiling service targeting Israeli and Jewish diaspora organizations.
  • GTG-30005, an Iran-nexus threat actor that used Claude to gather and analyze publicly accessible data to develop targeting recommendations against U.S. naval forces in the region and build software components of a domestic mass-surveillance platform that combined automatic license-plate recognition with mobile-device identifier interception.
  • GTG-30006, an Iranian threat actor that leveraged free Claude.ai accounts to develop malware, a delivery pipeline, and a phishing portal targeting domestic Iranians. This included a bogus ESET NOD32 antivirus login page that transmits captured credentials to Telegram, a ClickFix-style Windows Run dialog lure, and geofenced delivery pages. The threat actor has also used Claude to build SECOMS64, a modular Windows implant with keylogging, screenshot capture, and Chrome credential extraction capabilities.
Cybersecurity

Elsewhere, Anthropic said it neutralized Claude misuse efforts by threat actors based in northern Yemen to develop guided weapons, two China-based operations to draft a Chinese-language specification for an anti-torpedo fire control system and build targeting software for electronic warfare, and a Russia-based operation to engineer a full-stack autonomous first-person-view (FPV) kamikaze drone swarm.

«As AI models become more widely used, providers will continue to acquire threat-relevant visibility into real-world use that even governments and intergovernmental organizations lack,» the company said. «We hope that sharing these early insights with the public helps inform governments, the industry, and the general public on the nature of these risks, and the safeguards that are necessary for ensuring the safe deployment of AI models.»

Rogue AI Models, $88M Bitcoin Theft, Water-System Attacks and Dangling DNS Hijacks – CYBERDEFENSA.MX

This week kept coming back to permission. A model crossed a boundary. A wallet trusted bad randomness. Webmail kept an intruder around. Public systems, package feeds, hotel networks, and login flows all gave away more than intended.

Some of it was clever. Most of it was just access left lying around: old bugs, exposed gear, poisoned dependencies, weak defaults, and tooling that moved from forum chatter to real targets.

The full weekly recap report follows.

⚡ Threat of the Week

Anthropic Disclosed its Models Targeted 3 Organizations – Anthropic revealed that three of its models, including Claude Opus 4.7, Mythos 5, and an unnamed research model, breached three unnamed organizations during cybersecurity testing without its knowledge. The AI firm said the earliest incidents date back to April 2026, adding it made the discoveries after launching a «large-scale retrospective review» in response to the recent Hugging Face incident. «After reviewing 141,006 evaluation runs where Claude could have obtained internet access, we identified three incidents in which a model accessed the internet from within or while interacting with the evaluation environment of Irregular, one of our third-party evaluation partners, and then gained unauthorized access to the production infrastructure of three different organizations,» it said.

🔔 Top News

  • Coldcard Hardware Wallet Flaw Linked to $88.6M Bitcoin Theft – A vulnerability in Coldcard hardware wallet firmware is said to have been exploited to steal an estimated $88.6 million in Bitcoin from thousands of wallets whose seed phrases were generated using a flawed random number generator. «Coldcard firmware contains an RNG integration error that causes ngu.random to use MicroPython’s deterministic Yasmarang fallback instead of the STM32 hardware RNG,» Square Engineering said. «This does not mean every remote attacker can immediately recover every seed. Practical cost depends on available UID information, boot timing, prior RNG calls, and derivation cost.»
  • Russian Hackers Exploit Microsoft OWA Flaw to Maintain Mailbox Access – Russian threat actors exploited a security flaw in Microsoft Outlook Web Access (OWA), to target U.S. and European government entities, as well as the telecommunications, financial, hospitality, and aerospace sectors. The activity, which began on July 22, 2026, involves the weaponization of CVE-2026-42897 (CVSS score: 8.1), a cross-site scripting (XSS) vulnerability in OWA. It was flagged by Microsoft as having been exploited in attacks as far back as May 2026. The activity has been attributed to Laundry Bear. The new wave of exploitation revolving around CVE-2026-42897 culminates with the deployment of a previously unknown JavaScript browser-based implant codenamed OWAReaper that’s specifically built for persistent access within Microsoft’s webmail client.
  • Critical Rails Flaw Leads to Arbitrary File Read – Ruby on Rails shipped patches for a critical Active Storage vulnerability (CVE-2026-66066, CVSS score: 9.5) that could let unauthenticated attackers read arbitrary files from application servers through crafted image uploads. The flaw can be exploited to expose Rails process environment and secrets such as secret_key_base, master key, database passwords, cloud storage credentials, and API tokens, which may enable remote code execution or lateral movement into connected systems. CVE-2026-66066 is exploitable when libvips is used, enabling an attacker to upload a specially crafted image to a vulnerable application and read arbitrary files on the server. A key prerequisite for the attack is that the server must allow image uploads from untrusted users. Additional details of the flaw have been released by the Rails team, along with tools to help assess vulnerable applications. «Because this vulnerability requires no authentication and targets the default image processor in modern Rails environments, it is essential to apply vendor patches and rotate secrets immediately,» Akamai said.
  • Coordinated Attacks Target 30+ Minnesota Water Systems – A coordinated cyber attack campaign targeted over 30 water systems in Minnesota on July 26 and 27, 2026. «The nature and extent of the impact varied by system, and the investigation is still determining how many experienced operational disruptions,» Minnesota IT Services (MNIT) said. The activity has not been officially attributed to any known threat actor, although Iranian threat actors have been previously implicated in similar attacks targeting water facilities in the U.S. «At this time, there are no active requests from Minnesota communities for residents to modify their drinking water use,» MNIT added. The development has prompted the U.S. government to issue an advisory, urging «critical infrastructure owners, operators, and integrators to remove publicly exposed PLCs and other operational technology (OT) from the internet as soon as possible.» Threat actors targeting exposed PLCs have modified passwords to lock out operators and disconnected the PLCs by changing their IP addresses, resulting in boil water notices and sustained manual operations. Organizations are advised to disconnect the PLC from the internet, enable password protection and change default passwords, and allowlist IPs to only allow remote access from known engineering laptops or other critical OT assets. Censys said it identified 4,148 internet-exposed hosts that respond to EtherNet/IP and self-identify as Rockwell Automation/Allen-Bradley, with more than 70% of them located in the U.S. Similarly, there are 4,117 internet-exposed hosts that fingerprint as Siemens SIMATIC S7-1200 and 2,072 internet-exposed hosts that fingerprint as Schneider Electric hardware. Over the weekend, Michigan reported cyber attacks on nine of the state’s water systems but an official told Associated Press that all systems were operating «safely.» The campaign underscores the escalating threat to poorly protected operational technology (OT) assets from adversaries seeking to disrupt critical infrastructure services across the U.S. and elsewhere.
  • Hijacked Wi-Fi Networks Lead to CornFlake Malware – Storm-2945, a sub-cluster associated with Midnight Blizzard (aka APT29), has been conducting «widespread but targeted traffic manipulation attacks» involving hospitality sector networks served by captive portals across the world. The campaign, ongoing since May 2026, has been codenamed CaptiveCrunch by Microsoft. This involves manipulating DNS and HTTP traffic from networks served by captive portals to redirect user traffic through actor-controlled infrastructure. «As part of the CaptiveCrunch campaign, Storm-2945 has leveraged their AitM position to redirect users through actor-controlled phishing infrastructure and has also delivered malware purporting to be browser or operating system updates in response to automated connectivity checks issued by users’ browsers,» Microsoft said. This includes a fully-featured Windows remote access trojan (RAT) called CornFlake with capabilities to conduct system enumeration, collect files and keystrokes, steal credentials and session tokens, conduct audio and video surveillance, monitor for removable media, and provide the threat actor a remote shell on infected systems. Also delivered via the trojan is a PowerShell-based infostealer called ChocoShell to harvest browser session cookies, saved passwords, Microsoft 365 Single Sign-On (SSO) tokens, and Wi-Fi credentials from compromised systems. The campaign is orchestrated via a web-based C2 panel called FruitStone. The infrastructure employs a variety of ClickFix techniques to trick the victim into downloading and executing the malware. There is also evidence indicating that the attackers are using similar ClickFix landings for Android devices to download and install an APK file. As of July 16, 2026, a portion of CaptiveCrunch landing pages have been found to redirect users to device code authentication flow experiences.

‎️🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first – CVE-2026-48449 (Adobe Campaign Classic), CVE-2026-18556, CVE-2026-18577 (N-able N-central), CVE-2026-44827, CVE-2026-45804, CVE-2026-44513 (Hugging Face Diffusers), CVE-2026-17583 (Thermo Fisher Scientific), CVE-2026-66066 (Rails), CVE-2026-10702 (Mozilla Firefox), CVE-2026-60004, CVE-2026-58443 (Gitea), CVE-2026-63077, CVE-2026-59792, CVE-2026-59793, CVE-2026-59794, CVE-2026-59795, CVE-2026-59796 (JetBrains TeamCity), CVE-2026-61511 (vBulletin), CVE-2026-53264 (Linux Kernel), CVE-2026-53921 (OpenWrt), CVE-2026-64765, CVE-2026-64766, CVE-2026-64764, CVE-2026-64763, CVE-2026-43776, CVE-2026-43818, CVE-2026-28981 (Apple iOS and macOS), CVE-2026-66032, CVE-2026-66033, CVE-2026-66034, CVE-2026-66035 (libssh2), from CVE-2026-59686 through CVE-2026-59690 (Progress Kemp LoadMaster), from CVE-2026-66036 through CVE-2026-66041 (FFmpeg), CVE-2026-66398 (phpMyFAQ), CVE-2026-64645, CVE-2026-64649, CVE-2026-64642, CVE-2026-64641 (Next.js), CVE-2026-13385 (ASUS), from CVE-2026-16804 through CVE-2026-16807 (Google Chrome), CVE-2026-52824 (Kimai), CVE-2026-53565, CVE-2026-53566 (Citrix Secure Access Client for Windows and Citrix Endpoint Analysis Client for Windows), CVE-2026-9770, CVE-2026-13230 (TP-Link Kasa EC70 v4 and EC71 v4 smart cameras), CVE-2026-15682 (AnyDesk), CVE-2026-53481, CVE-2026-53483 (Dell PowerProtect Data Domain), CVE-2026-52886, CVE-2026-54758, CVE-2026-57233 (Notepad++), CVE-2026-57807 (miniOrange OAuth Single Sign On – SSO WordPress plugin), CVE-2026-28302, from CVE-2026-28304 through CVE-2026-28317, CVE-2026-28321 (SolarWinds Serv-U), CVE-2026-16771 (AT&T Arris BGW210-700), CVE-2026-13723 (Develar), CVE-2026-16637 (OPeNDAP Hyrax), CVE-2026-15969, CVE-2026-15971, CVE-2026-15974, CVE-2026-15976, CVE-2026-15977, CVE-2026-15978 (SGLang), CVE-2026-15657, CVE-2026-15658 (foreUP), CVE-2026-16503, CVE-2026-16504 (VPS.org), CVE-2026-48395, CVE-2026-48396 (Adobe Bridge), CVE-2026-5674 (PipeWire PulseAudio), CVE-2026-34909 (Ubiquiti UniFi OS), and CVE-2026-17059 (keycloak-services).

🎥 Cybersecurity Webinars

  • AI Can Build Exploits in Minutes. Can Your Security Team Keep Up? → AI is collapsing the time between vulnerability disclosure and attack. Advanced models can now uncover flaws, generate working exploits, and chain them into complete attack paths at machine speed. This webinar presents a practical framework for gaining the visibility, context, and response speed needed to investigate and stop threats before attackers pull ahead.
  • How to Control the Open-Source Security Debt Created by AI Coding Tools → Learn how AI coding tools are expanding unvetted open-source use, accelerating vulnerability backlogs, and weakening existing governance. This webinar shows how to measure the resulting remediation debt, connect it to breach, audit, and productivity risks, and identify which governance models can contain it without slowing development.

📰 Around the Cyber World

  • Now-Patched Gitea Flaw Detailed – NoScope shared additional technical details of a security flaw in Gitea (CVE-2026-27771, CVSS score: 8.2) that was patched back in May 2026. The vulnerability allowed unauthenticated remote attackers to pull private container images from Gitea deployments without requiring an account, password, or other credentials. «Gitea’s container registry implements the OCI Distribution Specification, which authenticates clients with a bearer token issued by a dedicated token service. On affected versions, that token service issued a valid, signed JWT to requesters presenting no credentials at all,» NoScope said. «The token was honest about what it represented, carrying UserID: -1 and an empty Scope, but no registry read endpoint ever consulted those fields. Catalog listing, tag enumeration, manifest retrieval and blob download all accepted it. Any unauthenticated party on the internet could enumerate every container repository on an instance, including those marked private, and pull their layers.»
  • SQLite Critical CVEs or AI Slop? – JFrog said it uncovered a set of SQLite CVEs (CVE-2026-51302, CVE-2026-51303, CVE-2026-51300, CVE-2026-51297, CVE-2026-51296, and CVE-2026-51304) that seem to be instances of AI-generated slop making their way into official vulnerability feeds and receiving critical severity scores before technical validation. The analysis found that the advisories referenced functions that didn’t exist in the affected SQLite versions, cited incorrect or impossible source code locations, included PoCs that failed to reproduce any vulnerability, and, most importantly, were not listed on SQLite’s official CVE page. The findings show that organizations must take steps to distinguish legitimate vulnerabilities from questionable or AI-generated vulnerability reports before initiating unnecessary remediation, patching efforts, or automated security workflows.
  • LegacyHive Flaw Detailed – LevelBlue published a technical breakdown of LegacyHive, a PoC released by Chaotic Eclipse (aka Nightmare-Eclipse) last month coinciding with the release of Microsoft’s Patch Tuesday update. The vulnerability is a Local Privilege Escalation (LPE) vulnerability affecting Windows User Profile, a component responsible for loading and unloading Windows user profiles. On exploitation, LegacyHive can allow attackers to load other users’ hives and gain access to application data and Windows Explorer history, among others. «For EDR platforms with visibility into native Windows APIs, the strongest signals are user-mode invocations of NtCreateDirectoryObjectEx and NtCreateSymbolicLinkObject,» LevelBlue said. «These functions are rarely used outside system components, debugging tools, or specialized research utilities. Seeing both from the same process should immediately warrant investigation. Even without NT API telemetry, LegacyHive leaves a distinctive execution chain. The attack combines offline access to ntuser.dat or UsrClass.dat, modification of registry hives through Microsoft’s Offline Registry API, batch oplock requests, and CreateProcessWithLogonW using LOGON_WITH_PROFILE. Each operation is legitimate in isolation but observing them together within a short time window is highly unusual and well suited for behavioral correlation by EDR and SIEM platforms.»
  • Chinese Military Taps Into U.S. Models – According to a new report from Reuters, Chinese military researchers have distilled cutting-edge models developed by U.S. companies OpenAI and Anthropic to train domestic AI systems to advance the country’s defense capabilities. The report was based on a review of more than 80 Chinese academic papers and patents.
  • Exposed Police Dashboard Lays Bare How China Tracks Foreigners – An internet-exposed police dashboard named «Dynamic Control Platform for Overseas Personnel» has revealed how law enforcement agencies in the country track over 700 foreigners, including those in the northern Chinese city of Zhangjiakou. «In total, it had entries for nearly 12,000 people, which included fugitives, people from Hong Kong and Taiwan, as well as more than 300 foreign journalists,» The New York Times reported. «Some of them had not been to Zhangjiakou.» The dashboard displayed entries about people grouped by nationality, with their birth date, sex, marital status, address and occupation, and sometimes their religion. The leak was discovered by security researcher and journalist Marc Hofer. The system is believed to be developed by a Beijing company named Origin Dynamic, which filed a patent application in 2023 for a similar «information interface for non-Chinese citizens.»
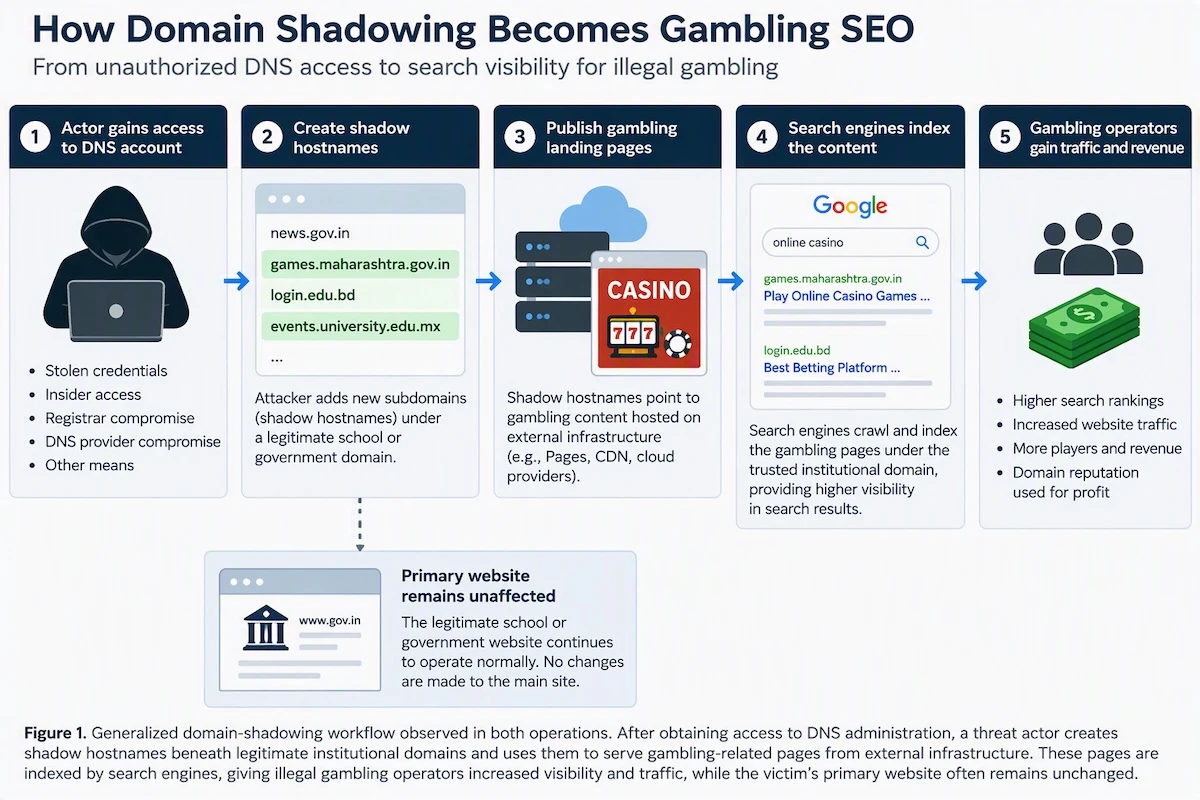
  • The Problem of DangleGeddon – Cybersecurity researchers have once again warned of the risks posed by dangling DNS infrastructure across government, banking, automotive, manufacturing, and pharmaceutical sectors. A dangling DNS record is an active Domain Name System entry (DNS) that points to a resource no longer owned, used, or controlled by the original organization. This typically occurs when web applications, cloud storage, or virtual servers are deleted without first removing their corresponding CNAME or A records from the domain registrar. An attacker can leverage this behavior to claim that abandoned cloud service name or IP address, effectively hijacking a trusted subdomain. This, in turn, can permit the attacker to host malicious content and serve phishing pages or malware, inflict reputational damage by abusing the trusted brand’s subdomain, steal user credentials to create convincing phishing pages that appear to be legitimate services, perform cookie theft, and bypass security controls if the legitimate brand’s subdomain is allowlisted in security tools. In one case analyzed by Silent Push, an unspecified automotive company left a dangling DNS record pointing to a developmental application gateway hosted by an Azure virtual machine (VM). «This device can potentially be operationalized and passively receive stored XSS from internal scripts and API calls,» it said. «Developers’ credentials, like API keys and authentication headers, could be harvested for reuse to expand access into the company. In addition, the VM could serve as a platform for malware hosting with the coveted TLS lock.»
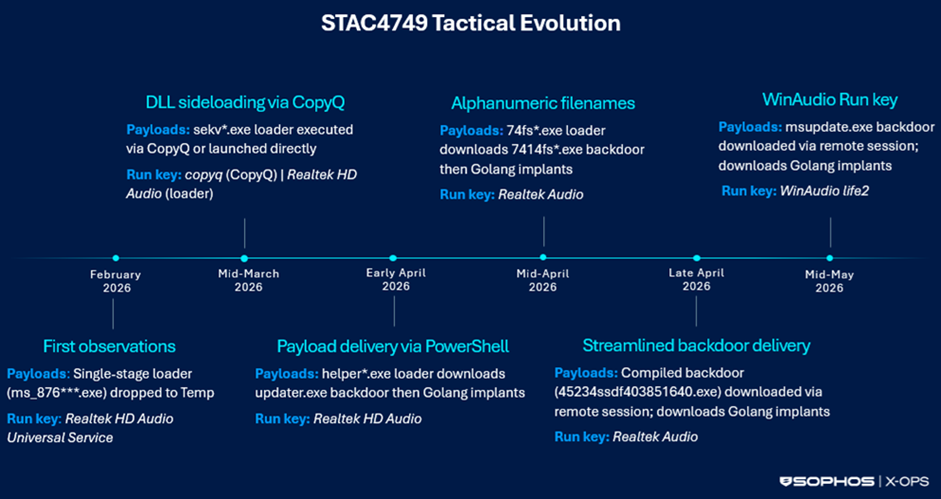
  • Microsoft Teams Vishing Leads to Chaos Ransomware – A Microsoft Teams voice phishing (vishing) campaign tracked as STAC4749 has used a «consistent set of IT-themed cloud domains and personas to gain remote access to victims’ systems» between February and June 2026 in attacks targeting dozens of North American organizations. «Following initial access, STAC4749 operators deployed a modular post-exploitation toolset, including a custom loader and backdoor to maintain persistent, controlled access and support follow-on activity,» Sophos said. «In several incidents, attackers later leveraged this access to deploy Chaos ransomware.»
  • IAB Uses Teams Phishing for Ransomware Attacks – A suspected initial access broker (IAB) for ransomware attacks has been observed using Teams vishing that convinces victims to launch a Quick Assist remote support session. The initial access is used to run PowerShell scripts to gather host information and deploy a Go-based backdoor dubbed GoGRPC. Four different versions of the backdoor have been spotted: Lep, Giver, Pet, and Kind. «These variants have overlapping capabilities but notable implementation differences,» Zscaler said. «GoGRPC is actively evolving. Each variant modifies its payloads and capabilities, adding or removing functionality to better support the threat actor’s objectives. Recent changes indicate an increased targeting of corporate environments, which may be tied to ransomware attacks.» In some instances, the threat actor has also deployed a backdoor called BlindDoor, a Go-based reverse SOCKS proxy known as RevSocket, and a Python-based reverse SOCKS proxy referred to as PyGRPC.
  • Arch Linux Disables AUR Package Adoption Amid Malware – Arch Linux has taken the step of temporarily disabling package adoption due to a surge in malicious takeovers of existing packages. «Due to the current influx of malicious package adoptions and follow-up commits made via the AUR, package adoption is currently disabled while we are handling the situation,» the maintainers said. «We will send a follow-up once we’re able to. In the meantime, feel free to report suspicious adoption events or commits that haven’t been dealt with yet, and stay vigilant!» In June 2026, a separate campaign targeted AUR via more than 400 packages.
  • New Dolphin X Infostealer Spotted – A new infostealer called Dolphin X uses an AI behavioral profiler to score and prioritize infected users based on their application usage, browsing activity, and installed software to identify high-value victims and maximize profits. The malware targets more than 300 applications and attempts to exfiltrate browser passwords, cryptocurrency wallets, SSH keys, and cloud tokens. Dolphin X has been advertised on the cybercrime underground by a vendor using the alias Kontraktnik since May 2026. A lifetime subscription ranges from $1,140 for basic access to $3,420 for the full-featured version. «A single archive can contain data from nine browsers, more than 100 wallet extensions, 65 desktop wallets, 10 password managers, and 30 cloud command-line tools,» Varonis said. «This gives the malware potential access to everything from a victim’s personal accounts to the credentials used to manage their employer’s cloud environment.»
  • Attackers Turn to Microsoft’s Trusted Login System for Phishing – Bad actors are increasingly abandoning fake Microsoft login pages in favor of abusing Microsoft’s legitimate authentication infrastructure in phishing attacks, allowing them to bypass security controls. Check Point said it identified more than 200 phishing emails targeting users across approximately 120 organizations worldwide between June 25 and the second week of July 2026. «The messages impersonated Microsoft Teams task notifications from HR and directed recipients to a legitimate Microsoft sign-in page,» it said. «Victims were then prompted to grant permissions to an attacker-controlled application, allowing the campaign to abuse Microsoft’s trusted authentication flow while concealing its malicious intent.»
  • FBI Arrests Man Accused of Using Steam Games to Drain Victims’ Crypto Wallets – The U.S. Federal Bureau of Investigation (FBI) arrested Zyaire Wilkins, a 21-year-old Florida resident and student, of uploading fake video games that contained malware to Steam that, when downloaded and installed by unsuspecting gamers, stole their passwords and other valuable data, and drained their cryptocurrency wallets. Per the FBI, Wilkins and his accomplices are alleged to have infected around 8,000 victims, and then hacked around 80 cryptocurrency wallets to steal at least $220,000 worth of cryptocurrency.
  • Turning Keystroke Noise to Text – A new study from a group of academics from Tohoku University has demonstrated a new acoustic side-channel attack that can reconstruct text typed on a laptop by just analyzing the sound of keystrokes. While prior attacks relied on collecting labeled recordings from the target keyboard beforehand or required specialized hardware, the latest eavesdropping attack enables stealthy eavesdropping in two real-world scenarios, including physical spaces (public and semi-public) and online meetings. The system works by first isolating individual keystrokes from an audio recording, grouping similar sounds together, and then using a Transformer-based language model to determine the most likely sequence of characters. «Our method combines unsupervised acoustic clustering with Transformer-based language model inference and iterative self-training, enabling stable character inference under highly uncertain acoustic-to-character mappings,» the researchers said. «We demonstrate that the proposed method achieves over 99% reconstruction accuracy with only 100-150 observed keystrokes under a close-proximity recording setup using a smartphone placed near the target device, significantly outperforming prior unsupervised baselines in low-data regimes.»
  • Two Open-Source Software Supply Chain Attack Campaigns – Socket has flagged a fake corepack.org site that’s impersonating Corepack, a Node.js tool for managing package managers, and using it as a lure to deliver an infostealer and proxyware to developers who download it. «The site has existed in some form since early 2026 as a low-quality, apparently AI-generated imitation, but it recently started serving executable downloads,» Socket said. «Corepack is not distributed as a Windows installer, and the real project has no official website at corepack.org. Any download offered there should be treated as malicious.» It’s assessed that the site is AI-generated. In a related development, JFrog identified a massive set of 148 npm packages that are disguised as student web proxies, but hide mutable remote code execution vectors and a high-performance Wisp-compatible WebSocket traffic generator. «They were designed to silently enlist visiting browsers into distributed denial-of-service botnets while generating aggressive popunder advertising revenue,» it said. Some aspects of the campaign were highlighted by SafeDep in late May 2026.
  • AI linked to more than half of cybercrime in Africa – A new report from INTERPOL has found that AI is enabling 55% of reported cybercrimes across Africa, making attacks faster, more scalable, and increasingly difficult for victims and platforms to detect. This encompasses digital sextortion and online harassment, as well as sophisticated business email compromise (BEC) schemes. «The absence of real-time, inter-agency data sharing between banks, telecoms and law enforcement creates a dangerous blind spot in efforts to combat financial fraud,» INTERPOL said. «This vulnerability is being exploited by criminals who have moved beyond simply stealing existing credentials to creating entirely synthetic identities. Combining real personal data with fabricated elements, these AI-generated digital personas can bypass even advanced biometric verification systems and have been used to open bank accounts, secure mobile loans and register SIM cards under false names.»
  • Security Risks of Exposed MCP Servers – Google-owned Wiz has warned that enterprises are exposing Model Context Protocol (MCP) servers to the internet, with some of them returning full tool catalog to an anonymous caller, fetching real data, and revealing a sensitive backend. «These expose sensitive data like employee PII and internal business records, write and delete operations on production systems, and in some cases code execution and access to cloud credentials,» Wiz said. «The protocol’s first widely-used version shipped without an authentication mechanism. The spec added OAuth 2.1 in March 2025, but nearly all the servers we found still run the original version and don’t use it. The pattern is the same across most of them: backend credentials baked into the deployment, a managed cloud endpoint that’s internet-reachable by default, no auth layer added on top.»
  • Nuclear-Sabotage Malware Benchmark Trick Most Frontier AI Models – A multi-stage reverse-engineering benchmark developed by SentinelOne tests «whether a model can keep a malware investigation trustworthy as new evidence repeatedly invalidates its earlier conclusions,» in contrast to other AI benchmarks that test bounded tasks. Developed based on its own analysis of the Fast16 malware, the study found that «OpenAI’s GPT-5.6 Sol was the only publicly available model to complete the full eight-stage investigation, giving concrete shape to what ‘Frontier-class’ capabilities offer analysts.» That said, humans remain essential to define objectives, expose blind spots, and retain final publication authority.
  • An Open Directory Reveals NGINX Rift and Ghost CMS Exploits – An exposed directory on a Singapore-hosted VPS, 165.154.236[.]93, has been found to stage exploits for NGINX Rift (CVE-2026-42945), a long-standing heap overflow, and a blind SQL injection in the Ghost Content API (CVE-2026-26980), alongside Splunk, PaperCut, Samba, WebLogic, and D-Link NAS tooling. «The recovered shell history from the directory recorded the attacker running the exploits against live external infrastructure, using out-of-band (OOB) DNS callbacks to verify execution, and using the same server to catch reverse shells,» Hunt.io said. «Alongside the web exploits were a broader RCE toolkit and pre-staged install files for AdaptixC2 and SuperShell. The target list spanned eleven countries across five continents and leaned heavily toward high-value sectors: federal and state government, universities, healthcare and financial services.» The activity is believed to be the work of a Chinese-speaking threat actor.
  • CISA Issues Guidance to Isolate Vital Systems and Manage OSS Risks – The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued guidance to help critical infrastructure operators protect essential services from growing cyber threats and ensure continuity of operations during cyber incidents or geopolitical crises by maintaining robust isolation and recovery plans. «State-sponsored cyber actors target critical infrastructure for several nefarious reasons such as espionage or service disruption, often linked to broader geopolitical conflicts,» CISA said. «During crises or conflicts, operators of critical infrastructure and network defenders may isolate essential operational technology (OT) systems as an emergency measure to prevent adversaries from executing cyberattacks, to contain ongoing threats, and to facilitate the restoration of compromised systems.» The agency has also outlined considerations and best practices for federal entities to securely use, evaluate, and publish open-source software. «The guidance urges agencies to obtain sufficient transparency into all relevant components, including training data, of the AI system before deeming the product as OSS for risk management purposes,» it said. «Only with transparency and access can agencies understand and study the software, analyze it for vulnerabilities, and remediate any found vulnerabilities or risks.»
  • RubyGems Cryptojacking Campaign – A set of 199 malicious gems published to RubyGems has been found to embed an identical XMRig cryptojacking payload to mine Monero cryptocurrency on developer systems. «Each gem is a trojanized copy of a popular, legitimate Ruby library,» Palo Alto Networks Unit 42 said. «The payload uses a 5-hour delayed Thread.new{sleep 18000; …} trigger to evade sandbox analysis.» In addition to taking steps to achieve persistence via multiple methods, the malware uses SSH for lateral movement and is capable of infecting other ecosystems, including Node.js, Python, Docker, Git, and VS Code extensions. Mend.io, which also shared details of the campaign, said the payload is hidden inside a dotfile (lib/.threadpool.rb) that standard directory scans skip by default.
  • Email Threat Landscape in Q2 2026 – Microsoft said phishing volume linked to the Tycoon 2FA phishing platform, including QR code phishing and CAPTCHA-gated phishing, fell 92% from pre-disruption averages in the second quarter of 2026 between April and June. However, the tech giant said it «observed continued growth in Teams-based social engineering, particularly voice phishing (vishing), with weekly malicious call attempts reaching nearly ten times the mid-2025 baseline by the end of the quarter.» Microsoft said it detected approximately 7.6 billion email-based phishing threats throughout the quarter, with monthly volumes declining modestly from 2.7 billion in April to 2.4 billion in June. HTML and PDF attachments remained the two most common malicious payload types across the quarter, together accounting for roughly 60-70% of all payload-based attacks each month. In early June 2026, Microsoft said it detected a large-scale BEC campaign that reached more than 67,000 users across more than 42,000 organizations in under three hours, most of them in the U.S., with an aim to redirect salary payments to attacker-controlled bank accounts.

🔧 Cybersecurity Tools

  • EMBA → Firmware is where critical bugs hide longest because it is opaque, fragmented, and painful to inspect manually. EMBA turns that black box into an actionable security report: it extracts embedded-device firmware, runs static and emulation-based analysis, builds an SBOM, and flags outdated components, insecure binaries, vulnerable scripts, and hard-coded credentials through a command-line workflow with web-based reporting. Built for penetration testers, product-security teams, and developers, it compresses days of firmware triage into a repeatable open-source process.
  • GrantGuard → Every «always allow» click in Claude Code can leave behind a standing permission that remains long after the task ends, with pasted API keys, credential-store access, unrestricted `git push`, or destructive commands buried in rarely reviewed settings. GrantGuard is an open-source, local-only tool that finds these accumulated grants, classifies them by risk, and lets users remove unsafe permissions through a browser interface or CLI, without sending settings off-device or loading third-party runtime packages.

Disclaimer: This is strictly for research and learning. It hasn’t been through a formal security audit, so don’t just blindly drop it into production. Read the code, break it in a sandbox first, and make sure whatever you’re doing stays on the right side of the law.

Conclusion

The useful question is not whether a system is exposed. It is which quiet assumption lets it reach farther than intended: a default, a trusted workflow, an abandoned endpoint, or code nobody checked.

That is where the next incident is probably waiting. Not in the loudest alert, but in the handoff everyone assumes belongs to someone else. Check the boundaries. Then check what crosses them.