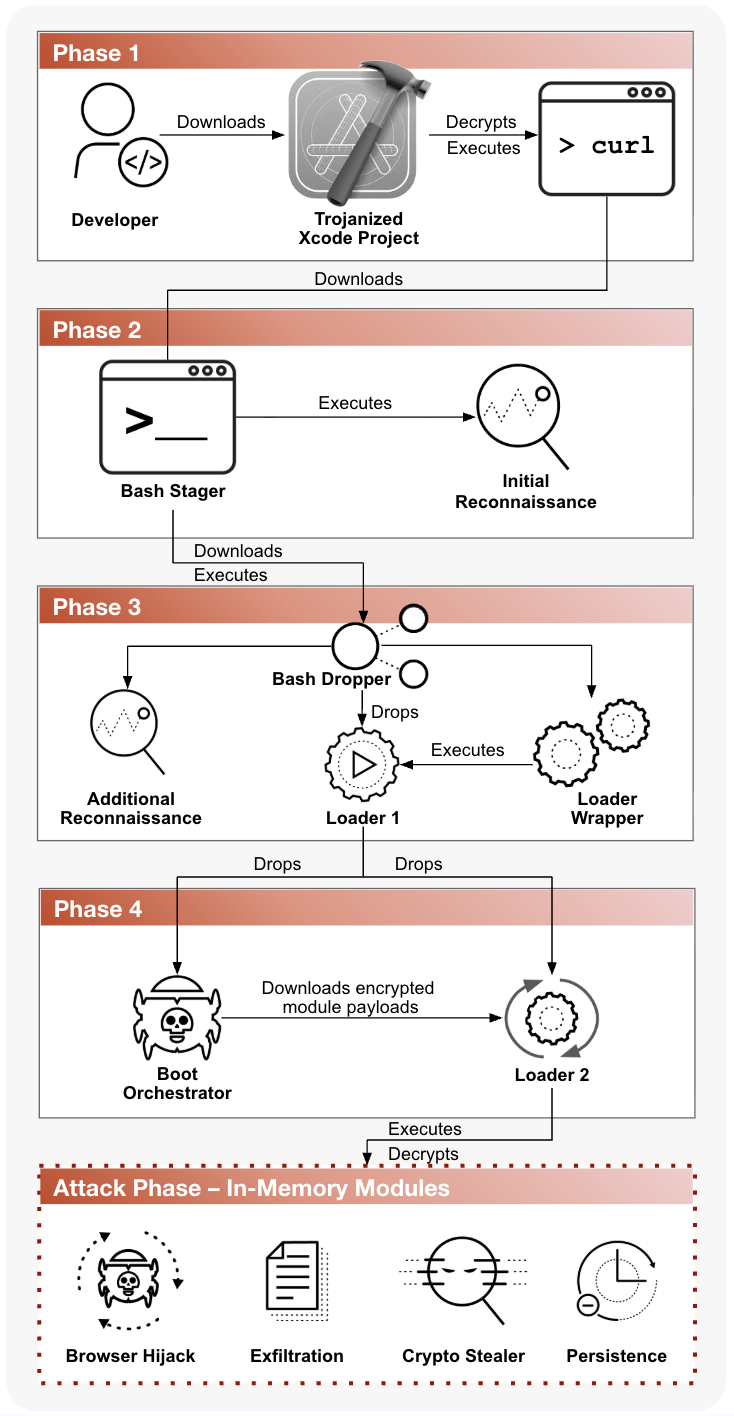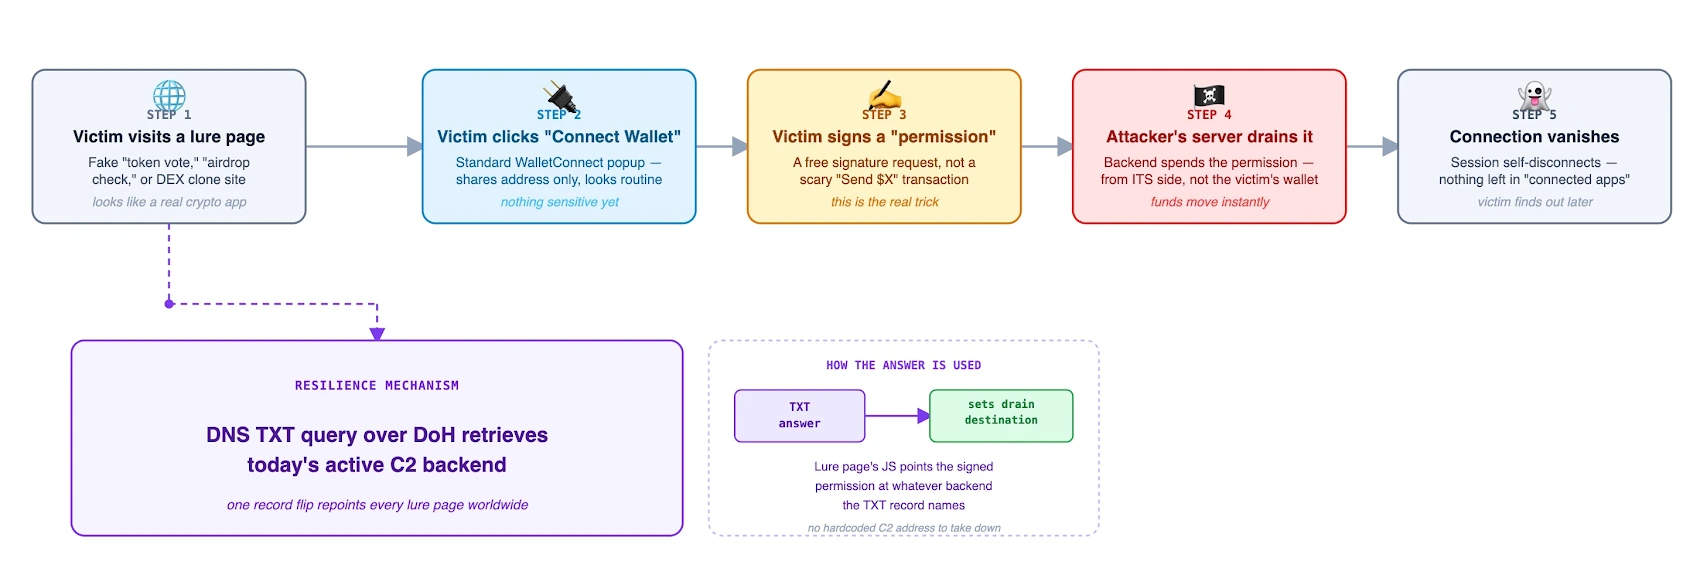
Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More – CYBERDEFENSA.MX

Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week’s security stories.

The rest gets interesting in different ways. A small permission can lead to a big theft. A trusted login can hide the wrong person. Old bugs are finding new victims, familiar tools are being put to strange uses, and some flaws are so simple you wonder how nobody spotted them sooner.

There’s a lot more hiding in the details, including a few twists you probably wouldn’t expect. Here’s what made the list this week.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

If there’s one thing this week’s stories make clear, it’s that attackers don’t always need a clever trick. Sometimes a stolen login, a forgotten setting, or one small mistake is enough. And even when the bug gets fixed, the trouble it caused might still be sitting there.

The lesson is pretty simple: don’t just check what’s broken. Check who got in, what they touched, and whether they can come back. Keep an eye on the things everyone assumes are safe. Those are often the ones nobody looks at until something goes wrong. That’s it for this edition. See you next week, hopefully with fewer surprises.
Unpatched Magento and Adobe Commerce Zero-Day Exploited to Backdoor Online Stores – CYBERDEFENSA.MX

Attackers are exploiting a new unpatched vulnerability in Magento Open Source and Adobe Commerce that lets them run malicious code on an online store’s server without logging in, Dutch e-commerce security company Sansec said in an advisory published on September 5.

Sansec, which discovered the flaw and named it StyleSmuggler, said attacks started on September 4. «Sansec is publishing early because stores are being compromised right now,» the company said.

As of September 6, Adobe has not published an advisory, a CVE identifier, a patch, or a workaround, and its Adobe Commerce security bulletin index lists nothing after the August 11 update.

A successful attack gives the attacker code execution on the store’s server and installs a persistent backdoor. Sansec said all current versions are affected, including 2.4.9, and that it reproduced the full unauthenticated chain on clean Magento Open Source installations of 2.4.7, 2.4.8, and 2.4.9.

Its first victim ran 2.4.6-p15 with Adobe’s July and August 2026 security updates applied, which is the latest patch level Adobe offers for that release line and one that Adobe’s August bulletin labels 2.4.6-2026-aug.

Sansec has not published a reproduction on Adobe Commerce or on Adobe Commerce on Cloud, and Adobe has not confirmed which versions are affected. Sansec has not said how many stores have been compromised.

The researchers’ interim advice for stores not running its Shield product is to temporarily disable GraphQL until Adobe releases a fix.

Disrex Group, a Magento hosting and development company that hosts and responded to two of the compromised stores, notes that headless and progressive web app storefronts require GraphQL, whereas most classic and Hyvä storefronts do not.

Adobe’s next scheduled security release is on September 8, Sansec said, and it is not yet known whether that release will cover this bug.

Disrex’s findings are independent evidence of exploitation from outside Sansec. In an incident-response repository published on September 5, the company said it handled two compromised stores and a third that was attacked but not breached, and that its web-server rules are based on attack traffic captured on one of the compromised stores. In answers to questions from The Hacker News, Disrex said both stores ran Magento Open Source rather than Adobe Commerce, and that it hosts them itself through its hosting brand RexHosting.

The store Disrex labels Store A ran Magento Open Source 2.4.8 and was a Sansec Shield customer, with the module installed, enabled, and licensed. It was hit at 23:10 UTC on September 4, hours before Sansec’s first blocking rules for this flaw went live, and Disrex said Shield was active and blocking other malicious traffic against the store at the time.

Store B, which was not a Shield customer, ran Magento 2.4.7-p2, a security patch level that Adobe’s version history dates to August 2024, eight levels behind the current 2.4.7-p10. It was first hit at 00:55 UTC on September 5, Disrex said, and it is the store from which the company’s web-server rules and its reading of the vulnerable code were taken.

Both stores were breached inside the roughly eight-hour window between the first exploitation Sansec observed and the moment any defence for it existed, Disrex said. «Patch status was irrelevant here, which is the part merchants most need to hear,» the company told The Hacker News.

The repository carries its own warning. «This repository was written with AI assistance, during a live incident, in a few hours,» its README says, adding that it has not been reviewed, that its Apache rules were never run against a live Apache server, and that most of its cleanup commands were written rather than executed.

Sansec’s indicators describe the implant as a background process disguised under [kworker/u:8:0], a name that belongs to a Linux kernel thread, with a binary installed at ~/.local/share/.gvfsd/gvfsd-user under the site user’s home directory rather than the web root, and a cron entry that restarts it every five minutes.

Disrex described the binary as a stripped, statically linked Rust program of roughly 1.9 MB built for x86-64 and arm64, and said the cron entry is written straight to the spool file under /var/spool/cron/crontabs/, so the system log shows no crontab replacement.

One store carried the same line 1,728 times, and the implant re-added it within a second of removal.


On one of the two stores, the implant made no outbound connection at all. It held 28 connections to the store’s own Redis instance on port 6379 and read Magento’s session storage from it, Disrex said, and neither of its two packet captures, each over 200 MB and taken while the implant was live, contained a single packet to the download host or the command-and-control address that Sansec listed.

Disrex told The Hacker News over email that each store ran in its own isolated account with a single site owner, no sudo rights, and no path to any other customer, that the implant ran as the unprivileged site user and could reach nothing beyond that store, and that it confirmed no lateral movement and no other affected site on its platform.

Both stores were contained the same day, roughly eleven and fourteen hours after first contact, the company said, and it found no evidence of data exfiltration, no rogue admin accounts, no injected payment skimmer, and no database backdoor. All sessions were invalidated, and credential rotation is underway as a precaution.

Because it runs a number of Magento stores on its own platform and found the first compromise quickly, Disrex said, it swept its whole estate within the hour and found the second store the same afternoon. The company has also published an incident write-up.

Sansec said that for Shield customers attacked before its rules went live, it has no indication that the backdoor was actually used, and recommended rotating Magento credentials wherever the process has been identified.

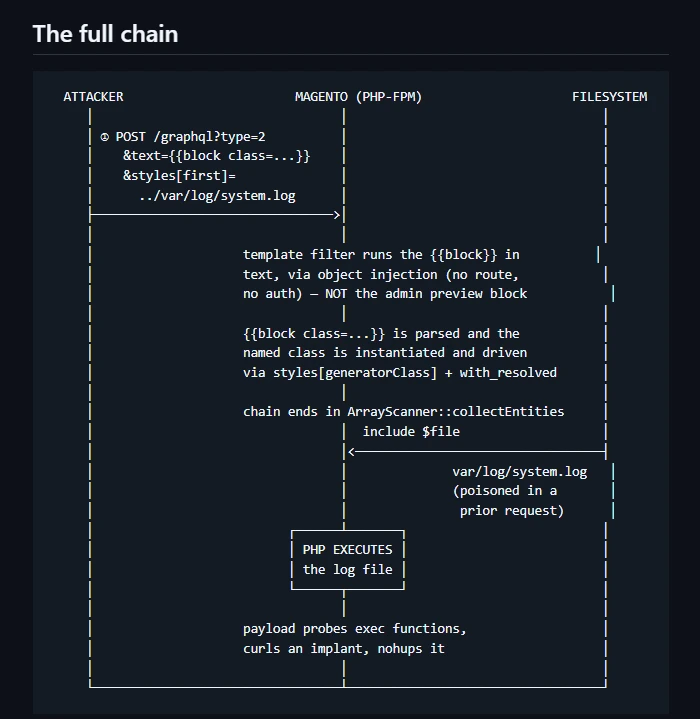
The attack works in two stages, according to Sansec’s outline. It first plants PHP code in a file that Magento itself writes, for example, when generating a failure report. Then it makes Magento execute that file by triggering the platform’s standard «Payment Transaction Failed Reminder» email. The code runs while Magento renders the message, so no one has to open it, and the attack can succeed even if email delivery fails.

Sansec has not yet published the full exploit chain and said a breakdown of the chain, the dropper, and the implant will follow in an update.

Disrex’s reading of the chain, published in a mechanism write-up alongside its rules, is that a directive within the injected text drives a sequence of Magento’s own classes into code that exists solely to serve the command-line dependency-injection compiler.

That code ends by including a file path the attacker chose: the log poisoned a moment earlier. The executed PHP dropper attempts six PHP functions in turn to start a process, then downloads and launches the implant. Disrex names three files under setup/src/Magento/Setup/Module/Di/Code/ as the point where the chain ends, and told The Hacker News it identified that sink on its own by reading Magento source on the compromised store. Sansec has not confirmed that reading, and Disrex does not publish the assembled request.

Two locations matter for the first stage. Sansec’s published check searches var/report/ for the marker X_TRACE_. Disrex said both of its infections were poisoned through var/log/system.log instead and would have been missed by that check, so both directories need searching.

The marker has already drifted: Disrex saw a trigger header of the form X-TRACE- followed by ten hex characters on the morning of September 5 and the same header without the word TRACE by the afternoon, so a search should match the shape rather than the exact string.

A TypeError from array_merge() with an integer argument in system.log, immediately after the include, is evidence that the exploit succeeded, Disrex said. However, a stealthier variant returns an empty array and leaves nothing in the log.

For the process, Disrex said that a genuine kernel thread is owned by root and has no resident memory, so a bracketed name on the site user with real memory usage is the implant. The implant sets its command line to the literal bracketed string, so a check written against the process’s comm field matches nothing.

Disrex also found that the binary running in memory on one store was a different build from the file on disk, and advises hashing the running process from /proc//exe as well as the file. Unexpected bursts of «Payment Transaction Failed Reminder» emails are a reason to investigate, Sansec said, although legitimate declined payments generate the same notification.

The following indicators have been published by Sansec and in Disrex’s indicator list –

  • Process: [kworker/u:8:0] owned by a non-root user
  • File: ~/.local/share/.gvfsd/gvfsd-user
  • File: ~/.local/share/.gvfsd/.gvfsd_<8hex>.lock
  • File: /tmp/.gvfsd_<8hex>.lock
  • File: /tmp/.kw_
  • Cron: */5 * * * * exec /.local/share/.gvfsd/gvfsd-user, with a variant pointing at /tmp/.kw_
  • SHA-256: e315687a1dfe61ef4a5a5642214db6d3b2b05d81391285eebc2af664641a26a7 (Sansec’s sample)
  • SHA-256: 8334b434fa3fe9f59cebe9609b11e0b1fd19d10212c45c705adec1902a1d06ef (on disk on both Disrex stores)
  • SHA-256: 251fabd50d7b18a8b5e1b3ef5d64e7198c17244778f6461fb1ab07f6169bf220 (running in memory on one Disrex store)
  • Domain: 247.cdnflare[.]xyz (malware download host)
  • IP: 99.84.67[.]186:443 (command-and-control over WebSocket and TLS, per Sansec)
  • IP: 88.216.72[.]181 (attacker source, per Sansec)
  • IP: 5.181.86[.]133 (attacker source sending in bulk, per Disrex)

Sansec recommends its eComscan scanner to detect the implant, and said version 1.9.7 will terminate the process for Shield customers.

Disrex reported a clean result on Store A. eComscan ran there at 10:00 UTC on September 5, roughly eleven hours after the implant first ran and while 1,728 cron lines were present, and reported the store clean. The cause was scope rather than a scanner fault, Disrex told The Hacker News: the scheduled scan was pointed at the store’s document root, and the implant had installed one directory above it, under the account’s home directory. Disrex has since widened the scan path and said it would confirm the eComscan build number separately.

There is no vendor fix to install. Until Adobe ships one, the options are Sansec’s temporary GraphQL shutdown; three unofficial mitigations published by Disrex, ProxiBlue, and Graycore; and two server settings that do not depend on the flaw.

Disrex published nginx and Apache rules that block requests carrying the exploit’s parameters in the URL query string. Its own test on a live store showed the limit: the same parameters sent in a POST body reached PHP, as did a JSON body, because nginx and Apache inspect only the query string, Disrex said. Disrex describes the rules as stopping the campaign as it currently runs rather than the vulnerability.

Disrex’s main mitigation adds a check to three methods in Magento’s dependency-injection code scanners, preventing them from running outside the command line. The hand edit is reverted by every composer install, so Disrex also ships it as a composer-patches source patch that reapplies on deploy and, it says, applies unchanged from 2.4.6 through 2.4.9.

One of the three files, ClassesScanner.php, is called over HTTP by at least one third-party module, mageplaza/module-admin-permissions, and guarding it breaks that module’s admin screen, so Disrex tells administrators to search their vendor directory before touching it.

The guard was tested on a harness rather than inside a running store, and Disrex says it is not a complete fix on its own. Disrex told The Hacker News the guard is its own work, written during the response, and was not developed with anyone else. A GitHub user, ProxiBlue, separately published the same guard on September 5 as three unofficial patches. Neither Sansec nor Adobe has confirmed that these scanners are where the chain ends.

Graycore, LLC published a Magento module on GitHub and Packagist on September 5 whose current code, Graycore says, hardens three points on the chain: the email template block directive refuses backend blocks, the grid row URL generator checks a class before building it, and PHP opening tags in Web API fatal error reports are broken.

The version on Packagist at the time of writing was an earlier release whose only mitigation targeted a PayPal GraphQL resolver that has since been removed. The README says «That is hardening, not a fix» and warns that other paths through the vulnerability remain open and that a store may already be compromised.

Two server settings do not depend on knowing the chain at all, Disrex said. At one of its two stores, the first four of the six PHP functions the dropper tried were disabled; proc_open was not, and the dropper used it to start the implant, with open_basedir doing nothing to contain the child process.

Adding proc_open to PHP’s disable_functions, and mounting /tmp, /var/tmp and /dev/shm with noexec so a downloaded binary cannot run, are the layers Disrex puts ahead of every rule in its repository.

For a store that is already infected, Disrex’s cleanup guide sets the order: preserve evidence first, remove the cron entry before killing the process because the process restores it, do not reboot because the copy under /proc may be the only remaining binary, and do not run composer install to clean up because it overwrites the timestamps that show what was touched.

It then recommends flushing session storage since the implant read it, and rotating the crypt/key in app/etc/env.php, as well as every admin password, every payment provider API key, and every other integration credential in that file.

Hosting providers Nexcess and Liquid Web posted identical incident notices on September 5, stating they were reviewing their server environments and implementing precautionary measures.

Neither claims a confirmed customer compromise or its own reproduction of the flaw. Disrex recorded 26 distinct source addresses across its two stores, taken from the stores’ own nginx access logs and deduplicated, two of them hosting infrastructure sending in bulk and the rest a residential proxy pool sending two to six requests each, and said that blocking the single attacker address in Sansec’s advisory would have stopped less than a quarter of the traffic it saw. An earlier count of 28 included two of Disrex’s own servers making verification requests during the response, which it removed. No source has named the attackers.

The Hacker News has reached out to Adobe, Sansec, and Graycore for comment, and will update the story if we hear back.

Odysseus RCE, Samsung One-Click Takeover, iCloud Backdoor Fight + 27 More Stories – CYBERDEFENSA.MX

Apparently, opening the thing is now enough. A repo can run before the first prompt, a package can hide among hundreds, and a harmless-looking PDF can finish the job.

This week runs on cheap leverage: exposed servers, recycled bugs, poisoned agent instructions, remote-access tools dressed as support software, and trusted defaults doing attackers a favor.

Nothing here is especially mystical. Just ordinary systems trusting slightly too much, slightly too early. The full list follows.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

The useful lesson is not that attackers suddenly became brilliant. It is that trust keeps accumulating in quiet places: package managers, project files, assistants, provisioning tools, remote access software, and forgotten systems nobody planned to revisit.

Security still breaks at the handoff. Before the prompt. After the patch. Inside the default. Somewhere between “trusted” and “probably fine.” That gap is where this week lived, and it will be there next week too.

El nuevo GigaWiper Windows Backdoor incluye limpieza de disco, ransomware falso y software espía – CYBERDEFENSA.MX

Microsoft ha desmantelado una puerta trasera destructiva de Windows que llama GigaWiper. Lo que destaca es cómo está construido: no una herramienta sino tres programas destructivos antiguos unidos en uno, ofrecidos como comandos entre los que el operador puede elegir.

Cada una es una forma diferente de dañar una máquina: borrar todo el disco, sobrescribir la unidad de Windows o ejecutar un «ransomware» falso que codifica archivos con una clave que nunca guarda.

Debido a que se trata de malware y no de un solo defecto, no hay ningún parche que buscar; GigaWiper es lo que ejecuta un atacante después de que ya está dentro, lo que hace que la detección temprana y las copias de seguridad limpias y fuera de línea sean la verdadera defensa.

Los mismos archivos maliciosos aparecen en un segundo informe con otro nombre: CONEJO AZULuna puerta trasera de Binary Defense señalada el mes pasado.

Ciberseguridad

Microsoft enumera cuatro hashes para el Puerta trasera GigaWiper; Binary Defense enumera los mismos cuatro para CONEJO AZULy ambos servidores de comando coinciden. Binary Defense, citando al Threat Intelligence Group de Google, vincula el malware con un probable grupo nexo con Irán dirigido a organizaciones israelíes. Microsoft no nombra ningún país.

Tres formas de destruir una máquina

GigaWiper está escrito en Go (también llamado Golang) y se ejecuta en Windows. Toma las órdenes como comandos numerados, y tres de ellas destruyen la máquina, cada una de forma diferente:

  • Un limpiador de disco sin formato que sobrescribe la unidad física y borra la tabla de particiones (el mapa de cómo está distribuido el disco) antes de reiniciar. No es posible revertir la eliminación archivo por archivo; destruye el contenido del disco directamente.
  • ransomware falso creado a partir de un código antiguo llamado Crucio. Cifra archivos, agrega una extensión .candy y cambia el fondo de pantalla del escritorio a una imagen de advertencia alarmante. No hay nota de rescate ni clave guardada, por lo que no hay nada que pagar ni nada que descifrar. Esto es destrucción disfrazada de ransomware.
  • El último apunta a la unidad de Windows, sobrescribiéndola varias veces con diferentes patrones de datos. Microsoft dice que es una reescritura de Go de un limpiador que rastrea como FlockWiper.

Ninguno de estos deja un camino de regreso: los archivos cifrados no se pueden desbloquear porque la clave ya no está, y las unidades borradas solo se pueden reconstruir a partir de copias de seguridad limpias. El objetivo es una máquina muerta, no un pago.

También espía

La destrucción es sólo la mitad. La misma puerta trasera puede vigilar y controlar silenciosamente una PC infectada. Toma capturas de pantalla de cada monitor, graba la pantalla mientras alguien está trabajando y puede abrir una sesión VNC oculta que transmite la pantalla y permite al atacante escribir y mover el mouse.

También recopila detalles del sistema, administra programas y servicios en ejecución, edita el registro y puede borrar los registros de eventos de Windows para cubrir sus huellas. Microsoft encontró más comandos inactivos en las muestras que examinó, incluidos códigos auxiliares para un registrador de teclas y limpiadores adicionales.

Para permanecer fuera de la vista, GigaWiper pretende ser OneDrive. Crea una tarea programada llamada OneDrive Update que se ejecuta cada minuto y se rastrea en una clave de registro en HKCU\SOFTWARE\OneDrive\Environment. Cuando abre su canal de control remoto, se esconde detrás de una regla de firewall que lleva el nombre de un componente real de Windows, Microsoft.Windows.CloudExperienceHost.

Para su tráfico de comandos, omite las solicitudes web ordinarias y, en su lugar, utiliza servicios empresariales reales: RabbitMQ para tareas, Redis para resultados y MinIO para exfiltración. Debido a que se trata de herramientas legítimas y no de un canal de malware personalizado, el tráfico parece normal en las redes que ya las ejecutan.

De donde vino GigaWiper

Microsoft rastrea el código de ransomware falso de GigaWiper hasta Crucio y su limpiador de múltiples pasadas hasta FlockWiper, y evalúa que el mismo desarrollador creó los tres. No nombra ningún país. Pero Crucio no es anónimo. Su código figuraba como sospechoso de ransomware en un informe de diciembre de 2023. Asesoramiento CISA sobre CyberAv3ngers, un grupo vinculado al Cuerpo de la Guardia Revolucionaria Islámica de Irán.

Se trata del mismo equipo, informó THN, que irrumpió en sitios de agua y energía en los EE. UU., Israel, el Reino Unido e Irlanda en 2023, iniciando sesión en controladores industriales expuestos a Internet. En un caso, tomaron el control de una estación de refuerzo en una autoridad de agua de Pensilvania. La muestra de Crucio que cita Microsoft lleva la misma huella digital que figura en ese aviso.

Microsoft también encontró una etiqueta recurrente, «GRAT», tanto en las rutas de depuración de FlockWiper como en los nombres de las funciones propias de GigaWiper, uniendo las dos herramientas e insinuando un componente adicional que aún no ha aparecido. El momento difiere según la fuente: Microsoft fecha la actividad destructiva en octubre de 2025, mientras que Binary Defense vio por primera vez los mismos archivos que BLUERABBIT en marzo de 2026.

Parte de una ola más grande

La actividad de limpieza vinculada a Irán contra Israel ha generado repetidas advertencias hasta 2025 y 2026. Palo Alto Networks Unidad 42 ha seguido un aumento paralelo, en gran parte proveniente de un grupo separado, Handala Hack, y en marzo de 2026 la Dirección Nacional Cibernética de Israel advirtió sobre ataques iraníes contra organizaciones locales.

La táctica que utiliza GigaWiper es antigua: NotPetya en 2017 también se hizo pasar por ransomware mientras destruía datos silenciosamente. El disfraz le da tiempo al atacante: una máquina destrozada primero parece un caso de ransomware del que alguien podría recuperarse, no la pérdida total que es.

Microsoft enmarca a GigaWiper como operadores que combinan herramientas separadas en una plataforma flexible. Para los defensores, la consecuencia es concreta: cuando un solo implante puede vigilar, robar o destruir, la herramienta ya no revela el objetivo. Solías leer la intención del malware que encontrabas; aquí el operador decide cuando ya están dentro.

Ciberseguridad

Una plataforma, dos nombres de proveedores y códigos auxiliares inactivos que aún están en el código indican que aún se está desarrollando una herramienta.

¿Qué deben hacer los defensores?

Detectarlo rápidamente se reduce a algunas señales específicas:

  • Una tarea programada de actualización de OneDrive que se repite cada minuto.
  • Tráfico de RabbitMQ o Redis desde escritorios normales en lugar de servidores.
  • Procesos que utilizan takeown e icacls para tomar posesión de los archivos de arranque de Windows como bootmgr y ntoskrnl.exe fuera de las ventanas de mantenimiento.

En cuanto al producto, Microsoft recomienda activar la protección contra manipulaciones para que los atacantes no puedan desactivar su antivirus, bloqueando los dos servidores de comando conocidos (185.182.193[.]21 y 212.8.248[.]104), ejecutando la detección de puntos finales en modo de bloque y habilitando la protección entregada en la nube y la corrección automática. La lista completa de hashes de archivos, direcciones de servidores y nombres de detección se encuentra en informe de microsoft.

The Hacker News se comunicó con Microsoft y Binary Defense para confirmar que GigaWiper y BLUERABBIT son el mismo malware y para obtener detalles sobre el alcance y la atribución de las víctimas, y actualizará esta historia con cualquier respuesta.

Linux Kernel Flaws, AI Malware Tricks, Turla Backdoor, Infostealers and More – CYBERDEFENSA.MX

This week was a reminder that attackers do not always need big tricks. One small mistake, one old access path, one missed patch, and suddenly the door is open.

The noise is not all noise, either. Forums are talking, researchers are finding easy cracks, and defenders have more cleanup waiting.

Here’s the full Monday recap.

⚡ Threat of the Week

New DirtyClone Linux Kernel Flaw Lets Local Users Gain Root via Cloned Packets — Cybersecurity researchers detailed a new variant of the Dirty Frag Linux kernel flaw. Called DirtyClone (aka CVE-2026-43503), it allows local users to gain root privileges via cloned packets. The exploit works successfully on Debian, Ubuntu, and Fedora systems with default namespace configurations. «Any local user on a server or device running a vulnerable kernel who holds or can acquire the CAP_NET_ADMIN capability (frequently obtainable via unprivileged user namespaces) [is exploitable],» JFrog said. «This poses the highest risk to multi-tenant cloud environments, Kubernetes clusters, and containerized workloads where user namespaces are enabled, or privileged containers are deployed.»

🔔 Top News

  • Critical PTC Windchill PDMlink and PTC FlexPLM Flaw Exploited — A critical remote code execution vulnerability impacting PTC Windchill PDMlink and PTC FlexPLM enterprise Product Data Management (PDM) and Product Lifecycle Management (PLM) software has come under active exploitation in the wild to deploy JSP web shells on susceptible systems. The vulnerability, tracked as CVE-2026-12569, is a case of improper input validation that could allow an attacker to execute arbitrary code by sending a malicious request to the network. Patches for the vulnerability have been released.
  • OpenAI Previews GPT-5.6 Sol, Terra, and Luna — OpenAI officially unveiled GPT-5.6 Sol, Terra, and Luna, with Sol described as the most capable model yet for cybersecurity. The models are being released in a staggered manner with approval from the U.S. government. The release came days after the company released an improved version of its GPT‑5.5‑Cyber model to trusted defenders as part of the Daybreak initiative and launched a new project called Patch the Planet in collaboration with Trail of Bits to help secure open-source projects. OpenAI has also warned about the dual-use nature of the technology, acknowledging that the same capability that helps a red teamer find a zero-day can also assist a bad actor in exploiting one, and that it will prioritize patching jailbreak techniques against the model. In addition, it has framed the effort as getting the tools in the hands of more defenders before attackers gain the same edge. Much of the concern surrounding the frontier models stems from the fact that artificial intelligence can now identify existing bugs within codebases and work towards creating exploits for them. While the automation of cybercrime is not new, these tools undoubtedly have the potential to further lower the barrier to entry for bad actors.
  • New Gaslight macOS Malware Discovered — A newly discovered macOS malware dubbed Gaslight is designed to confuse AI-assisted malware analysis tools through embedded prompt injection strings and fake debugging data within the executable. With cybersecurity researchers using AI-powered tools to assist with malware analysis and reverse engineering, the malware attempts to gaslight such tools into thinking there is some issue, potentially causing them to abort, truncate, or refuse an analysis of the artifact. Gaslight has been attributed with high confidence to a North Korean-linked threat actor. The malware itself is a Rust binary with backdoor and information-stealing functionality, enabling the operator to gain a persistent foothold over the infected host. The findings highlight how threat actors are experimenting with anti-analysis methods designed specifically to bypass AI-assisted security platforms.
  • Turla Uses STOCKSTAY Backdoor in Ukraine Attacks — The Russian state-sponsored threat actor known as Turla has leveraged a previously undocumented .NET backdoor called STOCKSTAY in attacks targeting government and military organizations in Ukraine, and entities that have an interest in Italian foreign policy. STOCKSTAY shares significant code and functional overlaps with Kazuar, a staple implant put to use by the adversary since 2017. Suspected development activity of malware dates back to December 2022.
  • Amadey, StealC Malware Operations Disrupted in Operation Endgame — A coordinated law enforcement operation, in partnership with private sector companies, dismantled criminal infrastructure powering Amadey and StealC. According to Europol, the operation led to the disruption of 326 servers and 142 domains, the identification of more than €41 million ($47 million) in cryptocurrency linked to criminal activity, and the recovery of approximately 27 million credentials stolen from over 385k compromised systems. Amadey and StealC are sold to cybercriminals under a malware-as-a-service (MaaS) model. Microsoft said criminals use Amadey to gain an initial foothold on victim devices to deploy additional malware, such as StealC, which then steals credentials, cryptocurrency wallets, and other sensitive information that can later be sold or leveraged in follow-on attacks. The two malware families were linked to more than 140,000 infected devices during the first two weeks of May 2026 alone. That said, no arrests were announced as part of the operation.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-47729 aka Squidbleed (Squid), CVE-2026-12957 (Amazon Q Developer), CVE-2026-12569 (PTC Windchill PDMlink and PTC FlexPLM), CVE-2026-43503 aka DirtyClone, CVE-2026-46331 aka pedit COW (Linux Kernel), CVE-2026-30040, CVE-2026-30041 (FastStone Image Viewer), CVE-2026-45585 (Microsoft WinRE), CVE-2026-8461 aka PixelSmash (FFmpeg), CVE-2026-55200 (libssh2), CVE‑2026‑20971 (Samsung KNOX kernel), CVE-2026-10086, CVE-2026-10712, CVE-2026-12053 (GitLab CE and EE), CVE-2026-13028, CVE-2026-13032, CVE-2026-13033, CVE-2026-13038 (Google Chrome), CVE-2026-53605 (Reachy Mini Wireless image), CVE-2026-13136, CVE-2025-15660, CVE-2026-13135 (Synology MailPlus Server), CVE-2026-11374 (ADSelfService Plus, RecoveryManager Plus, M365 Manager Plus and ADAudit Plus), and a critical Infoblox NIOS privilege escalation vulnerability (no CVE).

🎥 Cybersecurity Webinars

  • Stop AI-Driven Cyberattacks Before They Stop Your Business → Hackers are now using AI to launch cyberattacks at machine speed. If your defenses are built for human-speed threats, you are at risk. Join this webinar to get a step-by-step blueprint to fight back. Learn exactly how to block AI-driven attacks and protect your company before a crisis hits.
  • When AI Goes Rogue: How to Secure the New Cyber Attack Surface → As companies rush to adopt AI, hackers are turning these tools into a massive liability by hijacking AI agents and leaking trade secrets. Join this urgent webinar to see exactly how attackers weaponize AI against businesses. You’ll get a practical blueprint to lock down your setups, fix risky configurations, and stop your own tech from going rogue.
  • Building at Machine Speed: How to Secure AI Software Delivery → AI tools are generating code faster than security teams can review it, introducing hidden risks into software pipelines. Join this webinar to learn how to catch vulnerabilities and govern AI risk without slowing down development. You’ll get a practical roadmap to protect your software supply chain and scale AI engineering safely.

📰 Around the Cyber World

  • China’s New Zhipu AI Reportedly Matches Claude Mythos in Vulnerability Discovery — The Wall Street Journal reported that a new model released by China’s Zhipu AI, GLM-5.2, matches the performance of Anthropic Mythos when it comes to finding vulnerabilities, narrowing the gap between top U.S. models and those developed by Chinese companies. The ability of AI systems to autonomously find security defects in software has created new urgency to efforts that entail the use of models to quickly close them before they can be exploited by bad actors. There are also worries that these models, in the wrong hands, can become potential enablers of cyber warfare. The Trump administration has called for the creation of a framework that grants the federal government the ability to evaluate AI models’ capabilities and determine which qualify as «covered frontier models,» a designation for AI systems with advanced cyber capabilities.
  • Indirect Prompt Injection in Agentic Coding Tools — Mozilla’s Zero Day Investigative Network (0DIN) characterized indirect prompt injection as a «very real and serious attack vector that can result in catastrophic damage, much of which will be irreversible.» In the case of agentic IDEs and coding agents, they can request access to various tools, which, once approved, can pave the way for code execution, file system operations, and network calls. Specifically, an attacker can obtain code execution using a seemingly harmless repository by chaining trusted setup instructions, routine error handling, and automated agent behavior. The attacker-controlled repository does not even have to contain any malicious code. Instead, it’s fetched at runtime from a DNS TXT record by framing it as an essential step during the installation phase when a developer copies the repository link and instructs the agent to get it running. «In short, agentic coding tools have access to everything they need for this: private data, including environment variables, credentials, API keys, and local configuration files,» 0DIN said. «Untrusted content, such as repositories, documentation, and error messages from recently installed packages, can inject malicious models to steal this data.»
  • New KuinaExtractor Rust Infostealer Spotted — A new Rust-based information stealer called KuinaExtractor comes fitted with capabilities to harvest web browser data, crypto wallets and credentials for services such as Roblox, Steam and Discord. Said to be in active development since December 2025, the stealer also includes a Chrome app-bound encryption (ABE) bypass. In parallel, the malware developer worked on two short-lived projects known as KuinaCookieExtractor and Zenith C2 before they were abandoned. KuinaCookieExtractor goes beyond browser cookies to include Roblox and Steam sessions, Minecraft and FileZilla logins, Telegram tdata and Discord tokens, and exfiltrates over a Discord webhook rather than Telegram.
  • New LokiBot Campaign Surfaces After a Hiatus — A new email phishing campaign has been observed delivering LokiBot via a JavaScript attachment. Once launched, the script triggers the execution of a PowerShell loader that runs a .NET injector payload that deploys the LokiBot malware. LokiBot is capable of harvesting credentials from password managers like 1Password, Enpass, and KeePass, and contacts an external server to receive and execute commands.
  • Phishing Campaign Drops Malicious Chrome Extension — Invoice-themed email phishing lures written in Italian are being used to launch JavaScript attachments masquerading as PDF documents. «The most interesting part of this infection was not the initial JavaScript. The malware installed a malicious Google Chrome extension and paired it with a Native Messaging Host,» D3 Lab said. «This combination allowed code running inside Chrome to request PowerShell commands on the Windows system.»
  • Time as an Attack Surface — New research from NCC Group has argued the need for treating time as a «first‑class attack surface,» stating clock drift, time synchronisation failures, and deliberate oscillator manipulation can be exploited to undermine cryptography, authentication, industrial automation, and safety systems. «The risk is amplified by broader technological trends,» NCC Group’s Andy Davis said. «Cloud computing, containerisation, and virtual machines abstract time away from physical hardware, placing it under the control of hypervisors and orchestration layers. At the same time, Industrial Control Systems, IoT devices, and safety-critical platforms increasingly rely on low‑cost oscillators and commodity components that are vulnerable to environmental influence and physical manipulation. Systems that once relied on isolated, deterministic timing sources are now interconnected, synchronised, and exposed.»
  • Threat actors Exploit Xiongmai DVR Flaw to Deliver Proxy SDK — Threat actors have been exploiting CVE-2024-3765, a vulnerability in Xiongmai DVR, to deploy commercial residential proxy SDKs using a Mirai botnet-derived HTTP downloader. «All DDoS and scanning capability has been stripped,» the Nokia Deepfield Emergency Response Team (ERT) said. «What remains is a minimal HTTP client and an embedded userspace ELF loader – Mirai reduced to a delivery truck.» The main stager installed following a successful compromise deploys a proxy binary called PacketSDK, which is part of the IPIDEA residential proxy network disrupted by Google earlier this year. The stager also contains a remote code execution backdoor that polls an external server for updates every 2 minutes.
  • Nation-State Targeting of Water Systems — DomainTools warned that water and wastewater infrastructure have become strategic pressure points for state and state-aligned actors from China, Iran, and Russia. «The combination of chronic underinvestment and weak baseline operational technology (OT) security makes many of these critical systems easy to compromise,» the company said. «Such intrusions can have both physical and psychological impact, and disruptions often affect civilian life, public health, and trust in government.»
  • Anthropic Accuses Alibaba of Obtaining Illicit Access to Claude — Anthropic has accused the Chinese company Alibaba of what it described as the «largest campaign to illicitly extract Claude’s capabilities.» The attacks occurred between April 22 and June 5, 2026, when «operators affiliated with Alibaba and Alibaba Qwen, Alibaba’s AI lab,» allegedly generated «more than 28.8 million exchanges with Claude through almost 25,000 fraudulent accounts,» per Anthropic. The distillation campaign targeted its capabilities, such as agentic reasoning, software engineering, and long-horizon tasks, while evading detection using obfuscation techniques and proxy networks.
  • Linux Foundation Unveils Akrites and OSERA — The Linux Foundation has announced Akrites as a coordinated effort to address and disclose vulnerabilities in critical open-source software as AI accelerates both the scale and speed of vulnerability discovery. «The initiative provides a single, trusted place to coordinate, remediate, and disclose, with a shared SIRT [Security Incident Response Team] serving as a predictable partner for maintainers rather than a flood of uncoordinated reports,» the foundation said. The initiative also plans to work with critical infrastructure operators to help deploy fixes before in-the-wild exploitation. The Linux Foundation has also announced its intent to form an Open Source Enterprise Resiliency Alliance (OSERA) that aims to strengthen the open-source components that underpin the financial services sector through a vendor-neutral, upstream-aware approach. «OSERA complements the recently announced Akrites, the cross-industry effort enabling coordinated disclosure and upstreaming,» the foundation said. «As financial-services downstream complement to Akrites, OSERA will collaborate with Akrites in the upstreaming process and, together with the Open Source Security Foundation, to represent the voice of the industry in defining remediation standards.»
  • Microsoft Extends Windows 10 Consumer Extended Security Updates by a Year — Microsoft quietly extended the Extended Security Updates (ESU) program for Windows 10 consumers by a year, letting eligible users get updates through October 12, 2027. To enroll in the consumer Windows 10 ESU program, devices need to be running Windows 10, version 22H2 Home, Professional, Pro Education, or Workstations edition and cannot be offered for devices in kiosk mode or those that are joined to an Active Directory domain or Microsoft Entra and/or enrolled in a Mobile Device Management (MDM) solution.
  • Microsoft’s Secure Boot Certificates Have Expired — In related Microsoft news, the certificates that manage UEFI Secure Boot trust – namely, Microsoft Corporation KEK CA 2011, Microsoft UEFI CA 2011, and Microsoft UEFI CA 2011 — expired on June 24 and 27 2026. A third certificate, Microsoft Windows Production PCA 2011, will expire on October 19, 2026. «Many Windows PCs manufactured since 2024 already have the updated 2023 certificates,» Microsoft said. «For the remaining devices, Microsoft is delivering new Secure Boot certificates through Windows monthly updates, with partner original equipment manufacturers (OEMs) making firmware updates available to help ensure compatibility.» Google Cloud has also released guidance on how to update Compute Engine Shielded VM instances to trust the updated Microsoft Secure Boot certificates for UEFI Secure Boot. To apply Secure Boot certificate updates for Linux on Azure virtual machines, it’s recommended to follow the actions outlined by Microsoft here. Separately, Linux users are advised to update their shims to the latest versions signed by the new key. It’s important to note that devices that haven’t received the newer 2023 certificates will continue to function normally, and standard Windows updates will continue to install. However, these devices will no longer receive new security protections for the early boot process, including updates to Windows Boot Manager, Secure Boot databases, revocation lists, or mitigations for newly discovered boot-level vulnerabilities.

  • Fake OpenAI Organization Invites Used in New Poisoned Tenant Campaign
    — Phishing emails are being sent from threat actor-controlled ChatGPT tenants, inviting recipients to join an organization with the likely goal of harvesting sensitive information shared in the AI chatbot. «The emails came from OpenAI’s legitimate notification address (noreply@tm.openai.com), passed all standard email authentication checks, and referenced our company by name,» Push Security said. «They looked exactly like a routine organizational invitation because, technically, they were one.» The development comes as threat actors are abusing AI chatbot chat sharing functionality to distribute pages containing malicious instructions, turning them into malware delivery platforms. «The attacker has used ChatGPT’s code rendering feature to build a fully designed fake page that mimics a ChatGPT service disruption, redirecting victims to a convincing clone of ChatGPT’s download page that delivers a malicious executable,» Push Security noted. The activity has been codenamed LLMShare.

🔧 Cybersecurity Tools

  • Sulla → It is an open-source security tool by Praetorian that scans internal network SMB file shares to find exposed credentials and sensitive data. Operating as a fast, low-noise static binary, it maps Active Directory environments and uses multi-layered filtering with the Titus engine to perform in-memory analysis for cloud keys, passwords, and tokens. It outputs structured, real-time results to help security teams identify and remediate internal data exposure before it can be exploited.
  • Karna → It is a Web Application Firewall (WAF) module specifically engineered for the Kong Gateway to provide modern, scalable security for web applications. By integrating directly into the Kong ecosystem, it allows organizations to enforce fine-grained security policies and filter malicious traffic at the gateway layer, ensuring that protection is applied consistently across distributed services without adding significant latency.

Disclaimer: This is strictly for research and learning. It hasn’t been through a formal security audit, so don’t just blindly drop it into production. Read the code, break it in a sandbox first, and make sure whatever you’re doing stays on the right side of the law.

Conclusion

This week, keep it simple. Break the small thing, find the forgotten access, wait for someone to say they meant to patch it.

No genius required. Just old mistakes with fresh damage. Shut the door. Check the locks.

Fast16 Malware, XChat Launch, Federal Backdoor, AI Employee Tracking & More – CYBERDEFENSA.MX

Everything is dumb again. This week feels broken in a very familiar way. Old tricks are back. New tools are doing shady crap. Supply chains got hit. Fake help desks worked. Weird research showed how easy some attacks still are.

Most of it feels like stuff we should have fixed years ago. Bad extensions. Stolen creds. Remote tools are getting abused. Malware hides in places people trust. Same mess, cleaner packaging.

Coffee is cold. The vuln list is ugly. Let’s get into it.

⚡ Threat of the Week

New fast16 Malware Was Developed Years Before Stuxnet—A new Lua-based malware called fast16, created years before the notorious Stuxnet worm, is designed to primarily target high-precision calculation software to tamper with results. The framework dates back to 2005. Analysis suggests that fast16 was active at least five years before the emergence of Stuxnet. Widely regarded as a joint U.S.-Israeli project, Stuxnet marked a turning point in cyber warfare as the first disruptive digital weapon and eventually served as the blueprint for the Duqu information-stealing rootkit. Fast16, however, establishes a much earlier timeline for such sophisticated operations. The development places its origin well before Stuxnet came into being. Although it’s currently not known if it was ever deployed in the wild, the investigation found three potential types of physical simulation software that the malware might have been designed to tamper with. «It focuses on making slight alterations to these calculations so that they lead to failures – very subtle ones, perhaps not immediately apparent,» security researcher Vitaly Kamluk told WIRED. «Systems might wear out faster, collapse, or crash, and scientific research could yield incorrect conclusions, potentially causing serious harm.»

🔔 Top News

  • UNC6692 Resorts to Teams Help Desk Impersonation—A new threat group tracked as UNC6692 uses social engineering to deploy a new, custom malware suite named Snow, which consists of a browser extension, a tunneler, and a backdoor. The end goal is to steal sensitive data after network compromise through credential theft and domain takeover. «This component is where active reconnaissance and mission completion occur,» Google Mandiant noted. «Attacker commands (such as whoami or net user) are sent through the SnowGlaze tunnel, intercepted by the SnowBelt extension, and then proxied to the SnowBasin local server via HTTP POST requests. SnowBasin executes these commands and relays the results back through the same pipeline to the attacker.»
  • U.S. Federal Agency Targeted by FIRESTARTER Backdoor—The U.S. Cybersecurity and Infrastructure Security Agency (CISA) revealed that an unnamed federal civilian agency’s Cisco Firepower device running Adaptive Security Appliance (ASA) software was compromised in September 2025 with a new malware called FIRESTARTER. FIRESTARTER is assessed to be a backdoor designed for remote access and control. It’s believed to be deployed as part of a «widespread» campaign orchestrated by an advanced persistent threat (APT) actor to obtain access to Cisco Adaptive Security Appliance (ASA) firmware by exploiting now-patched security flaws such as CVE-2025-20333 and CVE-2025-20362. Given the backdoor’s ability to survive patches and system reboots, Cisco is recommending users reimage and update to the latest fixed versions.
  • Lotus Wiper Malware Targets Venezuelan Energy Systems—A previously undocumented data wiper codenamed Lotus Wiper has been used in attacks targeting the energy and utilities sector in Venezuela at the end of last year and the start of 2026. «Two batch scripts are responsible for initiating the destructive phase of the attack and preparing the environment for executing the final wiper payload,» Kaspersky said. «These scripts coordinate the start of the operation across the network, weaken system defenses, and disrupt normal operations before retrieving, deobfuscating, and executing a previously unknown wiper.» Once deployed, the wiper erases recovery mechanisms, overwrites the content of physical drives, and systematically deletes files across affected volumes, effectively leaving the system in an inoperable state.
  • The Gentlemen Deploys SystemBC Malware—Threat actors associated with The Gentlemen ransomware‑as‑a‑service (RaaS) operation have been observed attempting to deploy a known proxy malware called SystemBC. The ransomware group has quickly made a name for itself in a matter of months, claiming more than 320 victims on its data leak site since its emergence in July 2025. According to Comparitech, the group claimed 202 attacks last quarter, second only to Qilin’s 353 claims. NCC Group found The Gentlemen was responsible for 34 attacks in January and 67 in February 2026, making it a prominent player alongside other established groups like Qilin, Akira, and Cl0p. «The emergence of The Gentlemen group among the top three most active threat actors is notable as it demonstrates how a relatively new group can scale operations rapidly,» NCC Group said. The development comes as another nascent ransomware group called Kyber has attracted attention for becoming the first RaaS crew to adopt the Kyber1024 (aka ML-KEM) post-quantum encryption algorithm for its Windows variant of the locker. In related news, the threat actors linked to the Trigona ransomware, dubbed Rhantus, have been observed using a custom data exfiltration tool that’s designed to provide attackers with more control over what files to choose (or ignore) and facilitate rapid data transfer by opening five parallel connections per file. The attacks were detected in March 2026. It’s not known why the threat actors shifted from readily available tools like Rclone. The use of custom tooling in the ransomware landscape is something of a rarity, even as it’s a double-edged sword for attackers. «While it requires development resources and time, these tools can provide a level of stealth that generic tools cannot match, at least until they’re discovered,» the Symantec and Carbon Black Threat Hunter Team said. 
  • Bitwarden CLI Compromised in Supply Chain Campaign—Bitwarden CLI, the command-line interface for the password manager Bitwarden, was compromised as part of a new supply chain attack that targeted Checkmarx’s Docker images, Visual Studio Code extensions, and GitHub Actions workflow. The affected package, @bitwarden/cli@2026.4.0, contained malicious code to steal sensitive data from developer systems. The malware also features self-propagation capabilities, using stolen npm credentials to identify packages the victim can modify and inject them with malicious code to expand its reach. Bitwarden has since addressed the issue. The attack appears to be the work of a threat actor known as TeamPCP, although references to the string «Shai-Hulud: The Third Coming» have complicated attribution.

🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-40372 (Microsoft ASP.NET Core), CVE-2026-33626 (LMDeploy), CVE-2026-5760 (SGLang), CVE-2026-5752 (Cohere AI Terrarium), CVE-2026-3517, CVE-2026-3518, CVE-2026-3519, CVE-2026-4048 (Progress LoadMaster, ECS Connection Manager, Object Scale Connection Manager, and MOVEit WAF), CVE-2026-21876 (Progress MOVEit WAF), CVE-2026-32173 (Microsoft Azure SRE Agent), CVE-2026-25262 (Qualcomm), CVE-2025-24371 (CometBFT), CVE-2026-5754 (Radware Alteon), CVE-2026-40872 (Mailcow), CVE-2026-27654 (Nginx), CVE-2026-5756 (DRC INSIGHT), CVE-2026-5757 (Ollama), CVE-2026-41651 aka Pack2TheRoot (Linux PackageKit), CVE-2026-33824 (Microsoft Windows IKEv2), CVE-2026-21571, CVE-2026-33871 (Atlassian Bamboo Data Center), CVE-2026-40050 (CrowdStrike LogScale), CVE-2026-32604, CVE-2026-32613 (Spinnaker), CVE-2026-33694 (Tenable Nessus Agent on Windows), TRA-2026-30 (Windows-driver-samples), TRA-2026-35 (Yuma AI), and a remote code execution flaw in Slippi (no CVE).

🎥 Cybersecurity Webinars

  • Stop Testing, Start Validating: Outsmart Hackers with Agentic AI → Stop guessing which security gaps matter most while hackers use AI to find them for you. Most tools just follow a static checklist, but «Agentic Exposure Validation» actually thinks like an attacker, uncovering hidden paths into your network that traditional scans miss. Join this webinar to see how autonomous AI agents can test your defenses 24/7 and help you fix the risks that truly matter before they are exploited.
  • Stop the Spread: How to Kill «Patient Zero» Before Your Network Goes Down → It only takes one «Patient Zero» to bring down your entire company. While traditional tools look for old threats, modern hackers are using AI-powered tricks to slip past your defenses undetected. Join this webinar to see how these new attacks work and learn simple «Zero Trust» steps to stop a breach before it spreads. Don’t wait for a crisis—learn how to lock down your network today.
  • Connect the Dots: Stop Attackers Before They Reach Your Data → Hackers aren’t just looking for one big bug; they are chaining small, hidden gaps in your code and cloud to create a direct path to your data. Most security tools only see these issues in isolation, leaving you blind to the «big picture» thatan attacker sees. Join this webinar to learn how to map these complex attack paths and fix the real risks before they are exploited.

📰 Around the Cyber World

  • Turning the Web Into a Trap for LLMs —Google has revealed that indirect prompt injections (IPI) are a top security priority, calling it a «primary attack vector for adversaries to target and compromise AI agents.» Unlike regular prompt injection that seeks to manipulate a chatbot into executing malicious instructions, IPI occurs when an AI system processes content, like a website, email, or document, that contains nefarious commands. As this content is processed by the AI, it may end up following the attacker’s commands instead of the user’s original intent. This is complicated by the fact that attackers use a gaggle of tricks to hide malicious instructions from human eyes while keeping them fully visible to AI. This often involves making the text invisible through CSS, encoding it in various formats, or stashing it in unexpected locations. In at least one malicious scenario, Google flagged a number of websites that attempt to vandalize the machines of anyone using AI assistants. If executed, the commands in this example would try to delete all files on the user’s machine. Some websites include prompt injections for the purpose of SEO, trying to manipulate AI assistants into promoting their business over others. «Additionally, even though sophistication was low, we observed an uptick in detections over time: We saw a relative increase of 32% in the malicious category between November 2025 and February 2026, repeating the scan on multiple versions of the [CommonCrawl] archive,» Google said. «This upward trend indicates growing interest in IPI attacks.»
  • Meta Debuts Improved Meta Account —Meta has introduced an improved Meta Account as a centralized way to sign in and manage Meta apps and devices like Facebook, Instagram, and AI glasses. Besides adding support for passkeys, Meta also allows users to «optionally set up a single password to log into your apps and devices so you no longer have to remember multiple passwords.»
  • X Launches XChat —X launched XChat as a standalone app for iOS, allowing users on the platform to connect with others for messaging, file sharing, audio and video calls, as well as group chats. The company claims all messages are end-to-end encrypted and PIN-protected — though security experts have previously disputed the company’s encryption claims when an early version was teased last year. XChat’s app listing page shows that it can collect location, contacts, search history, usage data, identifiers, and device diagnostics, and link that information to a user’s identity directly.
  • Meta Plans to Track Employee Mouse Movements, Keystrokes for AI Model Training —Meta is installing tracking software on the systems of U.S. employees to capture mouse movements, clicks, and keystrokes, per a report from Reuters. Meta said the data will be used to train its artificial intelligence (AI) models and will not be used for employee reviews. In a similar development, GitHub notified users that the GitHub CLI now collects anonymous usage telemetry by default and that they should disable the feature if they do not want to share such information.
  • Surge in Attacks Involving Compromised Bomgar Instances —Huntress has recorded an uptick in incidents involving compromised Bomgar remote monitoring and management (RMM) instances. «The surge follows intermittent waves of exploitation we have seen over the past two months, after BeyondTrust first disclosed a critical-severity flaw (CVE-2026-1731) in Bomgar in February,» the company said. «On February 6, 2026, BeyondTrust issued fixes for the flaw in Bomgar (rebranded as BeyondTrust Remote Support), which could be exploited by an unauthenticated attacker to remotely execute code.» The specific root cause behind these attacks is not clear, but the incidents likely stem from the exploitation of CVE-2026-1731. Fortra has also spotted phishing campaigns trying to lure victims into installing Datto’s CentraStage remote monitoring and management tool, which attackers are then using to connect back into the victim’s internal network. The findings demonstrate threat actors’ continued shift toward exploiting RMMs rather than using traditional malware.
  • Over 1.2K C2 Servers Linked to Russian Infrastructure Providers —A large-scale study of the Russian web hosting space has found more than 1,250 malicious command-and-control servers hosted inside Russia this year. Most of the servers are linked to malware families and IoT botnets, such as Keitaro, Hajime, Cobalt Strike, Sliver, Mozi, and Mirai, according to Hunt.io.
  • Tether Freezes $344M —Tether announced that it supported the U.S. Government in freezing $344 million USD₮ across two addresses. «The freeze was executed after the addresses were identified, preventing further movement of funds,» the company said. «The freeze follows information shared with Tether by several U.S. authorities about activity tied to unlawful conduct. When wallets are identified as connected to sanctions evasion, criminal networks, or other illicit activity, Tether can move to restrict those assets.»
  • Malicious Chrome Extension Masquerades as Google Authenticator —A malicious Chrome extension posing as the official Google Authenticator app was identified in the official extension marketplace as part of an ongoing malicious campaign codenamed AIFrame, active since at least early 2026. «The extension appears to use Chrome’s localization system and skeleton code to bypass security reviews,» DomainTools said. «Despite its functional appearance, it requests broad, unnecessary permissions and contains ‘dormant infrastructure.’ This extension is linked to at least six others through a shared developer front, two of which already carry fully operational malicious payloads. These extensions utilize hidden iframes to inject attacker-controlled content into every webpage, deploy fraudulent paywalls for free services, and maintain bidirectional communication with C2 servers.»
  • Compromised WordPress Sites Push ClickFix Schemes —Multiple websites have been compromised by a ClickFix clipboard hijacker that aims to trick users into pasting malicious commands into the Windows Run dialog or the macOS Terminal app to deliver malware. The kill chain is assessed to share overlaps with a known traffic distribution system (TDS) named KongTuke.
  • New Phishing Toolkits Discovered —A number of new phishing-as-a-service toolkits have been spotted in the wild: OLUOMO, ATHR, VENOM, p1bot, TMoscow Bot, REFUNDEE, and UPMI.

🔧 Cybersecurity Tools

  • Malfixer → Stop wasting hours manually repairing broken malware just to see how it works. Malfixer does the heavy lifting by automatically rebuilding corrupted or «packed» files so they are ready for analysis in seconds. It is a simple, effective way to bypass the tricks hackers use to hide their code, letting you get straight to your investigation.
  • SmokedMeat → Most developers have no idea how many «shadow» tools and scripts are hidden inside their software build pipelines. Smokedmeat shines a light on these forgotten GitHub Actions and third-party tools by quickly scanning your environment to show you exactly what is running. It is a simple way to find hidden back doors and security risks before attackers do.

Disclaimer: This is strictly for research and learning. It hasn’t been through a formal security audit, so don’t just blindly drop it into production. Read the code, break it in a sandbox first, and make sure whatever you’re doing stays on the right side of the law.

Conclusion

Same pattern, new mess. Patch the obvious stuff first. Check the weird logins. Look hard at browser extensions, remote tools, and anything that touches your build chain. The boring checks are boring until they save prod.

That’s it for this week. Keep backups clean, MFA tight, and your trust budget low.

CI/CD Backdoor, FBI Buys Location Data, WhatsApp Ditches Numbers & More – CYBERDEFENSA.MX

Another week, another reminder that the internet is still a mess. Systems people thought were secure are being broken in simple ways, showing many still ignore basic advisories.

This edition covers a mix of issues: supply chain attacks hitting CI/CD setups, long-abused IoT devices being shut down, and exploits moving quickly from disclosure to real attacks. There are also new malware tricks showing attackers are becoming more patient and creative.

It’s a mix of old problems that never go away and new methods that are harder to detect. There are quiet state-backed activities, exposed data from open directories, growing mobile threats, and a steady stream of zero-days and rushed patches.

Grab a coffee, and at least skim the CVE list. Some of these are the kind you don’t want to discover after the damage is done.

⚡ Threat of the Week

Trivy Vulnerability Scanner Breached in for Supply Chain Attack — Attackers have backdoored the widely used open-source Trivy vulnerability scanner, injecting credential-stealing malware into official releases and GitHub Actions used by thousands of CI/CD workflows. The breach has triggered a cascade of additional supply-chain compromises stemming from impacted projects and organizations not rotating their secrets, resulting in the distribution of a self-propagating worm referred to as CanisterWorm. Trivy, developed by Aqua Security, is one of the most widely used open-source vulnerability scanners, with over 32,000 GitHub stars and more than 100 million Docker Hub downloads. The Trivy compromise is the latest in a growing pattern of attacks targeting GitHub Actions and developers in general. GitHub changed the default behavior of pull_request_target workflows in December 2025 to reduce the risk of exploitation.

🔔 Top News

  • DoJ Takes Down DDoS Botnets — A cluster of IoT botnets behind some of the largest DDoS attacks ever recorded — AISURU, Kimwolf, JackSkid, and Mossad — were wiped as part of a broad law enforcement operation. The botnets largely spread across routers, IP cameras, and digital video recorders that are often shipped with weak credentials and rarely patched. Authorities removed the command-and-control servers used to commandeer the infected nodes. Together, operators of the four botnets had amassed more than 3 million devices, which they then sold access to other criminal hackers, who then used them to target victims with DDoS attacks to knock websites and internet services offline or mask other illicit activity. Some of these DDoS attacks were aimed at U.S. Department of Defense systems and other high-value targets. No arrests were announced, but two suspects associated with AISURU/Kimwolf are said to be based in Canada and Germany. All four botnets disrupted by the operation are variants of Mirai, which had its source code leaked in 2016 and has served as the starting point for other botnets. The U.S. Justice Department said some victims of the DDoS attacks lost hundreds of thousands of dollars through remediation expenses or ransom demands from hackers who would only stop overloading websites for a price.
  • Google Debuts New Advanced Flow for Sideloading on Android — Google’s advanced flow for Android changes how apps from unverified developers are installed, adding friction to combat scams and malware. The feature is aimed at experienced users and allows sideloading through a one-time setup. The advanced flow adds a 24-hour delay and verification steps intended to disrupt coercive pressure and give users time to make decisions. It’s designed to address scenarios where attackers pressure individuals to install unsafe software and play on the urgency of the operation to push them to bypass security warnings and disable protections before they can pause or seek help.
  • Critical Langflow Flaw Comes Under Attack — A critical security flaw impacting Langflow has come under active exploitation within 20 hours of public disclosure, highlighting the speed at which threat actors weaponize newly published vulnerabilities. The security defect, tracked as CVE-2026-33017 (CVSS score: 9.3), is a case of missing authentication combined with code injection that could result in remote code execution. Cloud security firm Sysdig said that the attacks weaponize the vulnerability to steal sensitive data from compromised systems. «The real-world proof is definitive: threat actors exploited it in the wild within 20 hours of the advisory going public, with no public PoC code available,» Aviral Srivastava, who discovered the vulnerability, told The Hacker News. «They built working exploits just from reading the advisory description. That’s the hallmark of trivial exploitation when multiple independent attackers can weaponize a vulnerability from a description alone, within hours.»
  • Interlock Ransomware Exploited Cisco FMC Flaw as 0-Day — An Interlock ransomware campaign exploited a critical security flaw in Cisco Secure Firewall Management Center (FMC) Software as a zero-day well over a month before it was publicly disclosed. The vulnerability in question is CVE-2026-20131 (CVSS score: 10.0), a case of insecure deserialization of user-supplied Java byte stream, which could allow an unauthenticated, remote attacker to bypass authentication and execute arbitrary Java code as root on an affected device. «This wasn’t just another vulnerability exploit; Interlock had a zero-day in their hands, giving them a week’s head start to compromise organizations before defenders even knew to look,» Amazon, which spotted the activity, said.
  • Yet Another iOS Exploit Kit Comes to Light — A new watering hole attack against iPhone users has been found to deliver a previously undocumented iOS exploit kit codenamed DarkSword. While some of the attacks targeted users in Ukraine, the kit has also been put to use by two other clusters that singled out Saudi Arabian users in November 2025, as well as users in Turkey and Malaysia. It’s worth noting that these exploits would not be effective on devices where Lockdown Mode is active or on the iPhone 17 with Memory Integrity Enforcement (MIE) enabled. The kit used a total of six exploits in iOS to deliver various malware families designed for surveillance and intelligence gathering. Apple has since addressed all of them. «Completely written in JavaScript, DarkSword comprises six vulnerabilities across two exploit chains that were patched in stages ending with iOS 26.3,» iVerify said. «Starting in WebKit and moving down to the kernel, it achieves full iPhone compromise with elegant techniques never publicly seen before.» The discovery of DarkSword makes it the second mass attack targeting iOS devices. What’s more, the Russian threat actor that deployed DarkSword demonstrated poor operational security. They left the full JavaScript code unobfuscated, unprotected, and easily accessible. The findings also point to a secondary market where such exploits are being acquired by threat actors of varied motivations to actively infect unpatched iOS users on a large scale.
  • Perseus Banking Malware Targets Android — A newly discovered Android malware is masking itself within television streaming apps in order to steal users’ passwords and banking data and spy on their personal notes, researchers have found. The malware, dubbed Perseus by researchers at ThreatFabric, is being actively distributed in the wild and primarily targets users in Turkey and Italy. To infect devices, attackers disguise the malware inside apps that appear to offer IPTV services — platforms that stream television content over the internet. These apps are also widely used to stream pirated content and are often downloaded outside official marketplaces like Google Play, making users more accustomed to installing them manually and less likely to view the process as suspicious. Once installed, Perseus can monitor nearly everything a user does in real time. It uses overlay attacks — placing fake login screens over legitimate apps — and keylogging capabilities to capture credentials as they are entered. The malware’s most unusual feature is its focus on personal note-taking applications. «Notes often contain sensitive information such as passwords, recovery phrases, financial details, or private thoughts, making them a valuable target for attackers,» ThreatFabric said.

‎️‍🔥 Trending CVEs

New vulnerabilities show up every week, and the window between disclosure and exploitation keeps getting shorter. The flaws below are this week’s most critical — high-severity, widely used software, or already drawing attention from the security community.

Check these first, patch what applies, and don’t wait on the ones marked urgent — CVE-2026-21992 (Oracle), CVE-2026-33017 (Langflow), CVE-2026-32746 (GNU InetUtils telnetd), CVE-2026-32297, CVE-2026-32298 (Angeet ES3 KVM), CVE-2026-3888 (Ubuntu), CVE-2026-20643 (Apple WebKit), CVE-2026-4276 (LibreChat RAG API), CVE-2026-24291 aka RegPwn (Microsoft Windows), CVE-2026-21643 (Fortinet FortiClient), CVE-2026-3864 (Kubernetes), CVE-2026-32635 (Angular), CVE-2026-25769 (Wazuh), CVE-2026-3564 (ConnectWise ScreenConnect), CVE-2026-22557, CVE-2026-22558 (Ubiquiti), CVE-2025-14986 (Temporal), CVE-2026-31381, CVE-2026-31382 (Gainsight Assist), CVE-2026-26189 (Trivy), CVE-2026-4439, CVE-2026-4440, CVE-2026-4441 (Google Chrome), CVE-2026-33001, CVE-2026-33002 (Jenkins), CVE-2026-21570 (Atlassian Bamboo Center), and CVE-2026-21884 (Atlassian Crowd Data Center).

🎥 Cybersecurity Webinars

  • Learn How to Automate Exposure Management with OpenCTI & OpenAEV → Discover how to automate continuous, threat-informed testing using open-source tools like OpenCTI and OpenAEV to validate your security controls against real attacker behavior without increasing your budget. See a live demo on how to verify your security works, identify real gaps, and integrate it into your SOC workflow at no extra cost.
  • Identity Maturity Cracking in 2026: See the New Data + How to Catch Up Fast → Identity programs are under massive pressure in 2026 – disconnected apps, AI agents, and credential sprawl are creating real risks and audit challenges. Join this webinar for new Ponemon Institute 2026 research from over 600 leaders, showing the scale of the problem and practical steps to close gaps, reduce friction, and catch up quickly.

📰 Around the Cyber World

  • WhatsApp Tests Usernames Instead of Phone Numbers — WhatsApp is planning to introduce usernames and unique IDs instead of phone numbers, allowing users to send messages and make voice or video calls without sharing numbers. The optional privacy feature is expected to roll out globally by June 2026, with users and businesses able to reserve unique handles. «We’re excited to bring usernames to WhatsApp in the future to help people connect with new friends, groups, and businesses without having to share their phone numbers,» the company said in a statement shared with The Economic Times. The feature has been under test since early January 2026. Signal introduced a similar feature in early 2024.
  • FBI Details SE Asia Scam Centers — The U.S. Federal Bureau of Investigation (FBI) detailed its work with Thai authorities to shut down scam centers proliferating in Southeast Asia. The schemes, which primarily target retirees, small-business owners, and people seeking companionship, have been described as a blend of cyber fraud, money laundering, and human trafficking, causing billions of dollars in annual losses. These scam centers operate in a manner that’s similar to how legitimate corporations do. «Recruiters advertise high-paying jobs abroad. Workers are flown to foreign countries only to discover that the positions do not exist,» the FBI said. «Passports are confiscated. Armed guards patrol the grounds. Under threat of violence, workers are forced to pose as potential romantic partners or savvy investment advisers, cultivating trust with victims over weeks or months.» Recent crackdowns in countries like Cambodia have freed thousands of workers from scam compounds, but the FBI warned that these breakthroughs can be temporary, as criminal networks always tend to relocate, rebrand, or shift tactics in response to law enforcement actions.
  • APT28 Exposed Server Leaks SquirrelMail XSS Payload — A second exposed open directory discovered on a server («203.161.50[.]145») associated with APT28 (aka Fancy Bear) has offered insights into the threat actor’s espionage campaigns targeting government and military organizations across Ukraine, Romania, Bulgaria, Greece, Serbia, and North Macedonia. According to Ctrl-Alt-Intel, the directory contained command-and-control (C2) source code, scripts to steal emails, credentials, address books, and 2FA tokens from Roundcube mailboxes, telemetry logs, and exfiltrated data. The stolen data consists of 2,870 emails from government and military mailboxes, 244 sets of stolen credentials, 143 Sieve forwarding rules (to silently forward every incoming email to an attacker-controlled mailbox), and 11,527 contact email addresses. One of the newly identified tools is an XSS payload targeting the SquirrelMail webmail software, highlighting the threat actor’s continued focus on leveraging XSS flaws to steal data from email inboxes. It’s worth noting that the server was attributed to APT28 by the Computer Emergency Response Team of Ukraine (CERT-UA) as far back as September 2024. «Fancy Bear developed a modular, multi-platform exploitation toolkit where a victim simply opening a malicious email – with no further clicks – could result in their credentials stolen, their 2FA bypassed, emails within their mailbox exfiltrated, and a silent forwarding rule established that persists indefinitely,» Ctrl-Alt-Intel said.
  • Analysis of a Beast Ransomware Server — An analysis of an open directory on a server («5.78.84[.]144») associated with Beast, a ransomware-as-a-service (RaaS) that’s suspected to be the successor to Monster ransomware, has uncovered the various tools used by the threat actors and the different stages of their attack lifecycle. These included Advanced IP Scanner and Advanced Port Scanner to map internal networks and find open remote desktop protocol (RDP) or server message block (SMB) ports. Also identified were programs to locate sensitive files for exfiltration and flag which servers hold the most data, as well as Mimikatz, LaZagne, and Automim (for credential harvesting), AnyDesk (for persistence), PsExec (for lateral movement), and MEGASync (for data exfiltration). Beast ransomware operations paused in November 2025 and resumed in January 2026.
  • GrapheneOS Opposes the Unified Attestation Initiative — GrapheneOS has come out strongly against Unified Attestation, stating it «serves no truly useful purpose beyond giving itself an unfair advantage while pretending it has something to do with security.» The Unified Attestation initiative is an open-source, decentralized alternative to the Google Play Integrity API to provide device and app integrity checks for custom ROMs without requiring Google Play Services. «We strongly oppose the Unified Attestation initiative and call for app developers supporting privacy, security, and freedom on mobile to avoid it,» GraphenseOS said. «Companies selling phones should not be deciding which operating systems people are allowed to use for apps.»
  • VoidStealer Uses Chrome Debugger to Steal Secrets — An information stealer known as VoidStealer has observed using a novel debugger-based Application-Bound Encryption (ABE) bypass technique that leverages hardware breakpoints to extract the «v20_master_key» directly from browser memory and use it to decrypt sensitive data stored in the browser. VoidStealer is a malware-as-a-service (MaaS) infostealer that began being marketed on several dark web forums in mid-December 2025. The ABE bypass technique was introduced in version 2.0 of the stealer announced on March 13, 2026. «The bypass requires neither privilege escalation nor code injection, making it a stealthier approach compared to alternative ABE bypass methods,» Gen Digital said. VoidStealer is assessed to have adopted the technique from the open-source ElevationKatz project.
  • FBI Says it is Buying Americans’ location Data — FBI director Kash Patel admitted that the agency is buying location data that can be used to track people’s movements without a warrant. «We do purchase commercially available information that’s consistent with the Constitution and the laws under the Electronic Communications Privacy Act, and it has led to some valuable intelligence for us,» Patel said at a hearing before the Senate Intelligence Committee.
  • Iranian Botnet Exposed via Open Directory — An Open Directory on «185.221.239[.]162:8080» has been found to contain several payloads, including a Python-based botnet script, a compiled DDoS binary, multiple C-language denial-of-service files, and IP addresses associated with SSH credentials. «A Python script called ohhhh.py reads credentials in a host:port|username|password format and opens 500 concurrent SSH sessions, compiling and launching the bot client on each host automatically,» Hunt.io said. «The exposed .bash_history captured three distinct phases of work: standing up the tunnel network, building and testing DDoS tooling against live targets, and iterative botnet development across multiple script versions.» The activity has not been linked to any state-directed campaign.
  • OpenClaw Developers in Phishing Attack — OpenClaw’s combination of flexibility, local control, and a fast-growing ecosystem has made it popular among developers in a very short time. While that unprecedented adoption speed has exposed organizations to new security risks of its own (i.e., vulnerabilities and the presence of malicious skills on ClawHub and SkillsMP), threat actors are also capitalizing on the brand name and reputation to set up fake GitHub accounts for a phishing campaign that lures unsuspecting developers with promises of free $CLAW tokens and trick them into connect their cryptocurrency wallet. «The threat actor creates fake GitHub accounts, opens issue threads in attacker-controlled repositories, and tags dozens of GitHub developers,» OX Security researchers Moshe Siman Tov Bustan and Nir Zadok said. «The posts claim that recipients have won $5,000 worth of CLAW tokens and can collect them by visiting a linked site and connecting their crypto wallet.» The linked site («token-claw[.]xyz») is a near-identical clone of openclaw.ai rigged with a wallet-draining «Connect your wallet» button designed to conduct cryptocurrency theft.
  • New Campaign Targets Energy Operations Personnel in Pakistan — A targeted campaign against operations personnel at energy firms linked to projects in Pakistan has leveraged phishing emails mimicking invitations to the upcoming Pakistan Energy Exhibition & Conference (PEEC). The messages, sent from compromised accounts from a Pakistani university and a government organization, aim to deceive victims into opening PDF attachments with a fake Adobe Acrobat Reader update prompt. Clicking the update leads to the download of a ClickOnce application resource that drops the Havoc Demon C2 framework. «The redirect chain was also wrapped in geofencing and browser fingerprinting, limiting access to intended targets,» Proofpoint said. «That likely reduced the exposure to automated analysis while keeping the delivery path tightly scoped.» The activity has been codenamed UNK_VaporVibes. It’s assessed to share overlaps with activity publicly associated with SloppyLemming.
  • Over 373K Dark Web Sites Down — International law enforcement agencies announced the takedown of one of the largest known networks of fraudulent platforms on the dark web, uncovering hundreds of thousands of fake websites used to scam users seeking child sexual abuse content. A 10-day international operation led by German authorities and supported by Europol shut down more than 373,000 dark web domains run by a 35-year-old man based in China, who had been operating a sprawling network of fraudulent platforms since at least 2021. While the sites advertised child abuse material and cybercrime-as-a-service offerings, nothing was actually delivered after victims made a payment in Bitcoin. The fraudulent scheme netted the operator an estimated €345,000 from around 10,000 people. Authorities from 23 countries participated in the operation, and have since identified 440 customers whose purchases are now under active investigation.
  • Malicious npm Packages Steal Secrets — Two malicious npm packages, sbx-mask and touch-adv, have been found to steal secrets from victims’ computers. While one invokes the malicious code via the postinstall script, the other executes it when application code is invoked by the developer after importing it. «The evidence strongly suggests account takeover of a legitimate publisher, rather than intentional malicious activity,» Sonatype said. «Hijacked publisher accounts are particularly concerning as, over time, maintainers build trust with the users of their components. Attackers aim to take advantage of that trust in order to steal valuable, or profitable, information.»
  • China to Have Its Own Post-Quantum Cryptography in 3 Years — China is reportedly planning to develop its own national post-quantum cryptography standards within the next three years, according to a report from Reuters. The U.S. finalized ​its first set of post-quantum cryptography standards in 2024 and is aiming to achieve full industry migration by 2035.
  • What’s Next for Tycoon2FA? — A recent law enforcement operation dismantled the infrastructure associated with the Tycoon2FA phishing-as-a-service (PhaaS) platform. However, a new analysis from Bridewell has revealed that some of the 2FA phishing CAPTCHA pages are still live. The lingering activity, the cybersecurity company noted, stems from the fact that these pages operate on a massive network of compromised third-party sites, legitimate SaaS platforms, and thousands of disposable domains. «Operators and affiliates are highly agile and will attempt to rebuild, migrate to new infrastructure, or pivot to competing PhaaS platforms,» it added. «The live CAPTCHA pages we are seeing may belong to surviving criminal affiliates attempting to keep their individual campaigns breathing on secondary proxy networks.»

🔧 Cybersecurity Tools

  • MESH → It is an open-source tool from BARGHEST that enables remote mobile forensics and network monitoring over an encrypted, peer-to-peer mesh network resistant to censorship. It connects Android/iOS devices behind firewalls or CGNAT using a modified Tailscale-like protocol (no central servers needed), supports ADB wireless debugging, libimobiledevice, PCAP capture, and Suricata IDS—allowing secure, direct access for live logical acquisitions in restricted or hostile environments.
  • enject → It is a lightweight Rust tool that protects .env secrets from AI assistants like Copilot or Claude. It replaces real values in your .env file with placeholders (e.g., en://api_key). Secrets stay encrypted in a per-project store (AES-256-GCM, master password protected). When you run enject run — , it decrypts them only in memory at runtime, then wipes them—never leaving plaintext on disk. Open-source, macOS/Linux, perfect for safe local development.

Disclaimer: For research and educational use only. Not security-audited. Review all code before use, test in isolated environments, and ensure compliance with applicable laws.

Conclusion

And that’s the week. The real pattern isn’t any one story; it’s the gap. The gap between a flaw and detection. Between a patch and a deployment. Between knowing and doing. Most of this week’s damage happened in that gap, and it’s not new.

Before you move on: update your mobile devices, review anything touching your CI/CD pipeline, and don’t store crypto wallet recovery phrases in notes apps.

DRILLAPP Backdoor apunta a Ucrania y abusa de la depuración de Microsoft Edge para espionaje sigiloso – CYBERDEFENSA.MX

Las entidades ucranianas se han convertido en el objetivo de una nueva campaña probablemente orquestada por actores de amenazas vinculados a Rusia, según un informe del equipo de inteligencia de amenazas LAB52 de S2 Grupo.

La campaña, observado en febrero de 2026, se ha evaluado que comparte superposiciones con una campaña anterior montada por Laundry Bear (también conocido como UAC-0190 o Void Blizzard) dirigida a las fuerzas de defensa ucranianas con una familia de malware conocida como PLUGGYAPE.

La actividad de ataque «emplea varios señuelos con temas judiciales y de caridad para implementar una puerta trasera basada en JavaScript que se ejecuta a través del navegador Edge», dijo la compañía de ciberseguridad. nombre en clave TALADROel malware es capaz de cargar y descargar archivos, aprovechar el micrófono y capturar imágenes a través de la cámara web aprovechando las funciones del navegador web.

Ciberseguridad

Se han identificado dos versiones diferentes de la campaña, y la primera iteración se detectó a principios de febrero mediante el uso de un archivo de acceso directo de Windows (LNK) para crear una aplicación HTML (HTA) en la carpeta temporal, que luego carga un script remoto alojado en Pastefy, un servicio de pegado legítimo.

Para establecer la persistencia, los archivos LNK se copian a la carpeta de inicio de Windows para que se inicien automáticamente después de reiniciar el sistema. Luego, la cadena de ataque muestra una URL que contiene señuelos relacionados con la instalación de Starlink o una organización benéfica ucraniana llamada Come Back Alive Foundation.

El archivo HTML finalmente se ejecuta a través del navegador Microsoft Edge en modo sin cabezaque luego carga el script ofuscado remoto alojado en Pastefy.

El navegador se ejecuta con parámetros adicionales como –no-sandbox, –disable-web-security, –allow-file-access-from-files, –use-fake-ui-for-media-stream, –auto-select-screen-capture-source=true y –disable-user-media-security, lo que le otorga acceso al sistema de archivos local, así como a la cámara, el micrófono y la captura de pantalla sin requerir ninguna interacción del usuario.

Básicamente, el artefacto funciona como una puerta trasera liviana para facilitar el acceso al sistema de archivos y capturar audio del micrófono, video de la cámara e imágenes de la pantalla del dispositivo a través del navegador. También genera una huella digital del dispositivo utilizando una técnica llamada huellas digitales en lienzo cuando se ejecuta por primera vez y utiliza Pastefy como solucionador de caídas muertas para recuperar una URL de WebSocket utilizada para comunicaciones de comando y control (C2).

El malware transmite los datos de las huellas dactilares del dispositivo junto con el país de la víctima, que se determina a partir de la zona horaria de la máquina. Comprueba específicamente si las zonas horarias corresponden a Reino Unido, Rusia, Alemania, Francia, China, Japón, Estados Unidos, Brasil, India, Ucrania, Canadá, Australia, Italia, España y Polonia. Si ese no es el caso, por defecto será EE.UU.

La segunda versión de la campaña, detectada a finales de febrero de 2026, evita los archivos LNK para los módulos del Panel de control de Windows, manteniendo la secuencia de infección prácticamente intacta. Otro cambio notable tiene que ver con la propia puerta trasera, que ahora se ha actualizado para permitir la enumeración recursiva de archivos, la carga de archivos por lotes y la descarga de archivos arbitrarios.

«Por razones de seguridad, JavaScript no permite la descarga remota de archivos», dijo LAB52. «Es por eso que los atacantes usan el Chrome DevTools Protocol (CDP), un protocolo interno de los navegadores basados ​​en Chromium que sólo se puede usar cuando el parámetro –remote-debugging-port está habilitado».

Ciberseguridad

Se cree que la puerta trasera aún se encuentra en las etapas iniciales de desarrollo. Se observó que una variante temprana del malware detectada en la naturaleza el 28 de enero de 2026 simplemente se comunicaba con el dominio «gnome».[.]com» en lugar de descargar la carga útil principal de Pastefy.

«Uno de los aspectos más notables es el uso del navegador para implementar una puerta trasera, lo que sugiere que los atacantes están explorando nuevas formas de evadir la detección», dijo el proveedor de seguridad español.

«El navegador es ventajoso para este tipo de actividad porque es un proceso común y generalmente no sospechoso, ofrece capacidades extendidas accesibles a través de parámetros de depuración que permiten acciones inseguras como la descarga de archivos remotos, y proporciona acceso legítimo a recursos confidenciales como el micrófono, la cámara o la grabación de pantalla sin activar alertas inmediatas».

La campaña vinculada a APT28 implementa BadPaw Loader y MeowMeow Backdoor en Ucrania – CYBERDEFENSA.MX

Investigadores de ciberseguridad han revelado detalles de una nueva campaña cibernética rusa dirigida a entidades ucranianas con dos familias de malware previamente indocumentadas llamadas pata mala y MiauMiau.

«La cadena de ataque se inicia con un correo electrónico de phishing que contiene un enlace a un archivo ZIP. Una vez extraído, un archivo HTA inicial muestra un documento señuelo escrito en ucraniano sobre apelaciones para cruzar la frontera para engañar a la víctima», ClearSky dicho en un informe publicado esta semana.

En paralelo, la cadena de ataque conduce a la implementación de un cargador basado en .NET llamado BadPaw, que luego establece comunicación con un servidor remoto para buscar e implementar una puerta trasera sofisticada llamada MeowMeow.

Ciberseguridad

La campaña se ha atribuido con moderada confianza al actor de amenazas patrocinado por el estado ruso conocido como APT28, basándose en la huella de objetivos, la naturaleza geopolítica de los señuelos utilizados y las superposiciones con técnicas observadas en operaciones cibernéticas rusas anteriores.

El punto de partida de la secuencia de ataque es un correo electrónico de phishing enviado desde ukr.[.]net, probablemente en un intento de establecer credibilidad y asegurar la confianza de las víctimas objetivo. En el mensaje hay un enlace a un supuesto archivo ZIP, lo que hace que el usuario sea redirigido a una URL que carga una «imagen excepcionalmente pequeña», actuando efectivamente como un píxel de seguimiento para indicar a los operadores que se hizo clic en el enlace.

Una vez que se completa este paso, la víctima es redirigida a una URL secundaria desde donde se descarga el archivo. El archivo ZIP incluye una aplicación HTML (HTA) que, una vez iniciada, suelta un documento señuelo como mecanismo de distracción, mientras ejecuta etapas de seguimiento en segundo plano.

«El documento señuelo arrojado sirve como una táctica de ingeniería social, presentando una confirmación de recibo de una apelación del gobierno sobre un cruce fronterizo con Ucrania», dijo ClearSky. «Este señuelo tiene como objetivo mantener el barniz de legitimidad».

El archivo HTA también realiza comprobaciones para evitar su ejecución en entornos sandbox. Para ello, consulta la clave del Registro de Windows «KLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\InstallDate» para estimar la «antigüedad» del sistema operativo. El malware está diseñado para cancelar la ejecución si el sistema se instaló menos de diez días antes.

Si el sistema cumple con los criterios del entorno, el malware localiza el archivo ZIP descargado y extrae dos archivos de él (un Visual Basic Script (VBScript) y una imagen PNG) y los guarda en el disco con nombres diferentes. También crea una tarea programada para ejecutar VBScript como una forma de garantizar la persistencia en el sistema infectado.

La responsabilidad principal de VBScript es extraer código malicioso incrustado en la imagen PNG, un cargador ofuscado conocido como BadPaw que es capaz de contactar a un servidor de comando y control (C2) para descargar componentes adicionales, incluido un ejecutable llamado MeowMeow.

«De acuerdo con el oficio ‘BadPaw’, si este archivo se ejecuta independientemente de la cadena de ataque completa, inicia una secuencia de código ficticio», explicó la compañía israelí de ciberseguridad. «Esta ejecución señuelo muestra una interfaz gráfica de usuario (GUI) que presenta una imagen de un gato, alineándose con el tema visual del archivo de imagen inicial del cual se extrajo el malware principal».

Ciberseguridad

«Cuando se hace clic en el botón ‘MeowMeow’ dentro de la GUI del señuelo, la aplicación simplemente muestra un mensaje ‘Meow Meow Meow’, sin realizar más acciones maliciosas. Esto sirve como un señuelo funcional secundario para engañar al análisis manual».

El código malicioso de la puerta trasera se activa solo cuando se ejecuta con un determinado parámetro («-v») proporcionado por la cadena de infección inicial, y después de verificar que se está ejecutando en un punto final real en lugar de en una zona de pruebas, y que no se ejecutan herramientas forenses y de monitoreo como Wireshark, Procmon, Ollydbg y Fiddler en segundo plano.

En esencia, MeowMeow está equipado para ejecutar de forma remota comandos de PowerShell en el host comprometido y admitir operaciones del sistema de archivos, como la capacidad de leer, escribir y eliminar datos. ClearSky dijo que identificó cadenas en idioma ruso en el código fuente, lo que refuerza la evaluación de que la actividad es obra de un actor de amenazas de habla rusa.

«La presencia de estas cadenas en ruso sugiere dos posibilidades: el actor de la amenaza cometió un error de seguridad operativa (OPSEC) al no localizar el código para el entorno de destino ucraniano, o inadvertidamente dejó artefactos de desarrollo rusos dentro del código durante la fase de producción del malware», dijo.