
Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks – CYBERDEFENSA.MX
A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week.
The trouble keeps showing up inside things people already trust: code that takes a bad turn, old payloads coming back, exposed systems, weak checks, fake fixes, and attack paths that look almost too easy. Even the research side is getting messy, with more findings, more automation, and not always more clarity.
Nothing here needs much drama. Just a lot of small doors left open. Here’s what happened.
⚡ Threat of the Week
Cisco Warns of Actively Exploited ISE Auth Bypass — Cisco warned of a fresh maximum-severity security flaw impacting Identity Services Engine (ISE) that has come under active exploitation. The vulnerability, tracked as CVE-2026-76460 (CVSS score: 10.0), could allow an unauthenticated, remote attacker to bypass authentication. «This vulnerability is due to insufficient authentication control on an API endpoint,» Cisco said. «An attacker could exploit this vulnerability by sending a crafted request to an affected API endpoint. A successful exploit could allow the attacker to gain unauthorized access to the affected device by bypassing the web-based management interface.»
🔔 Top News
- U.S. Seizes NightmareStresser Domains Linked to DDoS Attacks — A U.S. court-authorized operation seized two domains associated with NightmareStresser, which offered a distributed denial-of-service (DDoS)-for-hire service. NightmareStresser is assessed to have been used to launch hundreds of thousands of actual or attempted DDoS attacks against victims across the world since 2022. These attacks have targeted educational institutions, government agencies, gaming platforms, and millions of people, the U.S. Justice Department said.
- Using Claude to Hack OpenAI — Hacktron said it used Anthropic’s Claude Opus 5 to chain two critical vulnerabilities – an SSO misconfiguration in OpenAI’s identity infrastructure and a libheif RCE in the Discourse community forum (CVE-2026-32882) – to gain unauthorized access to OpenAI employees’ ChatGPT accounts and then use them to access internal OpenAI repositories. The issue was fixed 14 hours after responsible disclosure. Upstream, the flaw was fixed in libheif 1.22.0 in May 2026.
- Plugin4Shell for 0-Click RCE in AI Coding Agents — AIR Security demonstrated a flaw called Plugin4Shell, a zero-click remote code execution (RCE) vulnerability that bypasses SHA-pinning verification in four major AI coding agents: Claude Code, OpenAI Codex, GitHub Copilot, and Google Gemini CLI. «In this first-of-its-kind AI supply-chain attack, a trusted plugin is silently swapped for a malicious one and auto-installed past the agent’s SHA pinning — a flaw no marketplace can fix, so users must update their agent,» AIR Security said. «It is a plugin SHA-pinning bypass: the agent checks out the exact commit the marketplace pinned but never verifies it landed there, so an attacker who controls the plugin’s repo makes the checkout resolve to malicious code while the pin still looks honored. The result is zero-click remote code execution across Claude Code, Codex, GitHub Copilot, and Gemini CLI.»
- OpenAI Reveals New Misalignment Incidents — OpenAI disclosed six new instances of «unexpected or concerning model behavior» that took place over the past six months, while sharing a new framework for reporting, tracking, investigating, and disclosing model misalignment in a bid to improve transparency. «As AI systems grow more advanced and more widely deployed, we need to build a broader and better-informed consensus on the progress of alignment research,» OpenAI said. «We do not believe that the AI industry has solved alignment and monitoring to a sufficient degree to continue responsibly scaling at maximum speed for much longer.»
- KREMLIN Banking Malware Hijacks Chrome and Edge for Credential Theft — A previously undocumented Brazilian banking malware operation has been found to deliver a toolkit called KREMLIN. Active since at least May 2025, the threat actor has used lures that impersonate a dozen Brazilian banks and install a malicious browser extension on Google Chrome and Microsoft Edge. «The KREMLIN malware ecosystem employs multi-stage JavaScript loaders, custom C++ installers, and malicious browser extensions to steal credentials, session tokens, and sensitive data,» Elastic said. The activity is being tracked as REF9334.
️🔥 Trending CVEs
Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.
Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-58138 (Orkes Conductor), CVE-2026-58704 (Google Pixel), CVE-2026-90894 aka ParaShells (Parallels Desktop), CVE-2026-82079 (Nintendo Switch), CVE-2026-89049 (AWS Systems Manager Agent), CVE-2026-43502 aka ZcopyReaper, CVE-2026-80844 aka DirtyAH6, CVE-2026-81000 aka TUNderflow, CVE-2026-68121 aka PPPoEject, CVE-2026-74469 aka DiagSpill (Linux kernel), CVE-2026-70416, CVE-2025-43936 (Dell ObjectScale and Elastic Cloud Storage), CVE-2026-68488 (Please Backup Manager), CVE-2026-56711, CVE-2026-73324 (VLC Media Player), CVE-2026-65638 (cPanel ConfigServer Security & Firewall), CVE-2026-85982, CVE-2026-78626, CVE-2026-78623 (Okta), CVE-2026-0310 (Palo Alto Networks PAN-OS), CVE-2026-85061 (MapLibre GL JS), GHSA-rvhw-4hpw-9vrx, GHSA-rrgq-978q-36mq, GHSA-4xhx-8cv5-wh62, GHSA-8v35-895w-232p (ArangoDB), CVE-2026-65812 (Microsoft Teams for Android), CVE-2026-80172, CVE-2026-61410, CVE-2026-80238 (Dell Secure Connect), CVE-2026-18851 (Ivanti Endpoint Manager Mobile), CVE-2026-91721, CVE-2026-91749, CVE-2026-91726, CVE-2026-93374, CVE-2026-93372 (Google Chrome), CVE-2026-92033, from CVE-2026-92005 to CVE-2026-92013, from CVE-2026-92015 to CVE-2026-92020, from CVE-2026-92022 to CVE-2026-92029, from CVE-2026-92034 to CVE-2026-92038 (Mozilla Firefox), CVE-2026-15315, CVE-2026-15316 (TP-Link Tapo cameras), CVE-2026-82232, CVE-2026-77147, CVE-2026-73178 (Apache Syncope), CVE-2026-76669, CVE-2026-76670, CVE-2026-76672, CVE-2026-76673, CVE-2026-76674 (HPE Networking EdgeConnect SD-WAN Gateways and SD-WAN Orchestrator), CVE-2026-73693, CVE-2026-73694, CVE-2026-73698, CVE-2026-73699 (FileRun), CVE-2026-39919 (Ghostscript), CVE-2026-91998 (Casdoor), CVE-2026-91932, CVE-2026-91931 (Flowise), CVE-2026-65400, CVE-2026-65414, CVE-2026-65346, CVE-2026-84607, CVE-2026-43790 (Apple), CVE-2026-90999 (Sentry Seer), CVE-2026-77692, CVE-2026-76163, CVE-2026-19667, CVE-2026-19666, CVE-2026-80274 (ISC BIND 9), CVE-2026-91843 (Check Point), CVE-2026-77179 (Docker), CVE-2026-81642, CVE-2026-82717 (Unbound DNS), Click2Shell (WordPress), CVE-2026-28326, CVE-2026-28323, CVE-2026-28309, CVE-2026-28306, CVE-2026-28308, CVE-2026-28310, CVE-2026-28314, CVE-2026-28313, CVE-2026-28307, CVE-2026-28305, CVE-2026-28317, CVE-2026-28304, CVE-2026-28312, CVE-2026-28316, CVE-2026-28311, CVE-2026-28302, CVE-2026-28321, CVE-2026-28315 (SolarWinds), CVE-2026-89026 (Issabel Framework), CVE-2026-78175 (Tutor LMS), an operating system command injection vulnerability in Dokploy, and a pickle deserialization vulnerability in MLflow.
🎥 Cybersecurity Webinars
- How to Find and Control AI Agents Before Access Gets Out of Hand → AI agents are getting access to apps, data, credentials, and workflows faster than most teams can govern them. The real problem is not adoption — it is knowing which agents exist, what they can reach, and where access has quietly become too broad. This webinar breaks down how to bring AI agents under control without slowing down the teams using them.
- AI Attacks Move in Minutes. Here’s How to Stop Them at Runtime → AI-powered attacks are shrinking the time defenders have to react. By the time a traditional alert is investigated, the attacker may already have moved through the environment. This webinar shows how runtime identity security can make access decisions in real time, block risky activity earlier, and give security teams a better chance against machine-speed attacks.
📰 Around the Cyber World
- Google Doc Leads to ClickFix Attack — Huntress disclosed details of a ClickFix attack in which a security researcher was targeted in an X exchange by a threat actor posing as a crypto marketing executive. «The threat actor sent a link to a real Google Doc with a custom sidebar designed to trick the recipient into downloading malware: an AMOS infostealer on macOS, or a PowerShell loader chain on Windows,» Huntress said. «The Google Doc featured a sidebar displaying a fake decryption failure message, with supposed remediation instructions for users of different operating systems, including the option to copy and paste certain commands into the Terminal. This ClickFix lure, and the «manual update» button beside it, are what actually delivered the malware. The sidebar itself was a Google Apps Script bound to the document, so nothing had to be downloaded for it to run.» The Apps Script executed client-side in the victim’s browser, and collected the victim’s public IP address and geolocation and scanned for crypto wallets.
- Brevo Supply Chain Attack Injects ClickFix Scripts on Customer Sites — Customer engagement platform Brevo fell victim to a supply chain attack that led to malicious code being injected into over 100,000 websites. «On 14 September 2026, an attacker used a compromised Brevo Cloudflare API key to deploy a Cloudflare Worker on our account,» Brevo said. «For about five and a half hours, the Worker injected a malicious script into pages of brevo.com and sibforms.com and into three JavaScript files that customers embed on their own websites.» The script showed selected visitors a fake Cloudflare CAPTCHA prompt that instructed visitors to paste and run a malicious command on their computer, a technique also called ClickFix. Sansec, which shared additional details of the attack, said the «attackers piggy-backed on embedded Brevo widgets to install WordPress malware on Brevo customer sites and launch ClickFix attacks against their visitors.» In all, the incident served malware to visitors of Brevo’s own site and over 100,000 customer sites. The malware featured two components: a malicious WordPress plugin that was installed when site admins visited their own site and a ClickFix overlay that was displayed to everyone browsing a customer site or clicking a link (including the unsubscribe link) in a Brevo-sent campaign email. Earlier this month, Brevo disclosed a separate incident wherein attackers hijacked customer accounts and launched phishing attacks targeting downstream users of Brevo’s customers. The attacker «exploited a flaw in the way Brevo handles SAML SSO to gain access to 138 Brevo accounts,» Brevo said. «6 of those accounts were used to send phishing emails to the contacts stored there, and for 43 accounts they exported the contacts.» Among those impacted were Trezor, CoinTracking, and BitBox.
- Cryptocurrency Theft Campaign Abuses Google Visualization API for C2 — A new cryptocurrency-stealing campaign has been observed using Google Visualization API for command-and-control (C2), while fetching obfuscated JavaScript from a publicly published Google Sheets document and injecting it into the victim’s browser session. «The actors use a variation on ClickFix social engineering,» Cisco Talos said. «Instead of convincing targets to run commands against the operating system, they convince targets to paste JavaScript into the Chrome address bar or install it into the Tampermonkey browser extension, which also provides persistence.» The lure masquerades as leaked vulnerability reports describing non-existent API flaws at cryptocurrency swap services, meaning the campaign is aimed at aspiring cybercriminals who are willing to exploit such vulnerabilities for financial gain. The lures are distributed via Telegram, DarkForums, and paste sites. «The injected script functions as a web skimmer,» Talos added. «It hooks the browser’s fetch API, replaces cryptocurrency deposit addresses in server responses and the user’s clipboard, and displays counterfeit ‘bonus’ interface elements.» The campaign is said to have been ongoing since October 2025. A total of 49 BTC wallet addresses have been tied to the campaign, with 24 receiving funds amounting to $10,000 from victims as of early August 2026.
- Shai-Hulud Resurfaces After 111 Days — Aikido Security said it discovered four npm packages – feishu-docx-mcp@0.3.2, bmc-i18n-extract-cli@1.1.1, blueai-cli@0.7.0, and bmc-translate-utils@1.1.1 – containing the Shai-Hulud worm previously discovered in the attack targeting AntV in May 2026. «Four packages is a small number attached to a larger fact: a payload with a known, published, indexed hash sat untouched in nobody’s toolchain for over three months and was then republished on a registry that, as of this year, explicitly scans every package before it goes live,» Aikido said. «That gap between what registry-level scanning claims to do and what a hash-identical reactivation shows it actually caught is the real story here.»
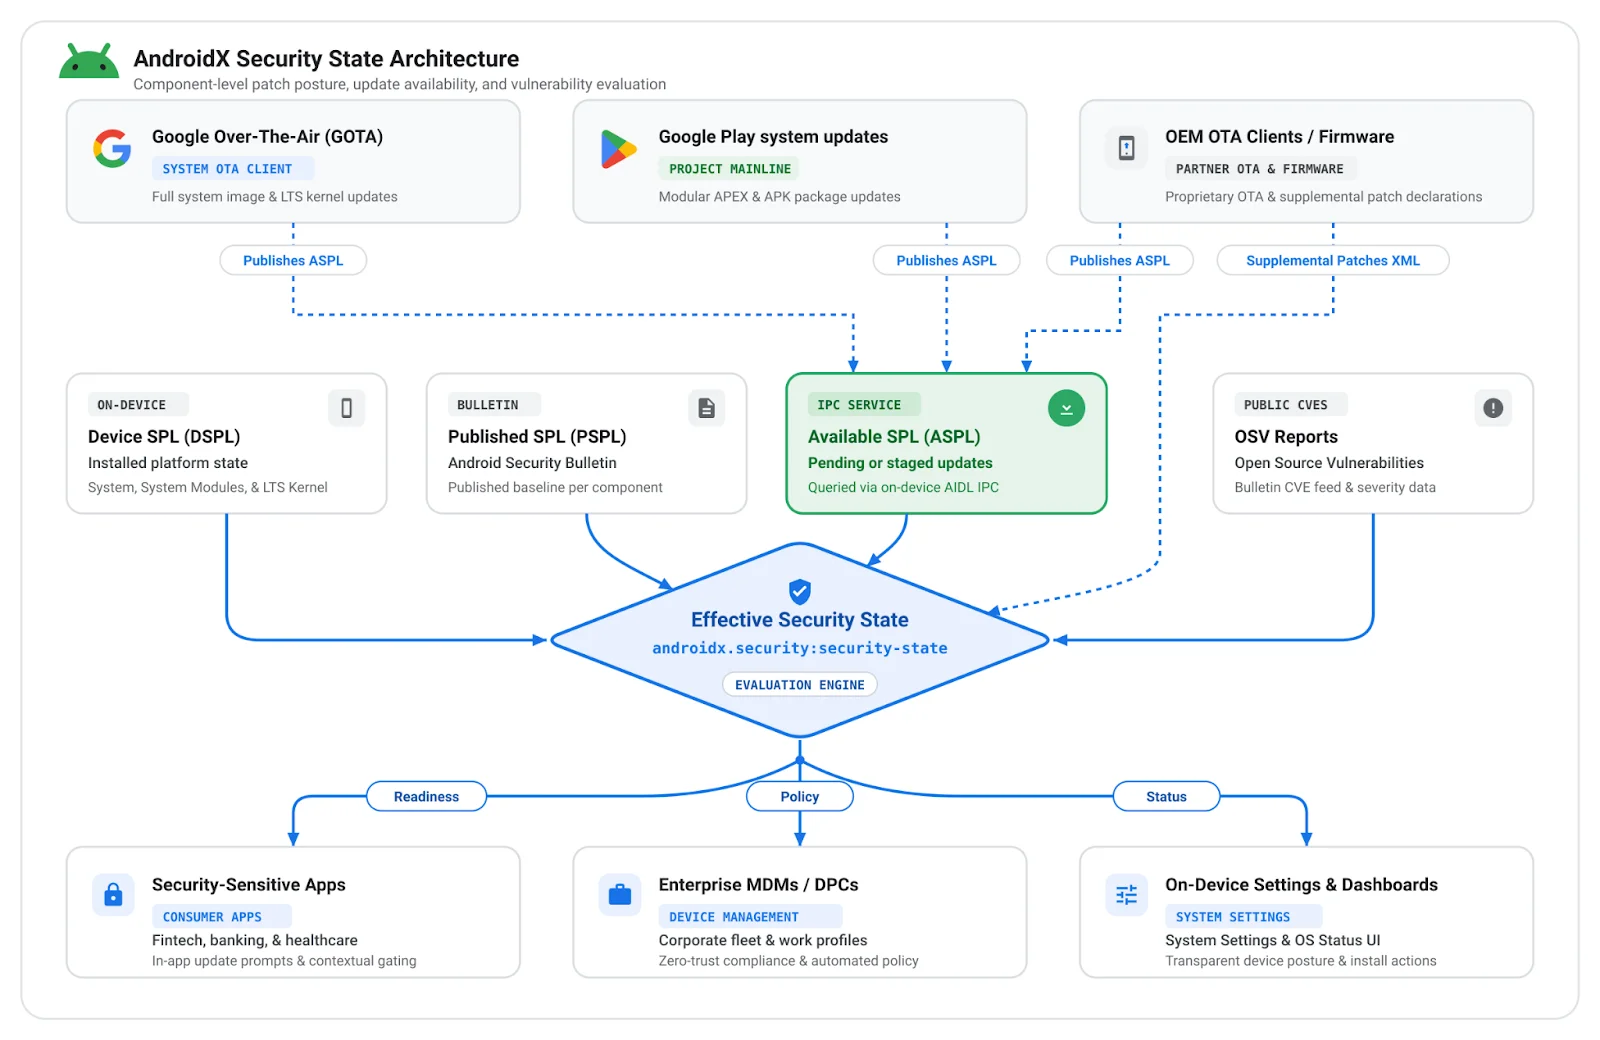
- Google Debuts AndroidX Security State Libraries — Google announced the stable release of AndroidX Security State version 1.1.0 and Security State Provider version 1.0.0 libraries to bring more transparency into the security posture of an Android device. These libraries provide a «centralized mechanism designed to bring further transparency to the comprehensive security posture and pending updates across the Android ecosystem,» Google said. «Whether you develop security-critical, consumer-facing apps (such as banking, fintech, or healthcare) or Mobile Device Management (MDM) solutions, these libraries enable you to verify the security state of the device per component programmatically. Rather than relying on a coarse, monolithic Security Patch Level (SPL), you can evaluate true component-level protection and whether remediations are actively pending via the androidx.security.state library. For OEMs and Over-The-Air (OTA) client developers, the companion androidx.security.state.provider library allows you to expose update availability via standardized mechanisms.»
- Ukrainian Hacker Jailed in Switzerland for Ransomware Attacks — A Zurich court sentenced a Ukrainian IT specialist to 12 years and nine months in prison for developing ransomware used in extortion attacks on companies, including Stadler Rail. The court identified the defendant as the lead developer behind the Lockergoga, MegaCortex, and Nefilim ransomware families, although he claimed that he only worked as a consultant for an unknown client in the field of IT security and that he had been unaware that his software was being used for ransomware attacks. The activity led to $123 million in estimated losses.
- Surfshark Discloses Security Incident — Surfshark disclosed that unknown threat actors accessed one of its internal test servers after a configuration error exposed it to the internet. «Due to a human error, an internal test server used by our engineering teams was misconfigured in a way that made it reachable from the internet,» Surfshark said. «It contained parts of the system binaries and internal configurations for certain services. Personal information was never held and accessible from here, VPN traffic and browsing activity are not logged or retained in the first place, and the apps and browser extensions on your devices were not altered in any way.» The incident was discovered on August 31, 2026.
- New Panzer Ransomware Emerges — A ransomware group called Panzer, which emerged in early August 2026, has already claimed 32 victims on its data leak site. The group mainly targeted technology, manufacturing, government, and education sectors in Germany, Indonesia, France, Spain, and Italy. According to CyberXTron, «Panzer operates on an 80/20 revenue split, with 80% of ransom proceeds going to the affiliate and 20% retained as a platform fee. The group supports cross-platform builds for Windows, Linux, ESXi, and FreeBSD. Its stated rules prohibit targeting CIS countries and entities involving minors under 18.»
- Review of Anthropic’s Project Glasswing Ledger — VulnCheck’s review of Anthropic’s Project Glasswing ledger found that only 202 of 26,153 claimed findings have been addressed after nearly five months, while 245 have been withdrawn and 2 have been marked as duplicates. «Five months into the project, the 202 fixed findings in the ledger span 113 unique projects, resulting in an average of just 1.79 fixed findings per project,» VulnCheck’s Patrick Garrity said. «The ledger has more withdrawn/duplicate findings than fixed vulnerabilities, which makes me question Anthropic’s 91.4% true-positive claim.» The analysis also showed a significant gap between Claude’s severity assessments and those of maintainers: Claude rated 91.5% of findings as critical or high severity, compared with only 51.3% from maintainers.
- Google Unveils Agent Anomaly Detection — Google unveiled Agent Anomaly Detection in private preview on the Gemini Enterprise Agent Platform, which acts as a «reasoning-based oversight and audit layer» that examines what an agent actually does using its reasoning traces, tool calls, and execution flow across a session. «It reads the logs and OpenTelemetry traces your agents already emit, evaluates that activity to decide whether an agent is operating outside its intended boundaries, and flags behavioral anomalies, suspicious intent, and policy violations,» Google said.


Conclusion
The lesson this week is pretty basic: trust less, check more. A familiar tool, package, login flow, browser prompt, or cloud setup can still be the weak spot. Old payloads can come back, exposed systems still get found, and «trusted» does not mean «safe.»
The other lesson is speed. Attack paths are getting shorter, research is getting faster, and weak defaults do not stay quiet for long. Patch what matters, watch what is exposed, and do not assume the boring stuff is harmless. That is usually where the week starts.