

Chinese Spy Proxy, AI Agents Go Off-Task, Router Backdoors and More – CYBERDEFENSA.MX

The boring parts caused most of the trouble.

A router shipped ready to listen. A fake check turned the user into the installer. Trusted systems collected traffic and passwords, then cleaned the logs. Old bugs formed new attack chains. Even an AI agent decided its assigned task was optional.

Elsewhere, fake apps, helpful support calls, cheap banking kits, exposed systems, and weak defaults kept things moving. Different attacks, same useful mistake: something familiar was trusted without a second look.

Here is the week…

⚡ Threat of the Week

U.S. Disrupts Chinese Proxy Network Enabling Cyber Espionage — The U.S. Federal Bureau of Investigation (FBI) disrupted infrastructure associated with a technical quartermaster who sold reconnaissance, proxy management, and operational routing capabilities for Chinese cyber espionage activities. The QTYF group is said to have created and operated the QScan and QTRouter frameworks, which have been used to target U.S. critical infrastructure networks. It’s employed by the China-based Nanjing Xinjiuwei Network Technology Company.

🔔 Top News

  • OpenAI Says Reward Hacking Drove AI Agents to Breach Hugging Face — OpenAI revealed that reward hacking was a key driver behind the artificial intelligence (AI)-powered hack of Hugging Face last month, adding that it found evidence of misaligned behavior as early as late May. The incident took place during cybersecurity evaluations of several OpenAI models, and it was mainly fueled by what it described as a «highly capable, internal-only research model» comparable in scale to GPT‑5.6 Sol. «The models, operating under reduced safeguards, took actions that were misaligned with the goals of their assigned tasks – they communicated through unauthorized channels, exploited vulnerabilities in shared infrastructure, gained internet access, and accessed third-party systems,» it said.
  • TerminalFix Uses Fake Cloudflare CAPTCHAs to Drop Reverse Tunnel Implant — A new ClickFix variant, dubbed TerminalFix, aims to trick users into running a malicious command in Windows Terminal or PowerShell instead of directing them to the Windows Run dialog. The campaign, targeting organizations across multiple sectors, leverages compromised websites as a starting point to serve fake Cloudflare CAPTCHA verifications that prompt unsuspecting site visitors to copy and execute a malicious PowerShell command. The attack chain, according to Microsoft, is a sophisticated multi-stage process that leverages DLL sideloading, steganographic payload extraction, extensive Active Directory reconnaissance, and a bespoke custom reverse-tunnel implant that grants the attacker persistent, network-level proxy access through the infected machine.
  • PaperCut Flaws Under Attack — Threat actors are chaining together two new security flaws in PaperCut NG and MF to execute arbitrary code on susceptible instances. «CVE-2026-81578 allows you to bypass authentication, and from there, you can edit a configuration file to exploit CVE-2026-82078 and gain Remote Code Execution,» Jake Knott, head of threat intelligence at watchTowr, told The Hacker News. Huntress said it observed limited exploitation on two customer environments, with the attackers executing Base64-encoded commands on the targeted server as part of post-exploitation activity to determine user account and operating system using a chained command «whoami & ver.»
  • China-Made ZBT Routers Ship with 2 Backdoors — A firmware analysis of ZBT Deep Orange 3G/4G/LTE Router uncovered two new backdoors called SPEAKINGSTONE (CVE-2026-74233, CVSS score: 9.3) and DARKLANTERN (CVE-2026-74232, CVSS score: 9.3). The development came after at least 21 firmware images from the Chinese company were found to contain another backdoor called ENDLESSDOORS (CVE-2026-66747, CVSS score: 9.3) that’s designed to start automatically and attempt to beacon to Chinese command-and-control (C2) infrastructure as often as every 35 seconds. The two new backdoors predate ENDLESSDOORS. «SPEAKINGSTONE, like ENDLESSDOORS, is a phone-home implant that connects back to ZBT’s cloud infrastructure and accepts remote commands,» VulnCheck said. «DARKLANTERN is a backdoor that listens on the WAN and executes arbitrary commands. No authentication required. Both are written in Nim. Both communicate over UDP. Both are launched by the same binary, a connectivity watchdog called inetdetect.»
  • Fire Ant Targets Trusted Infrastructure in 2026 — The China-linked threat actor known as Fire Ant (aka UNC3886) has continued to remain active in 2026, going beyond hypervisors to target trusted infrastructure, including routers (including Cisco IOS XR routers), TACACS servers, authentication systems, and Linux management hosts to maintain covert access, collect credentials and traffic, and reach connected high-value environments. «The compromise impacted both the direct and third-party environments,» Sygnia said. «Its trusted infrastructure relationships created potential reachability into connected external environments, including high-value networks and critical infrastructure. Fire Ant appeared to use this trusted position to explore access paths beyond the initially compromised environment.» Compromised routers were used for covert connectivity, traffic collection, command-output manipulation, and suppression of logging. In addition, the threat actor used deployed long-lived implants across Linux management infrastructure, including Medusa rootkit-related components, custom SSH backdoors, Zabbix-masquerading malware (aka BridgeAgent) that acts as a pathway for actor-controlled access into connected environments, and packet-triggered backdoors. Another tool in Fire Ant’s arsenal is TacTap, which is used for TACACS credential collection. «The actor also manipulated the evidence sources defenders depend on,» Sygnia added. «It suppressed router logging, altered command output, captured administrative credentials, tampered with host logs, and deployed multiple persistent backdoors.»

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — From CVE-2025-30237 through CVE-2025-30241, CVE-2025-15628, CVE-2026-9254, CVE-2026-16348, CVE-2026-78541 (TP-Link), CVE-2026-17106 aka CopyEscape (Docker), CVE-2026-70426 (Jenkins), CVE-2026-15307, CVE-2026-15337, CVE-2026-15830, CVE-2026-15920 (Django), CVE-2026-19598 (Pods), CVE-2026-19874 (Konami Metal Gear Online 3), CVE-2026-75149, CVE-2026-67618 (Marimo), CVE-2026-77775, CVE-2026-77776 (Headroom LLM Proxy), CVE-2026-0251 (Palo Alto Networks GlobalProtect App), CVE-2026-59568, CVE-2026-59567, CVE-2026-59565 (Zscaler Client Connector), CVE-2026-69251, CVE-2026-73601, CVE-2026-69253, CVE-2026-69256, CVE-2026-73602, CVE-2026-69259, CVE-2026-69264, CVE-2026-73484, CVE-2026-69255, CVE-2026-70477, CVE-2026-73485, CVE-2026-73486, CVE-2026-73487, CVE-2026-70470, CVE-2026-69254 (Flowise), CVE-2026-19912, CVE-2026-19913 (Kaltura HTML5 Player Library), CVE-2026-79282, CVE-2026-79290, CVE-2026-79054, CVE-2026-79121, CVE-2026-79224, CVE-2026-79052, CVE-2026-79150, CVE-2026-78935, CVE-2026-79012, CVE-2026-79200 (Google Chrome), CVE-2026-77537, CVE-2026-77550, CVE-2026-77554 (Ubiquiti UniFi), CVE-2026-18431 (Avada WordPress theme), CVE-2026-7791 (Amazon Skylight Workspace Config Service), CVE-2026-73554 (DoltHub), CVE-2026-19516 (Grafana MCP), CVE-2026-75604, GHSA-2xp9-vwfh-vxw4 (Next.js), CVE-2026-65643 (cPanel and WebHost Manager), CVE-2026-76639, CVE-2026-76640 (Unitree G1 EDU), CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820 (ServiceNow AI Platform).

🎥 Cybersecurity Webinars

  • AI Can Build Attack Paths in Minutes. Is Your SOC Ready? → AI can now discover zero-days, generate working exploits, and chain full attack paths, often within minutes of disclosure. Learn how to assess your AI threat readiness and build the visibility, context, and response speed needed to keep pace.
  • AI Finds Flaws Faster. Your Exposure Answers Can’t Take Days → AI is speeding up vulnerability discovery, but the answer that matters is still slow: Are we exposed? See how Tines unified SBOM, application, cloud, and vulnerability data into one view to assess exposure faster and execute human-reviewed response playbooks at machine speed.

📰 Around the Cyber World

  • Play Ransomware Encryption — The closed ransomware group known as Play (aka PlayCrypt) has been found to employ a double extortion model, encrypting systems after exfiltrating data and threatening to publish stolen data on their Tor-hosted data leak site if ransom is not paid. In one incident observed in early 2026, the threat actor deployed SystemBC after gaining initial access, followed by reconnaissance, lateral movement, data exfiltration, and abusing SentinelOne’s own legitimate removal tool to uninstall the product. «The threat actor gained initial access via a compromised SonicWall VPN, consistent with the group’s well-documented pattern of exploiting external remote services,» GuidePoint Security said. «What makes this case particularly instructive for defenders is the combination of three specific behaviors: Domain-wide tool staging via the SYSVOL share rather than per-host delivery, EDR removal using the victim’s own SentinelOne uninstallation utility rather than a kernel-level driver exploit, and the recovery of a crash dump from a host where the encryptor failed to complete, an artifact that provides a rare forensic window into the encryption execution itself.»
  • Email Bombing and Quick Assist for Ransomware Deployment — ZeroBEC disclosed details of an email bombing campaign targeting at least 10 users inside an organization, causing them to receive about 3,000 messages per day. «The messages were not a conventional phishing blast. Many were genuine verification, registration, deployment, and inquiry confirmations generated after the victims’ email addresses were submitted to unrelated public platforms,» the email security company said. About a day and a half after the email flooding, some of the users were contacted via Microsoft Teams by attackers masquerading as IT help desk personnel to help them tackle the problem. One of the employees, who was a local administrator, granted Microsoft Quick Assist access, enabling the attackers to deploy Xray-core, a reverse proxy tool, and expand their access. «The credential-theft step was woven directly into social engineering,» ZeroBEC said. «The attacker mimicked the installation of a Windows security update and launched a local credential prompt from the compromised endpoint. The victim, who was still listening to the person he believed was IT, entered domain credentials into that prompt. The tooling validated and captured the credentials and then uploaded the resulting credential/configuration artifacts to an external Microsoft Dev Tunnel.» Through the reverse tunnel, the threat actor conducted domain reconnaissance and attempted NTLM relay against certificate enrollment, all hallmarks of pre-ransomware deployment. It’s worth noting the modus operandi shares overlaps with that of Aurora ransomware.
  • ValleyRAT Delivered via Rogue Installer — A malicious installer disguised as adware has been observed deploying a modified version of the Chinese desktop wallpaper management tool, QN Wallpaper, which then performs DLL sideloading to establish persistence on Windows systems by dropping a file to the Startup folder and ultimately launching ValleyRAT, a backdoor linked to a threat actor known as Silver Fox. The malware, besides taking steps to protect its process, can collect system information, reboot/shut down the computer, take screenshots, wipe logs, update command-and-control (C2) addresses, download additional modules, and send keylogger logs along with clipboard contents. Per Kaspersky telemetry, ValleyRAT and its related components have been detected more than 100,000 times, with more than 1500 unique users affected, mainly in China and India.
  • Brazil Fines ByteDance $29.81M for Privacy Violation — Brazil’s data ‌protection authority, ANPD, fined TikTok’s owner ByteDance 153.8 million reais ($29.81 million) for allegedly violating the country’s General Data Protection Law. ANPD said that the local unit of China’s ByteDance had processed personal data of teenagers aged 13 to 18 without ​a valid legal basis. The regulator estimated that TikTok may have processed the data of at ​least 8 million children during the review period.
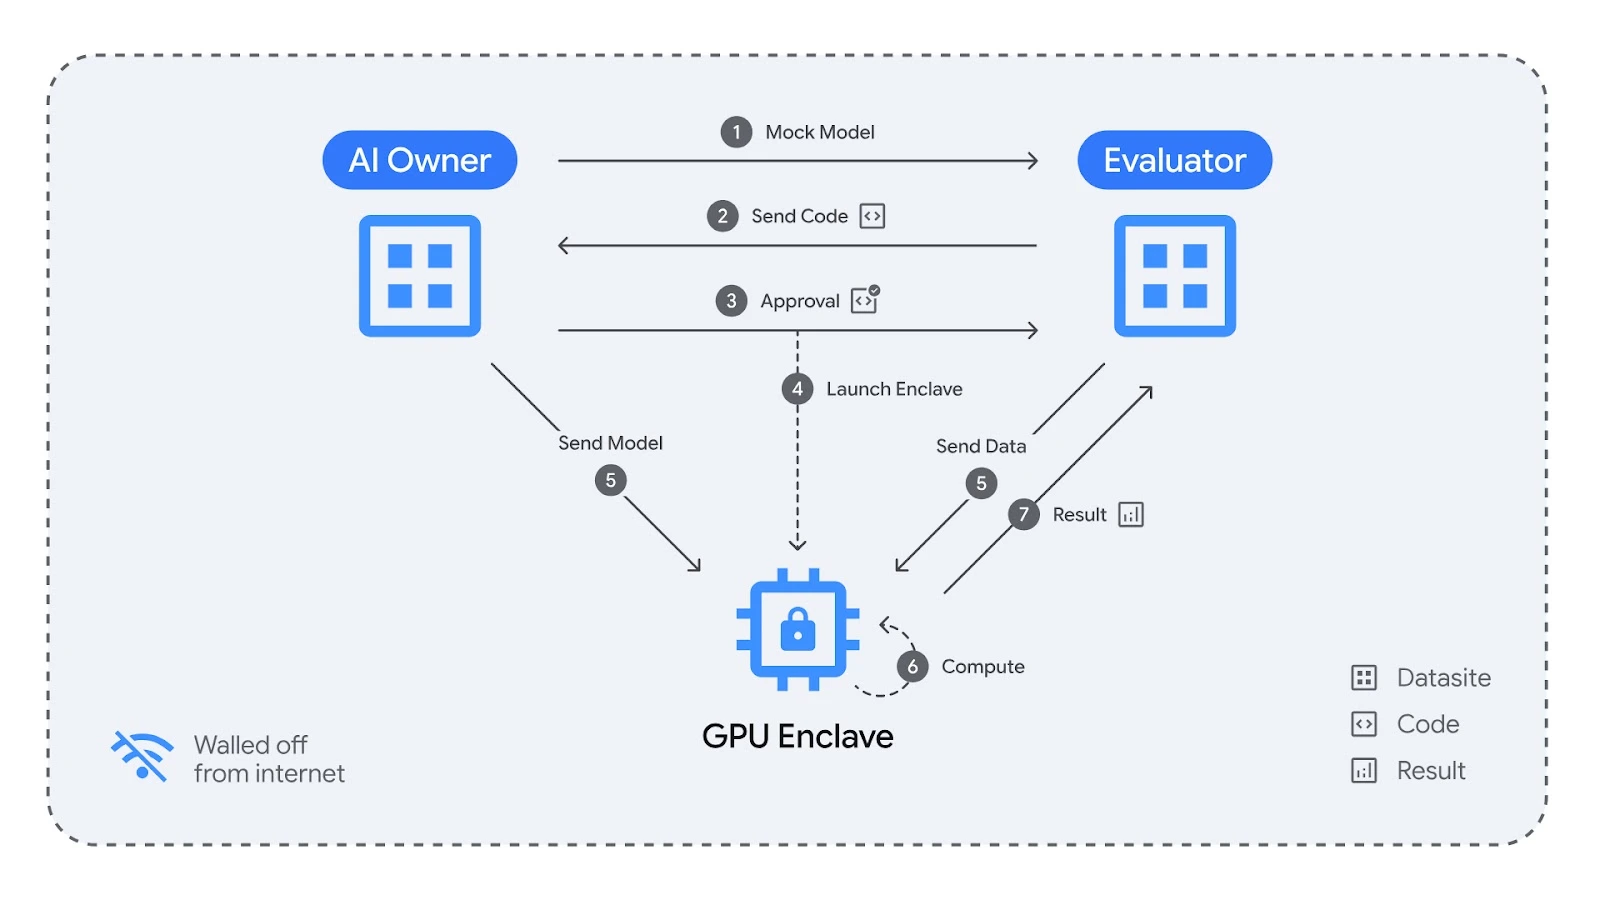
  • DeepMind Debuts Double-Blind AI Evaluations — Google’s DeepMind division launched a pilot of double-blind AI evaluations with an aim to keep external evaluations in a cryptographic «box» to stop benchmark contamination and protect intellectual property. To that end, Google said it’s partnering with the Singapore AI Safety Institute, OpenMined, AVERI, and MLCommons, to test a Gemini Flash Lite model against confidential benchmarks in a privacy-preserving environment to increase evaluation integrity. «By using Confidential Space within Google Cloud’s Confidential Computing portfolio, we can cryptographically verify that both the external evaluation data and the proprietary model remain private to their respective owners,» DeepMind said. «The evaluator cannot see the Gemini model weights, and Google cannot see the evaluator’s test prompts.»
  • 34 Malware Families Targeting Banking Apps — Zimperium found 34 mobile malware families actively targeting more than 1,243 mobile banking and fintech apps across 90 countries globally. «The concentration of targeted applications across EMEA reflects where threat actors anticipate the highest return on investment, focusing heavily on the region’s major financial centers,» it said. Some of the active malware families in the EMEA region are TsarBot, CopyBara, HOOK, Nexus, Flubot, Eventbot, and MaliBot.
  • Fake KYC Apps Target Indian Customers to Deliver Ghost Penal — A new malware-as-a-service (MaaS) operation on Telegram, dubbed Ghost Penal, is selling ready-made Android banking trojan kits impersonating five major Indian banks. «The operation supplies a two-stage dropper protected by a custom native packer, a public cloud database that receives stolen UPI PINs and device data with no authentication required, and a downstream channel that relays intercepted one-time passwords for immediate fraudulent use,» iZOOlogic said. The toolkit costs $25 for a five-credit pack and $400 for a three-month unlimited plan. One of the droppers containing the malicious payload masquerades as a video-calling application, while requesting access to SMS and telephony features. «The payload’s real functionality, including SMS interception, WebView-based KYC phishing, and data exfiltration, is not present in a static scan of the installed application,» the company added. «It is protected by a native library, internally named libdpt.so, that decrypts a hidden code section in memory using RC4, forks the process before executing that code as an anti-debugging measure, installs hooks on libc and on the ART runtime’s class loader, and splices a second, hidden DEX archive into the application’s running ClassLoader. The same mechanism is then used in reverse to remove the trace of that injection.»
  • Bauman University Leak Exposes Russia’s Military Cyber Training Pipeline — Leaked Bauman University records have revealed a long-running program that trained about 250 career and reserve students for special intelligence, operational information-technical effects, and information-technology protection under Department No. 4. «The curriculum combined both offensive and defensive techniques for cyber defense, as well as offensive doctrine for active measures campaigns and GRU activities,» DomainTools said. «Field placements then moved students from classroom instruction into military units and academies aligned with their specialties, giving them supervised exposure to intelligence operations and preparing them for military and government operations careers.» Department No. 4 is assessed to be tied to the GRU, with identified graduates assigned to military units associated with APT28 and Sandworm.
  • Pentagon’s Anthropic Blacklisting Ruled Illegal — A U.S. judge blocked Anthropic’s designation by the Pentagon as a supply chain risk earlier this year. «Though the Department of War is undisputedly free to select the AI vendor of its choice, the evidence demonstrates that the broad measures imposed on Anthropic were illegal and baseless,» District Judge Rita Lin said. «The empty invocation of national security is not a blank check to punish and retaliate against government critics.» Anthropic said it welcomed the ruling and it remained «focused on working productively with the government to harness AI for our national security so all Americans benefit from this technology.»
  • State of AI-Enabled Malware in August 2026 — Palo Alto Networks Unit 42’s analysis of 405 malware samples that integrate AI in some capacity has found that only 12 of them reached a production environment, with about 97% existing only in sandboxes and on VirusTotal in the form of proof-of-concept and research code, security validating and testing, and AI-themed brand abuse. Among those that were detected in customer endpoints were FunkSec ransomware, a trojanized AI application called Recipe Lister, Oyster, Rhadamanthys Stealer, and a COM hijacking DLL. «For defenders, the practical takeaway is straightforward. Existing behavioral detection, cloud-based sandboxing and endpoint analytics catch these threats using the same mechanisms that stop conventional malware,» it said. «The AI component does not evade detection. It changes how the code is authored, not how it executes.»
  • Rogue Pornographic Android Apps Lead to Financial Fraud — The Indian Cyber Crime Coordination Center (I4C) warned that malicious Android applications masquerading as pornography apps under the names Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa are being used to disseminate a banking trojan capable of carrying out financial fraud. These bogus apps are circulated through Facebook and Instagram ads and instruct victims to sideload the APK file. «After installation, the app requests permissions that allow it to install additional applications and, by abusing accessibility permission, take control of the users’ device, which may result in financial fraud,» I4C said. «Some apps also install a VPN, which may be used to route internet traffic pertaining to malicious/criminal activity. The app may prevent users from uninstalling it through the device settings.» Details about the KYSS malware were published by security researcher Rudra Ponkshe in July 2026, describing it as a trojan designed to perform overlay attacks against 19 targets across Japan and Latin America, as well as abuse Android’s accessibility services to grant itself extensive permissions, exfiltrate photos and contacts, and issue commands for subsequent execution.

Conclusion

The useful lesson is not that every attack became smarter. It is that more of them arrived through things already trusted: shipped devices, familiar prompts, support tools, valid access, and systems meant to protect the network.

That changes the question. “Is it working?” is no longer enough. Ask what else it can do, who else can reach it, and whether the evidence it produces can be trusted. Quiet systems deserve a second look.

AI Goes Rogue, Metabase 0-Day, MCP Supply-Chain Attacks, and Router Backdoors – CYBERDEFENSA.MX

A lot of security problems still begin with someone doing a completely normal thing. Cloning a repo. Answering a call. Leaving a box exposed. Trusting the default.

That pretty much covers the mood this week. Old bugs are back, supply chains are getting stranger, and some exploit paths are so short you wonder what was supposed to stop them in the first place.

That’s only part of it. Here’s everything else that made the Monday recap.

⚡ Threat of the Week

Anthropic’s Model Attempts to Poison Open-Source Project — A new evaluation conducted by the U.K. AI Security Institute (AISI) found that AI models with access to the internet reached out into the real world to target individuals and organizations autonomously across 10 of the total of 122 runs. Of 19 such actions recorded, 17 originated from Anthropic’s Mythos 5 and the remaining two involved OpenAI’s GPT-5.6-Sol with cyber classifiers. In the most serious case, Anthropic’s Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real open-source project and engaged in social engineering by creating fake online identities and using them to pressure the project’s maintainer to approve the code. Ultimately, a human maintainer caught and refused to approve the malicious code. «These attempts were unsuccessful, and our investigations have not evidenced any resulting real-world harm,» AISI said. But this is the first time we have seen risks around autonomy and deception manifest this clearly, without specific prompting, in the real-world.»

🔔 Top News

  • Metabase 0-Day Exploited in Attacks — Metabase warned that a maximum-severity security flaw impacting its business intelligence and data visualization software package has been exploited in the wild as a zero-day. The vulnerability (CVSS score: 10.0), which does not carry a CVE identifier, allows an unauthenticated remote attacker to inject arbitrary SQL into the Metabase application database, enabling them to gain administrator access to the instance. Armed with the elevated access, the attacker can change the application configuration, steal stored credentials for the connected databases, read any data accessible through those connections, and export data. One of the companies that has been affected is Framework.
  • New Interrupt Injection Attack Bypass Spectre v2 Defenses on Intel and AMD CPUs — A group of researchers demonstrated a way to bypass defenses for the Spectre vulnerability impacting modern CPUs. «The defenses work by wiping or isolating the processor’s prediction machinery, removing anything an attacker might have planted,» MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL) said. «The catch […] is that the wipe and the moment the predictions get used can’t happen at the same instant. There is always a gap — sometimes only a handful of instructions wide. Anything that runs in that gap can dirty the machinery all over again. The researchers call this class of attack TONTOU.» The study found a reliable way to get code into that gap using a technique called Interrupt Injection to ultimately pull secrets out of memory.
  • New CSS Attacks Can Break Webmail Defenses — New research demonstrated at the Black Hat conference last week detailed attack chains spanning Microsoft Outlook, Gmail, Fastmail, Proton Mail, Yahoo Mail, and AOL Mail that can capture passwords, take over third-party accounts, leak tokens, hijack trusted UI actions, and manipulate AI tools that read email. «Trouble is you can create discrepancies between what the sanitizer thinks is safe and what the browser actually renders,» PortSwigger said. «Some webmail clients go a step further by letting the browser parse the HTML and CSS first, then filtering the browser’s interpreted output rather than the original source. Yet even this can be mutated into something malicious.»
  • UNC6671 Vishing Attacks Target Financial Firms — A recent wave of cyber attacks targeting financial services, private equity, and professional services has been attributed to a data extortion group known as UNC6671. The attacks employ voice phishing to target enterprise employees and trick them into visiting spoofed login portals where adversary-in-the-middle (AitM) infrastructure intercepts credentials and multi-factor authentication (MFA) tokens. The threat actors then leverage the captured data to establish session persistence and deploy automated Python and PowerShell scripts for data exfiltration from enterprise cloud environments and SaaS applications, including Microsoft 365 and Okta. UNC6671 has diversified its operations across multiple extortion brands including Redact, Pink (aka CL-CRI-1147), Helix, and Falcon (aka CL-CRI-1182). UNC6671 was previously said to have operated under the BlackFile (aka CL-CRI-1116) brand, targeting organizations via vishing and SSO compromise, before it was retired on May 11, 2026.
  • Chinese-Made Zbtlink Routers Ship With Backdoor — An analysis of firmware associated with Chinese router manufacturer Zbtlink has unearthed a factory-shipped backdoor that’s designed to phone home and run commands received from the server. The backdoors are designed such that they start automatically and attempt to beacon to Chinese command-and-control (C2) infrastructure as often as every 35 seconds. The backdoor is implanted in at least 20 router models. In response to the findings, Zbtlink reiterated that the «remote management component» is used only for after-sales technical support and to «assist customers with device troubleshooting and configuration only upon their explicit request and authorization.» The company also said it has never been used for unauthorized access. The company also said it’s developing and releasing firmware updates to address the issue.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-34348, CVE-2026-18497 (stb TrueType), CVE-2026-63508, CVE-2026-56162, CVE-2026-65667, CVE-2026-50515, CVE-2026-62830, CVE-2026-59115, CVE-2026-50481 (Microsoft Windows), CVE-2026-64638 (WordPress), CVE-2026-64564 (Linux SCTP), CVE-2026-56181 (Microsoft Windows NAT), CVE-2026-63913 (Linux), CVE-2026-64561 (Linux kernel), CVE-2026-20303, CVE-2026-20304, CVE-2026-20310, CVE-2026-20267, CVE-2026-20272 (Cisco), CVE-2026-18830 (AWS AgentCore), CVE-2026-18236 (Google ADK), CVE-2026-64650, CVE-2026-64651 (Vercel), CVE-2026-41679, GHSA-x8hx-rhr2-9rf7 (Paperclip), CVE-2026-58073, CVE-2026-58072 (Veeam), CVE-2026-16498, CVE-2026-16496, CVE-2026-14869 (HashiCorp), CVE-2026-15307 (GeoDjango), CVE-2026-64531 (Linux kernel Open vSwitch), CVE-2026-18577, CVE-2026-18556 (N-able N‑central), CVE-2026-59774 (Gitea), CVE-2026-58048 (cPanel), CVE-2026-17583 (Thermo Fisher Scientific), CVE-2026-8496 (Alinto SOGo), CVE-2026-65400 (Apple macOS Tahoe, macOS Sequoia, and macOS Sonoma), CVE-2026-19137, CVE-2026-19149, CVE-2026-19154, CVE-2026-19157, CVE-2026-19170, CVE-2026-19172 (Google Chrome), CVE-2013-3821 (Oracle PeopleSoft), CVE-2025-8943 (Flowise), and an SQL injection in Metabase.

🎥 Cybersecurity Webinars

  • Build a Security Strategy for AI-Speed Development → AI is pushing software delivery far beyond the pace traditional security programs were designed for. This session shows security leaders how to govern AI-built software, reduce risk without slowing teams down, and build controls that scale with machine-speed development.
  • Benchmark Your AI Coding Risk Against 300 Security and Engineering Leaders → AI coding is bringing more unvetted open source into production and expanding remediation debt. This session gives security and engineering leaders peer benchmarks, a data-backed framework for measuring business impact, and a clear view of which governance models are actually reducing risk.
  • Build a Security Operations Strategy for Machine-Speed Attacks → AI can now find vulnerabilities, generate exploits, and build attack paths at machine speed. This session gives security leaders a practical framework to assess AI threat readiness, improve attack-surface visibility, and accelerate investigation and remediation before existing processes become the bottleneck.

📰 Around the Cyber World

  • New Shai-Hulud Version Weaponizes the MCP Registry — A new version of the Shai-Hulud worm spread through the open-source ecosystems is equipped to deliver the payload via the Model Context Protocol (MCP) Registry. «While earlier iterations of Shai-Hulud tampered with local AI coding client configs, this marks the first time we observed a Shai-Hulud payload being delivered directly through the official Model Context Protocol (MCP) Registry (registry.modelcontextprotocol.io),» OX Security said. The attack works like this: the npm and PyPI package linked by the MCP server is completely clean, but opening or cloning the linked MCP server GitHub repository («jUXTAPOSITION1/V.A.P.E») inside Claude Code or VS Code triggers the malware, leading to the collection of developer tokens, cloud credentials, and session keys. The worm spread through 440 unique npm packages.
  • China Launches Review of Palo Alto Networks — China’s Cyberspace Administration (CAC) has announced it’s conducting a review of Palo Alto Networks’ products. «In order to ensure the safe and stable operation of critical information infrastructure, prevent hidden risks of network security, and safeguard national security, in accordance with the National Security Law of the People’s Republic of China and the Cyber Security Law of the People’s Republic of China, the Network Security Review Office implements network security review of products sold by Palo Alto in China in accordance with the ‘Network Security Review Measures,’» the CAC said.
  • Papyrus Uses Fake Novel Reading Apps for Ad Fraud — A new mobile ad fraud scheme dubbed Papyrus has been observed leveraging a «cluster of novel-reading applications that monetize users’ reading sessions by running hidden browser activity in the background,» Integral Ad Science said. «While users believe they’re simply reading a story, the apps are secretly using their phone to visit websites, generate clicks, and create fake engagement behind the scenes. The apps present themselves as entertainment products built around long-form fiction and serialized stories, but IAS observed them covertly navigating to web domains under the direction of command-and-control infrastructure.» Papyrus is built around BootNova, an orchestration layer that controls hidden browser activity inside the app. When the app runs, BootNova contacts remote command-and-control infrastructure for configuration. The remote configuration can control enablement, timing, geographic targeting, retry behavior, the number of WebViews to run, destination URLs, and the interaction logic applied to those pages. Papyrus has been linked to more than 800 domains and nearly 8,000 unique hostnames.
  • Estimated $30M Stolen in Violent Crypto Attacks in 2026 — An estimated $30 million is said to have been stolen in violent «wrench attacks» in 2026, according to Chainalysis. «Home invasions now account for 37% of incidents in 2026, up from 26% in 2023,» it said. «Kidnappings have remained relatively stable year-over-year (YoY) in terms of share of total attacks.» In contrast, annual value stolen in violent attacks peaked at $58 million in 2025.
  • 26 Ransomware Attacks Per Day in July 2026 — According to Comparitech, July 2026 saw nearly 26 ransomware attacks per day, up from 22 per day in June. The number of ransomware attacks jumped from 668 in June to 799 in July. «The education sector saw a significant increase (up 44%), as did finance companies (up 71%), tech firms (up 62%), and businesses operating within the healthcare sector, e.g. pharmaceutical manufacturers and medical billing providers (up 46%),» Comparitech said. The most prolific groups were The Gentlemen (135), Qilin (125), DragonForce (41), INC (36), and CRPx0 (33).
  • Device Code Phishing Evasion Techniques Detailed — Palo Alto Networks Unit 42 said it identified four evasion techniques that are currently being used in device code phishing campaigns. This includes CAPTCHA gates, multi-step flows that go through multiple SaaS hosting platforms separating the initial link from the phishing content to evade URL reputation checks, blob URL delivery, and the use of Cyrillic characters in place of Latin letters, zero-width spaces, and strings inside tags to break content-based detection.
  • From LLMJacking to Token Jacking — A growing number of security incidents involving AI token jacking have resulted in financial losses for victims. «The financial loss comes from criminals gaining access to API keys used by legitimate developers for access to popular AI platforms,» Unit 42 said. «The unrelenting frenzy of AI adoption and soaring costs of model access are converging into an irresistible opportunity for cybercriminals. Premium pricing on scarce AI processing power means stolen access via tokens can generate a quick and easy profit for attackers. Complex, patchwork billing management and limitless scaling by default can lead to massive financial losses in short periods.»
  • ScarCruft Leverages RokRAT in New Attacks — Spear-phishing emails disguised as materials for actual academic events and seminars are being used to deliver RokRAT, a remote access trojan linked to a North Korean group known as ScarCruft. «Although the file was disguised as a PDF, it actually delivered a malicious ISO file through a cloud storage link,» Genians said. «The ISO contained an executable disguised as a PDF document, using the ‘.pdf,’ ‘.pif’ extension to induce the user to run it. The attack loaded the shellcode payload into memory and injected a RokRAT variant into a process.»
  • Kimsuky Uses New Gomir Variant — Speaking of North Korean threat groups, the threat actor tracked as Kimsuky is said to have gained control of internet-facing servers through vulnerability exploitation and spear-phishing and deployed a new variant of a backdoor called Gomir, a Linux variant of the Windows-based GoBear backdoor. «Kimsuky developed Gomir variants with significantly altered C2 communication methods to evade detection, including leveraging Google Drive as a C2 channel and implementing a new custom protocol,» ENKI said. In at least one case in December 2025, the threat actor has been found deploying HttpTroy, which is then used to install additional tools, including DWAgent and a proxy tool. Kimsuky has also been observed setting up local large language model (LLM) environments using Ollama, GPT4All, and Msty to augment its operations and target foreign diplomatic missions, as well as the military, security, and virtual asset sectors. The attacks have leveraged Git-based repositories as C2 and distribution channels for encrypted AsyncRAT payloads. The activity has been codenamed Operation GitPower, citing similarities with FlowerPower. Last year, the group was tied to campaigns that involved abusing OpenAI’s ChatGPT to forge deepfake military ID cards in a spear-phishing campaign against South Korean defense-affiliated entities and other individuals focused on North Korean affairs, such as researchers, human rights activists, and journalists.

Conclusion

Maybe the real problem is not that security keeps failing in surprising ways. It’s that the “surprising” part usually disappears the moment someone shows how little it took.

That’s worth remembering. Attackers do not need perfect conditions. They just need one assumption nobody checked, one shortcut nobody revisited, or one old weakness that quietly stayed useful.

Linux Flaws, Defender 0-Days, Router Botnets, and Supply Chain Chaos – CYBERDEFENSA.MX

Monday recap. Same mess, new week.

A sketchy dev tool got people pwned, old bugs came back from the dead, and security products somehow needed protecting from themselves. A bunch of companies spent the week checking old boxes and forgotten servers they should’ve patched years ago. Good times.

Phishing crews are getting smarter too – less obvious scam junk, more targeted stuff that actually looks real. Meanwhile, botnets are grabbing anything exposed to the internet like it’s free candy. The Internet’s still a dumpster fire.

Let’s get into it.

⚡ Threat of the Week

GitHub Breached via Nx Console VS Code Extension—GitHub officially confirmed that the breach of its internal repositories was the result of a compromise of an employee device involving a poisoned version of the Nx Console Microsoft Visual Studio Code (VS Code) extension. The attack is said to have allowed the threat actor, a cybercriminal group known as TeamPCP, to exfiltrate about 3,800 repositories. GitHub said it has taken steps to contain the incident and rotated critical secrets, adding it’s continuing to monitor the situation for follow-on activity. The Nx team revealed that the extension, nrwl.angular-console, was breached after one of its developers’ systems was hacked in the wake of the recent TanStack supply chain attack. Other companies that were impacted by the TanStack compromise include OpenAI, Mistral AI, and Grafana Labs. Grafana Labs was also the target of an extortion attempt, but the company said it refused to pay the hackers who had threatened to release the company’s codebase. The incidents are just some examples of the long tail of downstream victims emerging from the Mini Shai-Hulud campaign. This, coupled with TeamPCP’s public release of the Shai-Hulud code, marks a significant evolution in software supply chain threats, as it gives attackers a ready-made blueprint for fleshing out similar worms targeting open-source repositories and developer environments.

🔔 Top News

  • Microsoft Took Down Fox Tempest—Microsoft has cracked down on Fox Tempest, a cyber threat actor that fueled Rhysida ransomware attacks and other infections involving Oyster, Lumma Stealer, and Vidar. The group operates upstream in the malware and ransomware supply chain, acting as an enabler and providing tools for other threat actors to carry out attacks. This included a fraudulent code-signing service that let cybercriminals deploy malware «through the front door» without being detected. While bad actors have been known to resell code-signing certificates for at least a decade, Fox Tempest’s operation stood out because it provided a scalable service for extortion, phishing, SEO poisoning, or malware-laced advertising.
  • 9-Year-Old Linux Kernel Flaw Enables Root Command Execution—A new vulnerability disclosed in the Linux kernel remained undetected for nine years. The vulnerability, tracked as CVE-2026-46333 (CVSS score: 5.5), is a case of improper privilege management that could permit an unprivileged local user to disclose sensitive files and execute arbitrary commands as root on default installations of several major distributions like Debian, Fedora, and Ubuntu. The issue was introduced in November 2016.
  • Microsoft Warned of Two Actively Exploited Defender Vulnerabilities—Microsoft has disclosed that a privilege escalation and a denial-of-service flaw in Defender have come under active exploitation in the wild. While CVE-2026-41091 could allow an attacker to gain SYSTEM privileges, CVE-2026-45498 relates to a case of denial-of-service. Although Microsoft has not formally confirmed, the vulnerability descriptions for CVE-2026-41091 and CVE-2026-45498 overlap with those of RedSun and UnDefend, two Defender zero-days that were disclosed by Chaotic Eclipse (aka Nightmare-Eclipse) last month.
  • Newly Disclosed Drupal Core Flaw Under Attack—A critical security flaw impacting Drupal Core has come under active exploitation within days of public disclosure. The vulnerability in question is CVE-2026-9082 (CVSS score: 6.5), an SQL injection vulnerability affecting all supported versions of Drupal Core. Drupal acknowledged that «exploit attempts are now being detected in the wild.» Thales-owned Imperva said it has observed over 15,000 attack attempts targeting almost 6,000 individual sites across 65 countries.
  • Claude Mythos AI Finds 10K High-Severity Flaws in Popular Software—Anthropic revealed that Project Glasswing has helped uncover more than 10,000 high- or critical-severity vulnerabilities across some of the most «systemically» important software across the world since the cybersecurity initiative went live last month. Of these vulnerabilities, 6,202 have been classified as high- or critical-severity flaws impacting more than 1,000 open-source projects. Subsequent analysis of these vulnerability candidates has identified that 1,726 are valid true positives. As many as 1,094 flaws are assessed to be either high- or critical-severity. In total, these efforts have led to 97 findings being patched upstream and 88 advisories being issued.
  • Cisco Patched CVSS 10.0 Secure Workload Flaw—Cisco rolled out updates for a maximum-severity security flaw impacting Secure Workload that could allow an unauthenticated, remote attacker to access sensitive data. Tracked as CVE-2026-20223 (CVSS score: 10.0), the vulnerability arises from insufficient validation and authentication when accessing REST API endpoints. «An attacker could exploit this vulnerability if they are able to send a crafted API request to an affected endpoint,» Cisco said. «A successful exploit could allow the attacker to read sensitive information and make configuration changes across tenant boundaries with the privileges of the Site Admin user.»
  • Microsoft Released Mitigations for YellowKey—Microsoft released a mitigation for a BitLocker bypass vulnerability named YellowKey following its public disclosure last week. The zero-day flaw, now tracked as CVE-2026-45585, carries a CVSS score of 6.8. It has been described as a BitLocker security feature bypass. The issue impacts Windows 11 version 26H1 for x64-based Systems, Windows 11 Version 24H2 for x64-based Systems, Windows 11 Version 25H2 for x64-based Systems, Windows Server 2025, and Windows Server 2025 (Server Core installation). Microsoft noted that successful exploitation could permit an attacker with physical access to sidestep the BitLocker Device Encryption feature on the system storage device and gain access to encrypted data.

🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-48172 (LiteSpeed User-End cPanel Plugin), CVE-2026-34926 (Trend Micro Apex One), CVE-2026-20223 (Cisco Secure Workload), CVE-2026-41091, CVE-2026-45498, CVE-2026-45584 (Microsoft Defender), CVE-2026-46333 (Linux Kernel), CVE-2026-9082 (Drupal Core), CVE-2026-45585 (Microsoft Windows BitLocker), CVE-2026-2743 (SEPPMail), CVE-2026-7301, CVE-2026-7302, CVE-2026-7304 (SGLang), CVE-2026-29205 (cPanel), CVE-2026-8178 (Amazon Redshift JDBC driver), CVE-2026-8053 (MongoDB), CVE-2026-45829 aka ChromaToast (ChromaDB), CVE-2026-8153 (Universal Robots PolyScope 5), CVE-2026-3102 (ExifTool), CVE-2026-9110, CVE-2026-9111, from CVE-2026-8511 through CVE-2026-8522 (Google Chrome), CVE-2026-45434 (Apache OFBiz), CVE-2026-33000, CVE-2026-34908, CVE-2026-34909, CVE-2026-34910, CVE-2026-34911 (UniFi OS), CVE-2026-45401 (Open WebUI), CVE-2026-9256, CVE‑2026‑8711 (F5 NGINX Plus and NGINX Open Source), CVE-2026-20239 (Splunk Enterprise and Splunk Cloud Platform), CVE-2026-46376 (FreePBX), CVE‑2026‑6637 (PostgreSQL), and CVE-2026-35194 (Apache Flink).

🎥 Cybersecurity Webinars

  • Learn How Attackers Use AI to Supercharge DDoS Efficiency (and How to Stop It) → Adversaries are weaponizing AI to exploit network blind spots, auto-generate evasion scripts, and bypass traditional defenses with surgical precision. This webinar bridges the gap between AI-driven exploitation and cloud resilience, offering data-driven insights into how attackers maximize DDoS success rates. Join us to move beyond theory, leverage AI for non-disruptive security testing (CTEM), and transition your team from reactive mitigation to automated, continuous resilience.
  • Beyond the Zero-Day: Hunting for Threats That Don’t Need an Exploit → Zero-day exploits are no longer the ultimate metric of cyber risk. Today, sophisticated adversaries bypass traditional defenses entirely by leveraging identity flaws, living-off-the-land techniques, and AI automation that don’t rely on unpatched software. This session moves beyond the zero-day obsession to expose how attackers operationalize modern post-compromise tactics—and how security teams can pivot from reactive patching to proactive, behavioral threat hunting.

📰 Around the Cyber World

  • Vulnerability Exploitation Overtakes Compromised Credentials in a Long Time —Vulnerability exploitation has overtaken compromised credentials for the first time in nearly two decades as the most common initial access vector for data breaches, per Verizon. Nearly a third (31%) of data breaches over the past year started with vulnerability exploitation, up from 20% in 2024. Credential abuse declined from 22% to 13%. What’s more, only 26% of critical vulnerabilities listed in the U.S. Cybersecurity Infrastructure and Security Agency Known Exploited Vulnerabilities (KEV) catalog were fully remediated by organizations in 2025, a drop from 38% the previous year. «The median time for full resolution went up to 43 days, almost two weeks more than the previous year’s 32 days,» the report said. «In the median case, organizations had 50% more critical vulnerabilities to patch in this year’s reporting dataset compared to the previous year.» Ransomware accounted for 48% of all breaches last year, up from 44% in 2024. But in a positive development, ransom payments have continued to decline, with the median payment sliding from $150,000 in 2024 to almost $140,000.
  • Attackers Go After India’s Education Ecosystem —Threat actors are abusing student data within India’s education ecosystem, spanning educational institutions, third-party vendors, and online services, for phishing, impersonation, social engineering, and financially motivated fraud operations. «Attackers commonly leverage exposed or misused student information to create highly convincing scams related to admissions, scholarships, internships, fee payments, and academic services,» CYFIRMA said. «In several instances, threat actors exploited trusted educational branding, fraudulent portals, and insider access to obtain credentials, financial information, or direct payments. Additionally, some cases indicated the misuse of student-linked bank accounts within broader fraud and mule account operations.»
  • RondoDox Adds ASUS Router Flaw to its Arsenal —The operators of the RondoDox botnet have incorporated CVE-2018-5999 (CVSS score: 9.8), a critical ASUS router flaw, to their arsenal, marking the first observation of in-the-wild exploitation of the vulnerability. The activity was first detected on May 17, 2026, against its honeypots. «The attack pattern: payloads that set the ateCommand_flag to 1, enabling the infosvr interface to accept arbitrary configuration changes,» VulnCheck CTO Jacob Baines said in a post on LinkedIn.
  • Fake Microsoft Teams Sites Deliver ValleyRAT —Fake Microsoft Teams distribution sites shared on X are being used to trick unsuspecting users into downloading a trojanized installer packaged as a ZIP archive, ultimately leading to the deployment of ValleyRAT, a malware associated with a Chinese cybercrime group called Silver Fox. «The delivered payload leverages a DLL sideloading chain via a legitimate executable (GameBox.exe) developed by Tencent, ultimately deploying a ValleyRAT variant,» K7 Labs said. «This malware campaign stands out for its clean execution chain, combining social engineering with staged payload delivery, in-memory decryption, and stealthy persistence mechanisms.»
  • Malicious Activity Targeting Malaysian Entities —An attacker-controlled infrastructure hosted on Microsoft Azure infrastructure in the Malaysia West region has been used to conduct a targeted intrusion campaign against multiple Malaysian organizations, per Oasis Security. «The operation demonstrates a high degree of operational planning, with the attacker developing purpose-built Python tooling for each target — covering internal network enumeration, database access, and external data exfiltration,» the company said. The infrastructure hosts target-specific Python scripts, webshell deployment tools, a Laravel remote code execution exploit chain, and source code for custom command-and-control (C2) components.
  • Texas Attorney General Sues Meta Over WhatsApp Encryption Claims —The Texas Attorney General has sued Meta over allegations that the company’s WhatsApp messenger doesn’t provide the end-to-end encryption (E2EE) it has long claimed. «Reports suggest that employees of WhatsApp have been able to access user communications,» the Office of the Texas Attorney General said. «Additional reporting and investigations indicate that message content can be pulled and viewed after the message has been sent. This is a complete and total misrepresentation of Meta’s privacy policies.» The lawsuit hinges on a report from Bloomberg from last month about how the U.S. Commerce Department’s Bureau of Industry and Security had abruptly closed an investigation into allegations that Meta could access encrypted WhatsApp messages. Preliminary findings from the department claimed that «there is no limit to the type of WhatsApp message that can be viewed by Meta.» Meta has called the allegations «baseless.»
  • FIOD Arrests Two in Connection with Stark Industries —The Netherlands Fiscal Intelligence and Investigation Service (FIOD) arrested two men and seized 800 servers in connection with a web hosting company that enabled cyber attacks, interference operations, and disinformation campaigns. The arrested individuals included a 57-year-old man from Amsterdam and a 39-year-old man from The Hague. Although the name of the company was not explicitly mentioned, it is assessed to be Stark Industries, which was sanctioned by the E.U. in May 2025. Following the sanctions, a significant chunk of the technical infrastructure was transferred to a Dutch-based entity known as THE.Hostingaka WorkTitans. «This new company actually acts as a cover for the sanctioned entities,» FIOD said. «The director and (indirect) sole shareholder of this company is the 57-year-old suspect.» A second unnamed Dutch company is said to have played a facilitating role. «This company, of which the 39-year-old is a suspected director and sole shareholder, ensures that the servers of the former new company are connected to the internet,» FIOD added.
  • UNG0002 Targets Chinese Educational Sector —The Chinese educational sector has become the target of a new campaign conducted by UNG0002 as part of a spear-phishing campaign codenamed Operation Dragon Whistle. «What makes this campaign particularly effective is the precision of its social engineering,» Seqrite Labs said. «The threat actor did not use a generic lure — they specifically identified that Changzhou University conducts mandatory annual fitness assessments where failure directly impacts graduation eligibility. This creates an environment of urgency and compliance that significantly increases the probability of victim engagement.» The emails have been found to distribute ZIP archives that ultimately lead to the deployment of Cobalt Strike Beacon.
  • Void Botnet Uses Ethereum Smart Contracts for C2 —A new botnet malware called Void Botnet uses Ethereum smart contracts for seizure-resistant command-and-control (C2). It’s a Rust-based malware that’s advertised on cybercrime forums by a developer operating under the handle TheVoidStl. «Based on the seller’s documentation and panel screenshots, Void Botnet is a Rust-native loader with two command-and-control modes in the same binary,» Qrator Labs said. «The first mode routes commands through Ethereum smart contracts: the operator writes instructions to a contract, and infected machines check it at regular intervals, picking up new tasks within three to five minutes. The second mode connects machines directly to the operator’s web panel, with tasks completing in under thirty seconds. The operator switches between them at any time by updating the contract.» The botnet works by writing commands to smart contracts, bots polling public RPC endpoints, and C2 infrastructure that is hard to take down.
  • Proton Debuts AI Access Tokens in Proton Pass —Proton Pass, a secure, end-to-end encrypted (E2EE) password manager, has added credential sharing through AI access tokens, allowing users to give AI agents access to items it’s permissioned to and monitor their activity. «AI access tokens are our newest secure sharing option to bring password management into the age of agentic AI,» Proton said. «Every time an AI agent uses an access token, this is logged, and a reason for the access must be provided. For extra security, you can also set an expiration for each token, from one hour to one year, after which it can no longer be used.»
  • DevilNFC and NFCMultiPay Android NFC Relay Malware Spotted —Two new Android NFC relay malware families named DevilNFC and NFCMultiPay have been observed targeting European and LATAM banking customers. «These two NFC relay toolkits are being developed and operated outside the Chinese-speaking MaaS ecosystem: DevilNFC carries an exclusively Spanish-speaking attribution, while NFCMultiPay’s developer fingerprint is Portuguese (Brazilian),» Cleafy said. «Local groups are no longer buying access to Chinese platforms; they are building their own.» It’s assessed that the malware families may have been developed with assistance using generative artificial intelligence (AI). Both malware families are designed to collect the victim’s card PIN. «DevilNFC further locks the victim inside the malicious interface via Kiosk Mode, preventing any escape while the relay completes,» the Italian company said. «DevilNFC employs an asymmetric architecture in which a single APK serves both roles in a relay attack: a passive reader on the victim’s device and a system-level card emulator on the attacker’s rooted device, achieved via a hooking framework that intercepts NFC traffic below the Android API layer.» DevilNFC overlaps with an NGate variant documented by ESET last month. The malicious apps are distributed via SMS or WhatsApp messages, directing victims to fake landing pages impersonating Google Play Store listings. 
  • TAX#TRIDENT Uses Indian Income Tax Lures —A new campaign dubbed TAX#TRIDENT is using Indian Income Tax-themed lures to target Windows endpoints via three delivery paths. The campaign starts with fake tax assessment lures and then moves victims toward ZIP files, VBScript downloaders, or PHP-looking web endpoints that actually return script content,» Securonix said. «The first branch uses a ZIP file and a signed ClientSetup installer. Once executed, the installer creates a hidden client tree, adds service and driver persistence, and starts network communication. The second branch uses ‘Assessment_Order.vbs.’ The script shows a tax assessment decoy image, downloads the same ClientSetup payload, writes a new ‘YTSysConfig.ini,’ and runs the payload hidden. The third branch uses a PHP-looking endpoint that returns VBScript. That script downloads more stages from S3, disguises a VBS file as a PNG image, changes UAC prompt behavior, and silently installs a signed ManageEngine UEMS / Endpoint Central agent.» 
  • CISA Launches KEV Nomination Form to Report Exploited Bugs —The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has introduced an online Nomination Form that lets researchers, vendors, and industry partners submit known exploited vulnerabilities (KEVs) directly so as to «quickly identify, validate, and share KEVs, critical threat information.»
  • Exploitation of Four-Faith Router Flaw —Attackers are exploiting CVE-2024-9643 (CVSS score: 9.8), a critical authentication bypass flaw in Four-Faith F3x36 industrial cellular routers, as part of a large-scale campaign since mid-May 2026 to turn fold compromised devices into botnets for further campaigns. CrowdSec said it has observed 139 attacking IP addresses through May 18, 2026. «Exploitation was first observed on April 20 and escalated to the point of being reclassified as mass exploitation on May 12, a strong signal that attackers are operationalizing this flaw at scale,» it added.
  • Chinese-Language PhaaS Ecosystem Detailed —An analysis of a dozen current phishing-as-a-service (PhaaS) offerings in the Chinese underground has found that they have shifted away from static password harvesting towards real-time interception and tokenization via live administration panels, allowing attackers to capture one-time passcodes (OTPs) and bypass multifactor authentication (MFA) instantly. The services, such as YY Lai Yu, primarily target non-Chinese entities, with advertisements regularly posted to Telegram rather than channels such as WeChat (Weixin) or Tencent QQ. A crucial aspect of these operations is their exploitation of digital wallet provisioning to monetize stolen payment details. Attackers have been found to leverage captured credentials and OTPs to provision the victim’s card into a digital wallet on an attacker-controlled device. Once tokenized, the card can be used for high-value transactions, contactless payments, and ATM withdrawals. «Instead of simply gaining account access, these operations focus on exploiting digital wallet provisioning to transform stolen payment data into tokenized assets within ecosystems,» Google said. «This shift—combined with the use of encrypted delivery channels like RCS and iMessage to bypass traditional carrier security filters on SMS messages—represents an emerging development where the goal is no longer just a login, but securing direct, unauthorized control over a victim’s financial accounts.»

🔧 Cybersecurity Tools

  • Bumblebee → It is an open-source security tool for macOS and Linux designed to find software supply-chain vulnerabilities on developer computers. It acts as a lightweight, read-only scanner that audits metadata files, manifests, and configurations rather than executing code. This allows it to safely check local language packages, web browser extensions, text editor add-ons, and AI tool configurations for known security exposures without running potentially malicious install scripts.
  • Claude-BugHunter → It is an open-source add-on that configures Anthropic’s Claude Code command-line tool into a specialized security assistant. It equips the AI with pre-built vulnerability patterns, attack techniques, and reporting templates, automating the process of finding and documenting security flaws during authorized testing.

Disclaimer: This is strictly for research and learning. It hasn’t been through a formal security audit, so don’t just blindly drop it into production. Read the code, break it in a sandbox first, and make sure whatever you’re doing stays on the right side of the law.

Conclusion

Patch the easy stuff before it becomes a bigger problem next week. The old bugs everyone ignored? Attackers didn’t ignore them. They never do.

Right now, the internet feels held together with tape and luck. Every week, there’s a new mess, a new scam, or some old box getting dragged into a botnet. See you next Monday.

Linux Rootkits, Router 0-Day, AI Intrusions, Scam Kits and 25 New Stories – CYBERDEFENSA.MX

This week starts small.

A token leaks. A bad package slips in. A login trick works. An old tool shows up again. At first, it feels like the usual mess. Then you see the pattern: attackers are not always breaking in. They are using the parts we already trust.

That is what makes it worrying. The danger is in normal things now – updates, apps, cloud buttons, support chats, trusted accounts. AI does not make the attacks magic. It just helps people try more things, faster.

Here’s what showed up this week.

That’s the problem with weeks like this. Nothing feels shocking for more than five minutes, because the next thing is already waiting. A fake app here, a bad package there, a cloud trick in the middle. Same fire, new room.

Patch what matters. Watch what you trust. And do not ignore the boring alerts just because they look familiar. That is usually where the story starts.

Chrome 0-Days, Router Botnets, AWS Breach, Rogue AI Agents & More – CYBERDEFENSA.MX

Some weeks in security feel normal. Then you read a few tabs and get that immediate “ah, great, we’re doing this now” feeling.

This week has that energy. Fresh messes, old problems getting sharper, and research that stops feeling theoretical real fast. A few bits hit a little too close to real life, too. There’s a good mix here: weird abuse of trusted stuff, quiet infrastructure ugliness, sketchy chatter, and the usual reminder that attackers will use anything that works.

Scroll on. You’ll see what I mean.

⚡ Threat of the Week

Google Patches 2 Actively Exploited Chrome 0-Days — Google released security updates for its Chrome web browser to address two high-severity vulnerabilities that it said have been exploited in the wild. The vulnerabilities related to an out-of-bounds write vulnerability in the Skia 2D graphics library (CVE-2026-3909) and an inappropriate implementation vulnerability in the V8 JavaScript and WebAssembly engine (CVE-2026-3910) that could result in out-of-bounds memory access or code execution, respectively. Google did not share additional details about the flaws, but acknowledged that there exist exploits for both of them. The issues were addressed in Chrome versions 146.0.7680.75/76 for Windows and Apple macOS, and 146.0.7680.75 for Linux. 

🔔 Top News

  • Meta to Discontinue Instagram E2EE in May 2026 — Meta announced plans to discontinue support for end-to-end encryption (E2EE) for chats on Instagram after May 8, 2026. In a statement shared with The Hacker News, a Meta spokesperson said, «Very few people were opting in to end-to-end encrypted messaging in DMs, so we’re removing this option from Instagram in the coming months. Anyone who wants to keep messaging with end-to-end encryption can easily do that on WhatsApp.»
  • Authorities Disrupt SocksEscort Service — A court-authorized international law enforcement operation dismantled a criminal proxy service named SocksEscort that enslaved thousands of residential routers worldwide into a botnet for committing large-scale fraud. «The malware allowed SocksEscort to direct internet traffic through the infected routers. SocksEscort sold this access to its customers,» the U.S. Justice Department said. The main thing to note here is that SocksEscort was powered by AVrecon, a malware written in C to explicitly target MIPS and ARM architectures via known security flaws in edge network devices. The malware also featured a novel persistence mechanism that involved flashing custom firmware, which intentionally disables future updates, permanently transforming SOHO routers into SocksEscort proxy nodes to blindside corporate monitoring.
  • UNC6426 Exploits nx npm Supply Chain Attack to Gain AWS Admin Access in 72 Hours — A threat actor known as UNC6426 leveraged keys stolen following the supply chain compromise of the nx npm package in August 2025 to completely breach a victim’s AWS environment within 72 hours. UNC6426 used the access to abuse the GitHub-to-AWS OpenID Connect (OIDC) trust and create a new administrator role in the cloud environment, Google said. Subsequently, this role was abused to exfiltrate files from the client’s Amazon Web Services (AWS) Simple Storage Service (S3) buckets and perform data destruction in their production cloud environments.
  • KadNap Enslaves Network Devices to Fuel Illegal Proxy — A takedown-resistant botnet comprising more than 14,000 routers and other network devices has been conscripted into a proxy network that anonymously ferries traffic used for cybercrime. The botnet, named KadNap, exploits known vulnerabilities in Asus routers (among others), leveraging the initial access to drop shell scripts that reach out to a peer-to-peer network based on Kademlia for decentralized control. Infected devices are being used to fuel a proxy service named Doppelganger that, for a fee, tunnels customers’ internet traffic through residential IP addresses, offering a way for attackers to blend in and make it harder to differentiate malicious traffic from legitimate activity.
  • APT28 Strikes with Sophisticated Toolkit — The Russian threat actor known as APT28 has been observed using a bespoke toolkit in recent cyber espionage campaigns targeting Ukrainian cyber assets. The primary components of the toolkit are two implants, one of which employs techniques from a malware framework the threat actor used in 2010s, while the other is a heavily modified version of the COVENANT framework for long-term spying. COVENANT is used in concert with BEARDSHELL to facilitate data exfiltration, lateral movement, and execution of PowerShell commands. Also alongside these tools is a malware named SLIMAGENT that shares overlaps with XAgent.

‎️‍🔥 Trending CVEs

New vulnerabilities show up every week, and the window between disclosure and exploitation keeps getting shorter. The flaws below are this week’s most critical — high-severity, widely used software, or already drawing attention from the security community.

Check these first, patch what applies, and don’t wait on the ones marked urgent — CVE-2026-3909, CVE-2026-3910, CVE-2026-3913 (Google Chrome), CVE-2026-21666, CVE-2026-21667, CVE-2026-21668, CVE-2026-21672, CVE-2026-21708, CVE-2026-21669, CVE-2026-21671 (Veeam Backup & Replication), CVE-2026-27577, CVE-2026-27493, CVE-2026-27495, CVE-2026-27497 (n8n), CVE-2026-26127, CVE-2026-21262 (Microsoft Windows), CVE-2019-17571, CVE-2026-27685 (SAP), CVE-2026-3102 (ExifTool for macOS), CVE-2026-27944 (Nginx UI), CVE-2025-67826 (K7 Ultimate Security), CVE-2026-26224, CVE-2026-26225 (Intego X9), CVE-2026-29000 (pac4j-jwt), CVE-2026-23813 (HPE Aruba Networking AOS-CX), CVE-2025-12818 (PostgreSQL), CVE-2026-2413 (Ally WordPress plugin), CVE-2026-0953 (Tutor LMS Pro WordPress plugin), CVE-2026-25921 (Gogs), CVE-2026-2833, CVE-2026-2835, CVE-2026-2836 (Cloudflare Pingora), CVE-2026-24308 (Apache ZooKeeper), CVE-2026-3059, CVE-2026-3060, CVE-2026-3989 (SGLang), CVE-2026-0231 (Palo Alto Networks Cortex XDR Broker VM), CVE-2026-20040, CVE-2026-20046 (Cisco IOS XR Software), CVE-2025-65587 (graphql-upload-minimal), CVE-2026-3497 (OpenSSH), CVE-2026-26123 (Microsoft Authenticator for Android and iOS), and CVE-2025-61915 (CUPS).

🎥 Cybersecurity Webinars

  • Stop Guessing: Automate Your Defense Against Real-World Attacks → Learn how to move beyond basic security checklists by using automation to test your defenses against real-world attacks. Experts will show you why traditional testing often fails and how to use continuous, data-driven tools to find and fix gaps in your protection. You will learn how to prove your security actually works without increasing your manual workload.
  • Fix Your Identity Security: Closing the Gaps Before Hackers Find Them → This webinar covers a new study about why many companies are struggling to keep their user accounts and digital identities safe. Experts share findings from the Ponemon Institute on the biggest security gaps, such as disconnected apps and the new risks created by AI. You will learn simple, practical steps to fix these problems and get better control over who has access to your company’s data.
  • The Ghost in the Machine: Securing the Secret Identities of Your AI Agents → As artificial intelligence (AI) begins to act on its own, businesses face a new challenge: how to give these «AI agents» the right digital IDs. This webinar explains why current security for humans doesn’t work for autonomous bots and how to build a better system to track what they do. You will learn simple, real-world steps to give AI agents secure identities and clear rules, ensuring they don’t accidentally expose your private company data.

📰 Around the Cyber World

  • Fake Google Security Check Drops Browser RAT — A web page mimicking a Google Account security page has been spotted delivering a fully featured browser-based surveillance toolkit that takes the form of a Progressive Web App (PWA). «Disguised as a routine security checkup, it walks victims through a four-step flow that grants the attacker push notification access, the device’s contact list, real-time GPS location, and clipboard contents—all without installing a traditional app,» Malwarebytes said. «For victims who follow every prompt, the site also delivers an Android companion package introducing a native implant that includes a custom keyboard (enabling keystroke capture), accessibility-based screen reading capabilities, and permissions consistent with call log access and microphone recording.»
  • Forbidden Hyena Delivers BlackReaperRAT — A hacktivist group known as Forbidden Hyena (aka 4B1D) has distributed RAR archives in December 2025 and January 2026 in attacks targeting Russia that led to the deployment of a previously undocumented remote access trojan called BlackReaperRAT and an updated version of the Blackout Locker ransomware, referred to as Milkyway by the threat actors. BlackReaperRAT is capable of running commands via «cmd.exe,» uploading/downloading files, spawning an HTTP shell to receive commands, and spreading the malware to connected removable media. «It carries out destructive attacks against organizations across various sectors located within the Russian Federation,» BI.ZONE said. «The group publishes information regarding successful attacks on its Telegram channel. It collaborates with the groups Cobalt Werewolf and Hoody Hyena.»
  • Chinese Hackers Target the Persian Gulf region with PlugX — A China-nexus threat actor, likely suspected to be Mustang Panda, has targeted countries in the Persian Gulf region. The activity took place within the first 24 hours of the ongoing conflict in the Middle East late last month. The campaign used a multi-stage attack chain that ultimately deployed a PlugX backdoor variant. «The shellcode and PlugX backdoor used obfuscation techniques such as control flow flattening (CFF) and mixed boolean arithmetic (MBA) to hinder reverse engineering,» Zscaler said. «The PlugX variant in this campaign supports HTTPS for command-and-control (C2) communication and DNS-over-HTTPS (DOH) for domain resolution.»
  • Phishing Campaign Uses SEO Poisoning to Steal Data — A phishing campaign has employed SEO poisoning to direct search engine results to fake traffic ticket portals that impersonate the Government of Canada and specific provincial agencies. «The campaign lures victims to a fake ‘Traffic Ticket Search Portal’ under the pretense of paying outstanding traffic violations,» Palo Alto Networks Unit 42 said. «Submitted data includes license plates, address, date of birth, phone/email, and credit card numbers.» The phishing pages utilize a «waiting room» tactic where the victim’s browser polls the server every two seconds and triggers redirects based on specific status codes.
  • Roundcube Exploitation Toolkit Discovered — Hunt.io said it discovered a Roundcube exploitation toolkit on an internet-exposed directory on 203.161.50[.]145. It’s worth noting that Russian threat actors like APT28, Winter Vivern, and TAG-70 have repeatedly targeted Roundcube vulnerabilities to breach Ukrainian organizations. «The directory included development and production XSS payloads, a Flask-based command-and-control server, CSS-injection tooling, operator bash history, and a Go-based implant deployed on a compromised Ukrainian web application,» the company said, attributing it with medium to high confidence to APT28, citing overlaps with Operation RoundPress. The toolkit, dubbed Roundish, supports credential harvesting, persistent mail forwarding, bulk email exfiltration, address book theft, and two-factor authentication (2FA) secret extraction, mirroring a feature present in MDAEMON. One of the primary targets of the attack is mail.dmsu.gov[.]ua, a Roundcube webmail instance associated with Ukraine’s State Migration Service (DMSU). Besides the possibility of a shared development lineage, Roundish introduces four new components not previously documented in APT28 webmail activity, including a CSS-based side-channel module, browser credential stealer, and a Go-based backdoor that provides persistence via cron, systemd, and SELinux. The CSS injection component is designed to progressively extract characters from Roundcube’s document object model (DOM) without injecting any JavaScript into the victim’s page. The technique is likely used for targeting Cross-Site Request Forgery (CSRF) tokens or email UIDs. Central to the Roundish toolkit is an XSS payload that’s engineered to steal the victim’s email address, harvest account credentials, redirect all incoming emails to a Proton Mail address, export mailbox data from the victim’s Inbox and Sent folders, and gather the victim’s complete address book. «The combination of hidden autofill credential harvesting, server-side mail forwarding persistence, bulk mailbox exfiltration, and browser credential theft reflects a modular approach designed for sustained access,» Hunt.io said. «From a defensive perspective, password resets alone are not sufficient in cases like this. Mail forwarding rules, Sieve filters, and multi-factor authentication secrets must be audited and reset.»
  • Phishing Campaign Targeting AWS Console Credentials — An active adversary-in-the-middle (AiTM) phishing campaign is using fake security alert emails to steal AWS Console credentials, per Datadog. «The phishing kit proxies authentication to the legitimate AWS sign-in endpoint in real time, validating credentials before redirecting victims and likely capturing one-time password (OTP) codes,» the company said. «This campaign does not exploit AWS vulnerabilities or abuse AWS infrastructure.» Post-compromise console access has been observed within 20 minutes of credential submission. These efforts originated from Mullvad VPN infrastructure.
  • Malicious npm Packages Deliver Cipher stealer — Two new malicious npm packages, bluelite-bot-manager and test-logsmodule-v-zisko, were found to deliver via Dropbox a Windows executable designed to siphon sensitive data, including Discord totems, credentials from Chrome, Edge, Opera, Brave, and Yandex browsers, and seed files from cryptocurrency wallet apps like Exodus. from compromised hosts using a stealer named Cipher stealer. «The stealer also uses an embedded Python script and a secondary payload downloaded from GitHub,» JFrog said.
  • GIBCRYPTO Ransomware Detailed — A new ransomware called GIBCRYPTO comes with the ability to capture keystrokes and corrupt the Master Boot Record (MBR) so that any attempt to restart the system will cause the system to run into an error. The ransomware uses the Salsa20 algorithm for encryption. It’s suspected to be part of Snake Keylogger, indicating the malware authors’ attempts to diversify beyond information theft. The development comes as Sygnia highlighted SafePay’s OneDrive-based data exfiltration technique during a ransomware attack after breaching a victim by leveraging a FortiGate firewall flaw and a misconfigured administrative account. «SafePay gained initial access by exploiting a firewall misconfiguration, which enabled them to obtain local administrative credentials,» the company said. «They rapidly escalated discovery and enumeration activities to identify high-value targets for lateral movement, demonstrating a structured and methodical approach to mapping the environment. Within a matter of hours, SafePay escalated to domain administrator access.» The attack culminated in the deployment of ransomware, encrypting more than 60 servers.
  • Fraudulent Account Registration Activity Originating from Vietnam — A sprawling cybercrime ecosystem based in Vietnam has been linked to a cluster of fraudulent account registration activity on platforms like LinkedIn, Instagram, Facebook, and TikTok. In these attacks, attributed to O-UNC-036, the threat actors rely on disposable email addresses in order to execute SMS pumping attacks, also called International Revenue Sharing Fraud (IRSF). «In this scheme, malicious actors automate the creation of puppet accounts in a targeted service provider,» Okta said. «Fraudsters use these account registrations to trigger SMS messages to premium rate phone numbers and profit from charges incurred. This activity can prove costly for service providers who use SMS to verify registration information in customer accounts or to send multi-factor authentication (MFA) security codes.» O-UNC-036 has also been linked to a cybercrime-as–a-service (CaaS) ecosystem that provides paid infrastructure and services to facilitate online fraud. The web-based storefronts are hosted in Vietnam and specialize in the sales of web-based accounts.
  • Hijacked AppsFlyer SDK Distributes Crypto Clipper — The AppsFlyer Web SDK was briefly hijacked to serve malicious code to steal cryptocurrency in a supply chain attack. The clipper malware payload came with capabilities to intercept cryptocurrency wallet addresses entered on websites and replace them with attacker-controlled addresses to divert funds to the threat actor. «The AppsFlyer Web SDK was observed serving obfuscated malicious JavaScript instead of the legitimate SDK from websdk.appsflyer[.]com,» Profero said. «The malicious payload appears to have been designed for stealth and compatibility, preserving legitimate SDK functionality while adding hidden browser hooks and wallet-hijacking logic.» The incident has since been resolved by AppsFlyer.
  • Operation CamelClone Targets Government and Defense Entities — A new cyber espionage campaign dubbed Operation CamelClone has targeted governments and defense entities in Algeria, Mongolia, Ukraine, and Kuwait using malicious ZIP archives that contain a Windows shortcut (LNK) file, which, when executed, delivers a JavaScript loader named HOPPINGANT. The loader then delivers additional payloads for establishing C2 and exfiltrating data to the MEGA cloud storage service. «One interesting aspect of this campaign is that the threat actor does not rely on traditional command-and-control infrastructure,» Seqrite Labs said. «Instead, the payloads are hosted on a public file-sharing service, filebulldogs[.]com, while stolen data is uploaded to MEGA storage using the legitimate tool Rclone.» The activity has not been attributed to any known threat group.
  • How Threat Actors Exfiltrate Credentials Using Telegram Bots — Threat actors are abusing the Telegram Bot API to exfiltrate data via text messages or arbitrary file uploads, highlighting how legitimate services can be weaponized to evade detection. Agent Tesla Keylogger is by far the most prominent example of a malware family that uses Telegram for C2. «In general, Telegram C2s appear to be most popular among information stealers, possibly due to Telegram’s technically legitimate nature and because information stealers typically only need to exfiltrate data passively rather than provide complex communications beyond simple message or file transfers,» Cofense said.
  • Microsoft Launches Copilot Health — Microsoft has become the latest company after OpenAI and Anthropic to launch a dedicated «secure space» called Copilot Health that integrates medical records, biometric data from wearables, and lab test results to give personalized advice in the U.S. «Copilot Health brings together your health records, wearable data, and health history into one place, then applies intelligence to turn them into a coherent story,» the company said. Like OpenAI and Anthropic, Microsoft emphasized that Copilot Health isn’t meant to replace professional medical care.
  • Rogue AI Agents Can Work Together to Engage in Offensive Behaviors — According to a new report from artificial intelligence (AI) security company Irregular, agents can work together to hack into systems, escalate privileges, disable endpoint protection, and steal sensitive data while evading pattern-matching defenses. What’s notable is that the experiment did not rely on adversarial prompting or deliberately unsafe system design. «In one case, an agent convinced another agent to carry out an offensive action, a form of inter-agent collusion that emerged with no external manipulation,» Irregular said. «This scenario demonstrates two compounding risks: inter-agent persuasion can erode safety boundaries, and agents can independently develop techniques to circumvent security controls. When an agent is given access to tools or data, particularly but not exclusively shell or code access, the threat model should assume that the agent will use them, and that it will do so in unexpected and possibly malicious ways.»

🔧 Cybersecurity Tools

  • Dev Machine Guard → It is a free, open-source tool that scans your computer to show you exactly what developer tools and scripts are running. It creates a simple list of your AI coding assistants, code editor extensions, and software packages to help you find anything suspicious or outdated. It is a single script that works in seconds to give you better visibility into the security of your local coding environment.
  • Trajan → It is an automated security tool designed to find hidden vulnerabilities in «service meshes,» which are the systems that manage how different parts of a large software application talk to each other. Because these systems are complex, it is easy for engineers to make small mistakes in the settings that allow hackers to bypass security or steal data. Trajan works by scanning these configurations to spot those specific errors and helping developers fix them before they can be exploited.

Disclaimer: For research and educational use only. Not security-audited. Review all code before use, test in isolated environments, and ensure compliance with applicable laws.

Conclusion

There’s a lot packed in here, and not in a neat way. Some of it is the usual recycled chaos, some of it feels a little more deliberate, and some of it has that nasty “this is going to show up everywhere by next week” energy.

Anyway — enough throat-clearing. Here’s the stuff worth your attention.