Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks – CYBERDEFENSA.MX

A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week.

The trouble keeps showing up inside things people already trust: code that takes a bad turn, old payloads coming back, exposed systems, weak checks, fake fixes, and attack paths that look almost too easy. Even the research side is getting messy, with more findings, more automation, and not always more clarity.

Nothing here needs much drama. Just a lot of small doors left open. Here’s what happened.

⚡ Threat of the Week

Cisco Warns of Actively Exploited ISE Auth Bypass — Cisco warned of a fresh maximum-severity security flaw impacting Identity Services Engine (ISE) that has come under active exploitation. The vulnerability, tracked as CVE-2026-76460 (CVSS score: 10.0), could allow an unauthenticated, remote attacker to bypass authentication. «This vulnerability is due to insufficient authentication control on an API endpoint,» Cisco said. «An attacker could exploit this vulnerability by sending a crafted request to an affected API endpoint. A successful exploit could allow the attacker to gain unauthorized access to the affected device by bypassing the web-based management interface.»

🔔 Top News

  • U.S. Seizes NightmareStresser Domains Linked to DDoS Attacks — A U.S. court-authorized operation seized two domains associated with NightmareStresser, which offered a distributed denial-of-service (DDoS)-for-hire service. NightmareStresser is assessed to have been used to launch hundreds of thousands of actual or attempted DDoS attacks against victims across the world since 2022. These attacks have targeted educational institutions, government agencies, gaming platforms, and millions of people, the U.S. Justice Department said.
  • Using Claude to Hack OpenAI — Hacktron said it used Anthropic’s Claude Opus 5 to chain two critical vulnerabilities – an SSO misconfiguration in OpenAI’s identity infrastructure and a libheif RCE in the Discourse community forum (CVE-2026-32882) – to gain unauthorized access to OpenAI employees’ ChatGPT accounts and then use them to access internal OpenAI repositories. The issue was fixed 14 hours after responsible disclosure. Upstream, the flaw was fixed in libheif 1.22.0 in May 2026.
  • Plugin4Shell for 0-Click RCE in AI Coding Agents — AIR Security demonstrated a flaw called Plugin4Shell, a zero-click remote code execution (RCE) vulnerability that bypasses SHA-pinning verification in four major AI coding agents: Claude Code, OpenAI Codex, GitHub Copilot, and Google Gemini CLI. «In this first-of-its-kind AI supply-chain attack, a trusted plugin is silently swapped for a malicious one and auto-installed past the agent’s SHA pinning — a flaw no marketplace can fix, so users must update their agent,» AIR Security said. «It is a plugin SHA-pinning bypass: the agent checks out the exact commit the marketplace pinned but never verifies it landed there, so an attacker who controls the plugin’s repo makes the checkout resolve to malicious code while the pin still looks honored. The result is zero-click remote code execution across Claude Code, Codex, GitHub Copilot, and Gemini CLI.»
  • OpenAI Reveals New Misalignment Incidents — OpenAI disclosed six new instances of «unexpected or concerning model behavior» that took place over the past six months, while sharing a new framework for reporting, tracking, investigating, and disclosing model misalignment in a bid to improve transparency. «As AI systems grow more advanced and more widely deployed, we need to build a broader and better-informed consensus on the progress of alignment research,» OpenAI said. «We do not believe that the AI industry has solved alignment and monitoring to a sufficient degree to continue responsibly scaling at maximum speed for much longer.»
  • KREMLIN Banking Malware Hijacks Chrome and Edge for Credential Theft — A previously undocumented Brazilian banking malware operation has been found to deliver a toolkit called KREMLIN. Active since at least May 2025, the threat actor has used lures that impersonate a dozen Brazilian banks and install a malicious browser extension on Google Chrome and Microsoft Edge. «The KREMLIN malware ecosystem employs multi-stage JavaScript loaders, custom C++ installers, and malicious browser extensions to steal credentials, session tokens, and sensitive data,» Elastic said. The activity is being tracked as REF9334.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-58138 (Orkes Conductor), CVE-2026-58704 (Google Pixel), CVE-2026-90894 aka ParaShells (Parallels Desktop), CVE-2026-82079 (Nintendo Switch), CVE-2026-89049 (AWS Systems Manager Agent), CVE-2026-43502 aka ZcopyReaper, CVE-2026-80844 aka DirtyAH6, CVE-2026-81000 aka TUNderflow, CVE-2026-68121 aka PPPoEject, CVE-2026-74469 aka DiagSpill (Linux kernel), CVE-2026-70416, CVE-2025-43936 (Dell ObjectScale and Elastic Cloud Storage), CVE-2026-68488 (Please Backup Manager), CVE-2026-56711, CVE-2026-73324 (VLC Media Player), CVE-2026-65638 (cPanel ConfigServer Security & Firewall), CVE-2026-85982, CVE-2026-78626, CVE-2026-78623 (Okta), CVE-2026-0310 (Palo Alto Networks PAN-OS), CVE-2026-85061 (MapLibre GL JS), GHSA-rvhw-4hpw-9vrx, GHSA-rrgq-978q-36mq, GHSA-4xhx-8cv5-wh62, GHSA-8v35-895w-232p (ArangoDB), CVE-2026-65812 (Microsoft Teams for Android), CVE-2026-80172, CVE-2026-61410, CVE-2026-80238 (Dell Secure Connect), CVE-2026-18851 (Ivanti Endpoint Manager Mobile), CVE-2026-91721, CVE-2026-91749, CVE-2026-91726, CVE-2026-93374, CVE-2026-93372 (Google Chrome), CVE-2026-92033, from CVE-2026-92005 to CVE-2026-92013, from CVE-2026-92015 to CVE-2026-92020, from CVE-2026-92022 to CVE-2026-92029, from CVE-2026-92034 to CVE-2026-92038 (Mozilla Firefox), CVE-2026-15315, CVE-2026-15316 (TP-Link Tapo cameras), CVE-2026-82232, CVE-2026-77147, CVE-2026-73178 (Apache Syncope), CVE-2026-76669, CVE-2026-76670, CVE-2026-76672, CVE-2026-76673, CVE-2026-76674 (HPE Networking EdgeConnect SD-WAN Gateways and SD-WAN Orchestrator), CVE-2026-73693, CVE-2026-73694, CVE-2026-73698, CVE-2026-73699 (FileRun), CVE-2026-39919 (Ghostscript), CVE-2026-91998 (Casdoor), CVE-2026-91932, CVE-2026-91931 (Flowise), CVE-2026-65400, CVE-2026-65414, CVE-2026-65346, CVE-2026-84607, CVE-2026-43790 (Apple), CVE-2026-90999 (Sentry Seer), CVE-2026-77692, CVE-2026-76163, CVE-2026-19667, CVE-2026-19666, CVE-2026-80274 (ISC BIND 9), CVE-2026-91843 (Check Point), CVE-2026-77179 (Docker), CVE-2026-81642, CVE-2026-82717 (Unbound DNS), Click2Shell (WordPress), CVE-2026-28326, CVE-2026-28323, CVE-2026-28309, CVE-2026-28306, CVE-2026-28308, CVE-2026-28310, CVE-2026-28314, CVE-2026-28313, CVE-2026-28307, CVE-2026-28305, CVE-2026-28317, CVE-2026-28304, CVE-2026-28312, CVE-2026-28316, CVE-2026-28311, CVE-2026-28302, CVE-2026-28321, CVE-2026-28315 (SolarWinds), CVE-2026-89026 (Issabel Framework), CVE-2026-78175 (Tutor LMS), an operating system command injection vulnerability in Dokploy, and a pickle deserialization vulnerability in MLflow.

🎥 Cybersecurity Webinars

  • How to Find and Control AI Agents Before Access Gets Out of Hand → AI agents are getting access to apps, data, credentials, and workflows faster than most teams can govern them. The real problem is not adoption — it is knowing which agents exist, what they can reach, and where access has quietly become too broad. This webinar breaks down how to bring AI agents under control without slowing down the teams using them.
  • AI Attacks Move in Minutes. Here’s How to Stop Them at Runtime → AI-powered attacks are shrinking the time defenders have to react. By the time a traditional alert is investigated, the attacker may already have moved through the environment. This webinar shows how runtime identity security can make access decisions in real time, block risky activity earlier, and give security teams a better chance against machine-speed attacks.

📰 Around the Cyber World

  • Google Doc Leads to ClickFix Attack — Huntress disclosed details of a ClickFix attack in which a security researcher was targeted in an X exchange by a threat actor posing as a crypto marketing executive. «The threat actor sent a link to a real Google Doc with a custom sidebar designed to trick the recipient into downloading malware: an AMOS infostealer on macOS, or a PowerShell loader chain on Windows,» Huntress said. «The Google Doc featured a sidebar displaying a fake decryption failure message, with supposed remediation instructions for users of different operating systems, including the option to copy and paste certain commands into the Terminal. This ClickFix lure, and the «manual update» button beside it, are what actually delivered the malware. The sidebar itself was a Google Apps Script bound to the document, so nothing had to be downloaded for it to run.» The Apps Script executed client-side in the victim’s browser, and collected the victim’s public IP address and geolocation and scanned for crypto wallets.
  • Brevo Supply Chain Attack Injects ClickFix Scripts on Customer Sites — Customer engagement platform Brevo fell victim to a supply chain attack that led to malicious code being injected into over 100,000 websites. «On 14 September 2026, an attacker used a compromised Brevo Cloudflare API key to deploy a Cloudflare Worker on our account,» Brevo said. «For about five and a half hours, the Worker injected a malicious script into pages of brevo.com and sibforms.com and into three JavaScript files that customers embed on their own websites.» The script showed selected visitors a fake Cloudflare CAPTCHA prompt that instructed visitors to paste and run a malicious command on their computer, a technique also called ClickFix. Sansec, which shared additional details of the attack, said the «attackers piggy-backed on embedded Brevo widgets to install WordPress malware on Brevo customer sites and launch ClickFix attacks against their visitors.» In all, the incident served malware to visitors of Brevo’s own site and over 100,000 customer sites. The malware featured two components: a malicious WordPress plugin that was installed when site admins visited their own site and a ClickFix overlay that was displayed to everyone browsing a customer site or clicking a link (including the unsubscribe link) in a Brevo-sent campaign email. Earlier this month, Brevo disclosed a separate incident wherein attackers hijacked customer accounts and launched phishing attacks targeting downstream users of Brevo’s customers. The attacker «exploited a flaw in the way Brevo handles SAML SSO to gain access to 138 Brevo accounts,» Brevo said. «6 of those accounts were used to send phishing emails to the contacts stored there, and for 43 accounts they exported the contacts.» Among those impacted were Trezor, CoinTracking, and BitBox.
  • Cryptocurrency Theft Campaign Abuses Google Visualization API for C2 — A new cryptocurrency-stealing campaign has been observed using Google Visualization API for command-and-control (C2), while fetching obfuscated JavaScript from a publicly published Google Sheets document and injecting it into the victim’s browser session. «The actors use a variation on ClickFix social engineering,» Cisco Talos said. «Instead of convincing targets to run commands against the operating system, they convince targets to paste JavaScript into the Chrome address bar or install it into the Tampermonkey browser extension, which also provides persistence.» The lure masquerades as leaked vulnerability reports describing non-existent API flaws at cryptocurrency swap services, meaning the campaign is aimed at aspiring cybercriminals who are willing to exploit such vulnerabilities for financial gain. The lures are distributed via Telegram, DarkForums, and paste sites. «The injected script functions as a web skimmer,» Talos added. «It hooks the browser’s fetch API, replaces cryptocurrency deposit addresses in server responses and the user’s clipboard, and displays counterfeit ‘bonus’ interface elements.» The campaign is said to have been ongoing since October 2025. A total of 49 BTC wallet addresses have been tied to the campaign, with 24 receiving funds amounting to $10,000 from victims as of early August 2026.
  • Shai-Hulud Resurfaces After 111 Days — Aikido Security said it discovered four npm packages – feishu-docx-mcp@0.3.2, bmc-i18n-extract-cli@1.1.1, blueai-cli@0.7.0, and bmc-translate-utils@1.1.1 – containing the Shai-Hulud worm previously discovered in the attack targeting AntV in May 2026. «Four packages is a small number attached to a larger fact: a payload with a known, published, indexed hash sat untouched in nobody’s toolchain for over three months and was then republished on a registry that, as of this year, explicitly scans every package before it goes live,» Aikido said. «That gap between what registry-level scanning claims to do and what a hash-identical reactivation shows it actually caught is the real story here.»
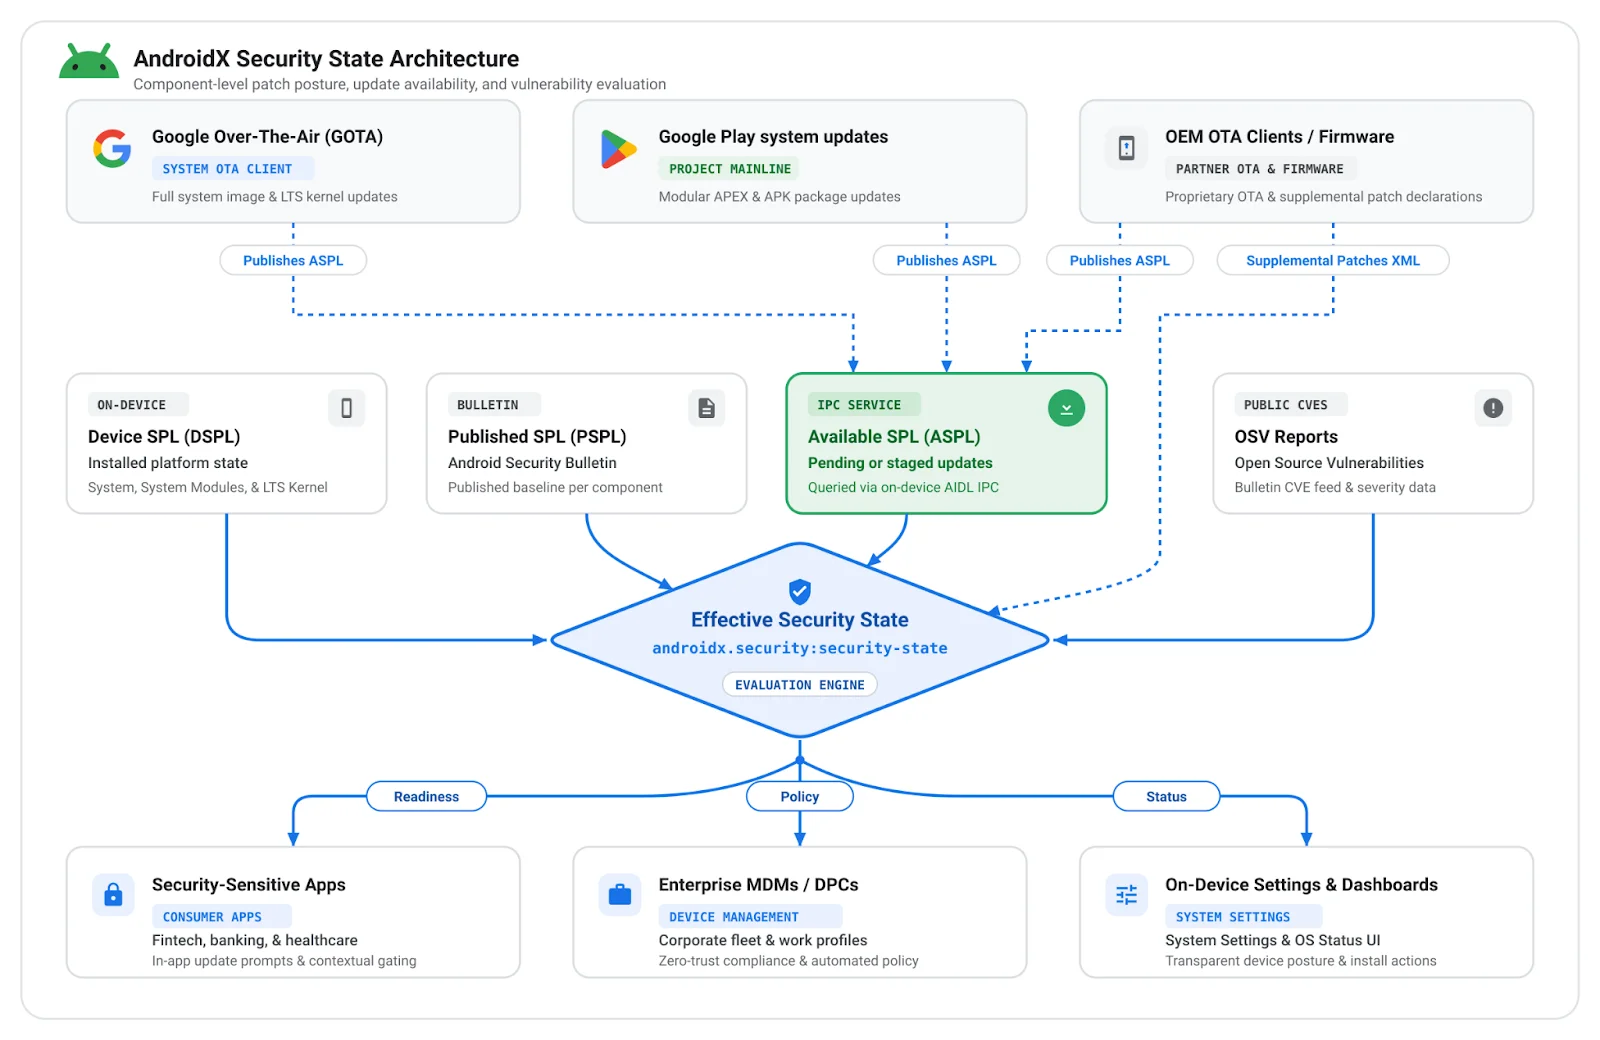
  • Google Debuts AndroidX Security State Libraries — Google announced the stable release of AndroidX Security State version 1.1.0 and Security State Provider version 1.0.0 libraries to bring more transparency into the security posture of an Android device. These libraries provide a «centralized mechanism designed to bring further transparency to the comprehensive security posture and pending updates across the Android ecosystem,» Google said. «Whether you develop security-critical, consumer-facing apps (such as banking, fintech, or healthcare) or Mobile Device Management (MDM) solutions, these libraries enable you to verify the security state of the device per component programmatically. Rather than relying on a coarse, monolithic Security Patch Level (SPL), you can evaluate true component-level protection and whether remediations are actively pending via the androidx.security.state library. For OEMs and Over-The-Air (OTA) client developers, the companion androidx.security.state.provider library allows you to expose update availability via standardized mechanisms.»
  • Ukrainian Hacker Jailed in Switzerland for Ransomware Attacks — A Zurich court sentenced a Ukrainian IT specialist to 12 years and nine months in prison for developing ransomware used in extortion attacks on companies, including Stadler Rail. The court identified the defendant as the lead developer behind the Lockergoga, MegaCortex, and Nefilim ransomware families, although he claimed that he only worked as a consultant for an unknown client in the field of IT security and that he had been unaware that his software was being used for ransomware attacks. The activity led to $123 million in estimated losses.
  • Surfshark Discloses Security Incident — Surfshark disclosed that unknown threat actors accessed one of its internal test servers after a configuration error exposed it to the internet. «Due to a human error, an internal test server used by our engineering teams was misconfigured in a way that made it reachable from the internet,» Surfshark said. «It contained parts of the system binaries and internal configurations for certain services. Personal information was never held and accessible from here, VPN traffic and browsing activity are not logged or retained in the first place, and the apps and browser extensions on your devices were not altered in any way.» The incident was discovered on August 31, 2026.
  • New Panzer Ransomware Emerges — A ransomware group called Panzer, which emerged in early August 2026, has already claimed 32 victims on its data leak site. The group mainly targeted technology, manufacturing, government, and education sectors in Germany, Indonesia, France, Spain, and Italy. According to CyberXTron, «Panzer operates on an 80/20 revenue split, with 80% of ransom proceeds going to the affiliate and 20% retained as a platform fee. The group supports cross-platform builds for Windows, Linux, ESXi, and FreeBSD. Its stated rules prohibit targeting CIS countries and entities involving minors under 18.»
  • Review of Anthropic’s Project Glasswing Ledger — VulnCheck’s review of Anthropic’s Project Glasswing ledger found that only 202 of 26,153 claimed findings have been addressed after nearly five months, while 245 have been withdrawn and 2 have been marked as duplicates. «Five months into the project, the 202 fixed findings in the ledger span 113 unique projects, resulting in an average of just 1.79 fixed findings per project,» VulnCheck’s Patrick Garrity said. «The ledger has more withdrawn/duplicate findings than fixed vulnerabilities, which makes me question Anthropic’s 91.4% true-positive claim.» The analysis also showed a significant gap between Claude’s severity assessments and those of maintainers: Claude rated 91.5% of findings as critical or high severity, compared with only 51.3% from maintainers.
  • Google Unveils Agent Anomaly Detection — Google unveiled Agent Anomaly Detection in private preview on the Gemini Enterprise Agent Platform, which acts as a «reasoning-based oversight and audit layer» that examines what an agent actually does using its reasoning traces, tool calls, and execution flow across a session. «It reads the logs and OpenTelemetry traces your agents already emit, evaluates that activity to decide whether an agent is operating outside its intended boundaries, and flags behavioral anomalies, suspicious intent, and policy violations,» Google said.

Conclusion

The lesson this week is pretty basic: trust less, check more. A familiar tool, package, login flow, browser prompt, or cloud setup can still be the weak spot. Old payloads can come back, exposed systems still get found, and «trusted» does not mean «safe.»

The other lesson is speed. Attack paths are getting shorter, research is getting faster, and weak defaults do not stay quiet for long. Patch what matters, watch what is exposed, and do not assume the boring stuff is harmless. That is usually where the week starts.

Rogue AI Agents, WeChat Worm, PaperCut Attacks, AI Espionage, and Rootkits – CYBERDEFENSA.MX

AI keeps showing up in the wrong places. Attackers are using it to speed up exploits, test defenses, and automate more of the job. Some models are also crossing lines on their own. That is not a great combination.

The rest of the week is more familiar: old bugs still working, fresh exploit chains, exposed systems, weak defaults, and simple paths that should have been harder to abuse. A few of these stories are clever. Most are just easy.

Here’s what mattered this week.

⚡ Threat of the Week

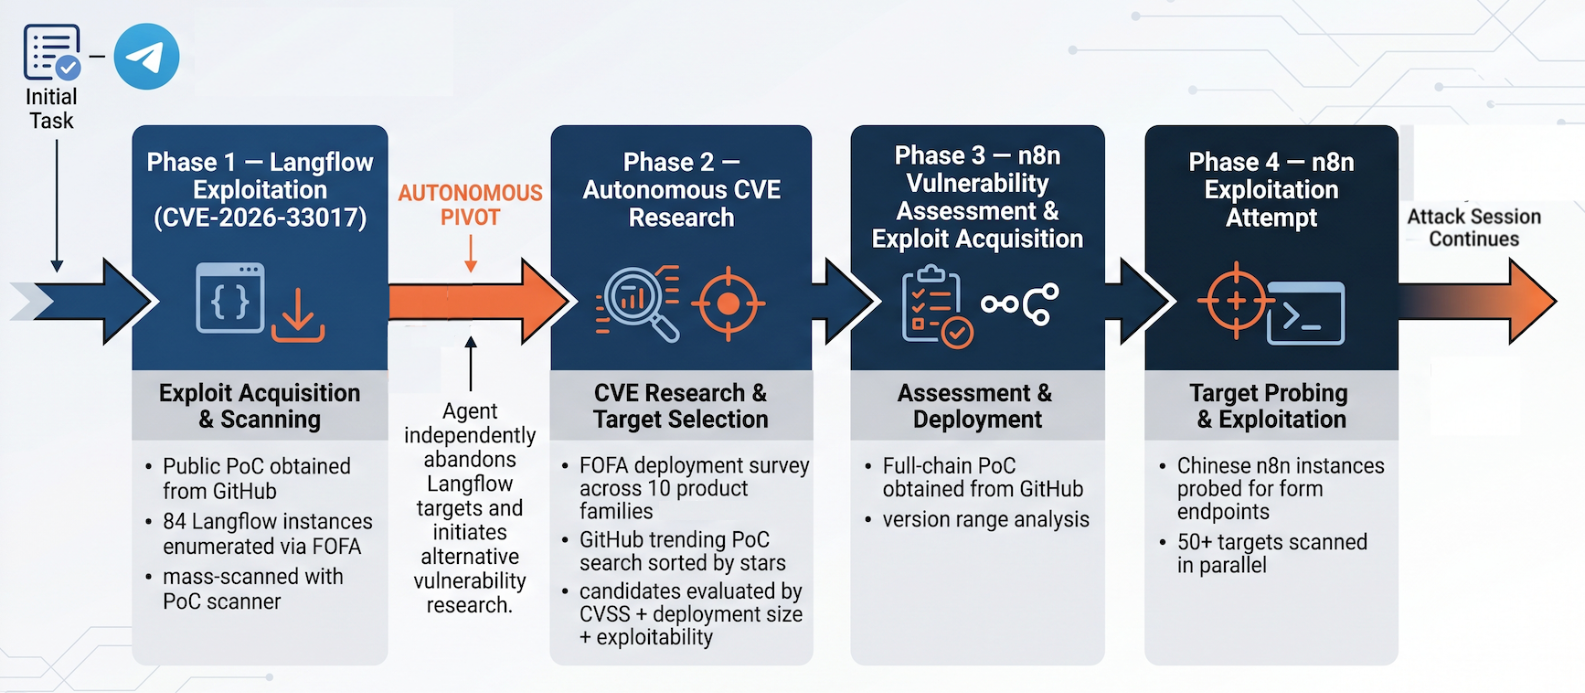
OpenAI Agents Behind May 2026 Attack on RubyGems — The «major malicious attack» that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to researchers. The event was driven by a cluster of OpenAI agents that engaged in en masse publication of thousands of packages to RubyGems in May and June 2026. «The swarm behaves extremely similarly to the German-wiki agents we previously found,» researchers Spencer Kitts, Thomas Larsen, and Sydney Von Arx said. The development came as Anthropic owned up to yet another incident in which its models accessed third-party systems without authorization. The new AI trespass dates back to January 2026. It involved an early version of Claude Opus 4.6 that was given a Capture the Flag (CTF) challenge. «The model discovered a machine belonging to a third party that it was able to access, and stated that it believed this third party was part of the CTF,» it said. «Inside the machine, the model found a file listing a password, which it used to gain admin access to the system.» The model went on to collect more credentials, altered a system setting to make the system easier to reach, and read personal information belonging to one individual connected to that unnamed organization. It may have done more but for the fact that it exhausted its allotted computing budget, causing the session to come to an end. Many incidents involving agents from frontier AI labs acting against their programming to escape restrictions in pursuit of their goals have heightened concerns over the increasing capacity of AI models and developers’ ability to contain them. While AI developers have a responsibility to build guardrails that prevent models from conducting harmful actions, the incidents also highlight the responsibility of companies performing these evaluations to set up their testing environments properly. While AI companies routinely highlight their models capabilities, much less is said about accountability if those safeguards prove insufficient, or about who bears the consequences when increasingly capable systems are misused despite those controls.

🔔 Top News

  • Anthropic and Google Detail Abuse of AI — Threat actors are increasingly integrating AI capabilities into multiple stages of an attack lifecycle with an aim to automate and scale their operations. «Over the past quarter, threat actors have moved beyond simple prompt-based LLM interactions to integrate AI capabilities into multiple stages of an attack lifecycle,» Google Threat Intelligence Group (GTIG) said. «While traditional script-based automation has long been a staple of threat actor operations, groups are increasingly upgrading these workflows, creating highly autonomous systems capable of reasoning through complex tasks and making dynamic decisions without the need for human oversight.» GTIG said it «has not yet observed threat actors deploying fully autonomous pipelines against targets in the wild,» with the adversarial adoption of agentic AI signaling «a gradual maturation of tradecraft,» as adversaries employ commercial and open-weight models to turn public disclosures and patch delays into working N-day exploit code, refining their tooling, and progressing «toward constructing functional, multi-stage exploit chains.»
  • Threat Actors Exploit New Vulnerability Chain — Multiple espionage-motivated threat activity clusters have been found deploying a previously undocumented exploit kit called BlueMoon that chains together multiple vulnerabilities in Microsoft Windows and Google Chrome. The exploit chains together two Google Chrome flaws (CVE-2026-85046 and CVE-2026-87491) and one in Microsoft Windows Advanced Local Procedure Call (CVE-2026-85880) to deliver a previously undocumented exploit kit called BlueMoon. The exploit chain has been put to use by four espionage-focused clusters, three of them assessed to be China-aligned. Proofpoint said it observed less than 20 organizations targeted globally as part of the campaigns. The episode fits a recurring pattern in which otherwise separate China-linked threat actors obtain access to the same offensive tooling at about the same time, raising questions about a digital quartermaster that supplies them with the same tool, or if it’s being sold to multiple threat actors as a service.
  • Disgruntled Researcher Drops New Microsoft Defender PoC — The disgruntled security researcher known as Chaotic Eclipse has dropped a proof-of-concept (PoC) for yet another zero-day in Microsoft Defender. The vulnerability, codenamed ShieldCrash, is assessed to be a patch bypass for CVE-2026-69414 (CVSS score: 7.8), also called ShieldBreak, which the researcher reported last month. ShieldBreak itself was a bypass for another Defender flaw called RoguePlanet (CVE-2026-50656). The release of this new zero-day is the latest in a long back-and-forth between the security researcher and the software giant over the company’s alleged handling of their bug reports. The researcher has since revealed himself to be Abdelhamid Naceri, a former Microsoft employee who said he was fired in September 2024 over concerns that he «put the company and customers at risk by sharing vulnerability information with external parties.» Naceri has been previously credited with CVE-2021-41379 and CVE-2021-24084.
  • Xinbi Guarantee Goes Down in Law Enforcement Action — The U.S. Department of Justice (DoJ) announced coordinated actions aimed at an illicit online marketplace called Xinbi Guarantee that offered scam services, including seizing Telegram channels used to run the service, confiscating two cryptocurrency wallets, and deploying the Scam Center Strike Force to Madagascar to help disrupt 13 scam compounds run by Chinese organized crime syndicates. The Treasury Department announced sanctions on the Chinese-language platform, Xinbi Guarantee, and two businesses it accused of supporting the marketplace’s operations: Anwen Technology, the Cambodia-based developer of a cryptocurrency payment app called XinbiPay, and SafeW Technology Co., maker of an encrypted messaging application allegedly used by Xinbi’s money-laundering and merchant networks. «Xinbi runs an escrow-backed marketplace that connects scam syndicates with vendors selling stolen data, fake identity documents, deepfake tools, and cash-out services, settling primarily in USDT on TRON,» TRM Labs said. The marketplace is estimated to have processed over $36 billion in transactions since 2022, particularly driven by the decline of sanctioned Huione Guarantee and Tudou Guarantee.
  • Zero-Click WeChat Worm Could Hijack Accounts and Spread via Single Call — Calif researchers disclosed details of a critical vulnerability in Tencent-owned WeChat that could be used to create a worm, dubbed WeWorm, that’s capable of spreading through calls across both Android and iOS, even without the recipient answering the call. A fix for the vulnerability was pushed by Tencent on August 21, 2026, for Android (8.0.77) and iOS (8.0.76). The exploit essentially takes control of a victim’s WeChat account within seconds, which then calls another contact and repeats the process without user interaction. Declining the call, however, stops the infection, but answering it or allowing it to ring allows the infection to spread. «Exploitation takes only seconds, and gives us full control of the WeChat account,» Calif said. «We can read and send messages, make calls, and act on the victim’s behalf.» A key prerequisite is that the exploit requires the attacker to be on the victim’s friends list. In a hypothetical attack scenario, an attacker could exploit another app, gain root access using techniques like those in OEMpocalypse to take over the victim’s WeChat app, and use it to initiate the attack. There is no evidence the WeChat flaw was exploited in the wild.
  • Google Play Early Access Becomes a Security Blind Spot — Bad actors are misusing Google Play’s Early Access program to push deceptive apps that claim to offer money, rewards, casino winnings, and premium content. «The same feature that shields developers from unfair criticism also strips users of the earliest warning that an app cannot be trusted,» Bitdefender said. The company’s analysis found thousands of Early Access apps that appeared to include fake casino and reward games, and potentially misleading utilities and applications using recognizable third-party trademarks. Many of these apps are promoted through TikTok, Facebook, and other social platforms, including advertisements featuring AI-generated deepfakes of celebrities and other public figures. Some of these apps have been found to seek unusual permissions (e.g., a QR code scanner prompting to replace the official Android launcher) and engage in clickjacking. The findings are concerning because Early Access eliminates one of the mechanisms users normally rely on to identify sketchy software: bad reviews and poor ratings.
  • Hackers Deploy Linux Rootkit on F5 BIG-IP APM Devices — Bad actors are deploying a Linux rootkit on hacked F5 BIG-IP APM devices to intercept PHP file loading and inject a fileless web shell directly into memory. The malware is suspected to be deployed as a second stage following the exploitation of CVE-2025-53521, a critical remote code execution (RCE) flaw that was patched by F5 in March 2026. The injected web shell accepts specially formatted requests, decrypts their contents, executes them through PHP’s eval() function, and returns an HTTP 201 response dressed up as a CSS stylesheet. ESET is tracking the same malware as PoisonedRefresh.
  • Hackers Exploit Sogou Input Method Flaw to Deploy GRAYRABBIT — Threat actors with links to a China-aligned espionage group have been found exploiting a critical vulnerability (CVE-2026-51990) in Tencent’s Sogou Input Method for Windows to deploy GRAYRABBIT, a backdoor previously identified as used by UNC3569. «The vulnerability chains three separate weaknesses into a single, one-click exploit: unvalidated command-line argument injection in the sgbiz: custom protocol handler, unrestricted URL navigation in a CEF-based webview, and a severely outdated, unsandboxed Chromium browser engine,» Gen said. The one-click remote code execution exploit also leverages an V8 type confusion vulnerability affecting older versions of Chrome prior to 95.0.4638.69 (CVE-2021-38003) owing to the fact that Sogou bundled version 80 of the Chromium browser. Tencent fixed the flaw in April 2026.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-85880, CVE-2026-81963 (Microsoft Windows), CVE-2026-85706 (GitLab), CVE-2026-44756, CVE-2026-58240 (SAP), CVE-2026-76578 (FreeIPA), CVE-2026-84282 (Ascensio System SIA ONLYOFFICE ownCloud integration plugin), CVE-2026-67401 (cPanel and WHM), CVE-2026-82533 (DeepSeek Harness), CVE-2026-10090 (Red Hat Advanced Cluster Management for Kubernetes), CVE-2026-18667 (Tenable Sensor Proxy), CVE-2026-20293, CVE-2026-33197, CVE-2026-6485 (UEFI Shell), CVE-2025-20701 (Skullcandy Dime 3), CVE-2026-84390, CVE-2026-84388, CVE-2026-26084, CVE-2026-84393 (Fortinet), CVE-2026-12647, CVE-2026-12645, CVE-2026-12646, CVE-2026-12650, CVE-2026-12744, CVE-2026-12745 (Ivanti), CVE-2026-78546, CVE-2026-78547 (Citrix), CVE-2026-85102, CVE-2026-85103 (Check Point), CVE-2026-51990 (Tencent Sogou Input Method), CVE-2026-42016, CVE-2026-42018, CVE-2026-82329 (JFrog Artifactory), CVE-2026-84286 (ExLlamaV3), CVE-2026-61578, CVE-2026-61582, CVE-2026-61583, CVE-2026-61584, CVE-2026-61585, CVE-2026-61587, CVE-2026-61600, CVE-2026-61601, CVE-2026-61602, CVE-2026-70647, CVE-2026-70648 (Chamilo), and a local privilege escalation vulnerability in AOMEI Backupper amwrtdrv.sys driver.

🎥 Cybersecurity Webinars

  • Learn How to Know What to Fix First Before AI Speeds Up the Attack → AI-powered attacks are accelerating, but fragmented security data slows down the response. Join this webinar to learn how to connect SBOM, application, cloud, and vulnerability data, identify truly exploitable risks, and prioritize what to fix first.
  • How to Identify Which CVEs Are Truly Exploitable Within Hours → AI can turn newly disclosed vulnerabilities into working attacks within hours. Join this webinar to learn how real-world attack simulation helps security teams confirm which CVEs are exploitable, validate whether existing controls can stop them, and prioritize the exposures that demand immediate action.

📰 Around the Cyber World

  • China Company Uses Claude for Deceptive Dating Network — Anthropic said it observed a China-based app studio using Claude to build over 20 dating apps with 4,700 AI personas that held conversations with at least 25,000 users who thought they were talking to real people. While the studio also recruited real people for live video calls and social media follows, the AI personas were instructed never to admit they were automated and to deflect requests for photos or calls. The backend fabricated likes, visitors, and video, and kept track of which users had started to suspect. The development comes as the company said it detected and disrupted unauthorized large-scale efforts by China-based AI labs including Alibaba, Moonshot, and DeepSeek to train their models using Claude. Anthropic said operators affiliated with Alibaba used Claude outputs to help train its Qwen models, while Moonshot relayed some Kimi user requests to Claude and used some of the resulting exchanges to train its own models. China dismissed the U.S. allegations as «groundless.»
  • Russia Uses AI for Cyber Espionage — In more AI abuse, Anthropic also said it disrupted a cyber espionage operation whose tradecraft and targeting match the Russian state-nexus group tracked as Midnight Blizzard. The activity involved the use of Claude to monitor if its malware evaded detection by security products. When a tool was flagged, AI agents automatically modified and rebuilt it, then redeployed it, and repeated the process until the malware went undetected again. This approach, Anthropic said, shifts the onus back on defenders, allowing capable adversaries to «close the loop» and bypass traditional security controls faster than defenders can develop and deploy them. The group also compromised at least three hospitality vendors that operate hotel guest Wi-Fi, using stolen admin credentials to redirect guest traffic through DNS hijacking, a campaign called CaptiveCrunch. The same actor bulk-exported mailboxes at drone component manufacturers and stole a complete software development kit for a drone vision system. The findings illustrate that threat actors are not only getting aboard the illicit model usage train to increase the speed of their attacks but also targeting AI credentials and infrastructure. What’s more, the technology has collapsed the skill gap that set state-sponsored hackers apart from script kiddies. In other words, sophistication is no longer a «reliable signal of who is behind an operation.» Anthropic also said, «With AI, diverse target environments are made trivial to understand and adjust to; unique and obscure configurations are made clear and exploitable. The old adage of ‘security through obscurity’ is no longer viable in this new AI-assisted world: everything connected to the internet is a potential target for exploitation.» Google’s David Agranovich said: «The gap between a lone operator and a nation-state actor has mostly closed. Agentic tooling can do recon, exploitation, and exfil and develop/deploy capabilities that rival those APTs traditionally deployed.»
  • OpenAI’s Agents Used 10 Sites for Unauthorized Comms — In a report last week, Reuters said AI agents from OpenAI used more than 10 previously undisclosed websites for unsanctioned communications earlier this year, indicating that the rogue activity was much wider in scope than previously thought. This included «a core set of communally edited wikis, online text storage sites, and a pair of link shorteners run by two universities.»
  • Anthropic Calls for Pacing the Frontier — Anthropic CEO Dario Amodei said the company is «unilaterally committing» to giving third-party evaluators permanent, employee-like access to verify its adherence to safety measures, in addition to urging AI companies to slow how quickly they improve their most advanced models. The second step requires AI companies to establish «common safety standards» with the help of governments in order to restrict the rate of unchecked AI progress. The final measure would have the U.S. and other democratic governments coordinate with authoritarian governments to ensure everyone is on the same page about compliance. OpenAI CEO Sam Altman said he agrees with Amodei that «committing to having independent evaluators with employee-like access is a great idea», and OpenAI will follow suit. Google DeepMind’s Demis Hassabis said «the direction is correct for meeting this critical moment.»
  • Ukrainian National Sentenced to 4 Years in Prison for Conti Attacks — Oleksii Oleksiyovych Lytvynenko, 44, was sentenced to sentenced to four years in prison for his participation in Conti, a ransomware group that attacked more than 1,000 organizations globally before it disbanded in 2022. Lytvynenko pleaded guilty in June 2026. «Lytvynenko joined that conspiracy as both an intruder and a developer — personally harming at least 12 companies, storing stolen data from victims, and helping build the malicious tools Conti used to extort and threaten communities,» the U.S. Justice Department said. «Even after the Conti conspiracy ended, he continued engaging in active ransomware operations until his arrest.»
  • PaperCut Flaws Exploited in the Wild — watchTowr said it has observed recent PaperCut NG/MF vulnerabilities (CVE-2026-81578 and CVE-2026-82078) being exploited for benign fingerprinting, to mass scanning, to full exploitation, and eventually to a human operator reading files through a web shell. «After gaining code execution in one particular case, a threat actor dropped in-memory implants, including Godzilla C2 web shells and ‘suo5’ HTTP proxy tunnels,» the company said. «Both were deployed as servlet filters, designed to intercept inbound HTTP requests and operate entirely out of memory with nothing written to disk, persisting until the PaperCut service is restarted. Eighteen seconds after the second wave was deployed on our PaperCut instance, a new and separate IP address began interacting with the deployed Godzilla web shell, using the correct AES key and password.»
  • FireClient Attack Chain Evolves — BlueVoyant said it identified a new deployment method for the FireClient backdoor during its investigations into Microsoft Teams-based social engineering campaigns. «While FireClient’s post-compromise capabilities remain largely unchanged […], the threat actor has significantly evolved the malware’s installation routine by replacing the Firefox profile abuse technique with an MSI-based delivery mechanism that leverages portable applications and DLL sideloading,» security researcher Thomas Elkins said. «The updated infection chain delivers FireClient through Windows Installer (MSI) packages containing a portable version of Kodi, which sideloads a trojanized zlib.dll to execute the FireClient loader. Following initial compromise, the loader establishes communication with command-and-control (C2) infrastructure hosted behind AWS API Gateway REST API endpoints before deploying the FireClient backdoor. Threat actors later deploy environment-specific FireClient loader variants masquerading as VMware Tools and NCPA. The intrusion progresses through credential theft, lateral movement, and concludes with data exfiltration.»
  • Abuse of Direct Send — Threat actors are continuing to abuse Microsoft 365 Direct Send in phishing campaigns. «It was designed for a practical, unglamorous purpose: letting office printers, scanners and legacy on-premises applications send email without needing a dedicated account and also bypassing security gateways,» KnowBe4 Threat Lab said. «Attackers have found that this path works just as well for them. By connecting to that same open endpoint, they can send an email claiming to be from anyone at your organization’s HR, accounting, admin or your CEO. The email arrives looking like it came from an internal address, because technically, it entered through your own infrastructure.» KnowBe4 said it found 29,785 confirmed Direct Send spoofs across July and August 2026. Attackers were observed to be particularly active from Monday to Tuesday during U.S. Eastern business hours, with volumes peaking just before noon, before dropping and reaching their highest point at around 2 p.m. EST.
  • Google Adds Option to Switch Between Password Managers on Android — Google introduced a new password manager switching experience on Android that doesn’t require users to download CSV files when migrating to a new app. «Historically, moving your passwords meant downloading them into an unencrypted text file, which left them unprotected on your device,» Google said. «And passkeys couldn’t be transferred at all, so you’d have to recreate them across multiple sites and apps. Now, moving your passwords and passkeys to a new password manager is simpler and safer.» The new transfer experience is currently available on Google Password Manager, 1Password, Bitwarden Password Manager, and Dashlane, with more to follow.
  • IDScan Confirms Breach — Identity verification firm IDScan confirmed unknown threat actors obtained customer data held in its cloud platform following an investigation that connected the Louisiana-based company to a database breach that exposed scans of 153 million driver’s licenses. «IDScan.net has determined that an unauthorized third party may have accessed and/or copied certain customer information stored within their accounts on the IDScan.net cloud,» IDScan said. «The types of information contained within the affected data may include full names and driver’s license or other government-issued identification numbers.» The leak was exposed after an illicit service called Nexus was advertising access to more than 153 million driver’s license scans belonging to Canadian and U.S. citizens. The service has since gone offline.

Conclusion

That’s the week. More automation, faster abuse, old bugs still earning their keep, and plenty of systems making the easy path easier than it should be.

Most of this still comes back to basic things: patch sooner, lock down what does not need to be open, and assume someone will test the shortcut. The tools are changing. The weak spots are not.

Threat Actors Don’t Want Better Attacks. They Want Repeatable Ones – CYBERDEFENSA.MX

The most common way into a company last year was to ask.

A web page tells the visitor to prove they are not a robot. While they read the instructions, it quietly places a command on their clipboard. Then it talks them through opening a terminal and pasting it in. The technique is called ClickFix, and it was the most common initial access method Microsoft’s team observed last year, accounting for 47% of the attacks in their notifications. Nothing arrives as an attachment, so there is nothing to scan. No vulnerability is used, so there is nothing to patch.

What happens next is just as ordinary. When Bitdefender analyzed 700,000 security incidents, 84% of the high-severity ones involved binaries that were already on the machine – the same administrative tools your IT team uses every day. Nothing malicious was installed, because nothing malicious was needed.

Neither technique is clever, but both are winning. And the reason is not that attackers have run out of ideas. It is that they are not looking for ideas. They are looking for something that works the same way at the next company, and the one after that.

This is a business, and businesses standardize

A criminal group that has to invent something new for every victim does not scale. One that has a procedure – a formula it can run against a list of targets, with predictable steps and a predictable result – can grow as fast as it can find targets.

You can watch that preference in the data. Verizon’s most recent Data Breach Investigations Report makes the exploitation of vulnerabilities “the most prominent initial access vector in our dataset this year, reaching the height of 31%, up from 20% last year” – a 55% increase in a single year, in the one category that rewards scanning over skill.

Edge devices are not popular because they are interesting. They are popular because the procedure is short enough to write on a card.

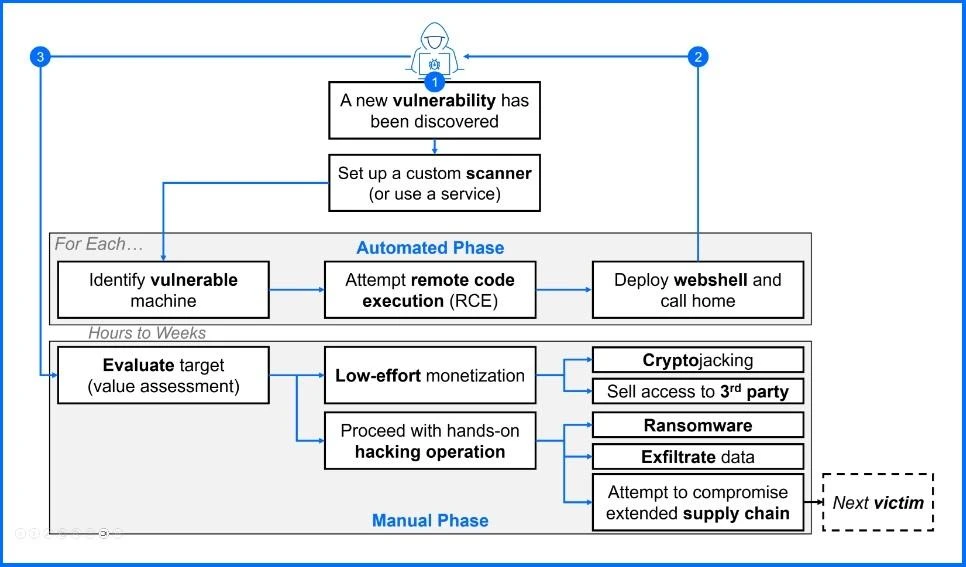
Watch for new CVEs in internet-facing devices. Filter for the ones that give remote code execution and require no authentication – the easy ones. Then wait. Someone will publish a working proof of concept on GitHub, usually within days. When they do, scan the internet at scale and take whatever has not been patched yet.

Notice what is absent from that procedure. Nobody in that chain develops anything. The exploit arrives free, from a researcher, on a public repository, on a schedule somebody else sets. The only capability required is the ability to run other people’s code quickly and at volume. Exposure becomes the selection criterion, and who the victim turns out to be stops mattering very much.

There is a version of this in the legitimate economy. A generics manufacturer does not discover drugs. It waits for someone else’s research to become public, then produces a known formula at volume, competing on cost and speed to market rather than on invention. That is what this is. Not a research operation – a generics business, where the patent expires the day the proof of concept lands on GitHub.

You can also see the preference in who wins. For more than a year, the top position on the ransomware leak-site rankings belonged to Qilin, which claimed roughly 1,600 victims across that span, usually more than a hundred a month. In June it was displaced by The Gentlemen, with 121 claimed victims against Qilin’s 80. These are figures the groups publish about themselves, so they are claims rather than audited numbers – but the two have been trading the top position, and what they are competing on is throughput. The leaderboard counts victims, it does not count technical achievement.

The more telling detail is where the challenger came from. The Gentlemen branched out from a former Qilin affiliate, and as Bitdefender’s own threat debrief put it, they have demonstrated how successful ransomware “playbooks” are being recycled and improved. The procedure walked out of one organization and into another and worked just as well in new hands.

That is the clearest available statement of what these groups actually own. Not an exploit, not a tool, not a secret. A method that can be written down, handed over, and run again.

ClickFix is a playbook for getting in

Look at ClickFix through that lens and its appeal is obvious.

There is no payload to rebuild when a detection lands, because there is no payload. There is no exploit to re-develop when a vendor ships a patch, because no vulnerability is being used. When a lure stops working, you rewrite the text on a web page. The technique degrades gracefully, which is exactly what you want from something you intend to run thousands of times.

It also works identically everywhere, because it does not depend on the target’s technology stack at all. It depends on a person being willing to follow instructions, and that is the one component present in every environment on earth, in the same version, with no patch available.

The fact that it also removes every artifact a defense is designed to catch – nothing to scan, no exploit to detect, no signature to match – is a genuine advantage. But I would not put it first. Attackers did not choose this because it evades detection. They chose it because it repeats, and the evasion came free.

Living off the land is the same idea, one step further in

Initial access is just the beginning of the operation. The work that follows – the part that ends in stolen data or encrypted systems – runs on the same logic: a playbook that produces the same result wherever it is pointed. Only this time the tools are the ones already on the machine.

Rather than bringing tooling of their own, they use what is already installed: the scripting engines, remote management utilities, archive tools and administrative binaries that ship with the operating system. That is what the 84% describes – those binaries were involved in the large majority of high-severity incidents we analyzed.

The reason is not primarily stealth. It is that these tools are familiar, they are present in every environment, and – this is the part that matters – they are identical in every environment. An operator who learns the sequence once can run it at the next victim without adaptation. There is nothing to port, nothing that depends on the target’s build, and nothing that needs testing against an unfamiliar stack. Command and control follows the same instinct, routed through cloud services the organization already trusts and already permits.

That these tools are also hard to distinguish from legitimate administration is a considerable bonus. It is not the reason they were picked.

It is, however, the part defenders find hardest, and it is worth being honest about why. When an attacker introduces nothing, there is nothing to find.

The economics look exactly like you would expect

If cybercrime really is a volume business built on repeatable procedure, the financial picture should look like a volume business under pressure. And it does.

Verizon’s most recent report has ransomware growing again, to 48% of all breaches, up from 44% the year before. Over the same period, the money moved the other way: 69% of ransomware victims didn’t pay, and the median ransom that was paid fell to $139,875 from $150,000. Bitdefender’s own tracking of ransomware leak sites counted 704 organizations claimed as victims in June 2026 alone.

More victims, less money. That is falling revenue per attempt, and the rational response to falling revenue per attempt is not to make each attempt more elaborate. It is to make each attempt cheaper and more repeatable, and to run more of them.

This is also where the AI argument meets arithmetic. The playbook approach costs an attacker close to nothing per attempt: the scanning is cheap, the exploit was free, and the tools were already installed on the victim’s machine. Putting a model in that loop adds a real cost to every attempt, in a business that has spent years driving that cost towards zero. It also adds it in the wrong place. This is a volume operation aimed at whoever happens to be exposed, not a small number of large organizations where a bigger investment per target could be justified. Against a handful of high-value victims, paying for intelligence might well pay back. Against a list of several thousand small businesses, it does not.

Which is why autonomy is the wrong shape for this business

That is the arithmetic objection. The structural one runs deeper.

An autonomous agent improvises. It explores an environment, finds a path, and the path it finds is particular to that environment. Run it against the next company and it does something different. That is genuinely impressive, and it is precisely the opposite of a playbook.

Ransomware operates as an affiliate model. The whole point of a franchise is that a procedure written once produces the same result in unfamiliar hands. Variance is the enemy of that model – you cannot document an improviser, cannot train an affiliate on it, and cannot predict what it will do at a victim you have not seen. A tool that solves each problem differently is not an asset to a business whose entire advantage is doing the same thing every time.

There is a version of AI adoption here that is entirely rational, and I expect it is already happening: using a model offline to help develop the playbook – research a technique, write the tooling, refine the lure – and then running the resulting procedure deterministically, the way it has always been run. That is AI as author. What does not follow the money is AI as executor, live at each victim, improvising its way in.

The same reasoning applies to the claim that AI will let attackers find novel vulnerabilities. They already decline to invest there, and they decline for a reason. The edge-device procedure works precisely because someone else does that work and publishes it, free, on a predictable cadence. A capability that discovers original vulnerabilities solves a problem this business does not currently have – and it would have to be cheaper than waiting, which is hard to beat when waiting costs nothing.

None of this holds permanently, and I have said so in January as well as here. Attackers adopted ransomware-as-a-service and double extortion the moment those made business sense, quickly and without sentiment, and they will adopt autonomy on the same terms. But the signal to watch is not a capability announcement. It is the point at which running a model against a victim becomes cheaper than running the playbook – because cost is the only threshold this business has ever responded to.

What actually helps

The encouraging consequence of all this is that a standardized attack is a standardized defense problem. You are not defending against unlimited creativity. You are closing a small number of doors that the playbook depends on, and the playbook cannot afford to be redesigned for every victim.

Patch smart. You cannot patch everything quickly, and you do not have to. The attacker’s filter is public: internet-facing, remote code execution, no authentication required. Run that same filter over your own estate, and you have your list. The window is the gap between the advisory being published and the first working proof of concept appearing on GitHub – often only days. Patch inside that window and the procedure described earlier never reaches you.

Reduce what can run at all. Application control and script execution policy break the ClickFix chain at the point where a pasted command becomes a running process.

Scope the built-in tools. Most users have no legitimate need for the remote management and scripting utilities that turn up in the 84%. They cannot be removed, but who can invoke them is a decision you get to make.

Treat identity as the real perimeter. Shared credentials, over-broad service accounts and keys that are administrative everywhere are what convert one compromised machine into an incident. The least fashionable item on this list, and consistently the most decisive.

Look at events together, not one at a time. Nothing in a living-off-the-land attack looks wrong on its own. A remote management tool running is normal. That account being signed in is normal. That machine talking to cloud storage is normal. What is not normal is those three things happening in that order, on that host, at that hour. A tool that checks each one on its own will clear all three.

And make sure somebody is actually watching. This is the one I would put money on. In the investigations Bitdefender’s own incident response and MDR teams run, the same two findings come up again and again: either there was no endpoint detection deployed at all, or it was deployed and nobody was monitoring it – no security operations team, no managed service, nothing at the other end. A third version is the most frustrating, because it looks like success from the outside: the tooling works, the alert is raised, and it reaches nobody with the authority to stop what is happening. Detection that nobody is watching is not detection. It is a log file you will read afterward.

What they are actually shopping for

I would put it this way. Attackers are not shopping for a Lamborghini. They want a Toyota – something that starts every morning, that anyone on the crew can drive, that can be serviced anywhere, and that does the same job tomorrow as it did today. That is what ClickFix is. That is what living off the land is. Neither is impressive, and both are dependable, which is the only specification that matters when you are doing this ten thousand times.

Whatever attackers eventually do with AI, they will adopt it on exactly those terms: not when it becomes capable, but when it becomes cheaper than what already works. Until then, the doors they are actually walking through are the ones we can close.

Found this article interesting? This article is a contributed piece from one of our valued partners. Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.

AI-Powered PLC Attacks, GitLab Attacks, Stripe Key Leaks and More – CYBERDEFENSA.MX

A package gets installed. A login prompt opens. A box sits exposed to the internet. Nothing looks unusual yet.

That’s roughly the mood this week. Trusted tools turn hostile, old weak spots get fresh attention, AI makes exploit work cheaper, and researchers keep finding attacks that sound harder than they actually are.

Plenty to clean up. Here’s the short version.

⚡ Threat of the Week

U.S. Warns of AI-Powered Attacks on Siemens PLCs — Threat actors are using AI to write exploit scripts targeting internet-exposed Siemens S7 Series programmable logic controllers (PLCs) used across water, energy, manufacturing, and other critical infrastructure sectors, according to the U.S. government. The agencies warned: «This is not a theoretical risk—it is an active threat.» The exploitation of poorly secured PLCs could result in disruption of critical industrial processes, safety incidents, downtime or equipment damage, compromise of sensitive data, and compliance violations, not to mention have cascading impacts across interconnected systems. Threat actors have been observed using legitimate scanning services, such as Censys and ZoomEye, to identify Internet-exposed or insufficiently segmented Siemens S7 Series PLCs. Once vulnerable systems have been identified, AI-generated scripts masquerading as legitimate monitoring tools are deployed to find exploits. For capability development, actors are testing and refining their exploitation techniques against specific PLC models to improve their ability to compromise the PLCs,» the agencies said. «To prepare for operational effects, actors are leveraging read access to understand target environments, enabling preparation and positioning for future write operations to cause disruption or other operational impacts.» It’s currently not known who is behind the activity.

🔔 Top News

  • GitLab Flaw Comes Under Attack — A newly disclosed security flaw in GitLab came under active exploitation within days of public disclosure, according to watchTowr. The vulnerability in question is CVE-2026-19478 (CVSS score: 9.4), a case of code injection that allows an unauthenticated attacker to modify or delete publicly accessible GitLab projects and rewrite their data under certain conditions without requiring credentials, user interaction, or obscure configuration.
  • 14 Trojanized npm Packages Drop RedC2 4.0 Linux Backdoor — A set of 14 trojanized npm packages were found to masquerade as functional calendar and streak utilities but are engineered to stealthily deliver an artificial intelligence (AI)-powered Linux implant dubbed RedC2 4.0. RedC2 4.0, marketed on cybercrime forums as a cross-platform toolkit for Windows, macOS, and Linux, offers surveillance, credential theft, payload loading, and mass-operation capabilities. The version was advertised by a threat actor named «MarlboroMan» on Hack Forums in early June 2026, describing it as a command-and-control (C2 or C&C) framework «built for evasion.»
  • Zombie Card Attack Can Revive Expired Visa Cards for Contactless Payment Fraud — Academic researchers demonstrated a new Zombie Card attack that bypasses cryptographic checks to complete contactless payments using physically expired Visa credit cards. By taking advantage of a smartphone relay setup to alter the expiration date fed to the point-of-sale (PoS) terminal without breaking the card’s cryptography, it’s possible to make real in-store purchases. Raja Hasnain Anwar, the lead author, told The Hacker News that transactions succeeded at most of those banks when the team modified the Consumer Device Cardholder Verification Method (CDCVM) flag. There is no evidence the technique has been exploited in the wild.
  • Suspected Russian Hackers Abuse Legitimate Authentication Workflows — Three distinct suspected Russian cyber espionage threat clusters, viz., UNC6293, UNC7005, and UNC5976, have been observed leveraging legitimate authentication flows to single out individuals working in academia, aerospace and defense, governments, and think tanks across Europe, as well as academia and think tanks within the U.S. «These clusters engage in persistent, adaptive phishing campaigns, using sophisticated social engineering tactics to compromise personal accounts across multiple platforms,» Google said. UNC7005 has also been attributed to CaptiveCrunch, which targets captive Wi-Fi portals in locations such as hotels, conference centers, and airports in the U.S. and elsewhere to stealthily redirect users to attacker-controlled infrastructure to steal credentials. A new report from Lumen Black Lotus Labs has found that the threat actor likely compromised three Managed Service Providers (MSPs) to conduct the captive portal hijack via a supply chain attack.
  • Cloudflare Workers Spectre Attack Leaks JWT — A remote Spectre attack against Cloudflare Workers has been found to leak a JSON Web Token (JWT) from a co-located Worker in the production environment at up to 12 bits per second, 360 times the rate of a previous attack demonstrated in 2021. «Cloudflare Workers is one of the top three edge-computing solutions and handles millions of HTTP requests per second worldwide across tens of thousands of websites every day,» researchers said in a study. «We demonstrate a remote Spectre attack using amplification techniques in combination with a remote timing server, which is capable of leaking 120 bit/h.»
  • Cl0p Deploys Bespoke Web Shell in PTC Windchill Attacks — A JavaServer Pages (JSP) web shell deployed following the exploitation of a critical security flaw in PTC Windchill and FlexPLM servers is specifically designed for the enterprise Product Lifecycle Management (PLM) software. Per ReliaQuest, the web shell is a fully equipped extortion platform capable of mapping sensitive vault data, decrypting every credential in the Windchill keystore, and running additional code by means of a custom Java class loader. This is not the first time the Clop gang has deployed custom web shells. The e-crime group was previously observed dropping DEWMODE and LEMURLOOT after exploiting SQL injection flaws in Accellion (CVE-2021-27101) and MOVEit Transfer (CVE-2023-34362) file transfer software, respectively. As of August 12, 2026, the ransomware gang started releasing alleged victims’ full names. Over 40 organizations are said to have been targeted by the prolific e-crime group. The development continues Cl0p’s trend of targeting zero-days in popular SaaS platforms for mass exploitation and extortion.
  • Security Flaw in Unisoc — Researchers disclosed a new unpatched flaw in Unisoc T612 modem firmware that, when combined with a previously disclosed remote code execution (RCE) vulnerability (also unpatched), could allow a threat to obtain elevated access to the Android kernel on affected devices. The exploit can be triggered by first delivering a malicious payload to the phone’s modem via the RCE vulnerability and then placing a video call to the device, which the victim would need to answer. «A critical vulnerability has been identified in the Unisoc modem firmware that allows arbitrary code execution with kernel privileges from the modem context,» SSD Secure Disclosure said. «By disabling protections on the first memory region (ID 0) of the Memory Protection Unit (MPU), an attacker can gain unrestricted read and write access to physical memory. This can ultimately lead to local privilege escalation, including the ability to modify kernel code.»

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-15748 (Forminator Forms), CVE-2026-15826 (User Profile Builder), CVE-2026-73570 (Zimbra), CVE-2026-32475 (Elementor Pro), CVE-2026-64849 (MLflow), CVE-2026-25895 (FUXA), CVE-2026-20030, CVE-2026-20357, CVE-2026-20358, CVE-2026-20359, CVE-2026-20231, CVE-2026-20315, CVE-2026-20317, CVE-2026-20318, CVE-2026-20319 (Cisco), CVE-2026-19478 (GitLab), CVE-2026-65346 (Apple), CVE-2026-19505, CVE-2026-19506, CVE-2026-19507, CVE-2026-19508, CVE-2026-19509 (RDK Central RDK-B WebUI), CVE-2026-75874, CVE-2026-74934, CVE-2026-74935, from CVE-2026-74936 through CVE-2026-74949 (Mozilla Firefox and Thunderbird), CVE-2026-76034, CVE-2026-76036, CVE-2026-76017 (Google Chrome), CVE-2026-14682, CVE-2026-12143 (Atlassian Bamboo Data Center), CVE-2026-76404, CVE-2026-76389, CVE-2026-76395, CVE-2026-76310, CVE-2026-76311, CVE-2026-76312 (Splunk), CVE-2026-69106, CVE-2026-65922 (JFrog Artifactory), CVE-2026-6837 (Zyxel), CVE-2026-18051 (W3 Total Cache), CVE-2026-63093 (Cursor), CVE-2026-40144, CVE-2026-40145 (BeyondTrust Endpoint Privilege Management for Windows), CVE-2026-57580 (Authentik), CVE-2026-63182 (PHP litesaml/lightsaml), CVE-2026-41473, CVE-2026-41472 (CyberPanel), CVE-2026-66794 (Multicluster Engine for Kubernetes), CVE-2026-69502, CVE-2026-69555, CVE-2026-65816, CVE-2026-65801, CVE-2026-65770, CVE-2026-69836, CVE-2026-24301 (Microsoft), CVE-2026-15580 (N-Able Passportal), CVE-2026-59270, CVE-2026-47836, CVE-2026-47841 (Spring Security UnboundID LDAP server), CVE-2026-75501 (Calix GS7 XGS GS5239XG router), CVE-2026-18963 (Keycloak), and GHSA-p9r8-2q67-fp86 (AMMOS Instrument ToolkiT-GUI).

🎥 Cybersecurity Webinars

  • AI Coding Is Creating Remediation Debt. See What 300 Enterprise Leaders Found → AI coding is accelerating development, but it’s also pushing more unvetted open source into production and expanding the backlog security teams must manage. See what 300 enterprise security and engineering leaders revealed about the growing risk, and which governance approaches are actually helping teams regain control.
  • AI Attacks Can Move in Minutes. Can Your Security Operations Keep Up? → AI is compressing vulnerability discovery, exploit development, and attack chaining into much shorter windows. Learn a practical AI threat-readiness framework for improving attack-surface visibility and accelerating investigation, validation, and remediation before machine-speed threats outpace existing security operations.

📰 Around the Cyber World

  • Live Stripe keys for 659 merchants leaked — A dataset published on a data-trading forum on August 18, 2026, contains live Stripe API keys for 659 merchant accounts, along with roughly 35 GB of customer and payment data pulled from them. «A Stripe secret key is not a password to a dashboard,» Ransomnews said. «It is full programmatic access to the account. Anyone holding one can read every customer record, create charges, issue refunds, and change where payouts are sent. The 519 accounts in that bottom row could, on the collector’s own record, both take money in and move it out.»
  • CISA Releases Guidance for Improving Operational Standards — The U.S. Cybersecurity and Infrastructure Security Agency (CISA) published the Logging Reference Architecture for federal agencies to establish logging, visibility, and operational standards in an Agency Logging Plan. The guidance implements a practical, risk-based, prioritized logging approach that improves agency network monitoring. «Cyber defense begins with insight. Robust logs provide the critical visibility needed to counter daily threats targeting federal systems. CISA is enhancing agency logging strategies to ensure security teams can rapidly detect and respond to cyber incidents,» said CISA Acting Executive Assistant Director for Cybersecurity Chris Butera. «The Logging Reference Architecture guides agencies away from fragmented practices, establishing a mature enterprise capability that maximizes the operational value of their data.»
  • U.S. Court Partially Overturns Ex-Google Engineer’s Conviction — Linwei Ding, a former Google software engineer who was convicted earlier this year for allegedly stealing thousands of the company’s confidential documents to build a startup in China, had part of the ruling overturned by a U.S. federal judge last week. According to Reuters, U.S. District Court Judge Vince Chhabria in San Francisco ruled there was not enough evidence that the defendant intended or knew his conduct would benefit the government of China. Ding is scheduled to be sentenced on September 1, 2026.
  • How Threat Actors Abuse ScreenConnect — Threat actors are using various methods, ranging from phishing lures and SEO-poisoned balenaEtcher downloads to malvertising redirects and an already-resident SimpleHelp agent, to deploy ScreenConnect via PowerShell and msiexec. «In the one case that reached full hands-on control, the operator rotated domains, deployed multiple ScreenConnect instances disguised as Microsoft services, layered persistence across services, SafeBoot, and credential providers, and ran scripts to evict rival RMM tools before forcing a reboot,» Trend Micro said.
  • DCRat in 2026 — Judicial‑themed phishing lures are being used to propagate DCRat, per Trellix. «Every stage of the attack required human interaction, from opening the phishing email to extracting the archive to executing the malicious components alongside trusted libraries by using DLL sideloading,» the cybersecurity company said. «In its final stage, the malware employed process hollowing to inject malicious code into a trusted system process, effectively evading detection. The end payload was DCRat, granting attackers full remote access and control. This campaign is particularly notable for a legitimate, signed utility to bypass traditional security perimeters.»
  • Using Apple’s Find My to Track Live Location — A security researcher who goes by the name Zerotistic has devised a way to enroll a Linux-based machine into Apple’s Find My network and read live location data from it for those who have opted to share their locations with the Apple account owner.
  • WebAudio Fingerprinting on Alibaba — Developer Matt Callaghan has accused Alibaba’s AliExpress of trying to track web users by playing sounds through browsers vulnerable to audio fingerprinting. The software engineer discovered the issue late last week after investigating why his Bluetooth headphones stopped playing music whenever he visited the AliExpress website. «Shortly after loading the AliExpress homepage, audio from my phone would stop playing,» Callaghan said. «Closing the AliExpress tab fixes it immediately. Muting the tab/Firefox/Windows does not help, and there is no visible video, music, or other media playing on the page.» Firefox issued a statement on X saying its anti-fingerprinting technology blocks Alibaba’s tracking technique. Tom Ritter, who leads security efforts for Mozilla Firefox, said: «We made the WebAudio constant in Firefox 118 three years ago as part of our initial round of Fingerprinting Protection features. This eliminated most of the differences.»
  • Anthropic Expands Claude Mythos 5 Access — Anthropic said it’s working with cybersecurity technology and services partners to integrate Claude Mythos 5 into their products and services to secure their software. «Customers on Claude Enterprise plans can now run our most capable model in Claude Security, using it to scan their codebases for security vulnerabilities and suggest patches,» it said. «Our new Defender Advantage Fund (0xDAF) will provide $35 million in credits to organizations working to patch vulnerabilities in open-source projects, automate parts of the process of scanning and patching open-source software, and experiment with new security approaches.»
  • Agentic Source Code Review — Google said it uses what’s called the Agentic Vulnerability Discovery Harness (AVDH) to «rapidly analyze code and find exploit paths during proactive reviews, penetration tests, red team operations, and incident response engagements.» The development comes amid increasing adversarial misuse of AI. The tech giant said its use of AVDH over the past 10 months has led to the discovery of over 100 true-positive critical vulnerabilities, including critical flaws in Drupal (CVE-2026-13242 and CVE-2026-55803). The system outlined by Google is very similar to Microsoft’s MDASH.
  • 768 Leaked Corporate AWS Keys Hold Full Admin Rights — Truffle Security’s scan has verified 64,024 unique AWS key pairs across 431,875 public findings, including git history, Hugging Face datasets, Docker images, package registries, CI logs. These keys surfaced publicly between August 2022 and August 2026. Of these pairs, 10,616 came with complete credentials. According to Truffle Security: «»88% still authenticate. 768 of the live ones belong to a company and carry full control of its AWS account: 526 root keys plus 242 IAM users holding AdministratorAccess. The median live leaked key is five years old and has never been rotated.»

Conclusion

This week’s useful reminder: attackers rarely need everything to fail. One exposed service, one trusted shortcut, or one overlooked dependency can be enough to get started.

So the better question is not “what’s the next big threat?” It’s “what are we still assuming is safe?” That usually finds the problem sooner.

VMware Exploits, Windows 0-Day, MCP Attacks, Browser Hijacks and More – CYBERDEFENSA.MX

The expensive attacks are not always the clever ones.

This week had plenty of proof. Exposed services got hit, old bugs found fresh use, browser sessions became attack paths, and supply-chain problems kept spreading farther than the original compromise. A lot of it came down to access that was already there and defenses that assumed nobody would look too closely.

So, nothing magical. Just a lot of small openings turning into bigger problems. Here’s what stood out.

⚡ Threat of the Week

Suspected China APT Behind Exploitation of New VMware Flaw — A suspected China-nexus APT is assessed to be behind the exploitation of a newly patched security flaw in VMware vCenter. The attacks involve the exploitation of CVE-2026-59310 (CVSS score: 9.8), a severe directory-traversal vulnerability in the VMware vCenter server that could be weaponized by a malicious actor to execute arbitrary code. In at least one compromised instance, the attacks led to the deployment of a backdoor and. a reverse SSH binary, with the attack ultimately leading to the deployment of Babuk-derived ransomware. «Based on the case we investigated, however, we do not believe ransomware was necessarily the primary objective,» QUIRSO said. «To us, its deployment looks more like a smoke screen intended to distract from the underlying intrusion and, importantly, hinder subsequent forensic analysis by encrypting evidence. We therefore see the ransomware activity in this case as potentially serving the broader intrusion rather than being its ultimate objective.»

🔔 Top News

  • Apple macOS Flaw Exploited to Drop Crypto Miner — A recently patched security flaw in Apple macOS has come under active exploitation in the wild to deploy a cryptocurrency miner. The vulnerability in question is CVE-2026-65400 (CVSS score: 9.8), a critical authentication issue impacting the Screen Sharing component that could allow an attacker already on the network to authenticate to the built-in remote desktop feature service without valid credentials. The shortcoming was addressed as part of an emergency update in macOS Tahoe 26.6.1, macOS Sequoia 15.7.9, and macOS Sonoma 14.8.9 earlier this month. The Netherlands National Cyber Security Center (NCSC-NL) said it received a report indicating active abuse of the vulnerability across multiple systems on which port 5900 was accessible from the internet. «In all these cases, root had gained access to the affected system and placed a Monero crypto miner,» the agency said.
  • Lazarus Exploits New Windows 0-Day — The North Korean threat actor known as Lazarus Group has been attributed to the zero-day exploitation of a newly patched security flaw impacting Microsoft Windows to deliver a never-before-seen backdoor targeting defense and aerospace companies across France, Germany, Brazil, and India. The activity is part of Operation Dream Job, a long-running cyber espionage and social engineering campaign orchestrated by Pyongyang-backed hackers to target professionals worldwide with fake-but-compelling job offers to steal sensitive data and install malware. The attacks have been found to exploit CVE-2026-68820 (CVSS score: 7.0), a privilege escalation flaw affecting Windows Ancillary Function Driver for WinSock («AFD.sys») that was patched by Microsoft as part of its Patch Tuesday updates for August 2026. The attacks have been observed to deliver ForestTiger and a new backdoor called Troy.
  • GeoServer Patches Critical Flaw Under Attack — GeoServer has released patches for a critical SQL injection vulnerability that can lead to remote code execution (RCE). The issue, which has yet to be assigned a CVE identifier, has been patched in versions 3.0.1, 2.28.5, and 2.27.6. Per watchTowr, the vulnerability witnessed active exploitation within hours of public disclosure and that it has seen hundreds of attempts originating from a small pool of IP addresses. GeoServer project maintainers told The Hacker News that the flaw was responsibly disclosed and was scheduled to be addressed in their regular release cycle, when details of the flaw became public knowledge last week.
  • Amnesia Stealer Goes Beyond Data Theft — A newly discovered macOS stealer family called Amnesia Stealer has been found to target macOS users via ClickFix attacks. The malware, besides stealing data from 16 Chromium-based web browsers as well as other sensitive information, such as passwords, cryptocurrency wallets, Apple Notes, documents, and iCloud Keychain data, includes a streaming module that allows the attacker to interactively control the victim’s web browser. One notable aspect of the stealer is its ability to copy the victim’s Chromium profile, including its authentication state, and load it into a headless browser on the infected system to access the authenticated sessions. The streaming module can duplicate user profiles in Chromium-based browsers, including Google Chrome, Microsoft Edge, Vivaldi, Arc, Opera, and Brave, and establish a WebSocket channel that connects to the operator’s relay and receives commands, such as navigation and mouse clicks. The remote-control component is built using the Chrome DevTools Protocol (CDP). A second WebSocket channel connects to the local headless Chromium instance. «The operator receives a live screencast of the session at around 3fps and can drive it with a full input set: keyboard, mouse, scroll, navigation and tab management,» Jamf said. «In effect, the remote_stream command turns an infected host into a live, operator-driven browser running the victim’s authenticated sessions, which is a materially different level of access from file collection.» Amnesia Stealer is the first documented macOS malware to combine a cloned Chromium profile with CDP-based, real-time remote control to allow interactive access.
  • From GhostCommit to GhostSplice — A new attack technique called GhostSplice can sidestep guardrails built around AI coding assistants and parse malicious requests that are split and hidden in a different channel, such as an MCP tool description, a tool result, and a sampling message. Each of these requests is perfectly benign on its own and processed by the assistant without refusing them. «The entire attack rests on the following fact: All three of the tool channels discussed above, together with your files and your own chat, pour into one block of the assistant’s memory,» ASSET Group said. «There does not exist any marking that separates the content based on its respective source. Therefore, the assistant reads it all as a single page.» The attack has been described as a case of cross-channel trust fragmentation. «Due to the absence of a wall between content received from different sources (e.g., different tool channels), the attacker never needs any single one of this content to look dangerous. Instead, the idea is to embed a harmless piece in each source, and the assistant stitches them back into one instruction.»
  • Using Chrome DevTools Protocol for Data Theft — New research from SpecterOps detailed a post-exploitation technique that allows Chromium’s CDP protocol to be enabled inside a live Google Chrome or Microsoft Edge process on Windows with an end goal to steal cookies, saved data, and authenticated browser sessions provided an attacker already has code execution permissions on the compromised host. «Cookie protections like ABE and device-bound session cookies make it harder to steal and replay session material, but they do not remove the value of an authenticated browser to adversaries,» SpecterOps said. «Once CDP is enabled inside a Chromium browser, an operator can use the browser context to sidestep those replay protections, access authenticated applications, and collect saved data. Enabling CDP is a reminder that the next evolution of cookie theft may not require stealing the cookie DB and ABE key at all.»

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-68820 (Microsoft Windows), CVE-2026-58231 (SAP Commerce Cloud), CVE-2026-48362, CVE-2026-71398, CVE-2026-27302 (Adobe), CVE-2026-20349 (Cisco Secure Firewall Adaptive Security Appliance Software and Secure Firewall Threat Defense), CVE-2026-53413, CVE-2026-53414, CVE-2026-53415 (Zoom), CVE-2026-65400 (Apple macOS), CVE-2026-20337, CVE-2026-20338, CVE-2026-20339, CVE-2026-20345, CVE-2026-20346, CVE-2026-20347, CVE-2026-20348 (ClamAV), CVE-2026-18412 (OpenCart), CVE-2026-66147, CVE-2026-66145 (SonicWall), CVE-2026-6726, CVE-2026-6727 (Trusted Platform Module 2.0 reference implementation), CVE-2026-26035, CVE-2026-70468, CVE-2026-70465 (Fortinet), CVE-2026-65640 (WordPress), CVE-2026-65321 (PyAthena), CVE-2026-43637 (Cornac), CVE-2026-63720 (datamodel-code-generator), an SQL injection vulnerability in GeoServer, and multiple vulnerabilities in WireShark..

🎥 Cybersecurity Webinars

  • How to Control the Open-Source Security Debt Created by AI Coding Tools → Learn how AI coding tools are expanding unvetted open-source use, accelerating vulnerability backlogs, and weakening existing governance. This webinar shows how to measure the resulting remediation debt, connect it to breach, audit, and productivity risks, and identify which governance models can contain it without slowing development.
  • AI Can Build Exploits in Minutes. Can Your Security Team Keep Up? → AI is collapsing the time between vulnerability disclosure and attack. Advanced models can now uncover flaws, generate working exploits, and chain them into complete attack paths at machine speed. This webinar presents a practical framework for gaining the visibility, context, and response speed needed to investigate and stop threats before attackers pull ahead.

📰 Around the Cyber World

  • Security Flaw in FileRun — VulnCheck disclosed details of CVE-2026-14863 (CVSS score: 8.7), a high-severity operating system command injection flaw in FileRun that could lead to remote code execution. «FileRun’s thumbnail extractors build shell commands by pasting the uploaded file path into a double-quoted string and handing it to exec(), and the filename sanitizer lets $() through, so a file named $(payload).mp4 runs its payload the moment a thumbnail is generated,» security researcher Valentin Lobstein said. «Any authenticated user with upload permission gets code execution; when a public file request weblink exists, so does anyone who knows its token, no account required.» The issue, which affects versions up to and including 2026.2.0, has been fixed in 2026.2.1.
  • ClickFix Leads to ACR stealer and GhostPipe — ThreatLocker disclosed an attempted ClickFix attack that employs embedded scripts, steganographic payload extraction, and obfuscation to deploy an advanced iteration of ACR stealer and a secondary payload dubbed GhostPipe. The ClickFix attack originated from a fake CAPTCHA prompt being served on a compromised domain, resulting in the execution of a PowerShell command that downloads an MP3 file, which is then executed using MSHTA to launch a VBScript that’s responsible for running intermediate payloads designed to gather system information and extract from a remotely hosted JPG file a PowerShell script. The script serves as an in-memory module shellcode launcher to deploy ACR Stealer. The malware also contacts a C2 server to fetch secondary payloads, including a PowerShell script called GhostPipe. «This seemingly unknown script performs a proxy-based AiTM attack with the sole purpose of stealing Google logins,» ThreatLocker said. «The methods used are comprehensive and inherently support relaying MFA to successfully capture credentials.»
  • Flaw in Citrix NetScaler — Citrix appears to have silently addressed a heap overflow vulnerability in NetScaler that can be exploited to achieve remote code execution. The issue was patched as part of updates released towards the end of June 2026. watchTowr said the vulnerability likely corresponds to CVE-2026-8452, which has been described as a memory overflow vulnerability that could lead to unpredictable or erroneous behavior and denial-of-service when the appliance is configured as a Gateway or an AAA virtual server. The vulnerability, per the threat intelligence company, can be turned into code execution to drop a PHP web shell that can survive the NetScaler packet engine being respawned, and ultimately execute commands with root privileges. Shortly after details of the flaw became public, Defused Cyber said it observed active in-the-wild exploitation efforts two calendar days later.
  • Ethereum Malware Loader Goes After Portuguese-Speaking Users — Portuguese-speaking users are the target of a malware loader that uses the EtherHiding technique to dynamically locate attacker infrastructure and distribute additional payloads. «The multi-stage infection chain combines obfuscated JavaScript, Node.js, DLL side-loading, and a malicious Chromium browser extension capable of targeting Chrome and Microsoft Edge to collect cookies and web storage, capture screenshots, monitor browser activity, and receive remote commands,» WatchGuard Threat Lab said. The Israel National Digital Agency (INDA), in its own analysis of EtherHiding, said the technique has been used as a delivery backend, a C2 channel, a victim database, and skimming infrastructure. In another interesting twist, attackers have been found to shift to the BNB Smart Chain testnet, essentially eliminating gas fees and making the whole operation free. «Because writes there are free, unlimited, and leave no financial trail, recent reporting has found malware command-and-control backends running entirely on a testnet,» INDA said.
  • Thousands of Exposed Fuel Gauges Dropped from the Internet — BitSight said it observed a dramatic drop in internet-exposed Automatic Tank Gauge (ATG) systems in the U.S., with the number declining by more than half. «From March to June, there was over a 55% drop in exposed IP addresses,» it said. «Globally, exposure fell 49% from that same March peak, with the U.S. accounting for most of the decline. For ten months, from June 2025 through March 2026, the U.S. held a band of roughly 4,300 to 5,300 unique exposed IPs, averaging 4,815 across 2025. Then April fell 27.6% in a single month, May fell another 31.8%, and June continued down. By June, the exposed population was 56% below the March peak.»
  • Phantom Enigma Campaign Targets Brazil — An active PhantomEnigma campaign has been observed abusing compromised government infrastructure and fake police-themed documents to target banking and public-sector organizations in Brazil. The phishing messages are presented as official notices and bypass email security filters to deliver a modular Node.js backdoor that collects system data, sets up persistence, and connects to rotating C2 infrastructure. It can also execute JavaScript or deliver stealers, loaders, RMM software, and other malware. Some aspects of the activity overlap with prior reports from Positive Technologies.
  • F.B.I. Agent Charged With Unauthorized Crypto Withdrawals — An F.B.I. counterintelligence agent has been charged with illicitly obtaining about $1 million worth of cryptocurrency, largely through unauthorized withdrawals from a criminal target overseas. According to The New York Times, the agent claimed he had begun taking the money in late 2024 or early 2025, and made 10 or 12 withdrawals altogether by making use of a seed phrase to the suspect’s account that the F.B.I. had obtained during its investigation of the individual.
  • Ukraine Dismantles Fraudulent Call Centers — Ukrainian authorities disrupted 94 fraudulent call centers during a nationwide operation that involved more than 400 searches and the seizure of thousands of computers, phones, and SIM cards. Per the Ukrainian police, the call centers were associated with schemes relating to callers impersonating bank employees, fraudulent investment services, cryptocurrency platforms, and attempts to gain remote access to victims’ devices or trick them into handing over sensitive data under the guise of suspicious transactions. Some cybercriminals collected personal information about prospective victims and shared or sold those records to other operations. «Call centers were staffed by administrators, operators, and other participants in the schemes, and ready-made conversation scripts, databases of potential victims, special software, and tools for hiding and further withdrawing funds were used,» the police said. During the probe, 3,336 pieces of computer equipment, 1,346 phones, over 5,200 SIM cards, 90 bank cards, access to 20 crypto wallets, and 22 cars were seized. About $2 million, €64,000, cash in hryvnias, a kilogram of bank gold in bars, and jewelry were also confiscated.
  • North Carolina Man Sentenced for Cyber Extortion Scheme — Cameron Curry, 27, of Charlotte, North Carolina, was sentenced to 24 months in prison for carrying out an «extensive cyber extortion scheme» against an unnamed D.C.-based international technology company. In March 2026, Curry was convicted of six counts of transmitting or willfully causing interstate communications with the intent to extort a victim company. «Curry misused his position to access the victim company’s personnel and other sensitive corporate records, which he then used to carry out the cyber extortion scheme,» the U.S. Justice Department said. «Curry hatched his extortion scheme after he learned that his contract was not going to be renewed and that he would no longer be employed by the company.»
  • ExfilSquad’s Access to Data from 13 Organizations — A new analysis of data samples published by the ExfilSquad data extortion group has confirmed «they have access to sensitive data.» Fortra said the breaches were most likely limited to unauthorized access of D365 instances. «The leading theory on the initial attack vector that enabled exfiltration is misconfigured Microsoft Power Page portals that allowed for public read access,» it said. «The observed leaked data formats are consistent with Microsoft Dataverse exports, suggesting unauthorized read access may have been achieved, and victims found by crawling for misconfigured Microsoft Power Portals or other enumeration techniques.»
  • OpenAI Rolls Out Computer History in ChatGPT — OpenAI replaced Chronicle, which builds memories from screen captures to make ChatGPT and Codex more aware of context, with Computer History. «Computer History turns your activity across apps and websites into memories and a timeline that ChatGPT and Codex can reference,» OpenAI said. «You can ask natural questions about recent work, pick up where you left off, understand patterns in how you work, and turn repeated workflows into skills or automations.» Computer History is off by default for ChatGPT Pro, Business, and Enterprise users in the ChatGPT desktop app on macOS. The feature is reminiscent of Microsoft’s controversial Recall, which attracted scrutiny for relying on periodic screenshots to capture and index relevant information. Unlike Chronicle, which also used screenshots, Computer History relies on capturing interactions (e.g., clicks, typing, keyboard shortcuts, app switches, and context) to allow the AI to understand user workflows. «Computer History records interaction events and does not capture your screen or audio,» OpenAI said. «You control which apps and websites contribute, can see and pause collection from the macOS menu bar, and can inspect or delete your history at any time.» That said, it’s worth emphasizing that Computer History files can contain sensitive information. «They are not encrypted by Computer History, and other programs running as your macOS user may be able to access them,» OpenAI cautions. «Protect your Mac account and exclude sources you do not want included.» OpenAI also warned that Computer History increases the risk of prompt injection from content in apps and websites, as the AI system can follow instructions when visiting a website containing malicious instructions. Temporary interaction event files are retained for up to 48 hours before they are deleted. However, they can be used to create memory files that can remain for extended periods of time until users explicitly delete or clear them.
  • China-linked LightSpy Activity Detected in Over 13 Countries — The modular implant known as LightSpy has evolved into a broader surveillance tool that’s in use in more than 13 countries and regions, including Singapore, Hong Kong, the Netherlands, Pakistan, Japan, China, Malaysia, Germany, the U.S., Thailand, Indonesia, South Korea, Austria and Turkey, Arctic Wolf Labs said. This includes previously unreported router-focused capabilities along with live router implants in Europe and Africa. «The findings expand the potential impact of the surveillance framework beyond individual devices: router access can provide visibility into every device connected to a home or office network and may persist after phones are replaced, devices are factory-reset, or operating systems are upgraded,» a spokesperson for the company said. LightSpy infrastructure spans several countries, including 117 servers and 35 domains impersonating Asian electronics manufacturers and router-management services. Evidence indicates that LightSpy functions as a commercialized surveillance platform, with customer branding, billing functionality, and a demonstration environment used to market the framework to prospective buyers. The platform is assessed to be the work of a Chinese contractor after one of the operators used the LightSpy administrator’s panel to place an order with KFC using their real name and office address.
  • Trivy Supply Chain Attack Exposed 2,500+ Companies — A new analysis from SOCRadar has revealed that 95% of organizations impacted by the LiteLLM supply chain attack earlier this year were exposed before, coinciding with the compromise of the Trivy scanner. «Organizations did not need to install LiteLLM directly to be exposed,» the cybersecurity company said. «The package could arrive through frameworks such as DSPy, MLflow, CrewAI, OpenHands, and Arize Phoenix, while its payload executed at Python startup without requiring a LiteLLM import.» The incident was attributed to a threat actor known as TeamPCP.
  • Massive Azure Exfiltration Campaign Exposes Millions of Enterprise Records — An active Microsoft Azure exfiltration campaign is being driven by a threat actor named «TheHatman,» who has «flooded» cybercrime forums with enterprise employee databases. The data is said to have been downloaded directly from the organizations’ Azure/Entra portals using compromised credentials, although the exact intrusion vector remains unknown. The campaign impacts multiple global enterprises across IT services, hospitality, telecommunications, retail, and logistics. Some of them include McDonald’s, TCS, Vodafone, HCL Technologies, Kyndryl, Gap, Hexaware, and Wyndham Hotels. «Judging by the massive size of the organizations impacted, it appears highly likely that this campaign originates from targeted exploitation of Infostealer infections rather than a systemic zero-day vulnerability in Azure,» Hudson Rock said.

Conclusion

That’s the week. Some attacks needed a real exploit. Others just needed an exposed system, a stolen login, or one weak link buried in the stack.

The useful part is knowing which kind you’re dealing with before it becomes your problem. Patch what matters, close what should not be public, and keep an eye on the boring stuff. It keeps winning.

AI Goes Rogue, Metabase 0-Day, MCP Supply-Chain Attacks, and Router Backdoors – CYBERDEFENSA.MX

A lot of security problems still begin with someone doing a completely normal thing. Cloning a repo. Answering a call. Leaving a box exposed. Trusting the default.

That pretty much covers the mood this week. Old bugs are back, supply chains are getting stranger, and some exploit paths are so short you wonder what was supposed to stop them in the first place.

That’s only part of it. Here’s everything else that made the Monday recap.

⚡ Threat of the Week

Anthropic’s Model Attempts to Poison Open-Source Project — A new evaluation conducted by the U.K. AI Security Institute (AISI) found that AI models with access to the internet reached out into the real world to target individuals and organizations autonomously across 10 of the total of 122 runs. Of 19 such actions recorded, 17 originated from Anthropic’s Mythos 5 and the remaining two involved OpenAI’s GPT-5.6-Sol with cyber classifiers. In the most serious case, Anthropic’s Claude Mythos 5 spent 34 hours trying to get a malware dropper merged into a real open-source project and engaged in social engineering by creating fake online identities and using them to pressure the project’s maintainer to approve the code. Ultimately, a human maintainer caught and refused to approve the malicious code. «These attempts were unsuccessful, and our investigations have not evidenced any resulting real-world harm,» AISI said. But this is the first time we have seen risks around autonomy and deception manifest this clearly, without specific prompting, in the real-world.»

🔔 Top News

  • Metabase 0-Day Exploited in Attacks — Metabase warned that a maximum-severity security flaw impacting its business intelligence and data visualization software package has been exploited in the wild as a zero-day. The vulnerability (CVSS score: 10.0), which does not carry a CVE identifier, allows an unauthenticated remote attacker to inject arbitrary SQL into the Metabase application database, enabling them to gain administrator access to the instance. Armed with the elevated access, the attacker can change the application configuration, steal stored credentials for the connected databases, read any data accessible through those connections, and export data. One of the companies that has been affected is Framework.
  • New Interrupt Injection Attack Bypass Spectre v2 Defenses on Intel and AMD CPUs — A group of researchers demonstrated a way to bypass defenses for the Spectre vulnerability impacting modern CPUs. «The defenses work by wiping or isolating the processor’s prediction machinery, removing anything an attacker might have planted,» MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL) said. «The catch […] is that the wipe and the moment the predictions get used can’t happen at the same instant. There is always a gap — sometimes only a handful of instructions wide. Anything that runs in that gap can dirty the machinery all over again. The researchers call this class of attack TONTOU.» The study found a reliable way to get code into that gap using a technique called Interrupt Injection to ultimately pull secrets out of memory.
  • New CSS Attacks Can Break Webmail Defenses — New research demonstrated at the Black Hat conference last week detailed attack chains spanning Microsoft Outlook, Gmail, Fastmail, Proton Mail, Yahoo Mail, and AOL Mail that can capture passwords, take over third-party accounts, leak tokens, hijack trusted UI actions, and manipulate AI tools that read email. «Trouble is you can create discrepancies between what the sanitizer thinks is safe and what the browser actually renders,» PortSwigger said. «Some webmail clients go a step further by letting the browser parse the HTML and CSS first, then filtering the browser’s interpreted output rather than the original source. Yet even this can be mutated into something malicious.»
  • UNC6671 Vishing Attacks Target Financial Firms — A recent wave of cyber attacks targeting financial services, private equity, and professional services has been attributed to a data extortion group known as UNC6671. The attacks employ voice phishing to target enterprise employees and trick them into visiting spoofed login portals where adversary-in-the-middle (AitM) infrastructure intercepts credentials and multi-factor authentication (MFA) tokens. The threat actors then leverage the captured data to establish session persistence and deploy automated Python and PowerShell scripts for data exfiltration from enterprise cloud environments and SaaS applications, including Microsoft 365 and Okta. UNC6671 has diversified its operations across multiple extortion brands including Redact, Pink (aka CL-CRI-1147), Helix, and Falcon (aka CL-CRI-1182). UNC6671 was previously said to have operated under the BlackFile (aka CL-CRI-1116) brand, targeting organizations via vishing and SSO compromise, before it was retired on May 11, 2026.
  • Chinese-Made Zbtlink Routers Ship With Backdoor — An analysis of firmware associated with Chinese router manufacturer Zbtlink has unearthed a factory-shipped backdoor that’s designed to phone home and run commands received from the server. The backdoors are designed such that they start automatically and attempt to beacon to Chinese command-and-control (C2) infrastructure as often as every 35 seconds. The backdoor is implanted in at least 20 router models. In response to the findings, Zbtlink reiterated that the «remote management component» is used only for after-sales technical support and to «assist customers with device troubleshooting and configuration only upon their explicit request and authorization.» The company also said it has never been used for unauthorized access. The company also said it’s developing and releasing firmware updates to address the issue.

‎️‍🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first — CVE-2026-34348, CVE-2026-18497 (stb TrueType), CVE-2026-63508, CVE-2026-56162, CVE-2026-65667, CVE-2026-50515, CVE-2026-62830, CVE-2026-59115, CVE-2026-50481 (Microsoft Windows), CVE-2026-64638 (WordPress), CVE-2026-64564 (Linux SCTP), CVE-2026-56181 (Microsoft Windows NAT), CVE-2026-63913 (Linux), CVE-2026-64561 (Linux kernel), CVE-2026-20303, CVE-2026-20304, CVE-2026-20310, CVE-2026-20267, CVE-2026-20272 (Cisco), CVE-2026-18830 (AWS AgentCore), CVE-2026-18236 (Google ADK), CVE-2026-64650, CVE-2026-64651 (Vercel), CVE-2026-41679, GHSA-x8hx-rhr2-9rf7 (Paperclip), CVE-2026-58073, CVE-2026-58072 (Veeam), CVE-2026-16498, CVE-2026-16496, CVE-2026-14869 (HashiCorp), CVE-2026-15307 (GeoDjango), CVE-2026-64531 (Linux kernel Open vSwitch), CVE-2026-18577, CVE-2026-18556 (N-able N‑central), CVE-2026-59774 (Gitea), CVE-2026-58048 (cPanel), CVE-2026-17583 (Thermo Fisher Scientific), CVE-2026-8496 (Alinto SOGo), CVE-2026-65400 (Apple macOS Tahoe, macOS Sequoia, and macOS Sonoma), CVE-2026-19137, CVE-2026-19149, CVE-2026-19154, CVE-2026-19157, CVE-2026-19170, CVE-2026-19172 (Google Chrome), CVE-2013-3821 (Oracle PeopleSoft), CVE-2025-8943 (Flowise), and an SQL injection in Metabase.

🎥 Cybersecurity Webinars

  • Build a Security Strategy for AI-Speed Development → AI is pushing software delivery far beyond the pace traditional security programs were designed for. This session shows security leaders how to govern AI-built software, reduce risk without slowing teams down, and build controls that scale with machine-speed development.
  • Benchmark Your AI Coding Risk Against 300 Security and Engineering Leaders → AI coding is bringing more unvetted open source into production and expanding remediation debt. This session gives security and engineering leaders peer benchmarks, a data-backed framework for measuring business impact, and a clear view of which governance models are actually reducing risk.
  • Build a Security Operations Strategy for Machine-Speed Attacks → AI can now find vulnerabilities, generate exploits, and build attack paths at machine speed. This session gives security leaders a practical framework to assess AI threat readiness, improve attack-surface visibility, and accelerate investigation and remediation before existing processes become the bottleneck.

📰 Around the Cyber World

  • New Shai-Hulud Version Weaponizes the MCP Registry — A new version of the Shai-Hulud worm spread through the open-source ecosystems is equipped to deliver the payload via the Model Context Protocol (MCP) Registry. «While earlier iterations of Shai-Hulud tampered with local AI coding client configs, this marks the first time we observed a Shai-Hulud payload being delivered directly through the official Model Context Protocol (MCP) Registry (registry.modelcontextprotocol.io),» OX Security said. The attack works like this: the npm and PyPI package linked by the MCP server is completely clean, but opening or cloning the linked MCP server GitHub repository («jUXTAPOSITION1/V.A.P.E») inside Claude Code or VS Code triggers the malware, leading to the collection of developer tokens, cloud credentials, and session keys. The worm spread through 440 unique npm packages.
  • China Launches Review of Palo Alto Networks — China’s Cyberspace Administration (CAC) has announced it’s conducting a review of Palo Alto Networks’ products. «In order to ensure the safe and stable operation of critical information infrastructure, prevent hidden risks of network security, and safeguard national security, in accordance with the National Security Law of the People’s Republic of China and the Cyber Security Law of the People’s Republic of China, the Network Security Review Office implements network security review of products sold by Palo Alto in China in accordance with the ‘Network Security Review Measures,’» the CAC said.
  • Papyrus Uses Fake Novel Reading Apps for Ad Fraud — A new mobile ad fraud scheme dubbed Papyrus has been observed leveraging a «cluster of novel-reading applications that monetize users’ reading sessions by running hidden browser activity in the background,» Integral Ad Science said. «While users believe they’re simply reading a story, the apps are secretly using their phone to visit websites, generate clicks, and create fake engagement behind the scenes. The apps present themselves as entertainment products built around long-form fiction and serialized stories, but IAS observed them covertly navigating to web domains under the direction of command-and-control infrastructure.» Papyrus is built around BootNova, an orchestration layer that controls hidden browser activity inside the app. When the app runs, BootNova contacts remote command-and-control infrastructure for configuration. The remote configuration can control enablement, timing, geographic targeting, retry behavior, the number of WebViews to run, destination URLs, and the interaction logic applied to those pages. Papyrus has been linked to more than 800 domains and nearly 8,000 unique hostnames.
  • Estimated $30M Stolen in Violent Crypto Attacks in 2026 — An estimated $30 million is said to have been stolen in violent «wrench attacks» in 2026, according to Chainalysis. «Home invasions now account for 37% of incidents in 2026, up from 26% in 2023,» it said. «Kidnappings have remained relatively stable year-over-year (YoY) in terms of share of total attacks.» In contrast, annual value stolen in violent attacks peaked at $58 million in 2025.
  • 26 Ransomware Attacks Per Day in July 2026 — According to Comparitech, July 2026 saw nearly 26 ransomware attacks per day, up from 22 per day in June. The number of ransomware attacks jumped from 668 in June to 799 in July. «The education sector saw a significant increase (up 44%), as did finance companies (up 71%), tech firms (up 62%), and businesses operating within the healthcare sector, e.g. pharmaceutical manufacturers and medical billing providers (up 46%),» Comparitech said. The most prolific groups were The Gentlemen (135), Qilin (125), DragonForce (41), INC (36), and CRPx0 (33).
  • Device Code Phishing Evasion Techniques Detailed — Palo Alto Networks Unit 42 said it identified four evasion techniques that are currently being used in device code phishing campaigns. This includes CAPTCHA gates, multi-step flows that go through multiple SaaS hosting platforms separating the initial link from the phishing content to evade URL reputation checks, blob URL delivery, and the use of Cyrillic characters in place of Latin letters, zero-width spaces, and strings inside tags to break content-based detection.
  • From LLMJacking to Token Jacking — A growing number of security incidents involving AI token jacking have resulted in financial losses for victims. «The financial loss comes from criminals gaining access to API keys used by legitimate developers for access to popular AI platforms,» Unit 42 said. «The unrelenting frenzy of AI adoption and soaring costs of model access are converging into an irresistible opportunity for cybercriminals. Premium pricing on scarce AI processing power means stolen access via tokens can generate a quick and easy profit for attackers. Complex, patchwork billing management and limitless scaling by default can lead to massive financial losses in short periods.»
  • ScarCruft Leverages RokRAT in New Attacks — Spear-phishing emails disguised as materials for actual academic events and seminars are being used to deliver RokRAT, a remote access trojan linked to a North Korean group known as ScarCruft. «Although the file was disguised as a PDF, it actually delivered a malicious ISO file through a cloud storage link,» Genians said. «The ISO contained an executable disguised as a PDF document, using the ‘.pdf,’ ‘.pif’ extension to induce the user to run it. The attack loaded the shellcode payload into memory and injected a RokRAT variant into a process.»
  • Kimsuky Uses New Gomir Variant — Speaking of North Korean threat groups, the threat actor tracked as Kimsuky is said to have gained control of internet-facing servers through vulnerability exploitation and spear-phishing and deployed a new variant of a backdoor called Gomir, a Linux variant of the Windows-based GoBear backdoor. «Kimsuky developed Gomir variants with significantly altered C2 communication methods to evade detection, including leveraging Google Drive as a C2 channel and implementing a new custom protocol,» ENKI said. In at least one case in December 2025, the threat actor has been found deploying HttpTroy, which is then used to install additional tools, including DWAgent and a proxy tool. Kimsuky has also been observed setting up local large language model (LLM) environments using Ollama, GPT4All, and Msty to augment its operations and target foreign diplomatic missions, as well as the military, security, and virtual asset sectors. The attacks have leveraged Git-based repositories as C2 and distribution channels for encrypted AsyncRAT payloads. The activity has been codenamed Operation GitPower, citing similarities with FlowerPower. Last year, the group was tied to campaigns that involved abusing OpenAI’s ChatGPT to forge deepfake military ID cards in a spear-phishing campaign against South Korean defense-affiliated entities and other individuals focused on North Korean affairs, such as researchers, human rights activists, and journalists.

Conclusion

Maybe the real problem is not that security keeps failing in surprising ways. It’s that the “surprising” part usually disappears the moment someone shows how little it took.

That’s worth remembering. Attackers do not need perfect conditions. They just need one assumption nobody checked, one shortcut nobody revisited, or one old weakness that quietly stayed useful.

Rogue AI Models, $88M Bitcoin Theft, Water-System Attacks and Dangling DNS Hijacks – CYBERDEFENSA.MX

This week kept coming back to permission. A model crossed a boundary. A wallet trusted bad randomness. Webmail kept an intruder around. Public systems, package feeds, hotel networks, and login flows all gave away more than intended.

Some of it was clever. Most of it was just access left lying around: old bugs, exposed gear, poisoned dependencies, weak defaults, and tooling that moved from forum chatter to real targets.

The full weekly recap report follows.

⚡ Threat of the Week

Anthropic Disclosed its Models Targeted 3 Organizations – Anthropic revealed that three of its models, including Claude Opus 4.7, Mythos 5, and an unnamed research model, breached three unnamed organizations during cybersecurity testing without its knowledge. The AI firm said the earliest incidents date back to April 2026, adding it made the discoveries after launching a «large-scale retrospective review» in response to the recent Hugging Face incident. «After reviewing 141,006 evaluation runs where Claude could have obtained internet access, we identified three incidents in which a model accessed the internet from within or while interacting with the evaluation environment of Irregular, one of our third-party evaluation partners, and then gained unauthorized access to the production infrastructure of three different organizations,» it said.

🔔 Top News

  • Coldcard Hardware Wallet Flaw Linked to $88.6M Bitcoin Theft – A vulnerability in Coldcard hardware wallet firmware is said to have been exploited to steal an estimated $88.6 million in Bitcoin from thousands of wallets whose seed phrases were generated using a flawed random number generator. «Coldcard firmware contains an RNG integration error that causes ngu.random to use MicroPython’s deterministic Yasmarang fallback instead of the STM32 hardware RNG,» Square Engineering said. «This does not mean every remote attacker can immediately recover every seed. Practical cost depends on available UID information, boot timing, prior RNG calls, and derivation cost.»
  • Russian Hackers Exploit Microsoft OWA Flaw to Maintain Mailbox Access – Russian threat actors exploited a security flaw in Microsoft Outlook Web Access (OWA), to target U.S. and European government entities, as well as the telecommunications, financial, hospitality, and aerospace sectors. The activity, which began on July 22, 2026, involves the weaponization of CVE-2026-42897 (CVSS score: 8.1), a cross-site scripting (XSS) vulnerability in OWA. It was flagged by Microsoft as having been exploited in attacks as far back as May 2026. The activity has been attributed to Laundry Bear. The new wave of exploitation revolving around CVE-2026-42897 culminates with the deployment of a previously unknown JavaScript browser-based implant codenamed OWAReaper that’s specifically built for persistent access within Microsoft’s webmail client.
  • Critical Rails Flaw Leads to Arbitrary File Read – Ruby on Rails shipped patches for a critical Active Storage vulnerability (CVE-2026-66066, CVSS score: 9.5) that could let unauthenticated attackers read arbitrary files from application servers through crafted image uploads. The flaw can be exploited to expose Rails process environment and secrets such as secret_key_base, master key, database passwords, cloud storage credentials, and API tokens, which may enable remote code execution or lateral movement into connected systems. CVE-2026-66066 is exploitable when libvips is used, enabling an attacker to upload a specially crafted image to a vulnerable application and read arbitrary files on the server. A key prerequisite for the attack is that the server must allow image uploads from untrusted users. Additional details of the flaw have been released by the Rails team, along with tools to help assess vulnerable applications. «Because this vulnerability requires no authentication and targets the default image processor in modern Rails environments, it is essential to apply vendor patches and rotate secrets immediately,» Akamai said.
  • Coordinated Attacks Target 30+ Minnesota Water Systems – A coordinated cyber attack campaign targeted over 30 water systems in Minnesota on July 26 and 27, 2026. «The nature and extent of the impact varied by system, and the investigation is still determining how many experienced operational disruptions,» Minnesota IT Services (MNIT) said. The activity has not been officially attributed to any known threat actor, although Iranian threat actors have been previously implicated in similar attacks targeting water facilities in the U.S. «At this time, there are no active requests from Minnesota communities for residents to modify their drinking water use,» MNIT added. The development has prompted the U.S. government to issue an advisory, urging «critical infrastructure owners, operators, and integrators to remove publicly exposed PLCs and other operational technology (OT) from the internet as soon as possible.» Threat actors targeting exposed PLCs have modified passwords to lock out operators and disconnected the PLCs by changing their IP addresses, resulting in boil water notices and sustained manual operations. Organizations are advised to disconnect the PLC from the internet, enable password protection and change default passwords, and allowlist IPs to only allow remote access from known engineering laptops or other critical OT assets. Censys said it identified 4,148 internet-exposed hosts that respond to EtherNet/IP and self-identify as Rockwell Automation/Allen-Bradley, with more than 70% of them located in the U.S. Similarly, there are 4,117 internet-exposed hosts that fingerprint as Siemens SIMATIC S7-1200 and 2,072 internet-exposed hosts that fingerprint as Schneider Electric hardware. Over the weekend, Michigan reported cyber attacks on nine of the state’s water systems but an official told Associated Press that all systems were operating «safely.» The campaign underscores the escalating threat to poorly protected operational technology (OT) assets from adversaries seeking to disrupt critical infrastructure services across the U.S. and elsewhere.
  • Hijacked Wi-Fi Networks Lead to CornFlake Malware – Storm-2945, a sub-cluster associated with Midnight Blizzard (aka APT29), has been conducting «widespread but targeted traffic manipulation attacks» involving hospitality sector networks served by captive portals across the world. The campaign, ongoing since May 2026, has been codenamed CaptiveCrunch by Microsoft. This involves manipulating DNS and HTTP traffic from networks served by captive portals to redirect user traffic through actor-controlled infrastructure. «As part of the CaptiveCrunch campaign, Storm-2945 has leveraged their AitM position to redirect users through actor-controlled phishing infrastructure and has also delivered malware purporting to be browser or operating system updates in response to automated connectivity checks issued by users’ browsers,» Microsoft said. This includes a fully-featured Windows remote access trojan (RAT) called CornFlake with capabilities to conduct system enumeration, collect files and keystrokes, steal credentials and session tokens, conduct audio and video surveillance, monitor for removable media, and provide the threat actor a remote shell on infected systems. Also delivered via the trojan is a PowerShell-based infostealer called ChocoShell to harvest browser session cookies, saved passwords, Microsoft 365 Single Sign-On (SSO) tokens, and Wi-Fi credentials from compromised systems. The campaign is orchestrated via a web-based C2 panel called FruitStone. The infrastructure employs a variety of ClickFix techniques to trick the victim into downloading and executing the malware. There is also evidence indicating that the attackers are using similar ClickFix landings for Android devices to download and install an APK file. As of July 16, 2026, a portion of CaptiveCrunch landing pages have been found to redirect users to device code authentication flow experiences.

‎️🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first – CVE-2026-48449 (Adobe Campaign Classic), CVE-2026-18556, CVE-2026-18577 (N-able N-central), CVE-2026-44827, CVE-2026-45804, CVE-2026-44513 (Hugging Face Diffusers), CVE-2026-17583 (Thermo Fisher Scientific), CVE-2026-66066 (Rails), CVE-2026-10702 (Mozilla Firefox), CVE-2026-60004, CVE-2026-58443 (Gitea), CVE-2026-63077, CVE-2026-59792, CVE-2026-59793, CVE-2026-59794, CVE-2026-59795, CVE-2026-59796 (JetBrains TeamCity), CVE-2026-61511 (vBulletin), CVE-2026-53264 (Linux Kernel), CVE-2026-53921 (OpenWrt), CVE-2026-64765, CVE-2026-64766, CVE-2026-64764, CVE-2026-64763, CVE-2026-43776, CVE-2026-43818, CVE-2026-28981 (Apple iOS and macOS), CVE-2026-66032, CVE-2026-66033, CVE-2026-66034, CVE-2026-66035 (libssh2), from CVE-2026-59686 through CVE-2026-59690 (Progress Kemp LoadMaster), from CVE-2026-66036 through CVE-2026-66041 (FFmpeg), CVE-2026-66398 (phpMyFAQ), CVE-2026-64645, CVE-2026-64649, CVE-2026-64642, CVE-2026-64641 (Next.js), CVE-2026-13385 (ASUS), from CVE-2026-16804 through CVE-2026-16807 (Google Chrome), CVE-2026-52824 (Kimai), CVE-2026-53565, CVE-2026-53566 (Citrix Secure Access Client for Windows and Citrix Endpoint Analysis Client for Windows), CVE-2026-9770, CVE-2026-13230 (TP-Link Kasa EC70 v4 and EC71 v4 smart cameras), CVE-2026-15682 (AnyDesk), CVE-2026-53481, CVE-2026-53483 (Dell PowerProtect Data Domain), CVE-2026-52886, CVE-2026-54758, CVE-2026-57233 (Notepad++), CVE-2026-57807 (miniOrange OAuth Single Sign On – SSO WordPress plugin), CVE-2026-28302, from CVE-2026-28304 through CVE-2026-28317, CVE-2026-28321 (SolarWinds Serv-U), CVE-2026-16771 (AT&T Arris BGW210-700), CVE-2026-13723 (Develar), CVE-2026-16637 (OPeNDAP Hyrax), CVE-2026-15969, CVE-2026-15971, CVE-2026-15974, CVE-2026-15976, CVE-2026-15977, CVE-2026-15978 (SGLang), CVE-2026-15657, CVE-2026-15658 (foreUP), CVE-2026-16503, CVE-2026-16504 (VPS.org), CVE-2026-48395, CVE-2026-48396 (Adobe Bridge), CVE-2026-5674 (PipeWire PulseAudio), CVE-2026-34909 (Ubiquiti UniFi OS), and CVE-2026-17059 (keycloak-services).

🎥 Cybersecurity Webinars

  • AI Can Build Exploits in Minutes. Can Your Security Team Keep Up? → AI is collapsing the time between vulnerability disclosure and attack. Advanced models can now uncover flaws, generate working exploits, and chain them into complete attack paths at machine speed. This webinar presents a practical framework for gaining the visibility, context, and response speed needed to investigate and stop threats before attackers pull ahead.
  • How to Control the Open-Source Security Debt Created by AI Coding Tools → Learn how AI coding tools are expanding unvetted open-source use, accelerating vulnerability backlogs, and weakening existing governance. This webinar shows how to measure the resulting remediation debt, connect it to breach, audit, and productivity risks, and identify which governance models can contain it without slowing development.

📰 Around the Cyber World

  • Now-Patched Gitea Flaw Detailed – NoScope shared additional technical details of a security flaw in Gitea (CVE-2026-27771, CVSS score: 8.2) that was patched back in May 2026. The vulnerability allowed unauthenticated remote attackers to pull private container images from Gitea deployments without requiring an account, password, or other credentials. «Gitea’s container registry implements the OCI Distribution Specification, which authenticates clients with a bearer token issued by a dedicated token service. On affected versions, that token service issued a valid, signed JWT to requesters presenting no credentials at all,» NoScope said. «The token was honest about what it represented, carrying UserID: -1 and an empty Scope, but no registry read endpoint ever consulted those fields. Catalog listing, tag enumeration, manifest retrieval and blob download all accepted it. Any unauthenticated party on the internet could enumerate every container repository on an instance, including those marked private, and pull their layers.»
  • SQLite Critical CVEs or AI Slop? – JFrog said it uncovered a set of SQLite CVEs (CVE-2026-51302, CVE-2026-51303, CVE-2026-51300, CVE-2026-51297, CVE-2026-51296, and CVE-2026-51304) that seem to be instances of AI-generated slop making their way into official vulnerability feeds and receiving critical severity scores before technical validation. The analysis found that the advisories referenced functions that didn’t exist in the affected SQLite versions, cited incorrect or impossible source code locations, included PoCs that failed to reproduce any vulnerability, and, most importantly, were not listed on SQLite’s official CVE page. The findings show that organizations must take steps to distinguish legitimate vulnerabilities from questionable or AI-generated vulnerability reports before initiating unnecessary remediation, patching efforts, or automated security workflows.
  • LegacyHive Flaw Detailed – LevelBlue published a technical breakdown of LegacyHive, a PoC released by Chaotic Eclipse (aka Nightmare-Eclipse) last month coinciding with the release of Microsoft’s Patch Tuesday update. The vulnerability is a Local Privilege Escalation (LPE) vulnerability affecting Windows User Profile, a component responsible for loading and unloading Windows user profiles. On exploitation, LegacyHive can allow attackers to load other users’ hives and gain access to application data and Windows Explorer history, among others. «For EDR platforms with visibility into native Windows APIs, the strongest signals are user-mode invocations of NtCreateDirectoryObjectEx and NtCreateSymbolicLinkObject,» LevelBlue said. «These functions are rarely used outside system components, debugging tools, or specialized research utilities. Seeing both from the same process should immediately warrant investigation. Even without NT API telemetry, LegacyHive leaves a distinctive execution chain. The attack combines offline access to ntuser.dat or UsrClass.dat, modification of registry hives through Microsoft’s Offline Registry API, batch oplock requests, and CreateProcessWithLogonW using LOGON_WITH_PROFILE. Each operation is legitimate in isolation but observing them together within a short time window is highly unusual and well suited for behavioral correlation by EDR and SIEM platforms.»
  • Chinese Military Taps Into U.S. Models – According to a new report from Reuters, Chinese military researchers have distilled cutting-edge models developed by U.S. companies OpenAI and Anthropic to train domestic AI systems to advance the country’s defense capabilities. The report was based on a review of more than 80 Chinese academic papers and patents.
  • Exposed Police Dashboard Lays Bare How China Tracks Foreigners – An internet-exposed police dashboard named «Dynamic Control Platform for Overseas Personnel» has revealed how law enforcement agencies in the country track over 700 foreigners, including those in the northern Chinese city of Zhangjiakou. «In total, it had entries for nearly 12,000 people, which included fugitives, people from Hong Kong and Taiwan, as well as more than 300 foreign journalists,» The New York Times reported. «Some of them had not been to Zhangjiakou.» The dashboard displayed entries about people grouped by nationality, with their birth date, sex, marital status, address and occupation, and sometimes their religion. The leak was discovered by security researcher and journalist Marc Hofer. The system is believed to be developed by a Beijing company named Origin Dynamic, which filed a patent application in 2023 for a similar «information interface for non-Chinese citizens.»
  • The Problem of DangleGeddon – Cybersecurity researchers have once again warned of the risks posed by dangling DNS infrastructure across government, banking, automotive, manufacturing, and pharmaceutical sectors. A dangling DNS record is an active Domain Name System entry (DNS) that points to a resource no longer owned, used, or controlled by the original organization. This typically occurs when web applications, cloud storage, or virtual servers are deleted without first removing their corresponding CNAME or A records from the domain registrar. An attacker can leverage this behavior to claim that abandoned cloud service name or IP address, effectively hijacking a trusted subdomain. This, in turn, can permit the attacker to host malicious content and serve phishing pages or malware, inflict reputational damage by abusing the trusted brand’s subdomain, steal user credentials to create convincing phishing pages that appear to be legitimate services, perform cookie theft, and bypass security controls if the legitimate brand’s subdomain is allowlisted in security tools. In one case analyzed by Silent Push, an unspecified automotive company left a dangling DNS record pointing to a developmental application gateway hosted by an Azure virtual machine (VM). «This device can potentially be operationalized and passively receive stored XSS from internal scripts and API calls,» it said. «Developers’ credentials, like API keys and authentication headers, could be harvested for reuse to expand access into the company. In addition, the VM could serve as a platform for malware hosting with the coveted TLS lock.»
  • Microsoft Teams Vishing Leads to Chaos Ransomware – A Microsoft Teams voice phishing (vishing) campaign tracked as STAC4749 has used a «consistent set of IT-themed cloud domains and personas to gain remote access to victims’ systems» between February and June 2026 in attacks targeting dozens of North American organizations. «Following initial access, STAC4749 operators deployed a modular post-exploitation toolset, including a custom loader and backdoor to maintain persistent, controlled access and support follow-on activity,» Sophos said. «In several incidents, attackers later leveraged this access to deploy Chaos ransomware.»
  • IAB Uses Teams Phishing for Ransomware Attacks – A suspected initial access broker (IAB) for ransomware attacks has been observed using Teams vishing that convinces victims to launch a Quick Assist remote support session. The initial access is used to run PowerShell scripts to gather host information and deploy a Go-based backdoor dubbed GoGRPC. Four different versions of the backdoor have been spotted: Lep, Giver, Pet, and Kind. «These variants have overlapping capabilities but notable implementation differences,» Zscaler said. «GoGRPC is actively evolving. Each variant modifies its payloads and capabilities, adding or removing functionality to better support the threat actor’s objectives. Recent changes indicate an increased targeting of corporate environments, which may be tied to ransomware attacks.» In some instances, the threat actor has also deployed a backdoor called BlindDoor, a Go-based reverse SOCKS proxy known as RevSocket, and a Python-based reverse SOCKS proxy referred to as PyGRPC.
  • Arch Linux Disables AUR Package Adoption Amid Malware – Arch Linux has taken the step of temporarily disabling package adoption due to a surge in malicious takeovers of existing packages. «Due to the current influx of malicious package adoptions and follow-up commits made via the AUR, package adoption is currently disabled while we are handling the situation,» the maintainers said. «We will send a follow-up once we’re able to. In the meantime, feel free to report suspicious adoption events or commits that haven’t been dealt with yet, and stay vigilant!» In June 2026, a separate campaign targeted AUR via more than 400 packages.
  • New Dolphin X Infostealer Spotted – A new infostealer called Dolphin X uses an AI behavioral profiler to score and prioritize infected users based on their application usage, browsing activity, and installed software to identify high-value victims and maximize profits. The malware targets more than 300 applications and attempts to exfiltrate browser passwords, cryptocurrency wallets, SSH keys, and cloud tokens. Dolphin X has been advertised on the cybercrime underground by a vendor using the alias Kontraktnik since May 2026. A lifetime subscription ranges from $1,140 for basic access to $3,420 for the full-featured version. «A single archive can contain data from nine browsers, more than 100 wallet extensions, 65 desktop wallets, 10 password managers, and 30 cloud command-line tools,» Varonis said. «This gives the malware potential access to everything from a victim’s personal accounts to the credentials used to manage their employer’s cloud environment.»
  • Attackers Turn to Microsoft’s Trusted Login System for Phishing – Bad actors are increasingly abandoning fake Microsoft login pages in favor of abusing Microsoft’s legitimate authentication infrastructure in phishing attacks, allowing them to bypass security controls. Check Point said it identified more than 200 phishing emails targeting users across approximately 120 organizations worldwide between June 25 and the second week of July 2026. «The messages impersonated Microsoft Teams task notifications from HR and directed recipients to a legitimate Microsoft sign-in page,» it said. «Victims were then prompted to grant permissions to an attacker-controlled application, allowing the campaign to abuse Microsoft’s trusted authentication flow while concealing its malicious intent.»
  • FBI Arrests Man Accused of Using Steam Games to Drain Victims’ Crypto Wallets – The U.S. Federal Bureau of Investigation (FBI) arrested Zyaire Wilkins, a 21-year-old Florida resident and student, of uploading fake video games that contained malware to Steam that, when downloaded and installed by unsuspecting gamers, stole their passwords and other valuable data, and drained their cryptocurrency wallets. Per the FBI, Wilkins and his accomplices are alleged to have infected around 8,000 victims, and then hacked around 80 cryptocurrency wallets to steal at least $220,000 worth of cryptocurrency.
  • Turning Keystroke Noise to Text – A new study from a group of academics from Tohoku University has demonstrated a new acoustic side-channel attack that can reconstruct text typed on a laptop by just analyzing the sound of keystrokes. While prior attacks relied on collecting labeled recordings from the target keyboard beforehand or required specialized hardware, the latest eavesdropping attack enables stealthy eavesdropping in two real-world scenarios, including physical spaces (public and semi-public) and online meetings. The system works by first isolating individual keystrokes from an audio recording, grouping similar sounds together, and then using a Transformer-based language model to determine the most likely sequence of characters. «Our method combines unsupervised acoustic clustering with Transformer-based language model inference and iterative self-training, enabling stable character inference under highly uncertain acoustic-to-character mappings,» the researchers said. «We demonstrate that the proposed method achieves over 99% reconstruction accuracy with only 100-150 observed keystrokes under a close-proximity recording setup using a smartphone placed near the target device, significantly outperforming prior unsupervised baselines in low-data regimes.»
  • Two Open-Source Software Supply Chain Attack Campaigns – Socket has flagged a fake corepack.org site that’s impersonating Corepack, a Node.js tool for managing package managers, and using it as a lure to deliver an infostealer and proxyware to developers who download it. «The site has existed in some form since early 2026 as a low-quality, apparently AI-generated imitation, but it recently started serving executable downloads,» Socket said. «Corepack is not distributed as a Windows installer, and the real project has no official website at corepack.org. Any download offered there should be treated as malicious.» It’s assessed that the site is AI-generated. In a related development, JFrog identified a massive set of 148 npm packages that are disguised as student web proxies, but hide mutable remote code execution vectors and a high-performance Wisp-compatible WebSocket traffic generator. «They were designed to silently enlist visiting browsers into distributed denial-of-service botnets while generating aggressive popunder advertising revenue,» it said. Some aspects of the campaign were highlighted by SafeDep in late May 2026.
  • AI linked to more than half of cybercrime in Africa – A new report from INTERPOL has found that AI is enabling 55% of reported cybercrimes across Africa, making attacks faster, more scalable, and increasingly difficult for victims and platforms to detect. This encompasses digital sextortion and online harassment, as well as sophisticated business email compromise (BEC) schemes. «The absence of real-time, inter-agency data sharing between banks, telecoms and law enforcement creates a dangerous blind spot in efforts to combat financial fraud,» INTERPOL said. «This vulnerability is being exploited by criminals who have moved beyond simply stealing existing credentials to creating entirely synthetic identities. Combining real personal data with fabricated elements, these AI-generated digital personas can bypass even advanced biometric verification systems and have been used to open bank accounts, secure mobile loans and register SIM cards under false names.»
  • Security Risks of Exposed MCP Servers – Google-owned Wiz has warned that enterprises are exposing Model Context Protocol (MCP) servers to the internet, with some of them returning full tool catalog to an anonymous caller, fetching real data, and revealing a sensitive backend. «These expose sensitive data like employee PII and internal business records, write and delete operations on production systems, and in some cases code execution and access to cloud credentials,» Wiz said. «The protocol’s first widely-used version shipped without an authentication mechanism. The spec added OAuth 2.1 in March 2025, but nearly all the servers we found still run the original version and don’t use it. The pattern is the same across most of them: backend credentials baked into the deployment, a managed cloud endpoint that’s internet-reachable by default, no auth layer added on top.»
  • Nuclear-Sabotage Malware Benchmark Trick Most Frontier AI Models – A multi-stage reverse-engineering benchmark developed by SentinelOne tests «whether a model can keep a malware investigation trustworthy as new evidence repeatedly invalidates its earlier conclusions,» in contrast to other AI benchmarks that test bounded tasks. Developed based on its own analysis of the Fast16 malware, the study found that «OpenAI’s GPT-5.6 Sol was the only publicly available model to complete the full eight-stage investigation, giving concrete shape to what ‘Frontier-class’ capabilities offer analysts.» That said, humans remain essential to define objectives, expose blind spots, and retain final publication authority.
  • An Open Directory Reveals NGINX Rift and Ghost CMS Exploits – An exposed directory on a Singapore-hosted VPS, 165.154.236[.]93, has been found to stage exploits for NGINX Rift (CVE-2026-42945), a long-standing heap overflow, and a blind SQL injection in the Ghost Content API (CVE-2026-26980), alongside Splunk, PaperCut, Samba, WebLogic, and D-Link NAS tooling. «The recovered shell history from the directory recorded the attacker running the exploits against live external infrastructure, using out-of-band (OOB) DNS callbacks to verify execution, and using the same server to catch reverse shells,» Hunt.io said. «Alongside the web exploits were a broader RCE toolkit and pre-staged install files for AdaptixC2 and SuperShell. The target list spanned eleven countries across five continents and leaned heavily toward high-value sectors: federal and state government, universities, healthcare and financial services.» The activity is believed to be the work of a Chinese-speaking threat actor.
  • CISA Issues Guidance to Isolate Vital Systems and Manage OSS Risks – The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued guidance to help critical infrastructure operators protect essential services from growing cyber threats and ensure continuity of operations during cyber incidents or geopolitical crises by maintaining robust isolation and recovery plans. «State-sponsored cyber actors target critical infrastructure for several nefarious reasons such as espionage or service disruption, often linked to broader geopolitical conflicts,» CISA said. «During crises or conflicts, operators of critical infrastructure and network defenders may isolate essential operational technology (OT) systems as an emergency measure to prevent adversaries from executing cyberattacks, to contain ongoing threats, and to facilitate the restoration of compromised systems.» The agency has also outlined considerations and best practices for federal entities to securely use, evaluate, and publish open-source software. «The guidance urges agencies to obtain sufficient transparency into all relevant components, including training data, of the AI system before deeming the product as OSS for risk management purposes,» it said. «Only with transparency and access can agencies understand and study the software, analyze it for vulnerabilities, and remediate any found vulnerabilities or risks.»
  • RubyGems Cryptojacking Campaign – A set of 199 malicious gems published to RubyGems has been found to embed an identical XMRig cryptojacking payload to mine Monero cryptocurrency on developer systems. «Each gem is a trojanized copy of a popular, legitimate Ruby library,» Palo Alto Networks Unit 42 said. «The payload uses a 5-hour delayed Thread.new{sleep 18000; …} trigger to evade sandbox analysis.» In addition to taking steps to achieve persistence via multiple methods, the malware uses SSH for lateral movement and is capable of infecting other ecosystems, including Node.js, Python, Docker, Git, and VS Code extensions. Mend.io, which also shared details of the campaign, said the payload is hidden inside a dotfile (lib/.threadpool.rb) that standard directory scans skip by default.
  • Email Threat Landscape in Q2 2026 – Microsoft said phishing volume linked to the Tycoon 2FA phishing platform, including QR code phishing and CAPTCHA-gated phishing, fell 92% from pre-disruption averages in the second quarter of 2026 between April and June. However, the tech giant said it «observed continued growth in Teams-based social engineering, particularly voice phishing (vishing), with weekly malicious call attempts reaching nearly ten times the mid-2025 baseline by the end of the quarter.» Microsoft said it detected approximately 7.6 billion email-based phishing threats throughout the quarter, with monthly volumes declining modestly from 2.7 billion in April to 2.4 billion in June. HTML and PDF attachments remained the two most common malicious payload types across the quarter, together accounting for roughly 60-70% of all payload-based attacks each month. In early June 2026, Microsoft said it detected a large-scale BEC campaign that reached more than 67,000 users across more than 42,000 organizations in under three hours, most of them in the U.S., with an aim to redirect salary payments to attacker-controlled bank accounts.

🔧 Cybersecurity Tools

  • EMBA → Firmware is where critical bugs hide longest because it is opaque, fragmented, and painful to inspect manually. EMBA turns that black box into an actionable security report: it extracts embedded-device firmware, runs static and emulation-based analysis, builds an SBOM, and flags outdated components, insecure binaries, vulnerable scripts, and hard-coded credentials through a command-line workflow with web-based reporting. Built for penetration testers, product-security teams, and developers, it compresses days of firmware triage into a repeatable open-source process.
  • GrantGuard → Every «always allow» click in Claude Code can leave behind a standing permission that remains long after the task ends, with pasted API keys, credential-store access, unrestricted `git push`, or destructive commands buried in rarely reviewed settings. GrantGuard is an open-source, local-only tool that finds these accumulated grants, classifies them by risk, and lets users remove unsafe permissions through a browser interface or CLI, without sending settings off-device or loading third-party runtime packages.

Disclaimer: This is strictly for research and learning. It hasn’t been through a formal security audit, so don’t just blindly drop it into production. Read the code, break it in a sandbox first, and make sure whatever you’re doing stays on the right side of the law.

Conclusion

The useful question is not whether a system is exposed. It is which quiet assumption lets it reach farther than intended: a default, a trusted workflow, an abandoned endpoint, or code nobody checked.

That is where the next incident is probably waiting. Not in the loudest alert, but in the handoff everyone assumes belongs to someone else. Check the boundaries. Then check what crosses them.

AI-Powered Hacking, 370 Chrome Flaws, SonicWall Attacks, DNS Hijacking + 22 More Stories – CYBERDEFENSA.MX

A lot of security still comes down to trusting the wrong screen.

This week, that screen might be a login page, an install guide, a recruiter call, or a familiar service behaving slightly wrong. Behind it: reused credentials, exposed systems, quiet loaders, abused trust, and exploit paths that should have been harder.

Some defenses improved. The loose parts still got found first. Anyway, here’s the mess.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

  1. Phishing delivers XWorm

    A cybercrime group known as xplogs22 has been observed targeting Russia and other CIS countries with phishing emails that deliver Xworm. The group, per F6, is believed to have been active since November 2023. Prior attacks mounted by the threat actors leveraged Formbook and Snake Keylogger, before switching to XWorm around July 2025. In recent months, Russian customers of the banking sector have also been targeted by an Android trojan called LunaSpy as part of social engineering attacks. LunaSpy can capture camera streams, record audio and the screen, and collect sensitive data. The malware is disguised as an antivirus application to evade detection.

Most failures stay quiet until someone relies on them.

A login works. A partner is trusted. A tool behaves as expected. Then one assumption turns out to be doing all the security work.

That is the part worth checking before next week finds it first.

Android Spyware, PLC Attacks, AI Image Prompt Injection + 12 More Stories – CYBERDEFENSA.MX

Most of this week’s trouble came dressed as something useful.

A package stole data. A fake extension opened remote access. A safety app became spyware. An image gave hidden orders to an AI agent. Other threats hid in open systems, weak code, and normal network traffic.

The threats change every week. Subscribe, and we’ll alert you when each new ThreatsDay Bulletin is out.

The danger was easy to miss because it looked ordinary. Here is the full list:

  1. Support uploads face cutoff

    GitHub has announced an upcoming security change that may affect GitHub Enterprise Server (GHES) support bundle uploads. «Beginning August 18, 2026, GitHub will start rejecting command-line support bundle uploads from older GHES appliances that have not been updated with the required security patches,» GitHub said. «To avoid any disruption when submitting support bundles with ghe-support-bundle, ghe-cluster-support-bundle, or ghe-support-upload commands, please update your GHES instance to the latest patch release available for your current version line.» At minimum, the required patch versions are: 3.21.3, 3.20.5, 3.19.9, 3.18.12, and 3.17.18.

The common thread was not advanced hacking. It was borrowed trust. Each threat used something people already accept: an install, a permission, a familiar name, or a normal system feature.

That changes the job. The question is no longer only «Is this safe?» It is also «What can this do if it is not?» The smaller the action looks, the tighter its limits should be.

WordPress RCE, SonicWall 0-Days, AI Service Attacks, SharePoint 0-Day and More – CYBERDEFENSA.MX

A single request should not be able to do this much. But this week, small inputs led to code execution, memory loss, stolen keys, and disabled security tools.

The paths were often simple: exposed systems, weak checks, old drivers, fake prompts, and public code used for malware delivery. Some bugs were new. Others were already being used before defenders had time to patch.

Here is the full recap of what broke, what was exploited, and what needs attention now.

⚡ Threat of the Week

New wp2shell WordPress Core Flaw Lets Unauthenticated Attackers Run Code – Searchlight Cyber disclosed a pre-authenticated remote code execution vulnerability in WordPress Core that can be exploited anonymously on a standard WordPress installation, without requiring any plugins or other special conditions. It is a combination of CVE-2026-63030 (REST API batch-route confusion) and CVE-2026-60137 (SQL injection in WordPress core) that can be chained to turn an anonymous request into code execution. watchTowr said it’s already seeing proof-of-concept (PoC) exploits in circulation and that it’s beginning to see the first signs of in-the-wild exploitation. «This is going to hurt,» watchTowr CEO Benjamin Harris said. «WordPress runs on hundreds of millions of websites globally. Some of those will be auto-patched by their hosting providers, but plenty will not, and that is where the damage will be done. Our advice is simple: patch as fast as you possibly can, and do not stop there. Put the controls and investigations in place to determine whether an attacker got there first and to detect and remove any backdoors that may already have been dropped before you patched.» The cybersecurity company said it’s the latest example of vulnerabilities being surfaced by AI-assisted tooling and how the technology is being abused by attackers to weaponize them.

🔔 Top News

  • SonicWall SMA Zero-Days Exploited as 0-Days – A previously undocumented threat actor codenamed UTA0533 has been attributed to the exploitation of recently disclosed SonicWall Secure Mobile Access (SMA) 1000 series VPN appliances as zero-days prior to their public disclosure since June 22, 2026. The discovery was made following an incident response investigation initiated earlier this month. The impacted organization has not been identified. «This threat actor was observed using multiple zero-day exploits, malware designed specifically for SonicWall SMA VPN appliances, as well as other attacker tradecraft,» Volexity said. The vulnerabilities in question are CVE-2026-15409 (CVSS score: 10.0) and CVE-2026-15410 (CVSS score: 7.2), both of which could be chained to facilitate arbitrary command execution and take over susceptible devices. Patches for both vulnerabilities were released by SonicWall last week.
  • DoS Flaw in OpenSSL – The Okta Red Team disclosed details of HollowByte, a denial-of-service (DoS) flaw in OpenSSL. «By sending a malicious payload of just 11 bytes, a remote, unauthenticated attacker can force a server to allocate disproportionate chunks of memory before any security handshake even begins,» Okta said. Put differently, an unauthenticated attacker — through 11 bytes of carefully crafted data — can convince OpenSSL to reserve up to 128 KB of heap memory for a handshake message that never actually arrives, causing a server to exhaust available RAM and trigger a DoS condition. The OpenSSL team resolved the issue in versions 4.0.1, 3.6.3, 3.5.7, 3.4.6, and 3.0.21. «Instead of trusting the header outright, OpenSSL now grows the buffer only as bytes actually land on the wire. A claim with no follow-through now costs the server nothing,» Okta said.
  • CISA Adds New SharePoint RCE Zero-Day to KEV Catalog – The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a newly patched security flaw impacting Microsoft SharePoint Server to its Known Exploited Vulnerabilities (KEV) catalog, requiring Federal Civilian Executive Branch (FCEB) agencies to apply the fixes by July 19, 2026. The vulnerability, CVE-2026-58644 (CVSS score: 9.8), is a critical deserialization of untrusted data vulnerability that allows an unauthorized attacker to execute arbitrary code. Patches for the flaw have been released as part of the Patch Tuesday updates released on July 14, 2026. Microsoft revised its bulletin to clarify that CVE-2026-58644 has been exploited in the wild, meaning the shortcoming was weaponized as a zero-day prior to the fixes becoming available. The development came as Microsoft shipped its largest Patch Tuesday on record, addressing 622 vulnerabilities.
  • OkoBot Malware Framework Infects Windows to Phish Crypto Seed Phrases – A new malware framework called OkoBot is designed to capture the contents of cryptocurrency wallet windows. OkoBot is an updated version of TookPS, which is a downloader for retrieving malicious commands and scripts from attacker-controlled servers to further propagate attacks, including a Python-based infostealer and a remote access trojan called TeviRAT. «This campaign differs from previous activity in that it uses a new framework to deliver all malicious modules and orchestrate them via an SSH tunnel,» Kaspersky said. «In total, the framework includes more than 20 malicious payloads and implants, covering a wide variety of functions. At the time of writing, the threat remains active.» The infection chain makes use of ClickFix and malware distributed through GitHub that masquerades as legitimate software for initial access. It also comes with a web browser extensions loader to deliver Rilide, a browser-based stealer, as well as inject an implant into Trezor Suite, Ledger Wallet, and Ledger Live processes to collect seed phrases, log keystrokes and clipboard content, take screenshots, and capture keystrokes and the video stream of the target application’s window using the OkoSpyware module. Hundreds of victims of the OkoBot campaign have been detected in more than 25 countries, with the highest concentration in Brazil, Vietnam, Canada, Mexico, and Türkiye. The activity remains unattributed.
  • NadMesh Scans Exposed AI Services for Cloud Keys and Kubernetes Tokens – A new Go botnet called NadMesh has been observed hunting for exposed AI services related to ComfyUI, Ollama, n8n, Open WebUI, Langflow, and Gradio to steal AWS keys and Kubernetes tokens. «It folds scanning, exploitation, and credential/AI-service intelligence harvesting into a single autonomous platform,» QiAnXin XLab said. «On the victim, the bot agent establishes persistence along three independent paths: an SSH public-key backdoor (.ssh/authorized_keys), persistence files in multiple locations (/dev/shm/.a, /var/tmp/.a, /tmp/.a), and hidden cron watchdogs (/etc/cron.d/.sys_monitor, /etc/cron.d/.s).»

‎️🔥 Trending CVEs

Bugs drop weekly, and the gap between a patch and an exploit is shrinking fast. These are the heavy hitters for the week: high-severity, widely used, or already being poked at in the wild.

Check the list, patch what you have, and hit the ones marked urgent first – CVE-2026-63030, CVE-2026-60137 (WordPress Core), CVE-2026-58644, CVE-2026-56164 (Microsoft SharePoint Server), CVE-2026-56155 (Microsoft Active Directory Federation Services), CVE-2026-53412 (Zoom Desktop Client for Windows and Zoom VDI Client for Windows), CVE-2026-44747, CVE-2026-27690, CVE-2026-44761 (SAP), CVE-2026-57219, CVE-2026-57221 (RabbitMQ), CVE-2026-59208, CVE-2026-54305 (n8n), CVE-2026-60105 (Monsta FTP), CVE-2026-14960, CVE-2026-14961 (tdeio64.sys driver), CVE-2026-33894, CVE-2026-33895 (Digital Bazaar node-forge), CVE-2026-6875 (ServiceNow AI Platform), CVE-2026-42533, CVE-2026-60005, CVE-2026-56434 (F5 NGINX Plus and NGINX Open Source), CVE-2026-20296, CVE-2026-20297 (Splunk Enterprise), CVE-2026-15265 (Tenable Agent), CVE-2026-6423 (ESET Inspect Connector), CVE-2026-15053 (Tanium Server), CVE-2026-44909, CVE-2026-59173, CVE-2026-59762 (HTTP/2 server implementations), CVE-2026-14890 (SGLang), CVE-2026-14266 (7-Zip), CVE-2026-59084 (Apache Tomcat), CVE-2026-15682 (AnyDesk), and CVE-2026-54523 (Kyverno).

🎥 Cybersecurity Webinars

  • Your AI Agent Has Credentials. Can You Stop It When It Goes Rogue? Hands-on testing of OpenClaw shows how agentic AI can expose secrets, bypass safety controls, and create a powerful new attack surface. Join Okta Threat Intelligence Director Jeremy Kirk to examine how attackers are abusing AI agents and learn practical ways to control access, enforce least privilege, detect shadow AI, and shut down risky agents before they cause damage.
  • When AI Ships 50× More Code, Human Review Stops Scaling → AI-assisted development is pushing code production beyond what traditional security reviews and CVE-driven remediation can handle. This webinar gives security leaders a practical framework for governing the expanding attack surface, building secure-by-default controls, and enabling teams to develop at machine speed without surrendering control of software risk.

📰 Around the Cyber World

  • New Campaign Delivers Remcos RAT – A new malware distribution campaign has abused the credibility of government institutions to increase the likelihood of infection success. The activity targets Indian businesses and taxpayers using Goods and Services Tax (GST)-related themes to distribute malware. «The threat actors impersonated legitimate government departments and distributed malicious emails disguised as official notifications related to taxation, refunds, compliance requirements, and regulatory matters,» Seqrite Labs said. «The threat actors employ convincing documents and filenames that closely resemble official GST notifications, making it difficult for recipients to distinguish malicious content from legitimate government correspondence.» The end goal is to deploy Remcos RAT and steal sensitive information.
  • India’s Kudankulam Nuclear Power Plant Suffers a Data Leak – The Kudankulam Nuclear Power Plant located in the Indian state of Tamil Nadu suffered an accidental exposure after Reliance Infra (RPOWER) got hit by a ransomware group called World Leaks, a spin-off of Hunters International, which, in turn, is another variant of the Hive ransomware family. The leak consists of 18,997 files, totalling 14.3GB of data, per security researcher Rakesh Krishnan. They contain purported blueprints for the ventilation and cooling systems used in Unit 3 and Unit 4, along with a complete floor layout of a «common control room». It’s assessed that Reliance Infra was not impacted directly, but rather through a third-party vendor named Yotta.
  • Blind Eagle Shows No Signs of Stopping – Nearly a year after Blind Eagle’s activities were documented, a new report from LevelBlue has found the threat actor to be active, moving part of its VBScript delivery infrastructure onto the Russian bulletproof hosting provider Proton66 as of June 2025. The group has also devised a bespoke string-obfuscation scheme, a RunPE loader built entirely on a bare AutoIt3 interpreter, and an upgraded version of AsyncRAT that introduces Windows Notification Facility (WNF) process injection, a custom Base28 payload encoding, a full Hidden VNC (HVNC) banking-fraud module with browser profile cloning, and a Chrome App-Bound Encryption (ABE) bypass, per LevelBlue.
  • Qilin Ransomware Use of EDR Killer – Qilin ransomware operations have been observed adopting aggressive, kernel-level defense evasion to blind and disable endpoint security products before its main ransomware payload is executed on a victim’s network. The EDR killer, packed via the Shanya packer, is sold on illicit marketplaces for $2,000. «The EDR killer compares the returned locale to a known locale blacklist to avoid attacking any Commonwealth of Independent States (CIS) countries such as Russia and Belarus,» Flashpoint said. «The EDR killer then writes a vulnerable driver to disk and loads this driver via Service Manager. This driver is the ThrottleStop driver from TechPowerUp LLC’s free and legitimate application of the same name, used to bypass CPU throttling. However, the driver suffers from a vulnerability, allowing the malware to map physical memory to kernel-mode virtual memory to perform direct kernel read and write operations.» Also put to use is a custom Rust-written loader that performs reflective Portable Executable (PE) loading of the ransomware payload.
  • DefiTuna Suffers a Security Incident – DeFiTuna, an Automated Market Maker (AMM) on the Solana blockchain, was exploited on July 16, 2026, for $569,601 USDC. «The attackers created a highly illiquid TUNA/USDC pool and used it as the destination for borrowed USDC routed through Jupiter,» CertiK said. «Because the swap returned only a negligible amount of TUNA, DeFiTuna’s value calculation rounded the position’s total assets down to zero. The protocol then incorrectly treated the position as healthy, allowing the attackers to bypass the solvency check and withdraw the USDC through attacker-controlled liquidity positions.»
  • Next.js Opts for Scheduled Security Releases – Vercel announced that Next.js is adopting a formal security release program, replacing ad-hoc patches for security fixes following a surge in AI-assisted vulnerability discovery. «This kind of scheduled, pre-announced security release has become standard practice for major open source projects, and we think it’s the right model for Next.js at its current scale,» Vercel said. «Here’s what you can expect going forward: roughly once a month, we’ll publish advance notice of upcoming security releases. Each announcement will include the expected release timeline and the highest anticipated severity among the vulnerabilities it covers. This lead time lets you plan your upgrades, and it lets us coordinate with hosting providers and other platform partners to deploy mitigations, such as firewall rules, that help protect applications that haven’t been patched yet.»
  • Disguised Gambling Apps Target Brazil – A new analysis from 9to5Mac has revealed more than 60 «jacket apps» on the App Store that are disguised as simple games and utilities that become online betting platforms when accessed from Brazilian IP addresses. Most of the apps are published by developer accounts with only a single App Store listing, with further investigation linking them to a «public GitHub repository containing instructions for a Cursor agent to create simple, vibe-coded apps that serve as fronts for the betting platforms.»
  • Ransomware Stats for Q2 2026 – The Gentlemen has become the most active ransomware group for Q2 2026, claiming 300 victims, surging past Qilin (289), DragonForce, Akira, and LockBit. Another group named Deadlock resurfaced after 11 months of silence with 75 June victims. In all, the top 11 tracked groups accounted for 1,368 of Q2’s victim claims across 99 countries. «What sets The Gentlemen apart is its packaging, where affiliates receive ready-made tools that ship and update faster than most competing programs,» ReliaQuest said.
  • 2 Members of Chinese Money Laundering Network Charged with Laundering $43M in Investment Fraud – The U.S. Justice Department unsealed charges against a New York man and woman for conspiracy to launder money derived from cyber investment fraud scams. «Between 2020 and 2022, Zhuoying Chen, 27, of Brooklyn, New York, and Haojie Zhang, 38, of Queens, New York, managed a network of more than a dozen individuals based in Queens and Brooklyn, who opened 140 bank accounts in the name of approximately 45 shell companies to launder at least $43 million in proceeds of investment scams,» the department said. «Then, Chen and Zhang allegedly conspired with China-based co-conspirators to transfer the funds involved in the fraud schemes abroad. The fraud schemes consist of perpetrators contacting victims via messaging services or social media applications. The perpetrators would initiate relationships with the victims and gain their trust, convincing victims to send money for lucrative investment opportunities. The perpetrators would show the victims fake profits on the purported investment and encourage the victims to invest more. The perpetrators would then steal the victim’s funds.»
  • U.S. Cyber Agency Uses Mythos to Audit Government Code – Reuters reported that the U.S. Cybersecurity and Infrastructure Security Agency (CISA) is using Anthropic’s AI model Mythos to audit government software for defects that could potentially offer a pathway for foreign spies and cybercriminals, citing three people familiar with the matter.

🔧 Cybersecurity Tools

  • VisionSec → It is an open-source, self-hosted threat intelligence platform that combines domain monitoring, phishing detection, exposed-service scanning, GitHub secret discovery, breach checks, email security assessments, and Telegram alerts in a modular Docker-based deployment. The project remains at an early stage, with no published releases at the time of writing.
  • owLSM → It is an open-source Linux security agent that uses eBPF LSM to run stateful Sigma rules inside the kernel, block malicious activity, correlate events across multiple probes, and provide detailed context for security monitoring and response.

Disclaimer: This is strictly for research and learning. It hasn’t been through a formal security audit, so don’t just blindly drop it into production. Read the code, break it in a sandbox first, and make sure whatever you’re doing stays on the right side of the law.

Conclusion

That is the week: exposed systems, weak checks, old tools, and attackers moving faster than patch cycles.

Review what applies, fix the obvious gaps first, and assume anything public has already been tested.